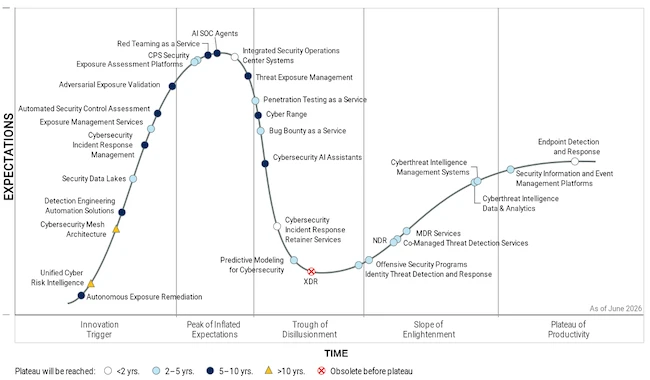
Gartner says AI SOC agents are moving rapidly from hype into real-world evaluations, but most organizations will only see measurable gains if they use a structured, outcomes-driven framework. The report highlights seven key evaluation areas, including workload reduction, vendor durability, analyst impact, autonomy boundaries, stack integration, and transparency, while survey data shows broad adoption but cautious trust. #Gartner #AI_SOC_Agents #Prophet_Security
Category: Cyber Security News
Tencent’s Zhuque Lab released AI-Infra-Guard, an open-source scanner for AI systems that fingerprints services like Ollama, vLLM, and ComfyUI, checks thousands of CVEs, inspects MCP servers and agent skills, and tests models for jailbreak resistance. It also highlights risks from indirect prompt injection and notes that the tool should not be exposed directly because the open-source build has no built-in authentication. #AI-Infra-Guard #ZhuqueLab #Ollama #vLLM #ComfyUI #SkillTrustBench #MCP
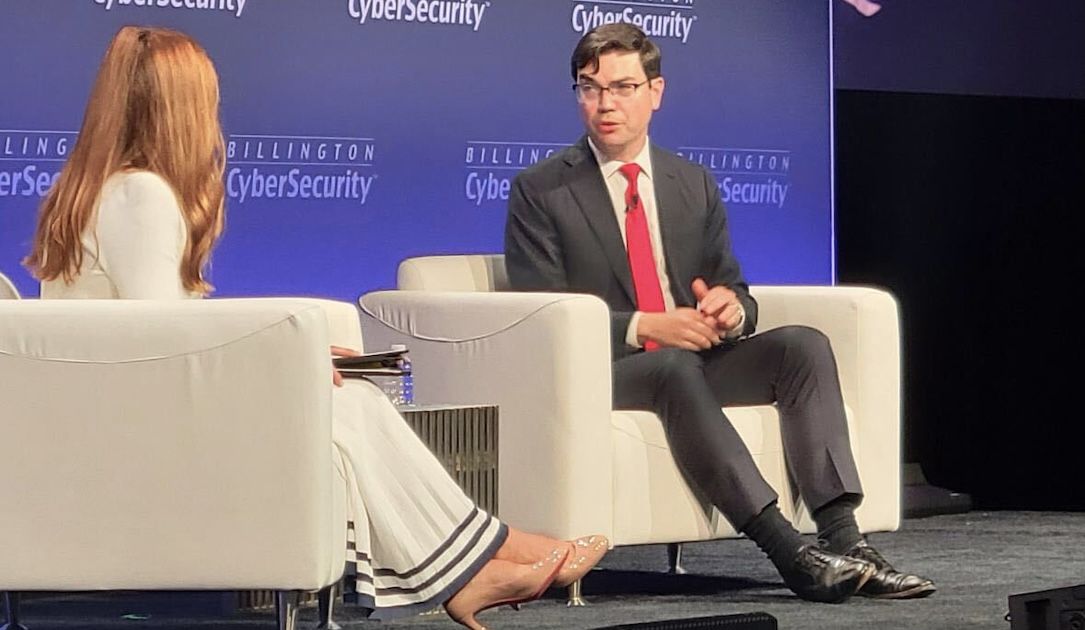
CIA cyber operators helped build a “flawless intelligence picture” that enabled U.S. forces to locate and capture Nicolás Maduro and his wife in Caracas during Operation Absolute Resolve. Deputy Director Michael Ellis also said AI will increasingly shape CIA cyber operations, intelligence collection, and analysis, with human oversight and safeguards in…
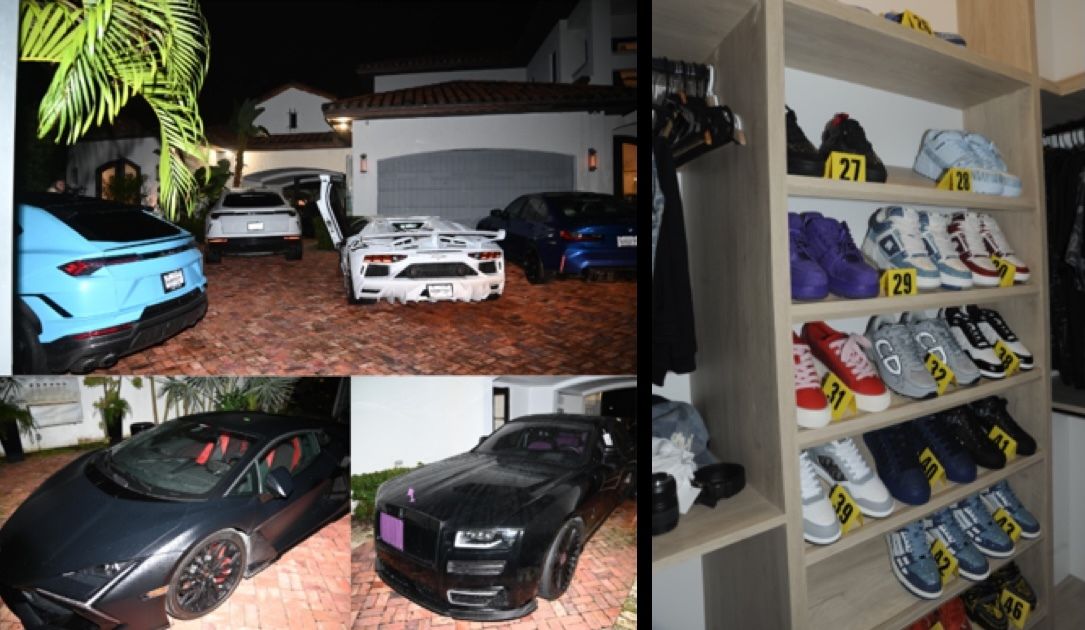
Malone Lam, a Singaporean national known as “Anne Hathaway” and “$$$,” pleaded guilty to racketeering for leading the Social Engineering Enterprise, which stole more than $245 million in cryptocurrency through coordinated scams and home break-ins. Prosecutors said the group impersonated Apple, Google, and customer support staff, targeted wealthy crypto holders, and…

CISA has added CVE-2026-86218, a critical static code injection flaw in N-able N-central, to its KEV catalog and ordered FCEB agencies to patch it by September 11, 2026. N-able said the issue has been exploited in the wild, while Huntress is investigating a compromise of a fully patched N-central environment and…

Daily Recap, Authorities dismantled a crypto scam spree linked to a $240 million Bitcoin theft after suspects spent the stolen funds, while MikroTik patched critical RouterOS flaws used for unauthenticated device hijacking. The week also saw major breach disclosures (including Mathspace, a Vietnam-linked API leak of ~220 million traveler records, and a Berlin city-agency credential leak), plus ongoing identity and backdoor activity such as help-desk social-engineering targeting Microsoft 365 and the StyleSmuggler zero-day dropping a Linux backdoor.
#Bitcoin #RouterOS #MikroTik #Mathspace #Microsoft365 #StyleSmuggler #Linux #BigBear #MFA #Chrome #Edge #PEEP #Chrome #Edge #Berlin #Vietnam #API #Microsoft
Researchers at Calif discovered and privately reported a critical WeChat vulnerability that enabled them to build “WeWorm,” a worm that spreads through WeChat calls without any user interaction. The flaw let attackers compromise accounts and propagate across iOS and Android devices, prompting Tencent to release mitigations for the app and its servers. #WeChat #Tencent #WeWorm #Calif
Microsoft patched 974 defects in its largest-ever Patch Tuesday update, including two actively exploited zero-day vulnerabilities in the Windows Update Stack and Windows Advanced Local Procedure Call. Security experts said AI-assisted vulnerability discovery is increasing the number of disclosed flaws, but it has not yet caused a matching surge in real-world exploitation. #CVE-2026-81963 #CVE-2026-85880 #WindowsUpdateStack #WindowsAdvancedLocalProcedureCall
Microsoft’s latest Patch Tuesday set a new record with 973 disclosed bugs, including two actively exploited vulnerabilities tracked as CVE-2026-81963 and CVE-2026-85880. Researchers warned that thousands of unpatched Exchange servers and weaknesses in the Windows update stack could help attackers chain exploits into ransomware-style intrusions. #CVE-2026-81963 #CVE-2026-85880 #Microsoft #Windows #Exchange #AdobeCommerce…

Check Point Research reported that a single hidden instruction in a ChatGPT conversation could make ChatGPT silently exfiltrate data from a user’s connected Gmail and conversation context while still replying normally. The researchers said the issue used a hidden communication channel between ChatGPT containers via internal JFrog Artifactory metadata, and that…

The Liquid Network suffered a major incident in which nearly 4,000 bitcoin were withdrawn from its federation wallet, prompting a pause of the sidechain and concern over L-BTC backing. After on-chain negotiations, 3,400 bitcoin were returned, while about 598.5 bitcoin remains unreturned amid debate over whether the actors were white hats…

A previously undocumented threat actor called Slim Spider has been targeting Brazilian financial institutions since at least March 2026, with a focus on cloud environments, cryptocurrency assets, and Pix payment infrastructure. CrowdStrike also linked Slim Spider and Breeze Comet to sophisticated operations that steal credentials, deploy backdoors, and abuse Brazilian payment…

Adobe has released fixes for more than 170 vulnerabilities across its products, including a critical zero-day in Adobe Commerce and Magento Open Source that was actively exploited in the wild. The exploited flaw, tracked as CVE-2026-75650 and dubbed StyleSmuggler, enabled unauthenticated remote code execution, prompting urgent guidance to patch systems and…
Microsoft’s September 2026 Patch Tuesday addresses a record 974 CVEs, including two zero-days in Windows ALPC and the Windows Update Stack that can let local attackers gain SYSTEM privileges. The update also fixes major flaws in Exchange Server, SharePoint, SQL Server, Remote Desktop Services, and other Microsoft products, with several issues…
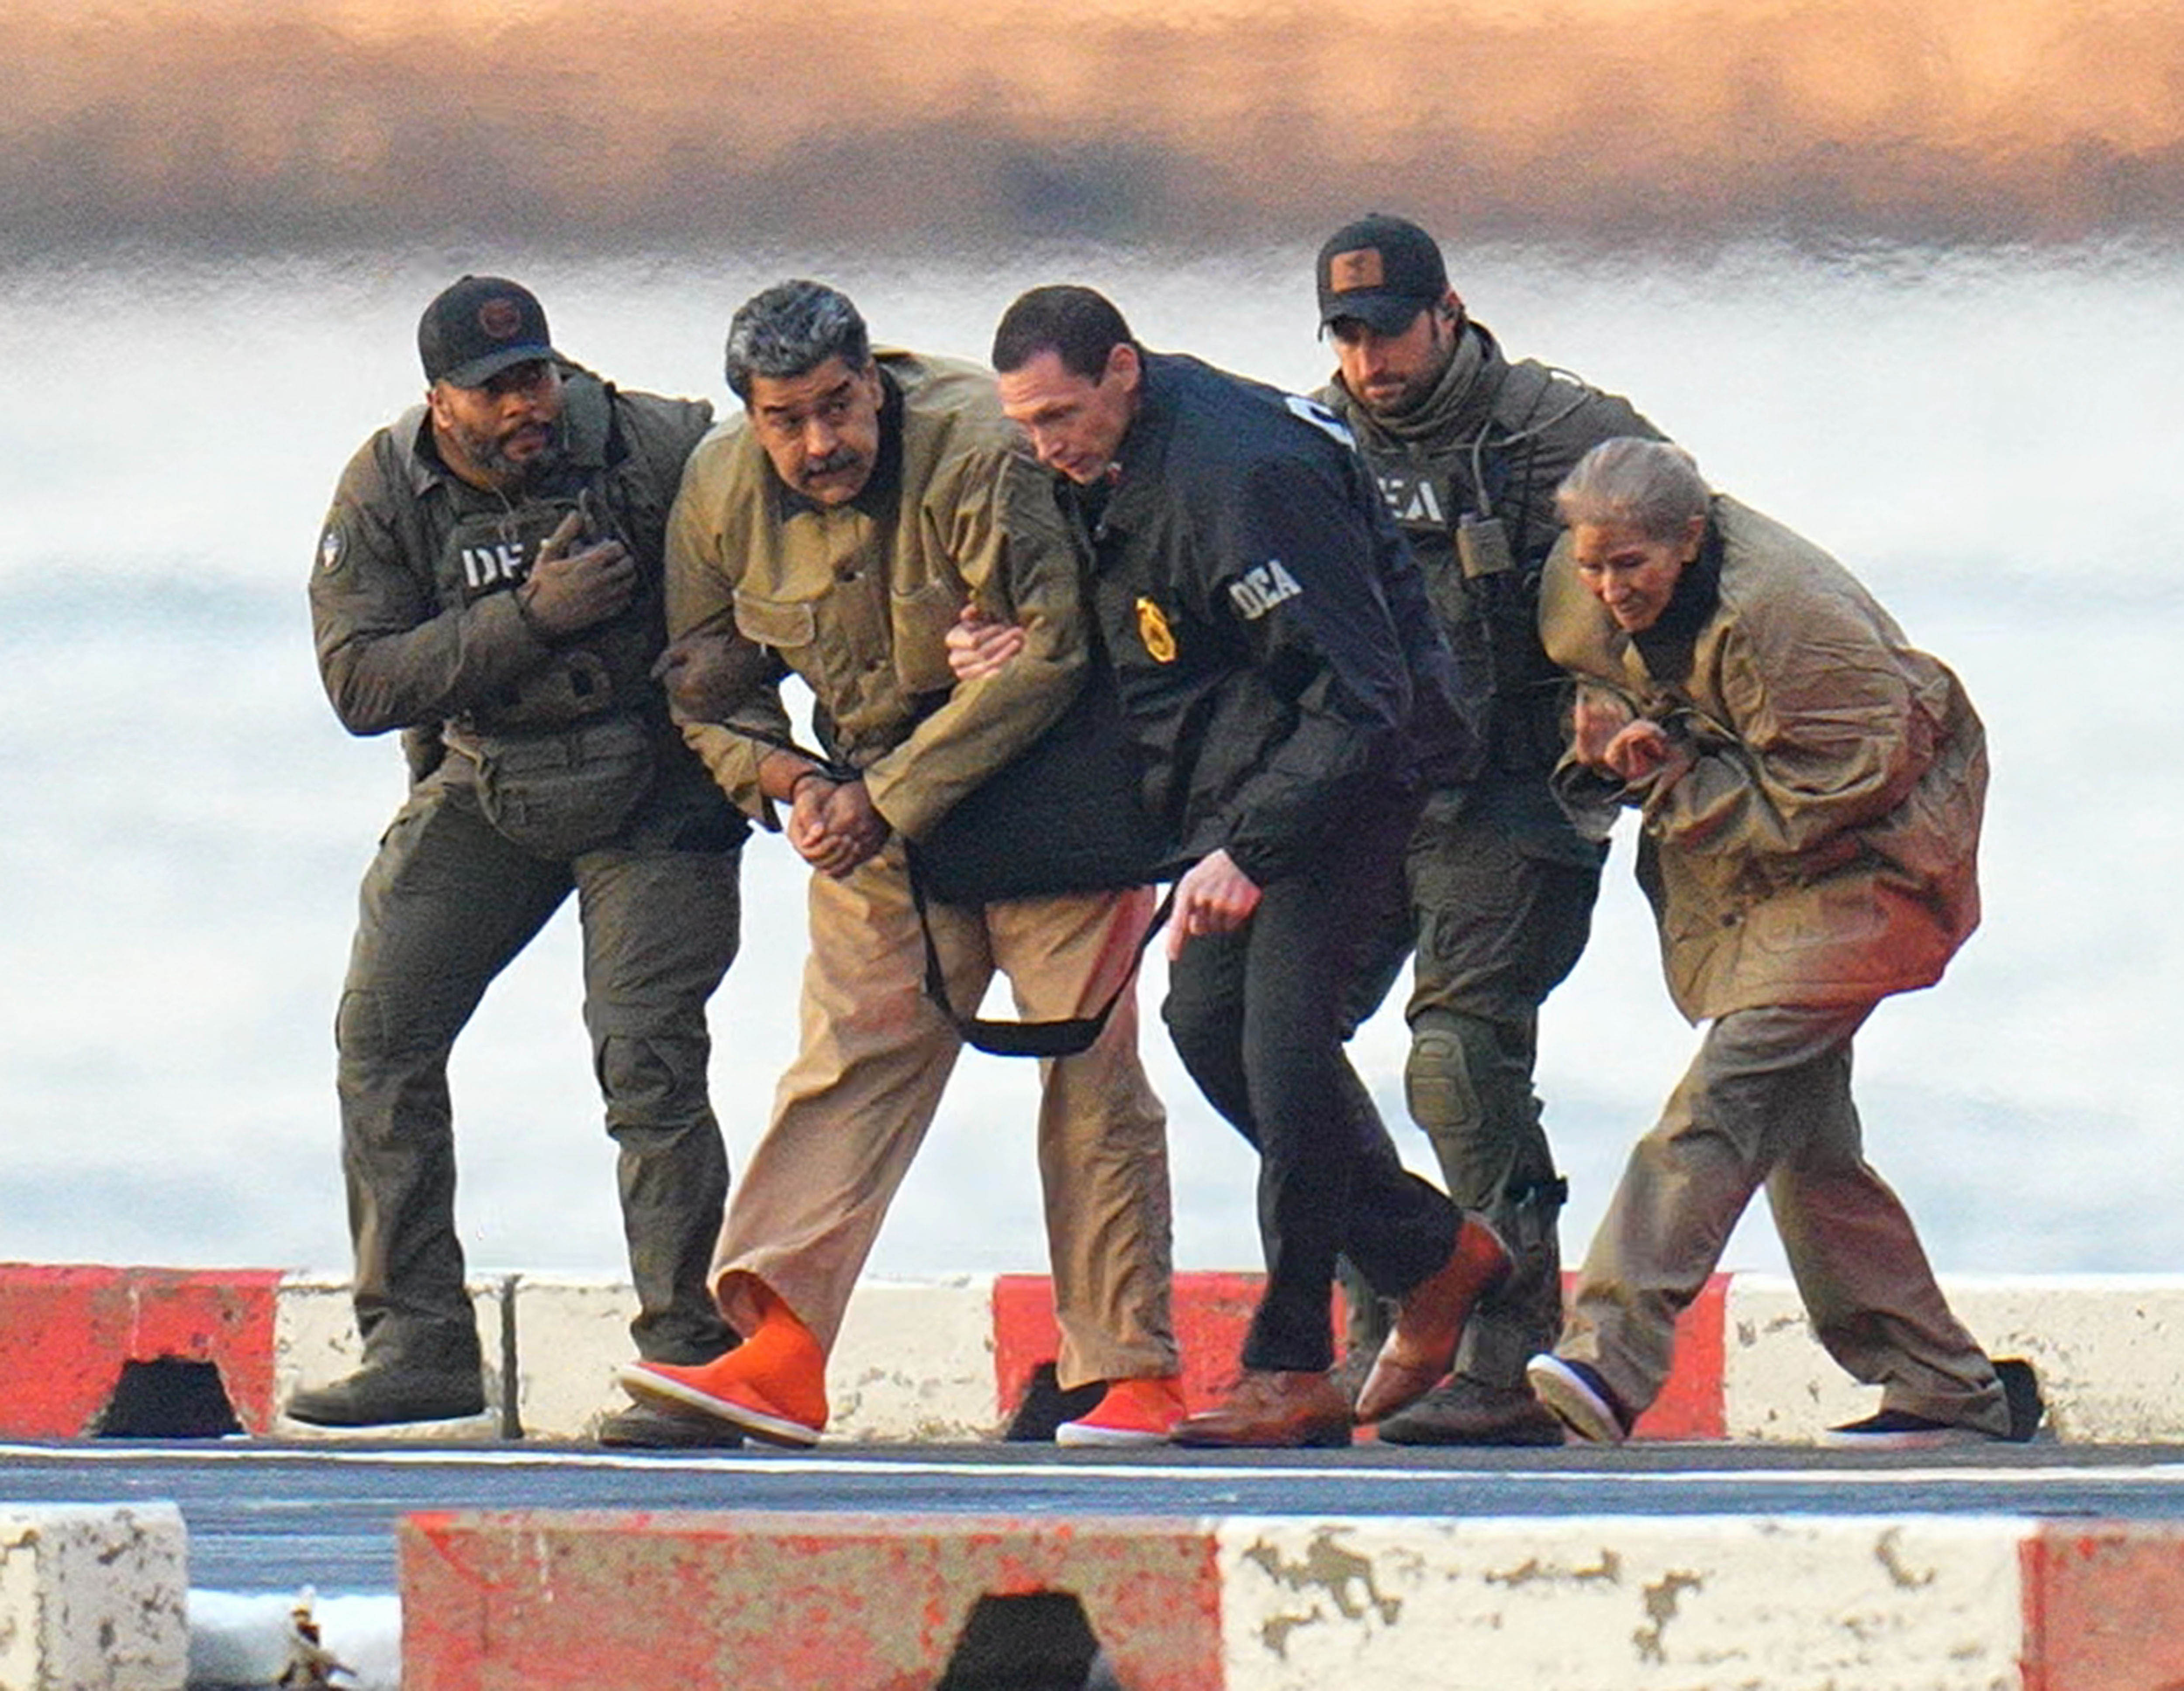
CIA Deputy Director Michael Ellis said Operation Absolute Resolve shows cyber operations are now central to intelligence collection and mission execution, helping U.S. forces locate and apprehend Nicolás Maduro. He also highlighted the CIA’s reorganization to elevate its Center for Cyber Intelligence and speed technology delivery through its new Directorate of Mission Systems. #CIA #OperationAbsoluteResolve #NicolásMaduro #CenterforCyberIntelligence #JohnRatcliffe