
Cybercriminals have published stolen data from Qantas and other major companies following a cyberattack in July, despite legal actions to prevent access. The breach exposed personal information of millions of customers, prompting ongoing investigations and advisories. #LAPSUS$ #Qantas #VietnamAirlines #Salesforce…
Category: Cyber Security News
Taiwan’s national security agencies warn of increased Chinese cyberattacks and disinformation campaigns aimed at destabilizing the Taiwanese government and public trust. The campaign involves sophisticated influence operations using AI-generated content and a coordinated effort by China’s military and intelligence agencies. #ChinaCyberattacks #DisinformationCampaigns…
California’s new online safety legislation introduces mandatory age checks for app downloads and chatbot safety measures to protect children. These laws aim to balance technological innovation with user privacy and child protection, contrasting with more invasive age verification laws elsewhere. #DigitalAgeAssurance #ChatbotSafety…
SAP has released 16 security patches addressing critical vulnerabilities across its enterprise software lineup, including severe flaws like insecure deserialization and directory traversal. While no exploits have been reported, timely patch application is crucial to prevent potential attacks by threat actors targeting SAP systems. #SAP #NetWeaver #CVEs #SecurityPatches…
LevelBlue, a major managed security service provider, has acquired cybersecurity firm Cybereason to enhance its security offerings. This acquisition integrates Cybereason’s XDR and DFIR capabilities into LevelBlue’s portfolio, strengthening their market position. #Cybereason #XDR #CybersecurityMergers…

HyperBunker has secured seed funding of nearly $925,000 to develop its innovative anti-ransomware device that goes beyond traditional data backup methods. The device offers a secure, immutable, and air-gapped solution focused on data recovery, addressing the increasing ransomware threats faced by businesses worldwide. #HyperBunker #RansomwareProtection…

A managed security provider detected widespread credential attacks on SonicWall SSLVPN devices, with over 100 accounts compromised across multiple customer environments. The attacks involved rapid authenticating attempts using valid credentials, and are possibly unrelated to the recent SonicWall backup breach. #SonicWall #SSLVPN #CredentialTheft…
Chinese state hackers exploited a component in ArcGIS GIS software to remain undetected for over a year, using a web shell to access internal networks. They extended their malicious activities by deploying SoftEther VPN to maintain persistence and conduct lateral movement within the compromised environments. #FlaxTyphoon #ArcGIS #SoftEtherVPN #RaptorTrain

Researchers have discovered a side-channel attack called Pixnapping that exploits Android APIs and GPU features to covertly steal 2FA codes and sensitive data from Google and Samsung devices. Google has released patches for the vulnerability, but some weaknesses like app installer bypass remain unpatched. #Pixnapping #AndroidVulnerability…

AMD has released security fixes for a flaw named RMPocalypse that compromises Secure Encrypted Virtualization with Secure Nested Paging (SEV-SNP). This vulnerability allows remote attackers to bypass confidentiality and integrity protections by manipulating the RMP table, affecting several AMD EPYC processor series. #RMPocalypse #SEV-SNP #AMDProcessors #EPYC #Vulnerability…

Security Awareness Month emphasizes the importance of proactive measures alongside traditional training to strengthen cybersecurity defenses. Threat hunting and continuous validation are essential to address vulnerabilities that awareness alone cannot fix. #CyberDefenseMatrix #ProactiveThreatHunting…
AI systems embedded in critical sectors pose ethical, transparency, and governance challenges, requiring careful oversight to maintain fairness, accountability, and public trust. Effective AI governance involves balancing openness, bias mitigation, data privacy, human rights, and environmental sustainability to ensure responsible deployment. #AIRegulation #Fairness #DataPrivacy #EnvironmentalImpact…
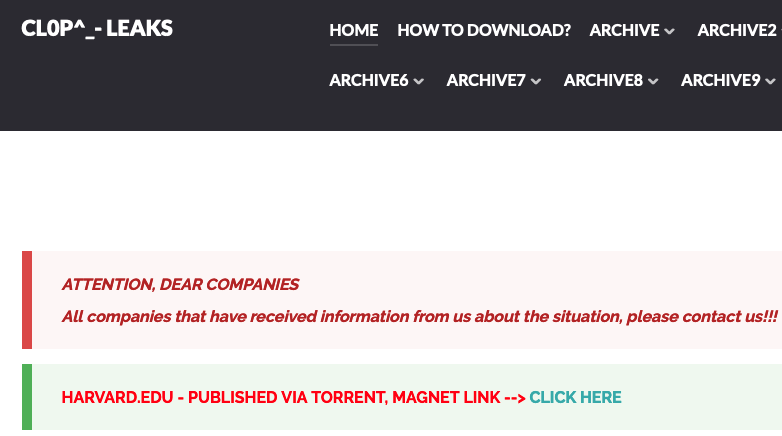
Harvard University was victimized in a cyberattack exploiting Oracle E-Business Suite vulnerabilities, with over 1.3 TB of data allegedly stolen and leaked. The attack is linked to the Cl0p ransomware group and involves sophisticated malware, with multiple organizations targeted. #Cl0p #FIN11…
Resistant AI has secured $25 million in Series B funding to enhance its fraud detection and transaction monitoring technology, addressing the rising threats posed by generative AI and large language models. The company’s solutions help detect sophisticated financial crimes such as money laundering, synthetic identities, and document fraud, serving major financial…
A significant security vulnerability has been discovered in Happy DOM, a popular JavaScript library, which allows attackers to escape the VM sandbox and execute arbitrary code. This flaw affects millions of applications using Happy DOM versions 19 and earlier, especially in server-side rendering and testing environments. #HappyDOM #CVE-2025-61927…