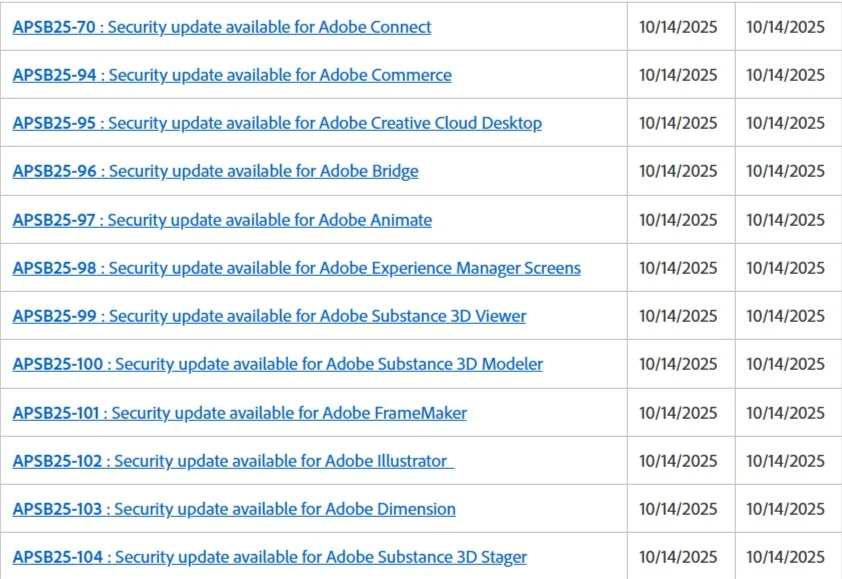
Adobe has released security updates fixing over 35 vulnerabilities across its suite of products, including Adobe Connect, Creative Cloud, and Magento. These patches address critical issues such as cross-site scripting, open redirects, and privilege escalation, urging users to update promptly. #AdobeConnect #MagentoOpenSource…
Category: Cyber Security News
Michigan City, Indiana, experienced a ransomware attack that affected its government systems, data, and communication channels. The Obscura ransomware gang claimed responsibility and stole 450GB of data, prompting a forensic investigation and active law enforcement involvement. #ObscuraRansomware #MichiganCity…

Daily Recap, A new 8-byte write called RMPocalypse targets AMD SEV-SNP and an array of exploits including CVE-2025-61927 and a CL0P-linked Oracle EBS zero-day affecting Harvard, while threats persist across NTDS.dit credential harvesting and geo-mapping persistence. Threat actors also exploit SonicWall VPNs, mass RDP botnets target the US, and a UK rise in nationally significant attacks highlights evolving risk in critical infrastructure #RMPocalypse #CVE-2025-61927 #NTDSdit #OracleEBS #Harvard #SonicWall #RDPBotnet #UKAttacks
Microsoft’s October 2025 Patch Tuesday addresses 172 security flaws, including six zero-day vulnerabilities, with a focus on critical remote code execution and privilege escalation issues. This update also marks the end of support for Windows 10, with users encouraged to adopt Extended Security Updates for continued protection. #Windows10 #ZeroDayVulnerabilities
Microsoft announces that Exchange Server 2016 and 2019 have reached the end of support, urging users to upgrade or migrate to Exchange Online or Exchange Server SE to maintain security. Continuing to use these outdated servers past October 14, 2025, poses significant security risks, as Microsoft will cease updates and support. #ExchangeServer2016 #ExchangeServer2019 #ExchangeOnline
A new side-channel attack called Pixnapping allows unprivileged Android apps to extract sensitive visual data, including 2FA codes and private messages, by exploiting graphical rendering processes. Despite recent patches from Google, the attack demonstrates ongoing vulnerabilities in modern Android devices, impacting various apps and systems. #Pixnapping #AndroidSecurity
Microsoft has released the final Windows 10 KB5066791 update, marking the end of support for the operating system, with extended security options available for a limited time. This mandatory update includes critical security patches, fixes for various issues, and updates Windows 10 to new build versions. #Windows10 #KB5066791
Threat actor TigerJack actively distributes malicious VSCode extensions on both Microsoft’s marketplace and OpenVSX, targeting developers to steal cryptocurrencies and install backdoors. Despite some extensions being removed from VSCode, they remain available on OpenVSX, posing ongoing risks to coding environments. #TigerJack #OpenVSX #VSCodeExtensions #CryptocurrencyTheft
Microsoft released patches for 175 vulnerabilities during October 2025, including three zero-day exploits actively under attack. Notable issues involve privilege escalation in Windows components and Secure Boot bypasses, with some updates marking the final support for Windows 10. #CVE2025-59230 #CVE2025-24990 #CVE2025-47827…
FuzzingLabs has accused Gecko Security of copying its vulnerability disclosures, including PoCs and re-submitting CVEs, and backdating blog posts to appear older. Gecko denies wrongdoing, attributing the overlaps to misunderstandings and coordination issues, while the cybersecurity community questions the claims. #FuzzingLabs #GeckoSecurity #CVEs #VulnerabilityDisclosure
Microsoft has announced the end of support for Windows 10, urging users to upgrade to Windows 11 or migrate to Windows 365 to stay protected. Despite continued use being possible, outdated systems remain vulnerable to security threats. #Windows10EndOfSupport #Windows11Upgrade
Oracle has released security patches for critical vulnerabilities in its E-Business Suite, which were actively exploited by threat groups like Clop and ShinyHunters. Despite these updates, confusion remains over the specifics of the exploits, vulnerabilities, and their remediation. #CVE-2025-61884 #ShinyHunters #Clop #OracleEBS #ZeroDayExploit
The U.S. Department of Justice has confiscated $15 billion in Bitcoin from the Prince Group, a criminal organization involved in elaborate cryptocurrency scams and forced labor camps. The case highlights the widespread impact of Southeast Asia-based scam operations and extensive money laundering techniques. #PrinceGroup #ChenZhi
Microsoft has released the October 2025 Patch Tuesday updates for Windows 11 versions 25H2, 24H2, and 23H2, addressing security vulnerabilities and bugs. These updates include enhancements for browsing, gaming, PowerShell, Windows Hello, and new AI features in File Explorer. #Windows11 #PatchTuesday

A Chinese state-sponsored hacking group, Flax Typhoon, compromised an ArcGIS system by turning it into a backdoor for over a year, leveraging legitimate tools for malicious purposes. The attack demonstrates advanced techniques like embedding a web shell, establishing covert VPN channels, and maintaining persistent access, highlighting the evolving threat landscape. #FlaxTyphoon…