
This article discusses the importance of understanding Active Directory attack techniques, especially the targeting of the NTDS.dit file, which contains critical domain data. It highlights the stealthy methods cybercriminals use to steal identity information and emphasizes the need for advanced detection tools. #ActiveDirectory #NTDSdit…
Category: Cyber Security News

Microsoft has ended support for Windows 10, exposing its vast user base to security vulnerabilities and cyber threats. Upgrading to Windows 11 or employing other security measures is crucial to remain protected. #Windows10EndOfSupport #CyberThreats #Windows11Upgrade…

Daily Recap, Australia launches CI Fortify program to bolster critical infrastructure security, and Oracle issues an emergency E-Business Suite patch tied to high-severity vulnerabilities and alleged Cl0p-style activity affecting Harvard. The week also highlights the RondoDox botnet, ChaosBot’s Discord-based C2, and Astaroth abusing GitHub for persistence, underscoring ongoing extortion and supply-chain concerns.
#CIFortify #RondoDox #ChaosBot #Astaroth #Harvard #Cl0p #Salesforce #Unity #TwoNet
SimonMed Imaging, a U.S. medical imaging provider, experienced a data breach exposing sensitive information of over 1.2 million individuals due to a cyberattack involving Medusa ransomware. The breach included potentially highly sensitive personal and medical data, and the company may have negotiated a ransom payment to hackers. #MedusaRansomware #SimonMedImaging
Microsoft is restricting access to Internet Explorer mode in the Edge browser due to zero-day exploits in the Chakra JavaScript engine used by threat actors. These exploits allowed hackers to gain remote code execution and full device control, prompting Microsoft to implement more strict controls. #ChakraZeroDay #IEModeSecurity

Last year, the UK experienced a record number of “nationally significant” cyberattacks, with over 200 incidents considered highly significant. The government is urging businesses to prioritize cyber resilience to combat increasingly sophisticated threats, emphasizing the impact on national security and economic stability. #UKCyberattacks #NCSC #JaguarLandRover #CyberResilience #NationalSecurity…
Microsoft is actively investigating a service disruption affecting some users’ access to Microsoft 365 applications. This incident follows recent outages involving Microsoft Teams, Exchange Online, and other services, highlighting ongoing infrastructure issues. #Microsoft365 #AzureFrontDoor
Researchers report a large-scale attack compromising over 100 SonicWall SSLVPN accounts using stolen credentials. The campaign involves network scanning and lateral movement, highlighting the importance of immediate security measures. #SonicWall #SSLVPN
A large-scale multi-country botnet is actively targeting Remote Desktop Protocol (RDP) services in the United States, exploiting vulnerabilities through specialized timing and enumeration attacks. Researchers recommend blocking attacking IPs and enhancing RDP security measures like VPNs and multi-factor authentication. #RDP #GreyNoise

The Netherlands has invoked exceptional government powers to oversee Nexperia, a Chinese-owned semiconductor firm, citing serious governance issues threatening technological knowledge. The move highlights concerns over Chinese espionage, intellectual property theft, and national security risks in the global semiconductor industry. #Nexperia #ChineseEspionage…
Ukraine is advancing its military cyber capabilities by proposing a dedicated Cyber Force under the Armed Forces, aiming to enhance offensive and defensive operations. This move aligns Ukraine’s cyber defense more closely with NATO standards and includes establishing a cyber reserve of civilian experts. #UkraineCyberForce #NATOstandards…
Harvard University was affected by a cyber campaign exploiting a zero-day vulnerability in Oracle’s E-Business Suite, leading to potential data theft. The attack, linked to the Clop ransomware group and tracked as CVE-2025-61882, highlights the risks of vulnerabilities in critical enterprise systems. #CVE-2025-61882 #Clop #OracleEBS #HarvardUniversity…

Born Defense is a new cybersecurity-focused investment issuer that supports national security efforts within the framework of the Just War Doctrine. It aims to enhance defenses against the ongoing global cyber conflict by backing companies and organizations engaged in cyber deterrence and defense. #JustWar #BornDefense…
JPMorgan Chase announced a $10 billion direct investment in U.S. companies vital to national security, focusing on critical industries like advanced manufacturing and strategic technologies. This initiative is part of a broader $1.5 trillion, 10-year plan to bolster America’s economic resilience and reduce dependence on unreliable global sources. #MPMaterials #NationalSecurityInvestments…
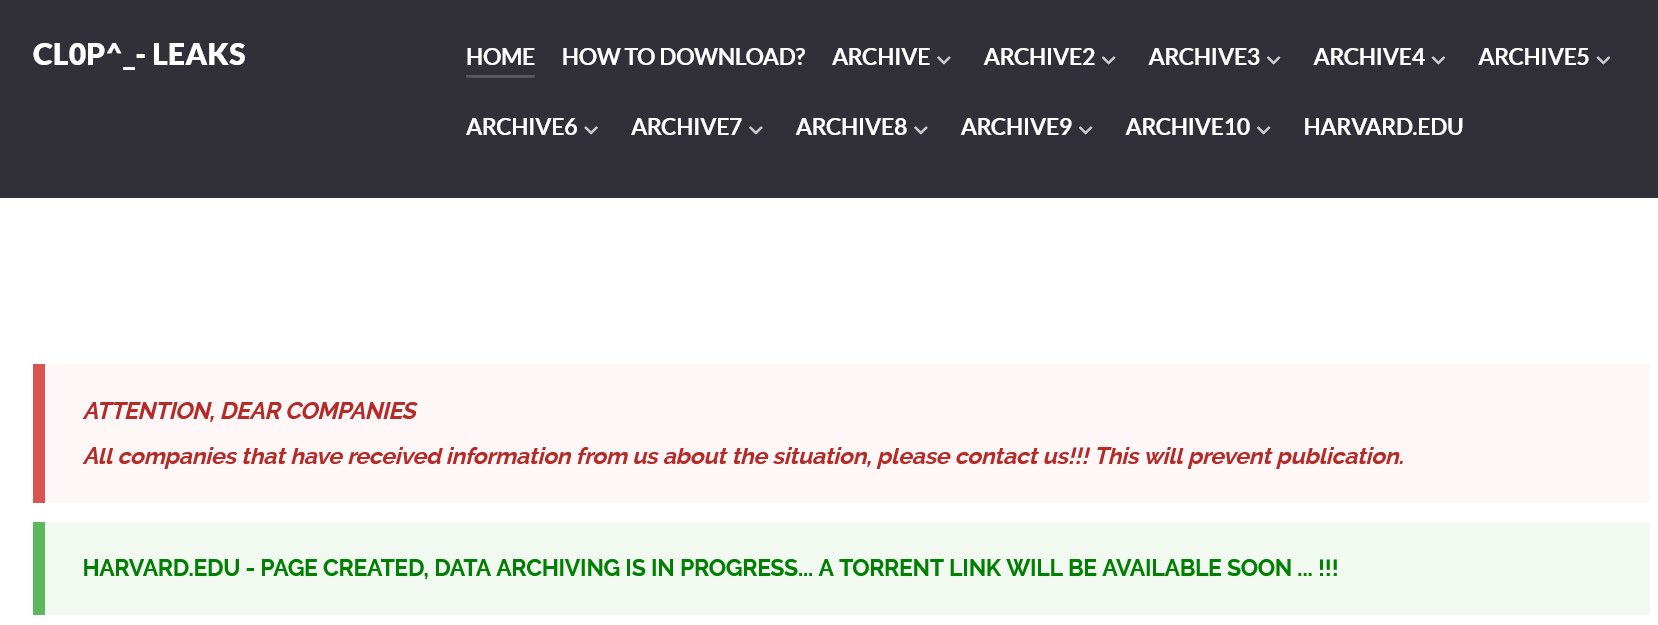
A new high-severity vulnerability (CVE-2025-61884) in Oracle E-Business Suite allows remote, unauthenticated access to critical data. This follows a previous exploit of CVE-2025-61882 by the CL0P ransomware gang, targeting vulnerabilities in Oracle systems. #CVE202561884 #CL0PRansomware #Harvard…