
India’s cybersecurity industry has grown into a $20 billion sector with over 400 startups and 650,000 professionals, driven by government and private sector initiatives. CERT-In plays a vital role in managing cyber threats, utilizing AI and automation to enhance national cyber resilience. #CERTIn #AI #IndiaCybersecurity…
Category: Cyber Security News
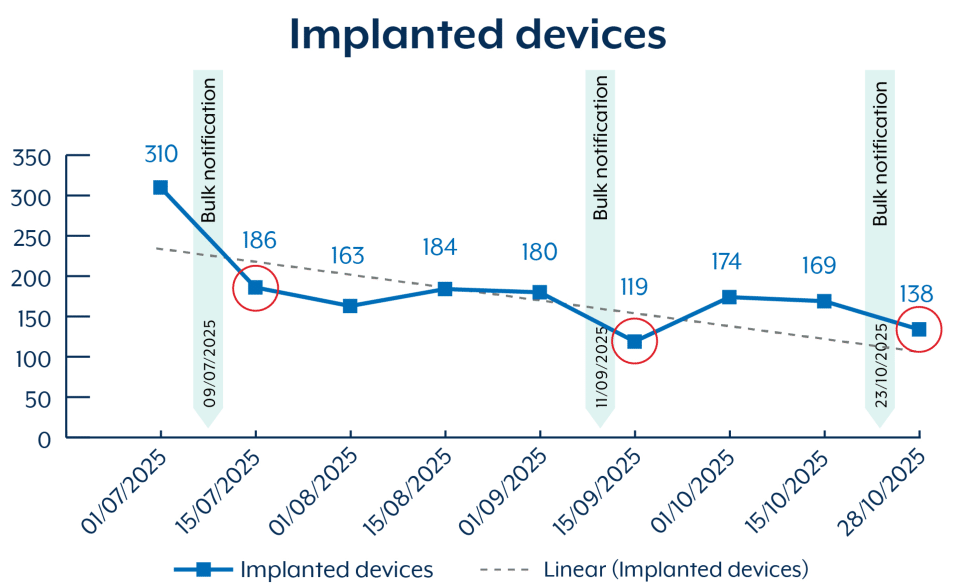
The Australian cyber agency warns that over 150 devices remain compromised with the BadCandy implant, two years after patches were released. This highlights the ongoing challenge of patch management and vulnerability re-exploitation in network edge devices. #BadCandy #CVE-2023-20198 #CiscoIOSXE…
Russian authorities have arrested a group of young IT specialists for creating and distributing the Meduza Infostealer malware, highlighting ongoing efforts to combat domestic cyber threats. The malware, which targets sensitive data and cryptocurrency wallets, was used in recent breaches, and the arrests may impact the underground infostealer market. #MeduzaInfostealer #CyberThreatActors

ThreatLocker’s new DAC for macOS helps organizations identify and fix configuration vulnerabilities before they are exploited. This tool enhances security visibility for Mac devices, making compliance easier across multiple security frameworks. #ThreatLocker #DACforMacOS…

A Chinese state-sponsored group, BRONZE BUTLER, has exploited a zero-day vulnerability (CVE-2025-61932) in Motex LANSCOPE Endpoint Manager to infiltrate corporate networks and steal sensitive information. The campaign features sophisticated malware variants like Gokcpdoor and deception techniques involving legitimate tools and cloud services. #BRONZEBUTLER #CVE202561932…

Peter Williams, a former U.S. defense contractor executive, pleaded guilty to stealing and selling sensitive cyber exploit components to Russian brokers, risking national security. This case highlights the dangers of insider threats in cybersecurity and the potential for stolen data to empower foreign cyber actors. #TradeSecretsTheft #RussianCyberBrokers…

Daily Recap, The latest security alerts cover a broad sweep of breaches, from a Vinomofo data protection ruling and a major Conduent breach to widespread misinformation around Gmail and a surge in NPM credential theft campaigns. The report also highlights tools and flaws enabling rapid credential harvesting, patching gaps, botnet attacks on PHP/IoT, AI misuse in executive-targeted campaigns, and notable industry moves like Reflectiz funding and Spektrum Labs’ market entry. #Vinomofo #Conduent #GmailHoax #WPPluginLeak #PhantomRaven #NPM #LoginsZip #Dovecot #TotalJS #Copilot #DNSOutage #Mirai #Gafgyt #Mozi #BlueNoroff #AICloking #MaliciousSEO #ThreatsDay #ExploitsSold #M&SImpact #Reflectiz #SpektrumLabs #Herodotus
A major data breach at Conduent has exposed the personal information of over 10.5 million individuals, primarily affecting the Oregon government. The incident was linked to a ransomware attack attributed to the Safepay gang and potentially impacts many more users nationwide. #SafepayRansomware #ConduentDataBreach

A new vulnerability called Brash affects Chromium-based browsers by exploiting DOM operations to crash or degrade performance. The flaw can be weaponized with precise timing and is present in browsers like Chrome, Edge, and Opera but does not affect Firefox or Safari. #BrashVulnerability #ChromiumEngine…

AdaptixC2 is an open-source command-and-control framework increasingly used by threat actors, including Russian-linked ransomware groups. While designed for penetration testing, its features have attracted cybercriminals, raising concerns about misuse. #AdaptixC2 #RansomwareGangs…

Google’s defenses on Android prevent over 10 billion malicious calls and messages each month and block more than 100 million suspicious numbers, showing robust protection against scams. The company also highlighted the evolving tactics of scammers, including group chats and scheduled messaging, as well as the most common scam types like…

The sharing of digital threat information between the U.S. government and industry continues steadily despite the expiration of the 2015 Cybersecurity Information Sharing Act. Key officials emphasize the importance of reauthorizing the law for long-term cybersecurity cooperation and risk management. #CybersecurityInformationSharing #CISA #CongressLegislation…
A Chinese hacking group, UNC6384, targeted Hungarian and Belgian diplomatic entities along with other European nations, utilizing spearphishing and exploiting recent Windows vulnerabilities to conduct cyber espionage. The campaign involved malware like PlugX and indicated a strategic focus on NATO, EU policies, and international diplomacy efforts. #UNC6384 #PlugX #MustangPanda #EuropeanDiplomacy #CyberEspionage…

Denmark’s justice minister has decided to abandon the push for an EU law mandating the scanning of encrypted messages to combat child abuse. The move marks a shift towards voluntary detection methods, emphasizing concerns over privacy and mass surveillance. #ChatControl #ChildProtection…

Symantec has uncovered complex cyber intrusions in Ukraine linked to Russian-affiliated threat actors, emphasizing the use of Living-off-the-Land techniques for stealthy operations. These campaigns involved minimal malware but demonstrated advanced knowledge of Windows tools for data theft and persistence. #Sandworm #LivingOffTheLand…