This roundup covers recent developments in cybersecurity, including international treaties, malware threats, and industry innovations. Key stories include the signing of the UN cybercrime treaty, surge in NFC relay malware, and new threat intelligence solutions from Mastercard. #UNCybercrimeTreaty #NFCRelayMalware #ClearviewAI #GhostGrab #Herodotus…
Category: Cyber Security News
The Federal Communications Commission (FCC) is planning to revoke a controversial 2025 ruling that aimed to impose comprehensive cybersecurity requirements on telecommunications carriers, shifting towards a voluntary industry collaboration model. This change comes amid recent Chinese-sponsored espionage attacks, like Salt Typhoon, which exposed vulnerabilities in U.S. networks. #SaltTyphoon #FCC #CALEAReinterpretation #CybersecurityPolicy…
A Ukrainian national linked to the Conti ransomware group has been extradited to the U.S. and faces serious charges for controlling stolen data and orchestrating cyber extortion. The Conti operation, responsible for over 1,000 attacks worldwide, has evolved into smaller groups since its shutdown, continuing to threaten critical infrastructure and organizations. #Conti #TrickBot
This alert raises awareness about recent cyber threats targeting internet-connected Industrial Control Systems (ICS) in Canada, affecting critical infrastructure such as water facilities, oil and gas companies, and farms. It emphasizes the importance of comprehensive security measures, collaboration, and timely reporting to law enforcement. #ICS #CriticalInfrastructure #CyberCentre #RCMP #Canada…
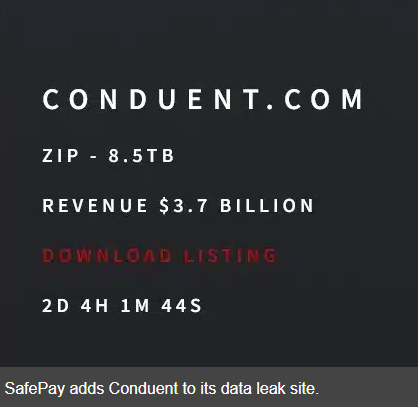
The Conduent data breach has affected over 10.5 million people across several US states, compromising sensitive personal information. The ransomware group SafePay claimed responsibility, highlighting the increasing threat of cyber extortion targeting government-related systems. #SafePay #ConduentBreach…
Hacktivists have targeted Canadian industrial control systems to cause disruptions and generate media attention, rather than for financial gain. These opportunistic attacks have affected critical infrastructure such as water facilities, oil companies, and farms, highlighting vulnerabilities in operational technology. #CanadianCyberSecurity #IndustrialControlSystems…
Docker Compose has a critical path traversal vulnerability (CVE-2025-62725) that allows attackers to write arbitrary files on the host system, urging users to upgrade to version 2.40.2. Additionally, Docker fixed a DLL hijacking flaw in its Windows Installer, emphasizing the importance of timely updates for Docker security. #DockerCompose #CVE202562725 #DockerDesktop #DLLHijacking…

CISA, NSA, and international partners have issued a guide to improve the security of Microsoft Exchange Server and prevent exploitation. Organizations are advised to follow best practices, especially decommissioning outdated servers, to reduce cyber threat risks. #MicrosoftExchange #CISA #NSA #ExchangeServerSecurity…

A high-severity vulnerability (CVE-2025-41244) affecting Broadcom VMware Tools and VMware Aria Operations has been added to CISA’s KEV list due to active exploitation by Chinese-linked threat actors. This flaw allows privilege escalation to root, posing significant risks to affected virtual machine environments. #CVE202541244 #UNC5174…

Open VSX and Microsoft have taken action to address leaked access tokens in Visual Studio Code extensions, reducing the risk of malicious activity. These steps include revoking leaked tokens, introducing new security measures, and removing malicious extensions linked to the GlassWorm campaign. #OpenVSX #VisualStudioCodeExtensions…

U.S. and international cybersecurity agencies have issued guidance to strengthen on-premise Microsoft Exchange Servers against ongoing exploitation threats, emphasizing best practices such as multi-factor authentication and patch management. Recent vulnerabilities like CVE-2025-59287 in Windows Server Update Services have been exploited by threat actors to steal data, urging organizations to prioritize system…
A Chinese threat group known as UNC6384 has been exploiting a Windows shortcut vulnerability (CVE-2025-9491) to target European diplomatic entities with spear-phishing campaigns. This attack leverages malicious LNK files to deliver the PlugX RAT, enabling remote access and control. #UNC6384 #PlugX #CVE-2025-9491 #MustangPanda #EuropeanDiplomats…
Private equity firm Francisco Partners plans to acquire Apple device management company Jamf for $2.2 billion, aiming to become a private entity by early 2026. This acquisition emphasizes ongoing consolidation in the cybersecurity and device management sector, with Jamf continuing operations under its existing leadership. #Jamf #FranciscoPartners…
The US CISA has expanded its KEV catalog to include vulnerabilities in XWiki and VMware, both actively exploited in the wild. These flaws pose significant risks, allowing remote code execution and privilege escalation, with threat actors already targeting them. #XWikiCVEs #VMwareThreats…
The Middle East Cybersecurity Market is rapidly expanding, driven by increased digital transformation, cyber threats, and government initiatives. The market is expected to double in size by 2030, with significant investments in cloud security, AI, and national resilience strategies. #MiddleEastCybersecurity #GCC #SaudiVision2030 #UAEVision2021…