Canadian cybersecurity officials warn of increasing hacktivist attacks on critical infrastructure, including water, energy, and agriculture sectors. Russia-linked hacktivists, particularly since the fall of 2024, have been prominent in targeting internet-accessible ICS devices to discredit organizations and undermine Canada’s reputation. #Z-Pentest #ICSgaps…
Category: Cyber Security News
A security researcher has documented an iOS exploit chain related to CVE-2025-24085 and CVE-2025-24201, sharing details through a GitHub repository. The attack was analyzed via log analysis, but the technical report on the attack chain has become inaccessible, indicating possible takedown or platform issues. #CVEs #iOSExploit…
Jenkins has issued a security advisory addressing vulnerabilities in multiple plugins across their platform. Users are urged to review the updates and apply patches to mitigate potential threats. #Jenkins #SecurityVulnerabilities…
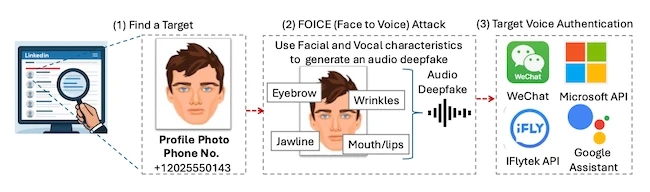
A new face-to-voice deepfake technique, FOICE, can generate convincing speech from photos, challenging existing detection methods. This innovation has significant implications for voice authentication systems, exposing vulnerabilities and highlighting the need for broader, more adaptable detection strategies. #FOICE #FaceToVoiceDeepfake…
A nation-state cyberattack compromised Ribbon Communications’ IT network, potentially affecting multiple government and telecom clients. The breach, linked in pattern to China’s Salt Typhoon group, highlights ongoing threats to critical infrastructure. #SaltTyphoon #TelecomBreaches
CISA has issued a warning to U.S. government agencies to patch a critical vulnerability in Broadcom’s VMware Aria Operations and VMware Tools software, actively exploited by Chinese state-sponsored hackers. The vulnerability, CVE-2025-41244, allows privilege escalation to root and has been exploited in the wild since October 2024, highlighting the importance of timely patching and mitigation. #CISA #UNC5174 #CVE202541244 #VMwareAdvisory
NFC relay malware infects Android devices predominantly in Eastern Europe, hijacking contactless payment data and emulating EMV fields to authorize transactions fraudulently. Over 760 malicious apps are currently exploiting this technique, highlighting its rapid growth and widespread impact. #NFCRelayMalware #AndroidThreats
Microsoft 365 is expanding its Copilot features to more companion apps, including the upcoming addition of Calendar. However, these features are exclusively available for enterprise or business users, enhancing productivity with AI-powered suggestions across various apps. #Microsoft365 #Copilot #EnterpriseApps

Cybersecurity researchers have uncovered a sophisticated supply chain attack targeting the npm registry with over 100 malicious packages, named PhantomRaven, designed to steal sensitive developer information. This attack exploits hidden dependencies and AI-generated package names to bypass security measures. #PhantomRaven #npmsecurity…

Cybercriminals and nation-state actors are increasingly targeting high-impact areas such as government, energy, and financial sectors using sophisticated methods like phishing, malware, and supply chain attacks. Ongoing developments include new malware like Atroposia RAT and critical vulnerabilities like BIND9 flaw, highlighting the importance of proactive cybersecurity measures. #HijackLoader #PureHVNC #OperationZero #CVE2025-40778…

This article emphasizes the importance of continuous proof-based testing in cybersecurity over traditional predictions or compliance checks. It highlights how Breach and Simulation (BAS) has evolved into a daily security practice, providing real-time validation of defenses and enabling faster, evidence-backed responses to threats. #PicusBAS #ThreatSimulation…

British retailers experienced varied impacts from recent cyberattacks, with Next benefiting from competitor disruptions and M&S suffering profits losses. The JLR cyberattack caused significant economic damage, highlighting the need for improved cybersecurity laws in the UK. #MarksAndSpencer #JaguarLandRover #CyberLegalReform…

Canada’s cyber authorities warn that hacktivists are increasingly attacking industrial systems, disrupting utilities and businesses. These incidents highlight the risks of poorly secured ICS components and follow a global rise in hacktivist activity targeting critical infrastructure. #CanadaCyberSecurity #Hacktivists…

A coalition of advocacy groups is urging the FTC to block Meta’s plan to use user conversations with AI chatbots for targeted advertising without opt-in consent. The groups argue that Meta’s approach violates laws against unfair and deceptive practices, raising concerns about privacy and children’s safety. #Meta #FTC #COPPA #AIchatbots #privacyabuses…
Conduent’s January 2025 data breach resulted in the theft of personal information from millions of individuals, affecting multiple US states and several sectors. The breach, claimed by the Safepay ransomware group, highlights ongoing risks to government and corporate data security. #Safepay #Conduent #DataBreach #Ransomware…