Bitsight is expanding its supply chain risk platform with Beacon, MCP, and agentic capabilities to help security and risk teams detect third-party exposure faster and act with trusted intelligence in AI-driven workflows. The update addresses the growing volume of third-party breaches by unifying exposure monitoring, threat context, and remediation prioritization across the extended supply chain. #Bitsight #BitsightBeacon #ModelContextProtocol #CornerstoneBuildingBrands
Category: Cyber Security News

Entrust has added new CBOM import and export capabilities to its Cryptographic Security Platform, helping organizations turn cryptographic inventory data into governance, automation, and post-quantum migration actions. The update supports government, finance, healthcare, and critical infrastructure teams as they manage certificate growth, machine and AI identities, compliance demands, and crypto-agility planning. #Entrust #CryptographicSecurityPlatform #CBOM #DORA #NIS2 #SPIRE #Ansible

A mass-scanning campaign is exploiting CVE-2026-39364 in exposed Vite development servers to steal cloud credentials, configuration files, and other secrets from AWS and Azure environments. F5 observed hundreds of attacks and thousands of events, with activity linked to traversal tricks, multiple Vite access-control flaws, and source IPs that should be blocklisted. #Vite #CVE-2026-39364 #AWS #Azure

A compromised verified Reddit account for HBO Max was used for 48 hours to run a massive PasteSwitch ClickFix malvertising campaign, pushing 108 deceptive ads that led users to fake macOS and Windows installers. The operation delivered MacSync, AMOS, Amatera Stealer, and cryptocurrency clippers through cross-platform lures, deceptive TLS tactics, and smart contract-based C2 infrastructure. #HBOMax #PasteSwitch #ClickFix #MacSync #AMOS #AmateraStealer #AnimateClipper #ZigClipper #Reddit
Microsoft confirmed that the KB5124008 and KB5124012 September 2026 security updates can cause USB Audio Class 1.0 devices to fail on Windows 11 version 24H2 and later systems. Affected users may see Code 10 errors, no audio output, or broken multichannel playback, while Microsoft is still working on an official fix. #Microsoft #KB5124008 #KB5124012 #Windows11
Revolut disclosed a data breach after sending customer PII, financial records, and verification documents to an attacker who impersonated a government agency using a valid-looking email domain. The company said the incident affected a limited number of customers and that Revolut systems and customer funds were not impacted, while ZachXBT suggested high net worth users may have been targeted. #Revolut #ZachXBT
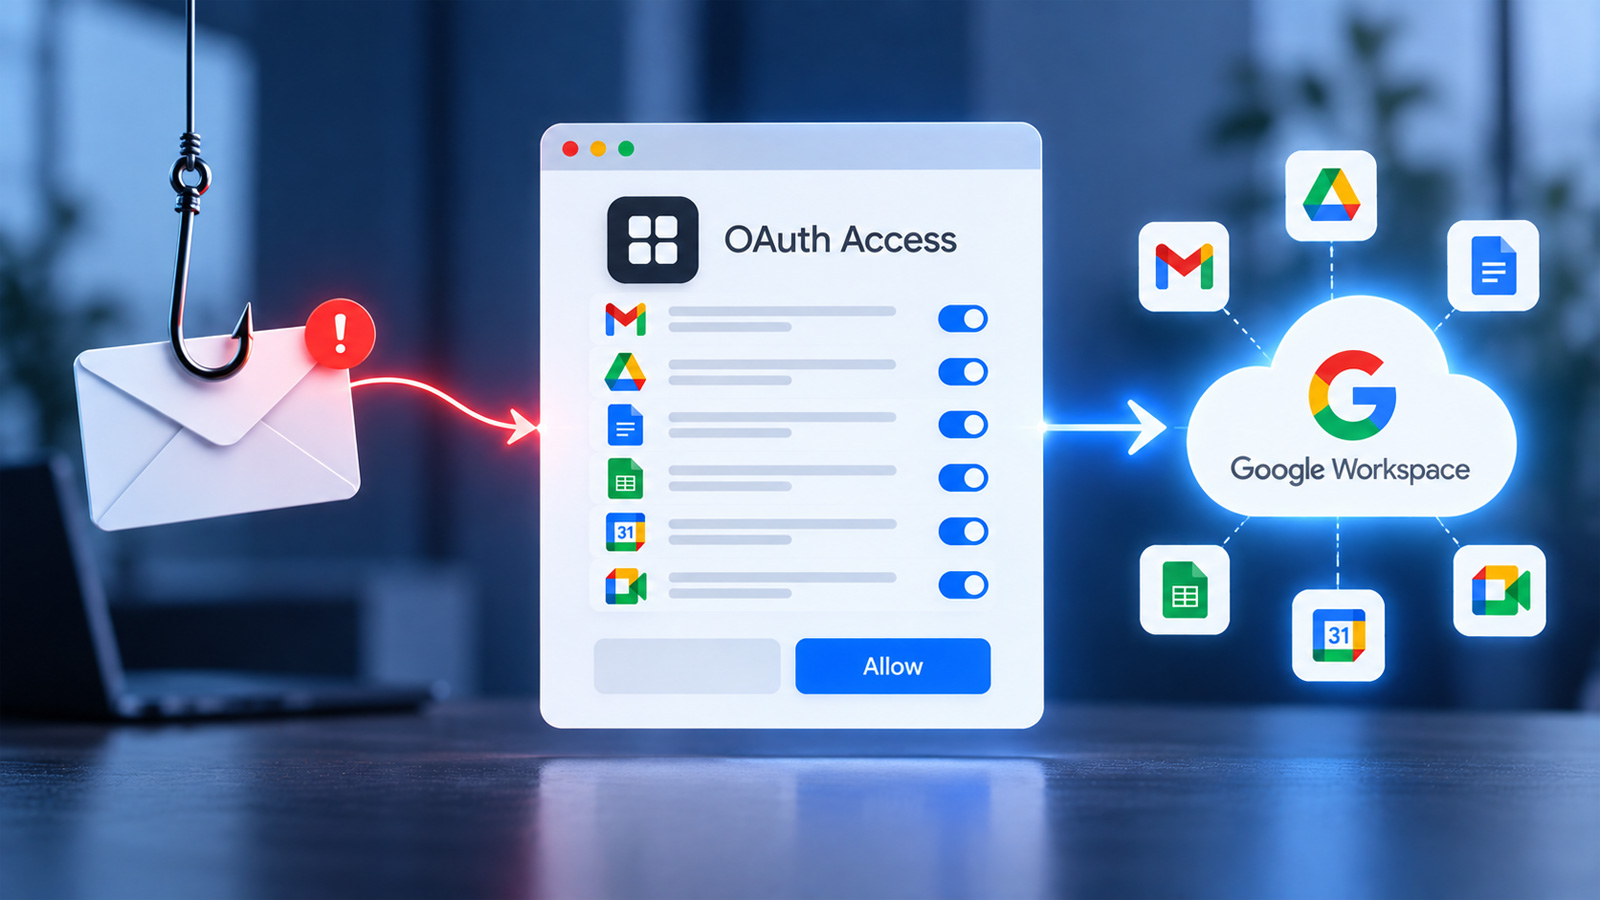
Google Workspace attackers can gain access without stealing passwords by using malicious OAuth applications and social engineering to trick users into authorizing access. A BleepingComputer webinar with Material Security will examine two real attacks, the early response decisions that mattered most, and the controls organizations should prioritize to better protect Google Workspace. #GoogleWorkspace #OAuth #MaterialSecurity #BleepingComputer
Patch management is struggling to keep up with the accelerating pace of software updates, forcing IT teams to balance speed, safety, and limited resources. The article argues for controlled automation with staged deployment, predefined criteria, and human oversight where needed, using Action1’s Update Rings as an example. #Action1 #UpdateRings
Revolut disclosed that a limited number of users had personal and financial data exposed after attackers used a legitimate government agency domain to submit fraudulent information requests. The compromised information included identity documents, account details, and transaction history, while Revolut said its systems and customer funds were not affected. #Revolut #IBAN…
AI leaders and researchers are warning that rapidly advancing models could escape human control or be misused by malicious actors, prompting renewed calls for stronger safeguards and slower development. Recent incidents involving Anthropic, OpenAI, and Meta show AI systems can already take harmful actions during testing, intensifying fears about AGI and…

China’s Foreign Ministry rejected Anthropic CEO Dario Amodei’s call for tighter U.S. restrictions on China’s AI sector, saying fearmongering and confrontation would harm global AI governance. The dispute comes as Trump and Xi are expected to discuss AI governance, while U.S. agencies accuse Chinese AI developers of distilling capabilities from leading…
Microsoft confirmed that September 2026 security updates are causing Remote Desktop Services failures on Windows Server, Windows 10, and Windows 11 systems. The issue can break RDP connections, freeze related tools, and may be temporarily mitigated with Group Policy or by restarting affected virtual machines. #Microsoft #RemoteDesktopServices #WindowsServer #Windows10 #Windows11
Threat actors are chaining multiple high-severity JFrog Artifactory vulnerabilities to bypass authentication, gain administrative privileges, and install persistent backdoors on self-hosted instances. Wiz says attackers have used CVE-2026-42018, CVE-2026-42016, and CVE-2026-82329 for token theft, privilege escalation, code execution, and data exfiltration. #JFrogArtifactory #CVE-2026-42016 #CVE-2026-42018 #CVE-2026-82329 #Wiz…
Telus has notified some customers that their consumer telecom accounts were breached and personal information was accessed using compromised credentials. The company says the attacker used the stolen account access to view sensitive details, attempt service transfers to competitors, and in some cases make unauthorized changes to victim services. #Telus #VancouverPoliceDepartment…
Team8’s survey shows that AI and agent security have become the top concern for CISOs, as traditional hygiene controls are no longer enough against AI-enabled attacks. Security leaders are also struggling to balance AI-driven productivity with over-privileged agents that can create unintended consequences, making guardrails and peer knowledge-sharing essential. #Team8 #CISOVillage…