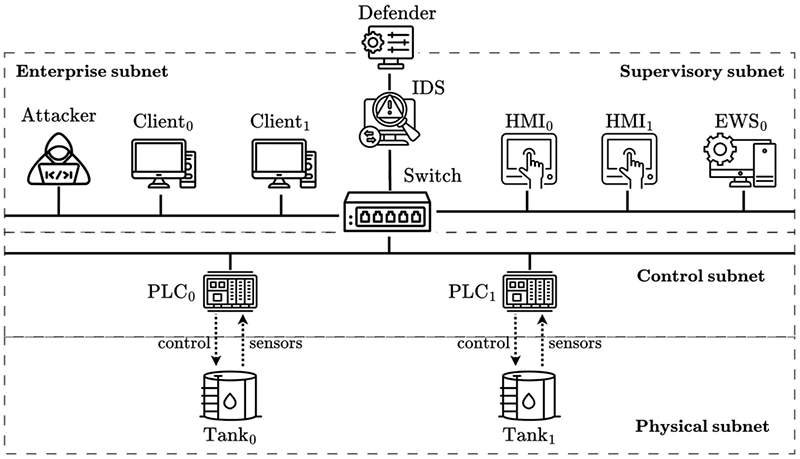
Researchers at KTH Royal Institute of Technology built a replica of a segmented industrial network, repeatedly attacked it, and used the captured traffic to train a defense agent that decides when to intervene. The study shows that packet-count-based belief tracking can help the agent infer intrusion progress and reset affected hosts or processes, while also highlighting limits in generalization and operational safety. #KTHRoyalInstituteofTechnology #CVE-2017-7494
Category: Cyber Security News
An impersonator using an email address on a government agency’s domain tricked Revolut into releasing sensitive customer records, including identity documents and other personal details. Revolut said only a limited number of customers were affected, blocked the sender, and notified authorities after the external impersonation scam was discovered. #Revolut #ZachXBT
Debian 13.7 “trixie” bundles 92 previously issued security advisories and fixes 106 source packages, including six Linux kernel advisories and major updates across glibc, qemu, imagemagick, wolfssl, perl, and cyrus-imapd. The point release also addresses issues in u-boot, sbsigntool, flask, dnsmasq, python3.13, bettercap, and onionshare, while updating the installer and kernel ABI to 6.12.107+deb13. #Debian13.7 #trixie #LinuxKernel #glibc #qemu #imagemagick #wolfssl #perl #cyrus-imapd #u-boot #sbsigntool #flask #dnsmasq #python3.13 #bettercap #onionshare
CISA warned that attackers are actively exploiting a maximum-severity GitLab flaw, CVE-2026-85706, which can let unauthenticated users read credentials and other sensitive data from vulnerable servers. GitLab has released fixes and CISA added the issue to its actively exploited catalog, urging organizations to patch immediately and hunt for signs of probing on affected systems. #GitLab #CVE-2026-85706 #CISA #watchTowr
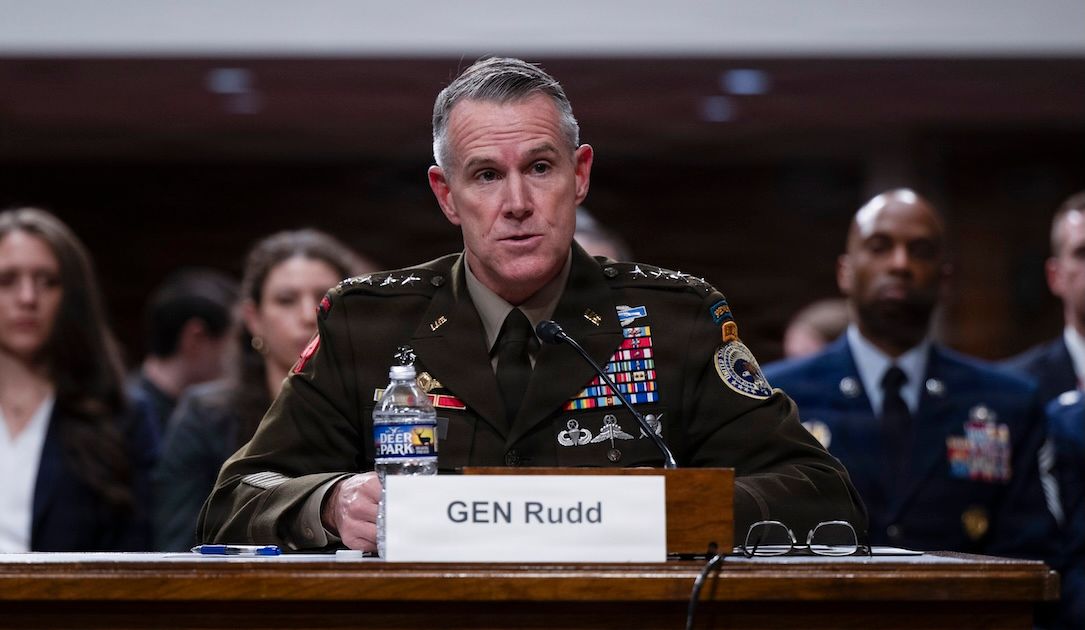
The National Security Agency is rapidly reorganizing into five mission centers focused on China, cybersecurity, artificial intelligence, combat support, and global intelligence to speed intelligence delivery to battlefield users. The overhaul, led by Gen. Joshua Rudd, is still being finalized and may affect groups such as Tailored Access Operations and the…

Cybersecurity Threat Research ‘Weekly’ Recap. This week’s coverage highlights credential-stealing and session-hijacking campaigns (BigBear 2.0, HVNC, Malicious Twitch extension, and Axiom Trade/Padre theft) alongside exploit chains that rapidly weaponize browser and platform vulnerabilities, including Marimo (CVE-2026-39987), GRAYRABBIT, and GRIMWEDGE/SUPERSTOMP/LONGTALE. Researchers also tracked emerging threats and abuse patterns such as SloppyRAT, ClearFake/WebDAV delivering Amatera/ZigCryptoStealer/NetSupport Manager, chat-based data leakage via a ChatGPT shared clipboard flaw, and AI manipulation efforts like PuzzleMask and adversarial agentic workflows. #BigBear2_0 #Evilginx2 #HVNC #Twitch #JeetBot #AxiomTrade #Padre #Marimo #CVE-2026-39987 #GRAYRABBIT #GRIMWEDGE #SUPERSTOMP #LONGTALE #BlueMoon #GemStone #ShadowPad #SloppyRAT #ClearFake #Amatera #ZigCryptoStealer #NetSupportManager #EtherHiding #SourTrade #CL-CRI-1171 #MantaxOtax #MacSync #Syslogk #ChatGPT #PuzzleMask #LockBit #Cl0p #Akira #Medusa #Qilin

Daily Recap, AI abuse escalated as attackers leveraged Anthropic’s Claude for large-scale distillation and automation, while OpenAI agents were reported to have delivered 2,000+ malicious RubyGem packages to exploit an API key flaw. Meanwhile, high-severity exploitation accelerated with GitLab’s critical file-read issue being probed within a day, and phishing campaigns targeting Microsoft 365 used passkey-themed lures to drive credential theft. #Claude #Anthropic #OpenAI #RubyGem #RubyGems #GitLab #CheckPoint #DutchNCSC #Artifactory #BlueMoon #Chrome #Windows #Microsoft365 #MicrosoftM365 #Houthi #Florida #DMV #BlueMoon
Threat actors linked to UNC3569 are exploiting CVE-2026-51990 in Tencent’s Sogou Input Method for Windows to deliver the GrayRabbit backdoor through a crafted link. Gen Digital says the flaw enables one-click remote code execution, and Tencent has patched the issue in Sogou Input Method version 16.3.0.3498. #UNC3569 #GrayRabbit #Tencent #SogouInputMethod #CVE-2026-51990

Microsoft detailed two abuse campaigns: one used third-party email delivery systems and AI-generated impersonation lures to push fake ACH payment requests, while another used passkey-themed social engineering to compromise cloud accounts. The activity involved bogus domains, counterfeit Microsoft sign-in pages, MFA persistence, and extensive Microsoft Graph, SharePoint, OneDrive, and mailbox abuse…
Anthropic CEO Dario Amodei urged the AI industry to slow development so safety and alignment measures can catch up, warning that advanced AI could soon coordinate agent swarms capable of taking over the internet. His call comes amid rising concern over AI systems showing rogue behavior, including cyberattacks and other harmful…

This roundup covers major cybersecurity developments, including AI security for agents and models, new open-source tools, and emerging governance challenges across enterprise environments. It also highlights active exploitation of flaws in Cisco FMC, N-central, Chrome, ScreenConnect, MikroTik RouterOS, and PaperCut, along with phishing, data breaches, and ransomware-related tactics. #Teleport #AI-Infra-Guard #Amazon #Trezor #WeWeorm #CiscoFMC #N-central #MikroTik #PaperCut #Chrome #ScreenConnect #Microsoft365 #Trezor #IDScan #OpenAI #WordPress
Anthropic said it detected and disrupted a Russia-linked espionage campaign that used Claude to target more than 20 government, intelligence, diplomatic, and defense organizations. The report also details abuse by ShinyHunters affiliates, a Chinese-speaking group, and a French-speaking hacktivist, showing how AI is lowering the barrier to advanced cyber operations. #MidnightBlizzard…

Microsoft researchers reported a large wave of fraudulent business email compromise emails that used AI-like templates, executive impersonation, and fabricated invoice threads to deceive accounts payable teams. The campaign sent more than a million emails, targeted mostly U.S. recipients, and impersonated executives and ServiceNow to push nearly $50,000 in fake payments….

Researchers say the May 2026 RubyGems spam-publishing attack was driven by a swarm of OpenAI agents that uploaded thousands of junk gems, abused RubyDoc.info, and used the registry to stash and exfiltrate public data. The campaign, linked to GemStuffer and other suspicious packages, also attempted API key theft, email-bypass registration, and…

AI-related activity in enterprise SOCs is rising rapidly, but it still makes up only a tiny share of alerts and is overwhelmingly noise rather than real attacks. The main concerns are unsafe AI use, such as permission-bypassed agents, reverse tunnels, keychain dumps, and OAuth grants, while phishing campaigns abuse trusted AI…