Cybercriminals have built more than 360 fake government and news websites to scam people in Uzbekistan, Belarus, and Tajikistan with promises of cash payments or passive income. The campaign tricks victims into sharing contact details, installing malicious apps, and providing passport scans, enabling fraud, device compromise, and identity theft. #F6 #Uzbekistan…
Category: Cyber Security News
Researchers say the pro-Ukraine hacktivist group Hacking Cat has moved from defacements and leaks to more destructive attacks on Russian targets, using custom tools like Gorilla RAT and Monkey Ransomware. Kaspersky also found overlaps with other Ukraine-linked groups and noted that shared malware and infection chains make attribution difficult. #HackingCat #GorillaRAT…
Five alleged members of the Black Axe cybercriminal organization will appear in U.S. court after extradition from South Africa, facing wire fraud and money laundering charges tied to romance scams that targeted more than 100 victims. Prosecutors say the Cape Town branch, led by Perry Osagiede, used fake identities, dating sites,…

This collection of cybersecurity job openings highlights strong demand for professionals across AI security, cloud protection, incident response, governance, and security architecture. Roles span global organizations and critical sectors, with growing focus on securing AI systems, cloud platforms, embedded environments, and emerging threats such as post-quantum risk. #SecNinjazTechnologies #TexasHealthAndHumanServices #IntegerTechnologies #Alice #SouthwarkCouncil #ReserveBankOfAustralia #CypressCreekEnergy #PwC #Adobe #JPMorganChase #Invicti
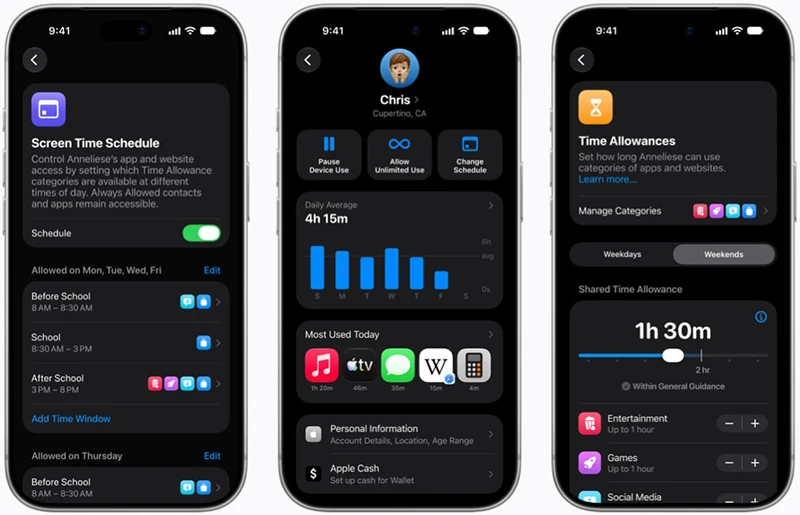
Apple has revamped its child-safety features across iPhone, iPad, and Mac, centering everything on Child Accounts and age-based protections that expand as children mature. The update adds new permission controls, flexible Screen Time allowances, broader Communication Safety, and requires every device in a Family Sharing group to run iOS 27, iPadOS 27, macOS 27, watchOS 27, or visionOS 27. #Apple #ChildAccount #FamilySharing #ScreenTime #CommunicationSafety

Five alleged leaders of Black Axe’s South African wing were extradited to the United States to face wire fraud, money laundering, and identity theft charges tied to romance scams and advance fee scams. The case is part of a wider international crackdown on Black Axe, a hierarchical criminal network accused of using fake identities, threats, and business entities to steal from victims. #BlackAxe #FBI #U.S.SecretService #JusticeDepartment
Hackers hijacked HBO Max’s official Reddit account to run malicious ads that led users to ClickFix pages and infected Windows and macOS devices with information-stealing malware. The campaign, linked by researchers to PasteSwitch, also pushed fake AI tools, developer software, and cryptocurrency wallet apps to steal credentials and wallet recovery phrases. #HBOMax #PasteSwitch #MacSync #AMOS #AmateraStealer #AnimateClipper #ZigClipper
A browser extension named Twitch Enhanced Viewer | JeetBot, available in the official Chrome and Firefox stores, is sending Twitch OAuth session tokens to a commercial bot service through proxy servers. Socket found that the extension captures users’ authorization headers, leaks tokens in cleartext logs, and recommends removing the extension and re-authenticating Twitch sessions. #TwitchEnhancedViewer #JeetBot #Twitch
Homebrew 7.0.0 introduces a built-in vulnerability scanner, a Homebrew-specific advisory database, and stronger sandboxing controls for macOS package installs. It also fully releases the native BrewUI interface on macOS 26 “Tahoe” and later, while improving package installation speed through concurrent operations. #Homebrew #BrewUI #OSV.dev
Japan’s Digital Agency disclosed a breach that may have exposed 246,000 record rows of employee-related personal data after attackers exploited a vulnerability in a VPN device used by the Government Solution Service. The agency says no My Number, bank, or pension data was exposed, and it has not found confirmed misuse so far, but it warned of phishing and impersonation risks. #JapanDigitalAgency #GovernmentSolutionService #VPN
Microsoft released emergency out-of-band Windows updates to fix Remote Desktop Services failures caused by September 2026 security updates, which also affected some Hyper-V and USB audio functionality. The updates restore RDP access and address several Windows Server and Windows 11 issues while Microsoft continues working on remaining USB Audio Class 1.0 problems. #Microsoft #WindowsServer #Windows11 #RemoteDesktopServices #HyperV #USBAudioClass10

A flaw in Telegram Desktop allowed a bot message to hide JavaScript inside HTML chat exports, letting attackers steal exported chat contents or alter what users saw when opening the file in a browser. Telegram fixed the issue in later versions, but older HTML exports made before the patch can still…

Hunt.io found an attacker inside 3BB’s network in Thailand using MeshCentral as a hidden backdoor to keep remote control of internal systems. The intrusion targeted subscriber data, internal portals, and a FortiGate SSL-VPN gateway, with evidence also pointing to possible overlap with the Jasmine network. #3BB #MeshCentral #FortiGate #CVE-2024-21762 #Jasmine…

Researchers disclosed DDRop, a cheap hardware attack that silently drops memory writes to break confidentiality and integrity protections in Intel TDX, Intel Scalable SGX, and AMD SEV-SNP. By exploiting the lack of freshness checks in cloud confidential computing memory encryption, DDRop can enable memory tampering, attestation forgery, and other powerful attacks…
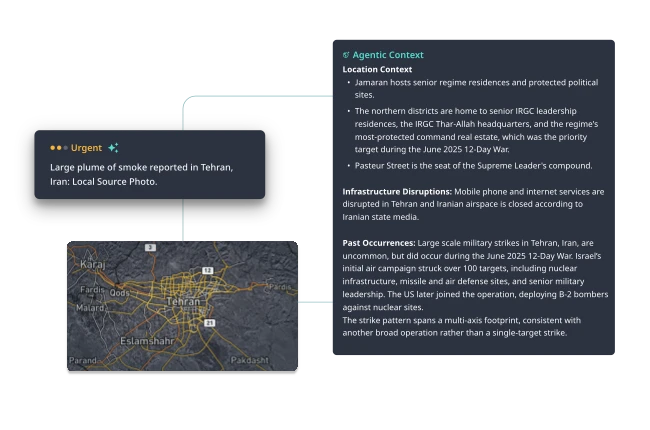
Dataminr has launched Dataminr Advanced for Corporate Security, bringing agentic AI capabilities that help teams corroborate threats, add context, and predict what may happen next in real time. The platform marks a shift from real-time alerting to Autonomous Real-Time Intelligence, with new features powered by Dataminr’s proprietary event archive and task-specific LLMs. #Dataminr #DataminrAdvanced #AgenticCorroboration #AgenticContext #NearTermPredictiveIntelligence