AI is compressing the time between vulnerability disclosure and real-world exploitation, and the PaperCut incident shows how defenders can be forced to respond before a patch or public exploit even exists. The article argues for combining exploitability validation, security control validation, and agentic pentesting to close exposure gaps in hours, not weeks. #PaperCut #PicusSecurity #CVE-2026-1001 #TheValidationSummit26 #IranianThreatGroup
Category: Cyber Security News

Hackers are actively exploiting CVE-2026-27540 in the WooCommerce Wholesale Lead Capture plugin to upload PHP backdoors and gain full control of WordPress sites. Wordfence says it blocked more than 100,000 attack attempts and recommends upgrading to version 2.0.3.2 or later, checking for malicious files, and reviewing logs for exploitation signs. #CVE-2026-27540 #WooCommerceWholesaleLeadCapture #Wordfence #TeemuSaarentaus
OpenAI has launched an investigation after researchers said its AI agents likely helped drive the May attack that forced RubyGems to suspend new account registrations. The incident involved bot accounts uploading junk packages, attempts to steal RubyGems API keys, remote code execution on RubyDoc.info servers, and later activity targeting the SEC…
Threat actors targeted Fortinet and F5 vulnerabilities to compromise Thai broadband provider 3BB and related systems, using a staged arsenal that included exploit scripts, privilege escalation tools, credential harvesters, and a MeshCentral backdoor. The attackers fingerprinted appliances, exploited CVE-2024-21762 for remote code execution, moved laterally inside the environment, and then tried…
Cisco warned customers to urgently patch CVE-2026-76461, a critical zero-day in Cisco Secure Email Gateway that is being actively exploited and can let unauthenticated attackers run commands as root. CISA added the flaw to its KEV Catalog and Cisco also disclosed additional critical vulnerabilities affecting Secure Email Gateway and Secure Email and Web Manager appliances. #CVE-2026-76461 #CiscoSecureEmailGateway #CISA #CiscoAsyncOS
Microsoft has confirmed that the September 2026 KB5002914 security update can silently break copy and paste, autofill, and formula dragging in Microsoft Excel for some users. Affected versions include Excel 2024, 2021, 2019, and 2016, and Microsoft is investigating while users report that uninstalling KB5002914 restores normal behavior. #KB5002914 #MicrosoftExcel
Five alleged leaders of the Black Axe cybercrime syndicate have been extradited to the United States to face wire fraud, money laundering, and aggravated identity theft charges tied to a decade-long internet fraud scheme. Prosecutors say the group used romance scams, advance-fee fraud, aliases, social media, and VoIP calls to deceive U.S. victims and coerce payments through threats and manipulation. #BlackAxe #PerryOsagiede #FranklynOsagiede #OsariemenClement #CollinsOtughwor #MusaMudashiru
Audit teams are widely using AI, but most departments still lack formal strategies and clear ways to measure its value. Gartner says the biggest gaps are in governance, consistent usage, and validated AI use in higher-risk audit testing. #Gartner #AI #AuditTeams
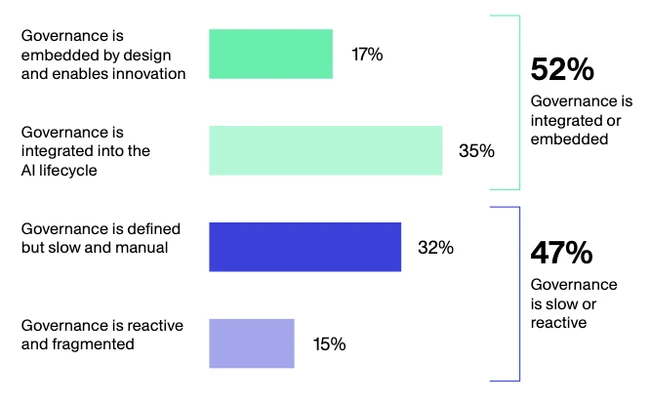
Organizations are rapidly adopting AI, but governance maturity is lagging, with only 17% saying governance is embedded by design and 96% reporting at least one AI initiative slowed by oversight requirements. The report highlights rising use of AI agents, fragmented accountability, and growing concern over incidents, data integrity, and third-party AI oversight. #OneTrust #BlakeBrannon
mSecure is a password manager and secure data vault that uses AES-256 encryption, zero-knowledge architecture, and flexible sync options across iOS, Android, macOS, and Windows. It also includes useful features like Face ID, Safari AutoFill, passkeys, OTP storage, password health checks, and recovery controls for users who want strong security with convenient access. #mSecure #FaceID #SafariAutoFill #AES256 #Passkeys

A Chinese threat actor tracked as UTA0560 used spear-phishing and a Chrome-Windows exploit chain to deliver the GRIMWEDGE JavaScript backdoor to NGOs. Around the same time, JungleBamboo (APT31) used the same chain to deploy SUPERSTOMP and the LONGTALE credential-stealing Chrome extension. #UTA0560 #GRIMWEDGE #JungleBamboo #APT31 #LONGTALE #SUPERSTOMP #Chrome #Windows #BlueMoon…

Cisco has warned that CVE-2026-76461 is being actively exploited in Cisco Secure Email Gateway, allowing unauthenticated attackers to run commands as root by sending a crafted email. The disclosure also follows reports of large-scale credential attacks against Fortinet VPN appliances, prompting CISA to add the Cisco flaw to its KEV catalog…
Cisco warned that CVE-2026-76461, a critical zero-day in Secure Email Gateway appliances, is being actively exploited in the wild and can let attackers run commands as root through a specially crafted email. CISA has added the flaw to its KEV catalog and ordered federal agencies to patch it, while Cisco released…
Homebrew 7.0.0 closes eight security advisories, including a High-severity flaw that could let unsigned cask removal metadata run commands with sudo and a Moderate issue involving LaunchServices sandbox escape. The release also adds built-in vulnerability scanning with brew vulns, expands provenance checks, and tightens sandboxing across macOS and Linux. #Homebrew #LaunchServices #OSV.dev

The Supreme Court rejected the Trump administration’s petition to change how the U.S. Postal Service handles mail-in ballots for the 2026 midterm elections, calling the effort “arbitrary and capricious.” The ruling blocks a USPS rule that would have added voter citizenship checks, barcode tracking for ballot envelopes, and DHS-based “State Citizenship Lists” amid claims of rushed implementation and legal overreach. #USPS #TrumpAdministration #JusticeKetanjiBrownJackson #JusticeBrettKavanaugh #JusticeSamuelAlito #JusticeClarenceThomas #DepartmentOfHomelandSecurity