The Predator spyware from Intellexa employs an innovative zero-click infection method called “Aladdin,” which infects devices through malicious advertisements without user interaction. Ongoing investigations reveal complex delivery networks across multiple countries and sophisticated exploits targeting devices and mobile networks. #Intellexa #Aladdin #PredatorSpyware #SamsungExynos #ZeroDayExploits
Category: Cyber Security News
The UK’s NCSC has launched a pilot of Proactive Notifications to identify and advise organizations on unpatched vulnerabilities using external internet scanning, with recommendations emailed from Netcraft. This service is part of a layered security approach and complements the Early Warning service, which monitors active threats; however, organizations should not rely solely on these tools for security. #NCSC #ProactiveNotifications #Netcraft #EarlyWarning
Threat actors are exploiting a command injection vulnerability in Array AG Series VPN devices to plant webshells and create rogue users, targeting primarily organizations in Japan and other countries. Although Array Networks released a security update in May, the flaw remains actively exploited, posing significant risks to enterprise remote access systems. #ArrayNetworks #CommandInjection
A Russia-aligned threat actor known as Callisto attempted to target Reporters Without Borders through a sophisticated phishing campaign. This group, linked to Russia’s FSB, has a history of attacking NGOs, government agencies, and Ukraine-supporting organizations. #Callisto #RSF #Phishing…

Chinese state-sponsored hackers are deploying the sophisticated BRICKSTORM malware to infiltrate government and IT sectors worldwide, maintaining long-term access for espionage and data theft. Cybersecurity agencies and firms have issued warnings and indicators of compromise, emphasizing the threat’s persistence and stealthy nature. #BRICKSTORM #PRCcyberactors…
Google Threat Intelligence uncovered an active iOS zero-day exploit chain linked to Intellexa, a commercial surveillance vendor, targeting individuals in Egypt. The attack involves a three-stage process to install Predator spyware, highlighting ongoing concerns about illegal digital espionage. #Intellexa #PredatorSpyware…

U.S. and Canadian cybersecurity agencies warn that China-sponsored threat actors are exploiting BRICKSTORM malware to compromise VMware vSphere environments and gain long-term access. These attacks primarily target government and IT sectors, enabling threat actors to steal data and create rogue VMs. #BRICKSTORM #PRCThreatActors…
Microsoft has addressed a critical Windows LNK vulnerability (CVE-2025-9491) exploited by multiple threat actors, including state-sponsored groups, by silently implementing mitigation measures. The flaw, which allows attackers to hide malicious commands in shortcut files, has been actively exploited in zero-day campaigns involving malware like Trickbot and PlugX. #CVE-2025-9491 #EvilCorp #APT37 #MustangPanda…
Sha1-Hulud has launched a sophisticated supply-chain attack targeting npm packages used by JavaScript developers, infecting nearly 1,000 packages and exposing tens of thousands of repositories. The latest campaign includes new features like cross-platform support, a self-destruct mechanism, and remote code execution via GitHub Actions, increasing the threat’s severity. #Sha1Hulud #npmSupplyChainAttack…
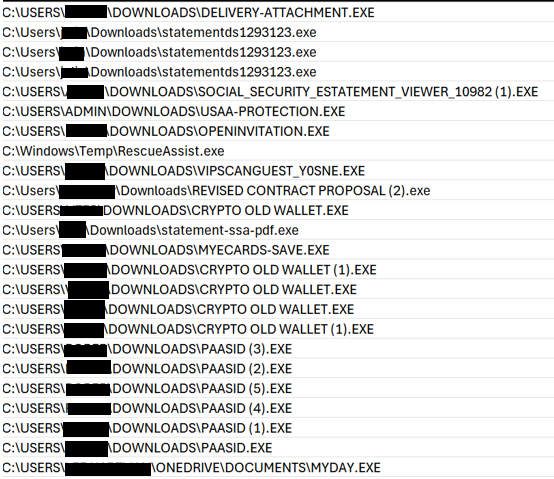
A new wave of cyberattacks exploits legitimate Remote Monitoring and Management (RMM) tools like LogMeIn Resolve and PDQ Connect to gain unauthorized remote access. Attackers deceive users into installing these trusted programs, allowing them to evade detection and maintain persistent control over infected systems. #LogMeInResolve #PDQConnect…
The Aisuru botnet has launched over 1,300 DDoS attacks within three months, including record-breaking peaks at 29.7 terabits per second. These attacks have targeted multiple sectors worldwide, demonstrating the increasing severity of hyper-volumetric DDoS threats. #Aisuru #Cloudflare #DDoSAttacks #HyperVolumetric…

CISA has added two new actively exploited vulnerabilities related to Android Framework to its KEV Catalog. These vulnerabilities pose significant risks, prompting organizations to prioritize their remediation efforts. #CISA #AndroidVulnerabilities…

This extensive cyber operation, active for over 14 years, primarily targets Indonesian citizens through illegal gambling platforms, malware distribution, and website hijacking. Researchers suggest it also serves as a command and control hub, employing sophisticated techniques to evade detection. #Malanta #IndonesianCyberThreats…
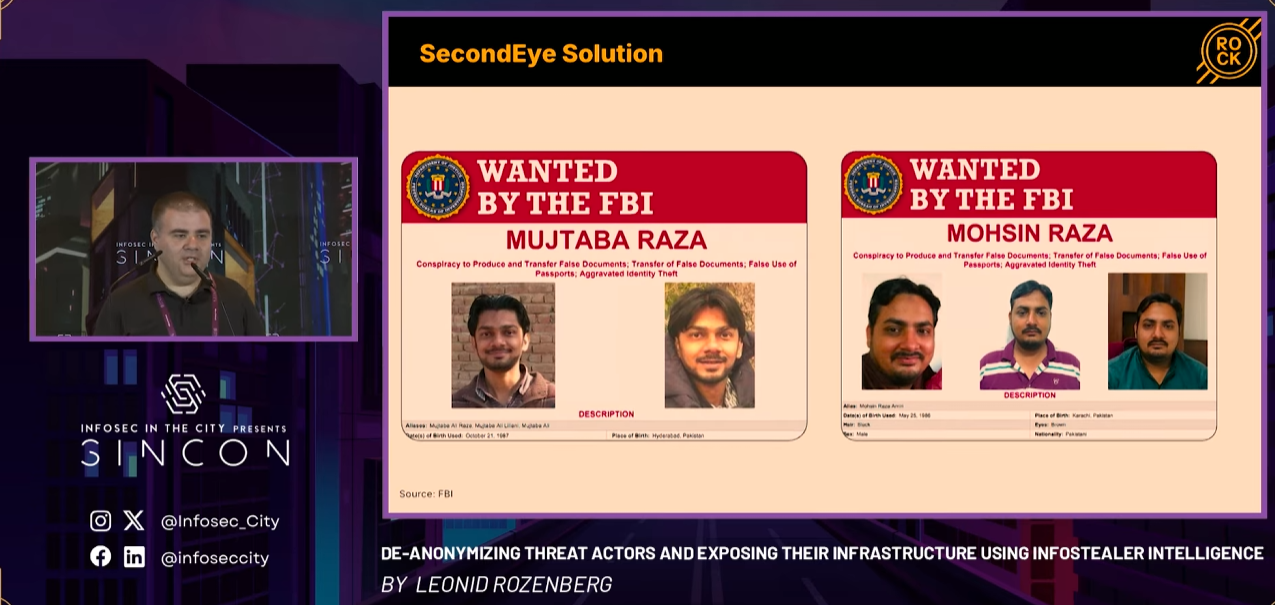
Infostealer malware is highly effective for cybercriminals but can sometimes backfire by infecting their own systems, revealing their operations. Hudson Rock researchers use these accidental infections to uncover threat identities and understand malware infrastructure. #Infostealer #Cybercriminals
Operational Technology (OT) plays a crucial role in controlling vital infrastructure but faces significant cybersecurity challenges due to outdated systems and password vulnerabilities. Strengthening password policies and deploying layered security measures can help protect OT environments from cyber threats. #OTSecurity #PasswordPolicies