
CISA has revealed details of BRICKSTORM, a sophisticated backdoor used by Chinese state-sponsored threat actors to maintain long-term access on VMware vSphere and Windows systems. The malware is employed in targeting government and IT sectors, supporting covert command-and-control operations through various protocols and concealment techniques. #BRICKSTORM #WarpPanda…
Category: Cyber Security News

This article emphasizes the importance of building trust with clients through education, empathy, and evidence rather than traditional sales tactics. It provides strategies for MSPs to transform sales objections into collaborative opportunities and foster long-term partnerships. #CyberAdvisor #GettingToYes…

A new report reveals that Intellexa’s Predator spyware has been used to target civil society members in Pakistan and potentially other countries, employing sophisticated zero-day exploits and various infection vectors. Despite international sanctions and public scrutiny, the company continues to develop and deploy invasive surveillance tools with possible human rights violations….
Helmet Security has launched its platform with $9 million in funding to protect the connections between AI agents and data. The company focuses on securing the Model Context Protocol (MCP) and offers an automated solution to monitor and control MCP server traffic. #ModelContextProtocol #AIConnections…
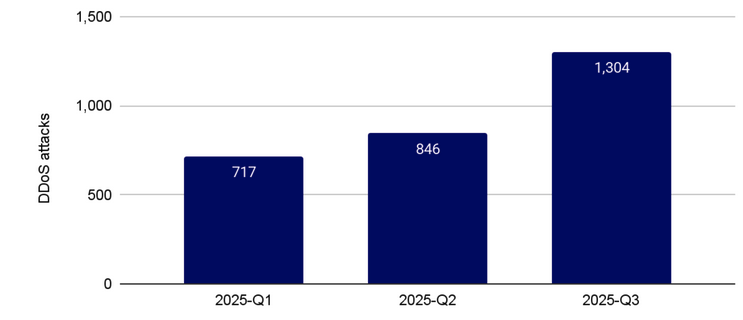
The Aisuru botnet continues to break DDoS attack records, with a peak of 29.7 Tbps in Q3 2025. This IoT-based botnet is responsible for massive assaults on cloud services, hosting providers, and financial institutions. #Aisuru #TurboMirai #DDoSattacks #Cloudflare #MicrosoftAzure…
Lumia Security, an Israeli startup, has raised $18 million to develop a platform that provides visibility and control over AI agent interactions within organizations. Their technology offers continuous risk assessment and policy enforcement without endpoint modifications. #LumiaSecurity #AIInteractionControl…
Internal leaks reveal Intellexa staff had direct remote access to at least 10 Predator customer systems, including surveillance dashboards and live targeting operations. The leaked documents expose how the sanctioned spyware vendor continues to operate despite US sanctions, with active deployments and infection vectors such as silent advertising-based infections. #Intellexa #PredatorSpyware…
A new critical vulnerability called React2Shell (CVE-2025-55182) has been quickly exploited by Chinese state-sponsored groups, highlighting the rapid weaponization cycle. Immediate patching is urged to prevent remote code execution attacks in React and Next.js applications. #React2Shell #CVE-2025-55182 #AWS #ChinaThreatActors…

A recent command injection vulnerability in Array Networks AG Series gateways has been actively exploited in Japan since August 2025, allowing attackers to implant web shells and access internal systems. Although a fix was released in May 2025, many devices remain unpatched, creating a significant security risk. #ArrayNetworks #WebShells…
Google has released a Chrome browser update addressing 13 security vulnerabilities, including four high-severity flaws. One critical flaw, CVE-2025-13633, involves a use-after-free vulnerability in the Digital Credentials feature, potentially exploited by remote attackers. #ChromeUpdate #DigitalCredentialsVulnerability…

A command injection vulnerability in Array Networks AG Series secure access gateways has been actively exploited since August 2025, mainly targeting systems with DesktopDirect enabled. This security flaw, addressed in May 2025, has led to web shell attacks in Japan, with attackers exploiting the vulnerability from a known IP address. #ArrayNetworks…
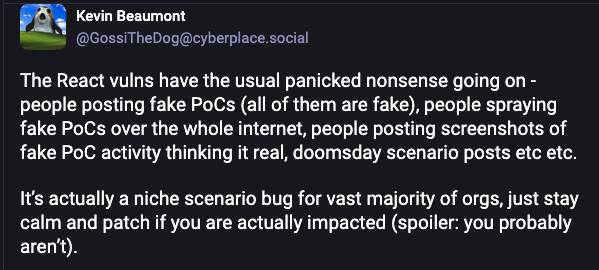
Threat actors are actively exploiting the recently disclosed React2Shell vulnerability (CVE-2025-55182), targeting many systems worldwide. Multiple threat groups, including Earth Lamia and Jackpot Panda, are attempting to leverage both fake and working PoC exploits, indicating high danger levels for affected organizations. #React2Shell #CVE-2025-55182…

Daily Recap, regulatory moves span India withdrawing the Sanchar Saathi mandate and the UK’s cookie-enforcement push, with broader state activity highlighting Russia’s connected-car vulnerabilities and sanctions related to cyber espionage. The week also features critical RSC bugs in React/Next.js, LNK flaws, Elementor/King Addons WordPress exploits, a record AISURU DDoS with up to 4 million bots, Predator spyware activity, and data breaches at Freedom Mobile and Marquis alongside Rhysida ransomware pressure on local governments. #SancharSaathi #PredatorSpyware #AISURU #Rhysida #KingAddons #LNK #FreedomMobile #Marquis

Patchwork, a South Asian-linked cyberespionage group, has launched a new campaign featuring the stealthy Trojan StreamSpy for targeted espionage activities. This malware uses advanced techniques like WebSocket and HTTP protocols to evade detection and maintain persistence on infected systems. #Patchwork #StreamSpy…

A new wave of cyber-espionage attacks targets NGOs, particularly press freedom advocates, using sophisticated spear-phishing campaigns linked to Russian state-sponsored hackers. The Calisto group, attributed to the FSB, employs advanced social engineering and custom attack tools to target entities supporting Ukraine. #Calisto #ReportersWithoutBorders #RussianIntelligence…