The European Commission issued a €120 million fine to X for violating transparency obligations under the Digital Services Act, marking the first non-compliance case. The platform was found to misuse verification badges, obstruct researcher access, and hinder transparency in advertising, undermining user trust and safety. #DigitalServicesAct #XPlatform
Category: Cyber Security News

The European Commission fined X, Elon Musk’s social media platform, €120 million for non-compliance with transparency and disinformation regulations under the Digital Services Act. This first-ever penalty under the DSA highlights ongoing tensions between the EU and American tech companies over online regulation and free speech. #DigitalServicesAct #ElonMusk…
Traditional passive internet-scan data often provides outdated and incomplete views of an organization’s attack surface. Continuous, automated reconnaissance offers real-time, validated insights that help security teams stay ahead of emerging threats and misconfigurations. #SprocketSecurity #AttackSurfaceMonitoring
The FBI warns about virtual kidnapping scams where criminals manipulate images and claim to have kidnapped loved ones to extort ransom payments. Victims are deceived by convincing fake proof of life photos and urgent messages, but these scams involve no actual abduction. #VirtualKidnapping #ImageManipulation

The Trump administration’s new national security strategy emphasizes collaboration between U.S. government, industry, and regional partners to safeguard critical infrastructure and networks from cyber threats. It highlights efforts to enhance real-time cyber defense capabilities, promote deregulation, and focus on regional partnerships, especially in the Western Hemisphere. #NationalSecurityStrategy #CyberDefense #WesternHemisphere #U.S.Infrastructure…
Barts Health NHS Trust experienced a data breach where Clop ransomware actors stole sensitive files by exploiting a critical Oracle E-Business Suite vulnerability. The stolen data includes personal information of patients, former employees, and suppliers, with the breach now exposed on the dark web. #Clop #OracleCVE-2025-61882

State-backed Chinese hackers are exploiting a critical vulnerability in the open-source React Server Components tool, which is embedded in millions of websites. The attack involves multiple threat groups using automated tools and proof-of-concept exploits, highlighting the urgent need for defenses against widespread exploitation. #ReactServerComponents #CVE-2025-55182…

Imper.ai is a cybersecurity startup specializing in detecting AI-driven impersonation and social engineering attacks in communication platforms like Zoom and Slack. The company aims to make real-time verification the foundation of enterprise security, addressing the rising threat of deepfakes and voice clones. #Deepfakes #SocialEngineering…
Cloudflare experienced an outage caused by its mitigation efforts for the React2Shell vulnerability (CVE-2025-55182). The incident highlights the challenges of balancing security measures and operational stability during critical vulnerability responses. #React2Shell #CVE2025-55182…
This cybersecurity roundup highlights recent developments, including AI-assisted ransomware execution and exploits in network vulnerabilities. Key incidents involve ransomware experiments with Claude Skills, North Korean hacking activities, and significant policy and vulnerabilities updates. #ClaudeSkills #LazarusGroup…
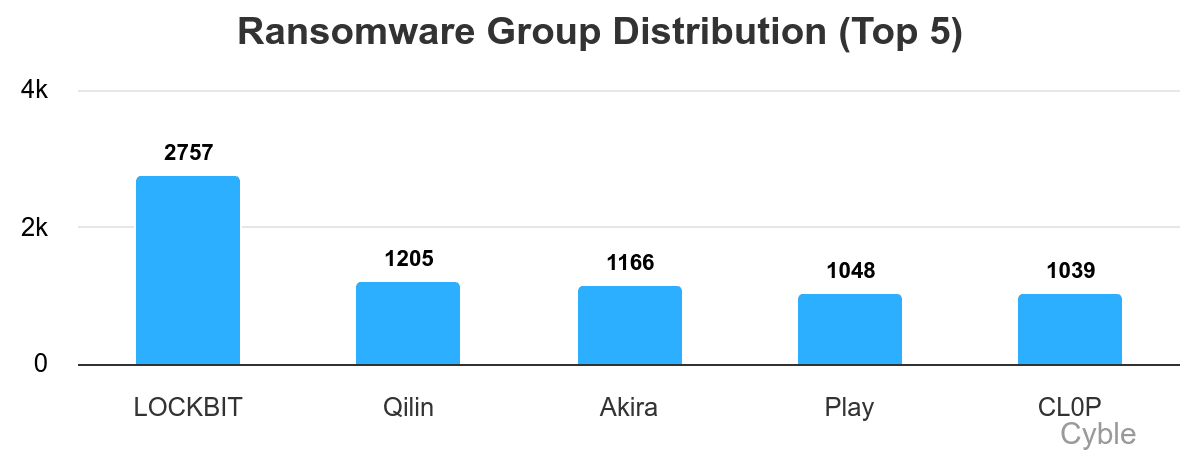
LockBit ransomware group is making a notable comeback with a new data leak site and recent victims, despite previous disruptions caused by law enforcement. Its latest variant, LockBit 5.0, offers enhanced features and targets diverse sectors and regions, raising ongoing cybersecurity concerns. #LockBit #LockBit5.0 #RansomwareRecovery…
Cloudflare is experiencing a major outage causing websites to display 500 Internal Server Errors, and the company is actively investigating the issue. This disruption affects many sites relying on Cloudflare’s services and APIs. #Cloudflare #InternalServerError
Multiple threat actors linked to China are actively exploiting the React2Shell vulnerability (CVE-2025-55182) shortly after its disclosure, leading to widespread attacks on React and Next.js applications. These attacks are facilitated by publicly available proof-of-concept exploits and are targeting various sectors globally, with several threat groups specifically focused on different regions; security updates have been issued but the vulnerability remains easy to exploit. #React2Shell #ChinaThreatActors
American pharmaceutical firm Inotiv suffered a ransomware attack in August 2025, resulting in the theft of personal data of thousands of individuals. The incident was claimed by the Qilin ransomware group, which leaked over 162,000 files. #Qilin #RansomwareAsaService
Cloudflare’s recent outage was caused by an emergency patch for a critical React Server Components vulnerability, which was actively exploited in attacks. Multiple hacking groups have begun exploiting this flaw, escalating the urgency for affected organizations to respond. #React2Shell #ReactVulnerability