Ursula von der Leyen used her 2026 State of the European Union speech to warn that AI brings massive risks, including advanced hacking and self-improving systems, while arguing Europe should harness AI through the AI Act and human oversight. She also pushed a tougher stance on social media harms to children,…
Category: Cyber Security News
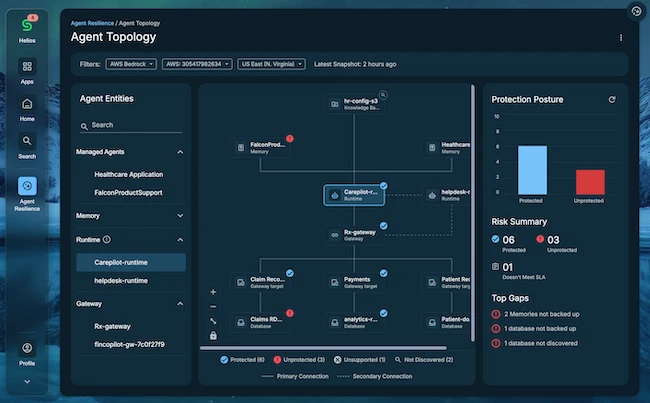
Cohesity has launched Agent Resilience to discover, protect, and recover the infrastructure behind enterprise AI agents, closing a critical gap when agent actions corrupt or change systems. The company also unveiled its vision for Autonomous Cyber Resilience and a free AI Resilience Academy course to help organizations manage the risks of AI agents as they move from advising to acting. #Cohesity #CohesityAgentResilience #AutonomousCyberResilience #CohesityDataCloud #AmazonBedrock #CohesityRecoveryAgent #CohesityMaestro #CohesityGaiaCatalog
Ursula von der Leyen urged frontier AI development to slow down, warning that upcoming models could enable hacking at an unprecedented level and that self-improving systems may pose growing security risks. She said the EU will work with Canada, the U.K., and other partners on model evaluation, verification, early warning, and AI security, while also pushing AI use across key sectors like health, transport, agrifood, manufacturing, and defense. #UrsulaVonDerLeyen #EuropeanCommission #AIAct #CETA #HuggingFace
CISA has released new guidance encouraging critical infrastructure operators to use cyber decoys, such as fake systems, accounts, and data, to detect and distract intruders already inside their networks. The 22-page guide explains how honeytokens and other decoy techniques can support zero-trust and assume-compromise defenses at low cost. #CISA #CyberDecoys #Honeytokens

Daily Recap, Cisco patched an actively exploited Secure Email Gateway zero-day that enables command execution as root, while China-linked actors chained a Chrome-Windows zero-day to deploy GRIMWEDGE. Attackers also targeted WooCommerce/WordPress via a third-party plugin, abused exposed Vite dev servers for AWS/Azure secrets, and leveraged a Telegram Desktop HTML export flaw to exfiltrate messages, alongside ongoing ransomware exploitation of a VMware vCenter RCE flaw.
#Cisco #GRIMWEDGE #WooCommerce #WordPress #Vite #AWS #Azure #TelegramDesktop #VMwarevCenter #ClickFix #PasteSwitch #DDROP #BlackAxe
The Spanish Data Protection Agency (AEPD) was notified of a breach allegedly carried out by an AI agent using a known large language model, which autonomously searched for vulnerabilities, logged into systems, and accessed personal and financial data. The incident underscores how AI can speed up, scale, and adapt attacks, prompting a review of identity security, response procedures, and data protection models. #AEPD #OpenAI #HuggingFace #GoogleGemini #AnthropicClaude
A banking malware campaign active since mid-2025 has used the KREMLIN toolkit to silently install malicious Chrome and Edge extensions that steal credentials, session tokens, and browser data. Elastic Security Labs linked the operation to a Brazilian threat actor, confirmed 1,515 infected systems, and disrupted part of the campaign by registering a key anti-sandbox domain. #KREMLIN #ElasticSecurityLabs #REMCOS #PulsarRAT #Brazil
Government agencies warn that Iranian state-linked hackers are using CHOSEN BRICK to spy on dissidents, activists, and journalists by stealing messages, screenshots, and audio. The malware is spread through social engineering on WhatsApp and Telegram, hides with Windows persistence, and sends stolen data through Telegram and cloud services. #CHOSENBRICK #Iranian #Telegram #WhatsApp #FBI
Microsoft is investigating reports that the Windows 11 KB5124008 security update is breaking domain trust relationships on some enterprise systems, causing valid domain credentials to fail after reboot. Administrators say the issue appears linked to the Machine Identity Isolation feature in Windows 11 25H2, with some systems recovering after disabling it and repairing the secure channel. #Microsoft #Windows11 #KB5124008 #MachineIdentityIsolation #ActiveDirectory
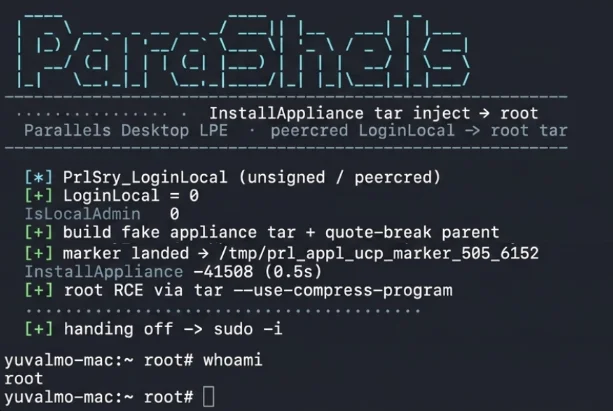
JFrog disclosed CVE-2026-90894, a Parallels Desktop flaw dubbed “ParaShells” that can let any local user on a Mac escalate to root on the host. The issue affects Parallels Desktop for Mac v26.4.0 on Apple ARM-based systems and was fixed by Alludo in Parallels Desktop v27.0.0. #CVE-2026-90894 #ParaShells #ParallelsDesktop #Alludo
Treasury Secretary Scott Bessent urged lawmakers not to grant AI labs liability exemptions, arguing that creators should be held responsible for what they build and generate. He also said Treasury is working on AI safety after the Mythos model release and is coordinating with banks and labs through Gold Eagle and other discussions. #ScottBessent #Mythos #Anthropic #GoldEagle #HuggingFace
The Coast Guard and FBI boarded two foreign tankers in the Gulf of Mexico after indications that both ships’ networks were compromised, but no operational disruptions or safety impacts have been reported. Investigators are examining possible links to Iran and broader risks tied to “dark fleets” carrying sanctioned oil. #CoastGuard #FBI #Iran #GulfofMexico
Attackers are exploiting a critical ConnectWise ScreenConnect vulnerability in the wild, prompting CISA to add it to its actively exploited catalog and order federal agencies to secure systems quickly. The flaw, tracked as CVE-2026-84869, can let attackers with basic privileges transfer or execute files, and more than 1,000 exposed instances remain unpatched online. #ConnectWise #ScreenConnect #CVE-2026-84869 #CISA #Shadowserver
This webinar from BleepingComputer and Material Security will examine real Google Workspace breaches and the critical decisions security teams must make in the first hours after discovering suspicious access. It will also explore how social engineering and malicious OAuth applications enabled access, and which controls can best protect fast-growing companies. #BleepingComputer #MaterialSecurity #GoogleWorkspace #OAuth
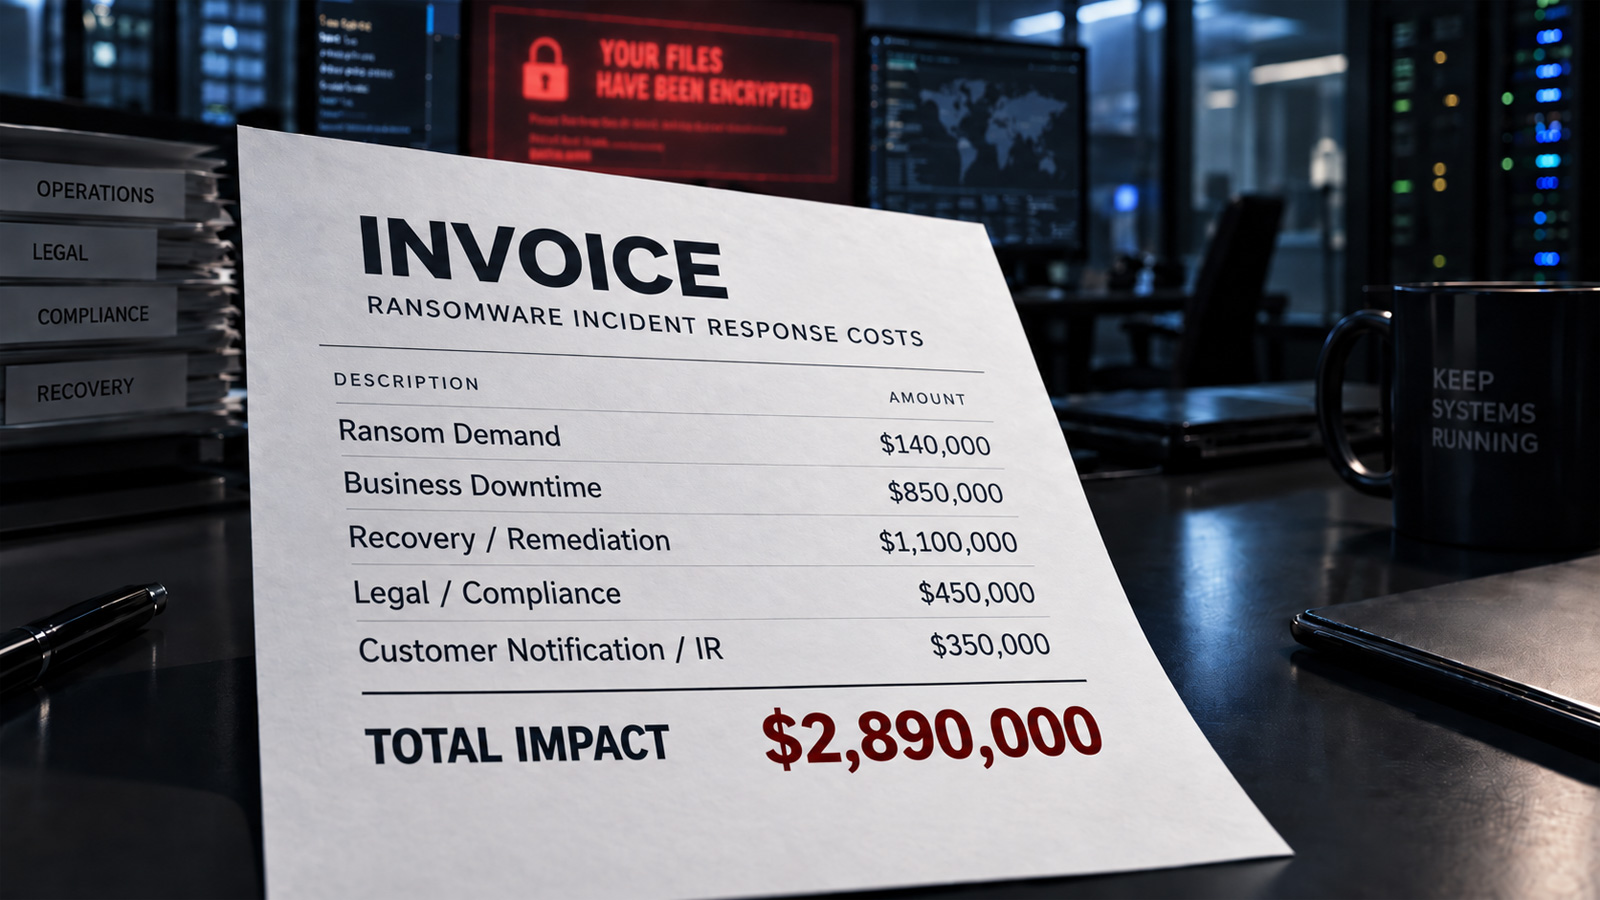
Ransomware costs far more than the ransom itself, with downtime, recovery, legal work, compliance, and business disruption driving the total impact to millions of dollars. A mature BCDR strategy can reduce recovery time, protect backups, and help organizations return to operations faster after an attack. #Datto #BCDR #GDPR #SEC #HIPAA #Techify