The Spanish Data Protection Agency (AEPD) was notified of a suspected AI agent attack that reportedly found vulnerabilities, logged into systems, modified personal data, and accessed financial documents. The incident highlights how AI-driven attacks can increase speed, scale, and adaptability, prompting a review of security and data protection models. #AEPD #OpenAI #GoogleGemini #AnthropicClaude #HuggingFace
Category: Cyber Security News
The Spanish Data Protection Agency (AEPD) has reported what appears to be the first known personal data breach carried out by an AI agent that chained together multiple stages of an attack. The incident raises new concerns about agentic AI, as defenders may need faster detection, containment, and response tools to…
Microsoft is still investigating a known issue in Classic Outlook for Windows that causes Copilot and Copilot Chat buttons to disappear for some users after upgrading to build 20026.20182 and higher. Microsoft also confirmed a separate Outlook crash bug tied to Kaspersky Antivirus, while suggesting temporary workarounds like enabling “Show Apps in Outlook” or using Outlook on the web. #Copilot #ClassicOutlook #KasperskyAntivirus

More than 200,000 WordPress websites may be exposed to takeover attacks through two critical-severity vulnerabilities in The Events Calendar plugin. StellarWP has released patches for CVE-2026-78159 and CVE-2026-78006, both of which can lead to remote code execution and full site compromise. #TheEventsCalendar #StellarWP #CVE-2026-78159 #CVE-2026-78006…
US, UK, and Dutch agencies warned about Chosen Brick, a Windows malware family used by Iranian state cyber actors to spy on dissidents, activists, and journalists worldwide. The malware steals messages and personal data, uses Telegram for command-and-control, and can also deploy secondary payloads and wipe data. #ChosenBrick #Telegram #FBI…
Microsoft has reminded customers that Windows Server 2022 will exit mainstream support on October 13, 2026 and move into extended support through October 14, 2031. Administrators are being urged to plan upgrades to Windows Server 2025, while Datacenter: Azure Edition systems will keep receiving hotpatching until October 2027. #WindowsServer2022 #WindowsServer2025 #DatacenterAzureEdition
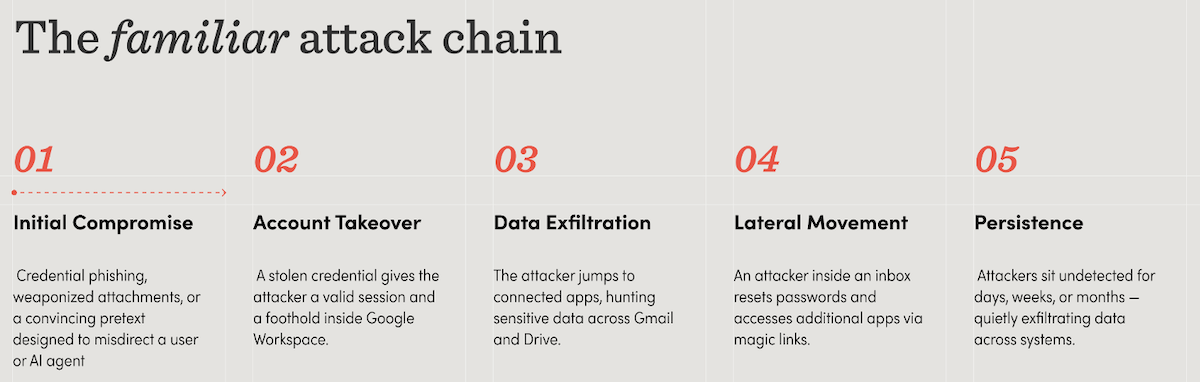
The Vercel and Composio incidents show that modern workspace attacks can start with OAuth grants instead of email, allowing access to Gmail, Drive, and broader connected systems. The article argues that AI agents using legitimate OAuth access can follow the same dangerous path, so organizations need environment-level controls across email, OAuth, and data access. #Vercel #Composio #OAuth #Gmail #Drive #GoogleWorkspace
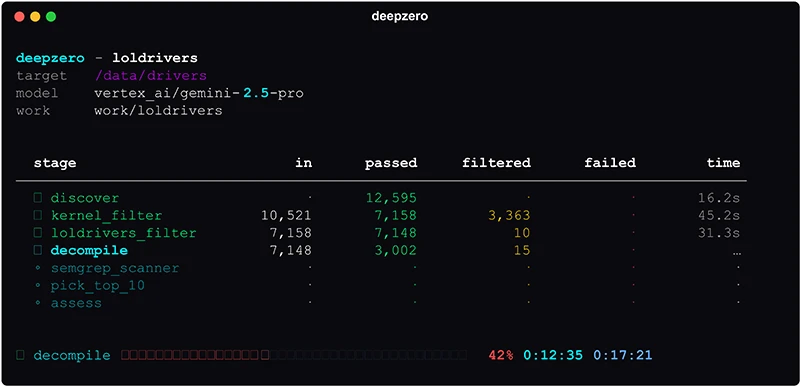
DeepZero is an open-source, Python-based engine that automates the hunt for exploitable Windows kernel drivers by parsing binaries, filtering candidates, and using a language model to assess exploitability. Its bundled pipeline focuses on BYOVD research and has already found multiple verified vulnerabilities in the Snappy Driver Installer corpus. #DeepZero #SnappyDriverInstaller #BYOVD
Gourab Basu of meshIQ explains that AI agent governance must happen inside the execution flow, because prompts alone cannot reliably control nondeterministic agent behavior. He also warns that scaling from a few agents to thousands requires framework-independent controls, auditability, and human approval for actions that affect enterprise systems. #meshIQ #GourabBasu
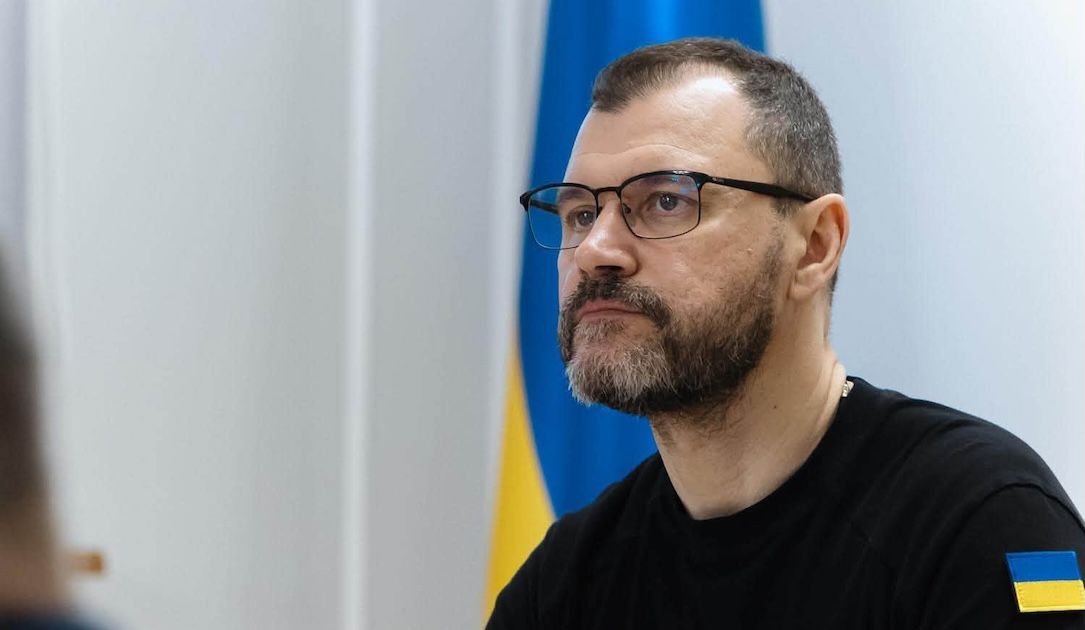
Ukrainian President Volodymyr Zelensky has appointed Ihor Klymenko to lead the National Cybersecurity Coordination Center, which oversees Ukraine’s government response to major cyberthreats. The move comes amid a wider reshuffle in Ukraine’s security leadership and ongoing efforts to counter Russian cyber operations and criminal networks. #VolodymyrZelensky #IhorKlymenko #NationalCybersecurityCoordinationCenter #NSDC #RussianCyberOperations…
British, American, and Dutch agencies warned that Iranian state-sponsored hackers are using CHOSEN BRICK spyware to target dissidents, activists, journalists, and others seen as threatening the regime. The malware is spread through social engineering and fake lures, then used to steal data, monitor victims, and support harassment and physical intimidation. #CHOSENBRICK…
Norwegian law enforcement is investigating whether Telenor may have aided crimes against humanity by repeatedly handing over customer traffic data to Myanmar’s military regime after the 2021 coup. The probes also examine whether Telenor violated sanctions when it sold its Myanmar subsidiary, amid claims that the company’s data and surveillance equipment…
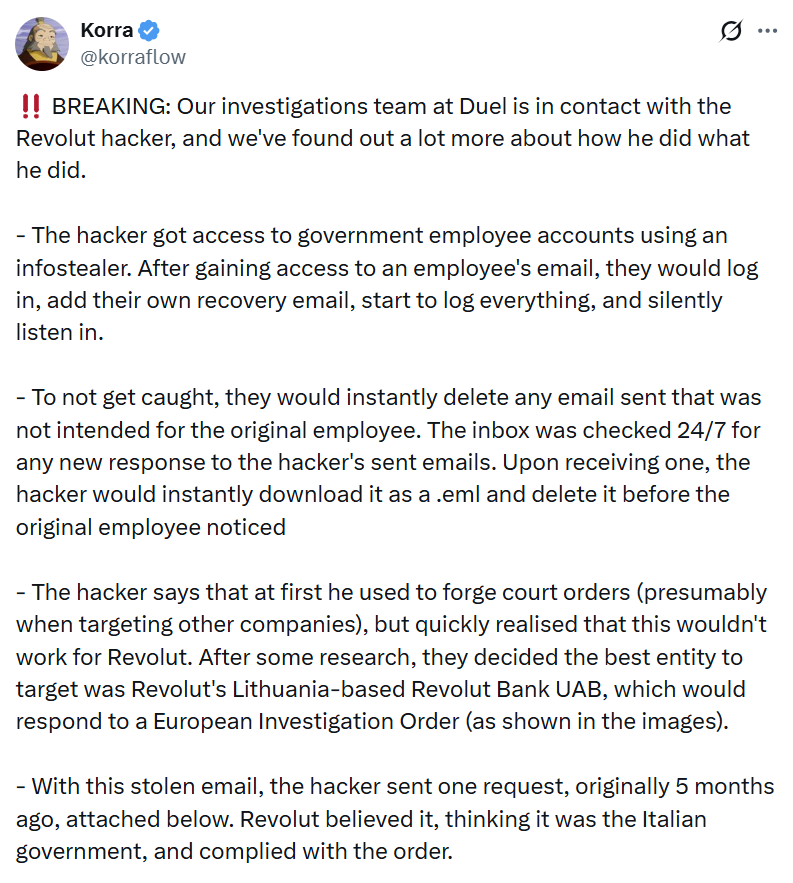
Duel’s investigations team says the hacker behind the Revolut incident used compromised Italian government email accounts, infostealer logs, and careful deletion of traces to sustain a five-month fraud campaign. Hudson Rock’s analysis suggests the attacker likely relied on pre-compromised pec.interno.it credentials rather than directly infecting the victims themselves. #Revolut #RevolutBankUAB #pecinternoit #ItalianMinistryoftheInterior #HudsonRock #Duel

UltraViolet Cyber has launched Equinox, an AI- and automation-driven detection engineering platform that maps customer telemetry and detections against MITRE ATT&CK and MITRE ATLAS to identify coverage gaps quickly. The platform helps SOC teams validate what actually works against their data, improve detection coverage without raising alert volume, and strengthen defense for both traditional and AI-targeted threats. #UltraVioletCyber #Equinox #MITREATTACK #MITREATLAS #TIDE
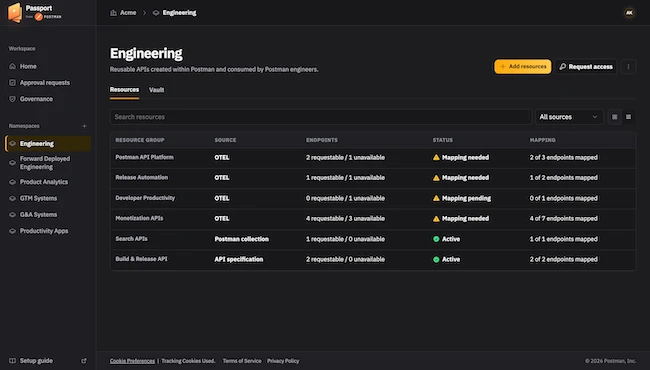
Postman has launched Passport by Postman as a standalone API security product, giving organizations secretless access to approved APIs for both human users and AI agents. The platform keeps real API credentials inside customer environments while providing granular control, full attribution, and fast revocation to reduce exposure from leaked secrets. #Postman #PassportbyPostman #AbhinavAsthana