
The U.S. Justice Department has seized a domain involved in an online fraud scheme that stole millions from Americans via bank account takeover. The scheme involved fake search engine ads and counterfeit banking websites to capture victims’ login credentials. #BankAccountTakeover #CyberFraud…
Category: Cyber Security News
Several cryptocurrency companies were sued by the SEC for running a sophisticated investment scam that defrauded investors of over $14 million using fake social media promotions and AI-generated content. The scam involved manipulated screenshots, false licenses, and fake security token offerings, with stolen funds transferred internationally to Southeast Asia. #SEC #CryptocurrencyFraud…

Aflac suffered a data breach exposing the personal information of over 22 million customers, including Social Security numbers and health data. The attack was linked to the broader threat group Scattered Spider, which has been involved in multiple insurance industry attacks. #ScatteredSpider #Aflac…

ServiceNow plans to acquire cybersecurity firm Armis for $7.75 billion, significantly expanding its security and risk management capabilities. The deal also follows ServiceNow’s recent acquisition of Veza Security, strengthening its position in identity and asset security sectors. #Armis #ServiceNow #VezaSecurity #CybersecurityM&A…
Italy’s competition authority fined Apple €98.6 million for abusing its market position through the App Tracking Transparency (ATT) framework, which creates double consent burdens for developers. Apple plans to appeal, emphasizing its commitment to user privacy and contesting regulatory concerns. #Apple #ATT #AGCM
La Poste’s digital services were severely disrupted due to a major network incident, likely a DDoS attack, affecting millions of customers’ online banking and postal services. The core banking functions remain operational, but many online platforms and services are still offline, impacting nationwide operations. #DDoSattack #LaPoste #GroupeLaPoste

Passwd is a business-focused password manager designed specifically for Google Workspace, emphasizing secure credential storage and controlled sharing within the Google ecosystem. Its features include AES-256 encryption, zero-knowledge architecture, and compliance support through SOC 2 and GDPR readiness. #Passwd #GoogleWorkspace #AES256 #ZeroKnowledge #SOC2 #GDPR…

A global law enforcement effort named Operation Sentinel has dismantled cybercrime networks across Africa, recovering $3 million and arresting 574 suspects. The operation targeted business email compromise, ransomware, and digital extortion, exemplifying the ongoing fight against sophisticated cyber threats in critical sectors. #INTERPOL #OperationSentinel…
A malicious NPM package named ‘Lotusbail’ masquerades as a WhatsApp Web API library and steals user credentials and data. It supports message sending, intercepts all communications, and grants persistent access to attackers, posing a significant security threat. #Lotusbail #NPMmalware…
The US Justice Department has seized a domain and password database linked to a cybercrime group involved in bank account takeovers and large-scale phishing schemes. The operation highlights ongoing efforts to combat financial cybercriminal activities, which have resulted in millions of dollars in losses. #web3adspanels.org #FBI #bankaccounttakeover #phishing #cybercrime…
Nissan disclosed a data breach involving unauthorized access to a Red Hat GitLab instance, which resulted in the theft of personal data of 21,000 customers. The hacking group Crimson Collective claimed to have stolen 570 Gb of data from Red Hat repositories, threatening to extort. #CrimsonCollective #RedHat #NissanFukuokaSales…
Japan has introduced a new five-year cybersecurity strategy emphasizing coordinated government action against state-backed cyber threats. The strategy includes enhancing public-private partnerships and international cooperation to address sophisticated cyberattacks involving AI and critical infrastructure. #JapanCybersecurity #StateBackedAttacks…
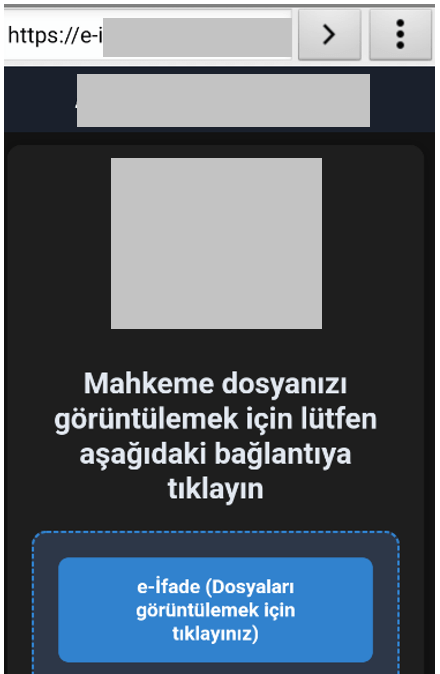
A dangerous Android Trojan named Frogblight has emerged in Turkiye, targeting mobile users through SMS phishing to steal banking information and personal data. The malware uses legitimate-looking apps and government portals to deceive victims, with recent updates increasing its stealth and capabilities. #Frogblight #SMSphishing #Turkiye #MobileBankingThreats…

The U.S. FCC has announced a ban on all drones and critical components made in foreign countries, specifically targeting China-made drones like DJI and Autel Robotics, citing national security risks. This measure aims to protect U.S. airspace from potential threats such as surveillance, data theft, and attacks, especially ahead of major…

A critical vulnerability has been found in the n8n workflow automation platform that allows for potential remote code execution if exploited. Users are urged to update to patched versions to prevent full system compromise. #n8n #CVE-2025-68613…