
The U.S. Justice Department has seized a domain used in a bank account takeover fraud scheme that targeted American victims. This operation highlights the ongoing threat of cybercriminals using fake websites and malicious ads to steal login credentials and drain funds. #BankAccountTakeover #FakeBankSites…
Category: Cyber Security News

A cyberattack caused a major disruption to France’s postal service and online banking during the busy Christmas season, impacting millions of customers. Authorities suspect it may be linked to complex cyber operations involving potential state-sponsored actors, amid ongoing security concerns in France. #DDoS #LaPoste #Russia #CyberattackFrance #EurofiberFrance…

A recent cyberattack exploiting zero-day vulnerabilities in Oracle E-Business Suite has compromised sensitive data of millions, including students and staff at major universities and organizations. The attack, linked to the Cl0p ransomware group and the FIN11 threat group, has led to widespread data exfiltration with several institutions affected. #OracleEBS #FIN11…
Africa’s authorities successfully dismantled multiple cybercrime networks through a major Interpol operation, arresting 574 suspects and recovering $3 million. The crackdown targeted business email compromise, ransomware, extortion, and fraud schemes across several countries, highlighting the continent’s growing cyber threat landscape. #Interpol #CyberCrimeAfrica…
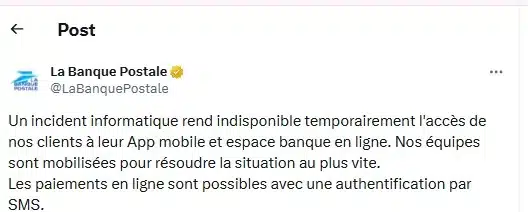
The La Poste cyberattack involved a DDoS incident that disrupted France’s postal and banking services during the busy holiday season. Although customer data was not compromised, the outage caused significant delays and operational challenges. #DDoS #LaPoste #FrenchGovernment #Cyberattack…

Kuaishou Technology, a major Chinese short-video platform, experienced a cyberattack that disrupted livestreaming services and exposed user content, causing a significant decline in its stock price. The incident highlights the increasing operational and security risks faced by social media and live-commerce platforms in the digital landscape. #KuaishouCyberattack #LiveStreamingSecurity…
The Shinhan Card data breach involved the unauthorized disclosure of personal details of around 192,000 merchants, primarily phone numbers and some names. The incident was caused by employee misconduct, not an external cyberattack, highlighting insider risks in financial institutions. #ShinhanCard #InsiderThreats…

Daily Recap, WatchGuard reports a zero-day RCE exploited in the wild affecting over 115,000 Firebox devices, alongside a Somalia e-visa data exposure and Docker releasing hardened open-source images to bolster container security. Daily Recap, RansomHouse upgrades encryption with multi-layered data processing while Nefilim affiliates are implicated, an Android malware campaign combines droppers, SMS theft and RATs, and the U.S. DOJ charges 54 for an ATM jackpotting scheme using Ploutus, with North Korea-linked groups Lazarus, Kimsuky, Bluenoroff and BlueDelta resurfacing and Infy reappearing on the scene. #Firebox #WatchGuard #Somalia #Docker #RansomHouse #Nefilim #Android #Ploutus #Lazarus #Kimsuky #BlueDelta #Bluenoroff #Infy #NorthKorea
The latest version of MacSync, a macOS information stealer, is delivered via a signed and notarized Swift application, marking a significant evolution in evasion techniques. Despite its initial valid signature, the certificate was revoked after a report to Apple, highlighting the ongoing threat. #MacSync #Mentalpositive
Nissan Motor Co. Ltd. experienced a data breach linked to a Red Hat security incident, resulting in the leak of customer information from its Fukuoka sales division. The breach involved the theft of sensitive customer details, but financial data remained secure, and there is no evidence of misuse. #RedHat #CrimsonCollective

A notorious Iranian state-sponsored threat group, “Prince of Persia,” has reemerged with new malware variants and sophisticated command-and-control techniques. Despite perceived silence, they continue to target Iran and Europe using innovative tools like Telegram-based C2 communications. #PrinceofPersia #Tonnerre #Foudre #IranianThreatGroup #CyberEspionage…

Spotify has responded to the public release of a database containing 86 million tracks scraped from its platform by Anna’s Archive, emphasizing their efforts to disable illicit accounts and safeguard artist rights. The incident highlights ongoing challenges in digital music preservation and copyright enforcement. #Spotify #Anna’sArchive…
The Romanian Water Management Authority was targeted by a ransomware attack, impacting around 1,000 systems but leaving critical water operations unaffected. Authorities are working to contain the incident and improve cybersecurity defenses, with ongoing investigations into the attack’s origins. #Lynx #Backmydata
A malicious NPM package called lotusbail impersonates a legitimate WhatsApp Web API library to steal user data and maintain persistent access. Researchers warn developers to remove this package and monitor their WhatsApp accounts for unauthorized linked devices. #WhatsApp #NPMMalware
Operation Sentinel, an Interpol-led initiative, successfully arrested 574 suspects and recovered $3 million linked to cyberattacks such as business email compromise, extortion, and ransomware. The operation involved international law enforcement, dismantled malicious infrastructure, and secured millions in illicit funds, demonstrating heightened global cooperation against cybercrime. #BusinessEmailCompromise #Ransomware #Interpol