This article highlights the evolving cybersecurity landscape, emphasizing that by 2026, security strategies will focus on governance, accountability, and advanced technologies like AI-driven security operations. It warns that traditional security programs will become obsolete, urging CISOs to adopt stricter controls and innovative tools to stay ahead of sophisticated threats. #Ransomware #CybleBlazeAI…
Category: Cyber Security News
Operation PCPcat is a large-scale cyber espionage campaign exploiting vulnerabilities in React frameworks to compromise servers and steal credentials. The attack involves automated scans, exploit chains, and a central C2 server to maintain persistence and expand infection, posing significant risks to modern web infrastructure. #CVE-2025-29927 #CVE-2025-66478 #ReactServers #CredentialTheft #OperationPCPcat…
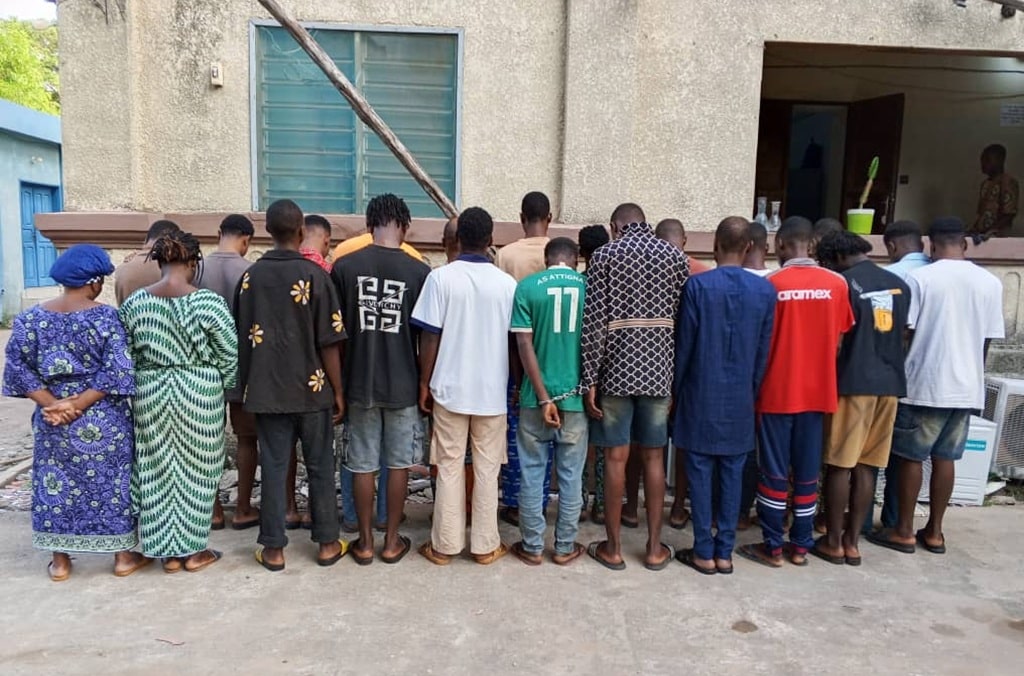
Law enforcement agencies across 19 African countries successfully dismantled cybercriminal networks, arresting 574 suspects and recovering millions. The crackdown targeted business email compromise, digital extortion, and ransomware, highlighting the growing scale of cyber threats in Africa. #OperationSentinel #INTERPOL #cyberattacks #AfricaCyberThreats…

Daily Recap, global cybersecurity incidents disrupted services from banking and postal providers to critical infrastructure, with law enforcement actions and incident responses spanning multiple regions. Highlights include the La Poste DDoS disruption, a guilty plea in the Nefilim ransomware case, BitLocker ransomware affecting Romania’s water agency, and BRICKSTORM backdoor guidance from CISA. #LaPoste #Nefilim

A sophisticated threat group APT-36 is targeting government systems using social engineering tactics that exploit security awareness. The campaign employs deceptive fake advisories and complex malware to establish long-term espionage capabilities. #APT36 #CYFIRMA #EspionageCampaign…
A new cyber-espionage campaign, Operation IconCat, targets Israeli organizations by disguising malicious implants as trusted antivirus updates, leveraging brand reputation and social engineering. The campaign includes two waves: one destructive, one espionage-oriented, linked by similar tactics and tools. #SentinelOne #CheckPoint #OperationIconCat #UNG0801…

The Artemis campaign is a sophisticated cyber-espionage effort by North Korea-linked APT37, targeting individuals by posing as media personnel and delivering malicious HWP files. The operation employs advanced evasion techniques, including legitimate process masquerading and multi-cloud infrastructure, to bypass detection. #APT37 #ArtemisCampaign…
The U.S. Department of Justice disrupted a major bank account takeover fraud operation responsible for over $28 million in unauthorized transfers, seizing a key domain used for managing stolen credentials. The operation relied on fake search engine ads and phishing sites mimicking legitimate banks to steal login information and drain victim…
Microsoft has announced that Teams will automatically enable messaging safety features by default from January 12, 2026, to enhance protection against malicious content. This update includes warning labels for suspicious URLs, blocking dangerous file types, and a report system, helping organizations improve their cybersecurity posture. #Teams #MessagingSafety
Two Chrome extensions called ‘Phantom Shuttle’ are disguising themselves as proxy tools but are actually hijacking user traffic and stealing sensitive data. Researchers warn that these extensions have been active since 2017 and can intercept and exfiltrate personal and business information through hardcoded proxies and malicious code. #PhantomShuttle #SocketDev
WebRAT malware is now being distributed through GitHub repositories claiming to host exploits for recent vulnerabilities, with the malware capable of stealing credentials and spying on victims. The campaign uses fake exploit files to deliver the backdoor and has targeted multiple critical system vulnerabilities. #WebRAT #GitHubMalware
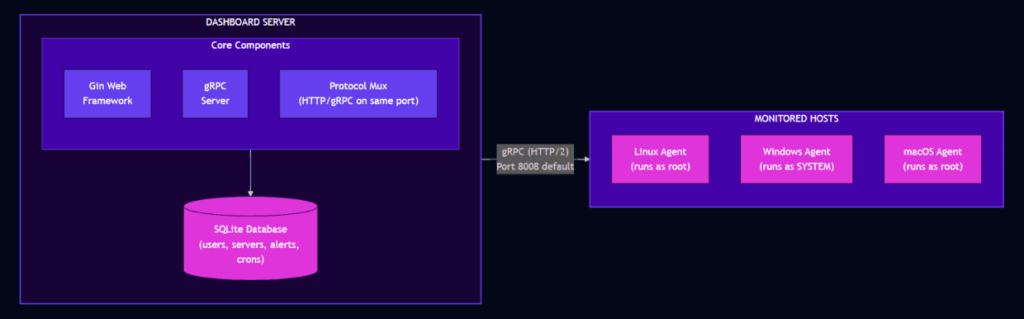
A legitimate open-source tool called Nezha is being exploited by hackers to gain full control over computers through a Remote Access Trojan (RAT). Experts warn that Nezha’s widespread use and ease of deployment make it a significant threat, especially when used to evade detection and maintain persistence. #Nezha #RemoteAccessTrojan…
Romania’s water management system was severely impacted by a ransomware attack affecting around 1,000 systems, though critical operations continued unaffected. The attack exploited Windows’ BitLocker encryption, and authorities advise against negotiating with cybercriminals to prevent further incidents. #RomanianWaters #BitLocker #WaterInfrastructure #Cyberattack #RansomNote…

An international operation resulted in the indictment of Zahid Hasan for running a digital marketplace selling fake government document templates, generating over $2.9 million. This case highlights cross-border collaboration to combat online identity theft and digital fraud. #ZahidHasan #FakeIDTemplates…

Cybersecurity researchers have identified two malicious Google Chrome extensions that impersonate VPN services but are designed to intercept traffic and steal user credentials. These extensions perform man-in-the-middle attacks, exfiltrate data to command-and-control servers, and pose significant risks to users and organizations. #ChromeExtensions #ManInTheMiddleAttack…