Disney has agreed to pay a $10 million civil penalty for mislabeling videos and allowing data collection for targeted advertising, violating the Children’s Online Privacy Protection Act (COPPA). The settlement requires Disney to improve its content labeling and obtain parental consent before collecting children’s data on YouTube. #COPPA #YouTube #Disney #TargetedAdvertising
Category: Cyber Security News
IBM has issued a security warning urging users to patch a critical authentication bypass vulnerability in its API Connect platform, which could allow attackers to access applications remotely without authorization. The flaw affects multiple versions and has a severity rating of 9.8/10, with potentially widespread impacts across industries like banking and healthcare. #CVE-2025-13915 #APIConnect #IBMsecurity

A hacker has claimed to breach the European Space Agency’s systems and is selling stolen data, prompting an ongoing forensic investigation. The attack appears to have compromised a small number of external servers supporting unclassified scientific activities. #BreachedSystems #DataTheft…

Poland has formally asked the European Commission to investigate TikTok for failing to properly moderate AI-generated disinformation promoting “Polexit” and threatening democratic stability. The case emphasizes concerns over synthetic media manipulation and TikTok’s obligations under the Digital Services Act. #Polexit #DigitalServicesAct…

The U.S. Department of the Treasury has removed three individuals linked to the Intellexa Consortium from the sanctions list, raising questions about the reasons for their removal. The Predator spyware, associated with these individuals, continues to pose significant security risks and has been used against civil society globally. #Intellexa #PredatorSpyware…
The Cyber Security Agency of Singapore (CSA) has issued a high-priority alert for a critical vulnerability, CVE-2025-52691, affecting SmarterMail versions Build 9406 and earlier, which could allow remote code execution via arbitrary file uploads. Organizations are urged to update to version Build 9413 or later immediately to mitigate the risk of…
ErrTraffic is a new cybercrime platform that automates ClickFix social engineering attacks to deceive users into downloading malicious payloads. It leverages fake glitches on compromised websites to increase infection success rates, targeting multiple operating systems. #ErrTraffic #ClickFix #Lumma #Vidar #Cerberus #AtomicStealer #LinuxBackdoors

The U.S. Treasury Department has removed sanctions from three individuals linked to Intellexa’s Predator spyware, reversing previous actions taken in 2024. The spyware, used for espionage by governments worldwide, has raised concerns about national security and civil liberties. #Intellexa #PredatorSpyware…
Two cybersecurity experts have pleaded guilty to federal charges for deploying the ALPHV BlackCat ransomware against multiple U.S. companies, highlighting the misuse of cybersecurity skills for criminal purposes. The case underscores the ongoing threat posed by insider threats and ransomware extortion in the cybersecurity landscape. #BlackCat #RansomwareExtortion…
Researchers have uncovered a new campaign called Zoom Stealer, targeting over 2.2 million browser users through malicious extensions that harvest meeting data. The campaign is linked to the China-based threat actor DarkSpectre, which has a history of large-scale espionage and malware campaigns. #DarkSpectre #ZoomStealer
The European Space Agency (ESA) experienced a security breach that compromised external servers containing unclassified engineering data, with threat actors leaking over 200GB of sensitive information. The incident highlights ongoing cybersecurity risks faced by space organizations, emphasizing the importance of proactive defense measures. #ESA #BreachForum

The Cyber Security Agency of Singapore (CSA) warns of a critical security vulnerability (CVE-2025-52691) in SmarterTools SmarterMail that could allow remote code execution through arbitrary file uploads. Users are urged to update to the latest version to mitigate potential exploitation risks. #SmarterMail #CVE202552691…

Two cybersecurity professionals pleaded guilty to conspiracy charges related to orchestrating ransomware attacks on behalf of the ALPHV/BlackCat group, highlighting ongoing threats from cybercriminal gangs. Their actions led to the theft and publication of sensitive data, raising concerns about insider involvement and cyber incident response practices. #ALPHV #BlackCat…
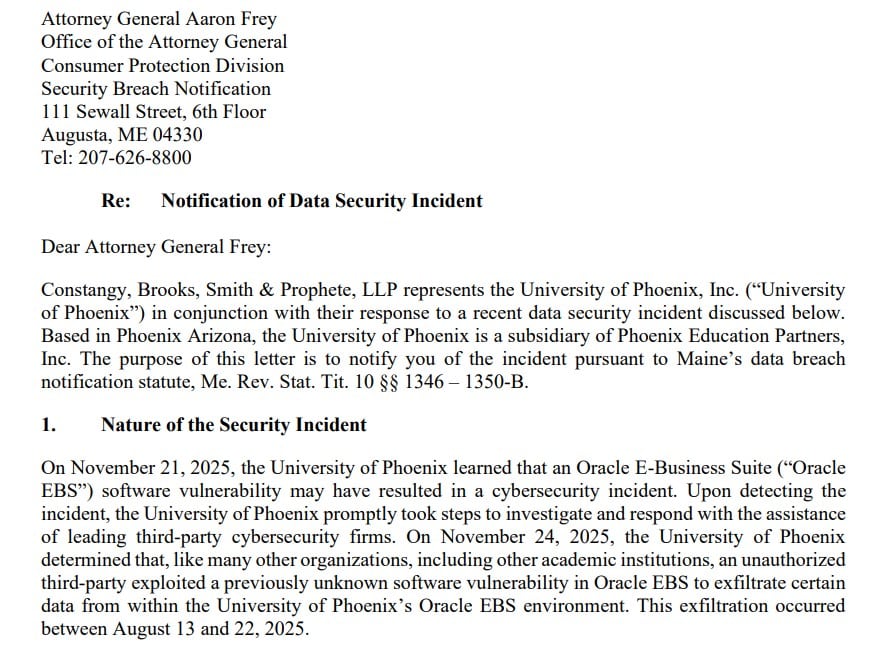
Victims of the CL0P ransomware group’s August campaign, including Korean Air and the University of Phoenix, are still dealing with data breaches affecting millions of individuals. CL0P continues to exploit vulnerabilities in file sharing services, expanding its reach beyond Oracle E-Business Suite. #CL0P #OracleEBS #KoreanAir #UniversityOfPhoenix #Fin11…
The U.S. CISA has mandated government agencies to patch the high-severity MongoDB vulnerability, CVE-2025-14847, which is actively exploited in the wild. The flaw allows attackers to remotely steal sensitive data, and over 87,000 MongoDB servers are potentially vulnerable. #MongoBleed #CVE202514847