
The beginning of 2026 reveals a landscape of subtle and targeted cyber threats, with hackers evolving their tactics even during holidays. Key incidents include malware scams, exploitation campaigns, and backdoored devices, highlighting the increasing sophistication of cyber adversaries. #KMSAuto #ColdFusionExploitation…
Category: Cyber Security News

Modern browsers with feature overload and background processes can hinder productivity, especially for professional users. Using a lightweight, task-focused browser like Adapt Browser enhances speed, minimizes distractions, and streamlines workflows. #AdaptBrowser #BrowserPerformance…

Cybersecurity experts have revealed a nine-month-long campaign targeting IoT devices and web apps, involving the exploitation of React2Shell vulnerability to build the RondoDox botnet. The campaign progressed through advanced phases, including malware deployment and infection persistence tactics, emphasizing the importance of timely updates and network segmentation. #React2Shell #RondoDox #IoTThreats #NextjsVulnerability…

Trust Wallet experienced a major supply chain attack involving the Shai-Hulud malware, leading to the theft of $8.5 million in assets via a compromised Chrome extension. The incident highlights vulnerabilities in software distribution and the importance of secure release processes. #ShaiHulud #TrustWallet #ChromeExtension #SupplyChainAttack…

The HoneyMyte cyber-espionage group has enhanced its toolkit by deploying a sophisticated kernel-mode rootkit to infiltrate government networks in Southeast Asia. This evolution in tactics emphasizes stealth, resilience, and long-term access, utilizing advanced malware like ToneShell and techniques to bypass traditional detection methods. #HoneyMyte #ToneShell…
Trust Wallet suffered a cyberattack involving the Shai-Hulud supply chain breach, resulting in the theft of $8.5 million in assets. White hat security experts actively responded by launching DDoS attacks to limit further damage and protect users. #ShaiHulud #TrustWallet #ChromeWebStore…
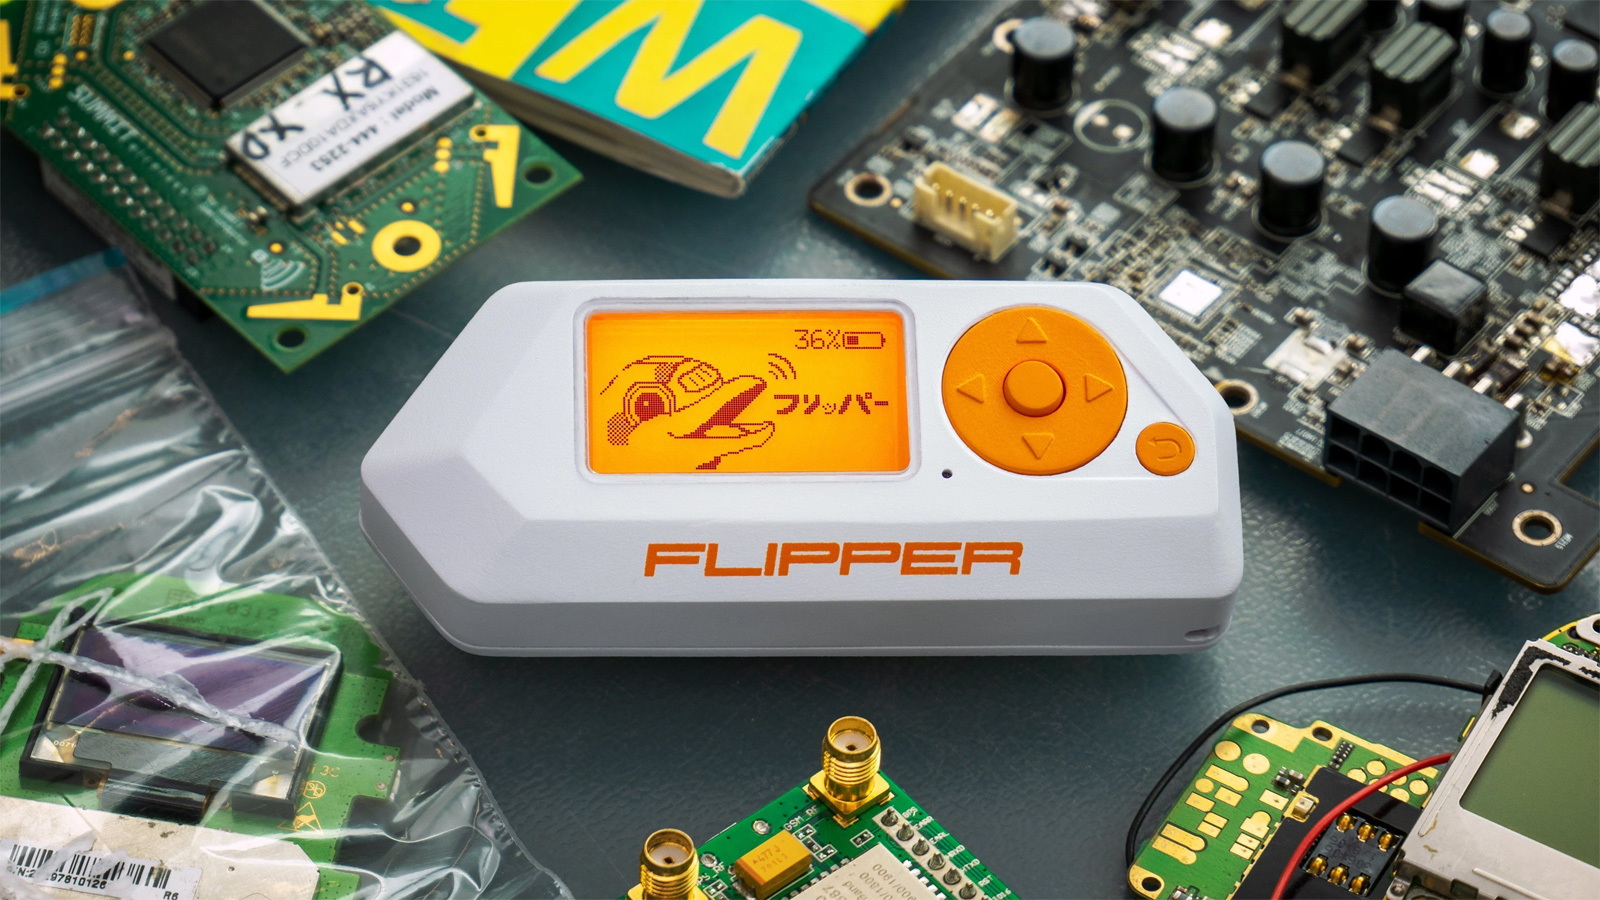
The New York City 2026 mayoral inauguration bans specific electronic devices, namely the Flipper Zero and Raspberry Pi, amid a long list of prohibited items. The exclusion raises questions about security and the reasons behind singling out these particular devices. #FlipperZero #RaspberryPi

Daily Recap, Mustang Panda and allied state‑backed actors used a signed kernel‑mode rootkit to load and hide the ToneShell backdoor while DNS‑poisoning campaigns installed the MgBot backdoor. The roundup highlights MongoBleed exploitation affecting the US and Australia, major breaches at Coupang, Sax, and Korean Air‑supplier data, regulatory fines on NexPublica, MarquisSoftware and Gentlemen ransomware incidents, ValleyRAT phishing infrastructure, KMSAuto campaigns, Trust Wallet theft, and AI/security developments like Copilot GPT‑5.2 in SOC workflows. #MustangPanda #ToneShell #MgBot #MongoBleed #Coupang #Sax #KoreanAir #CNIL #NEXPUBLICA #MarquisSoftware #GentlemenRansomware #ValleyRAT #KMSAuto #TrustWallet

The RondoDox botnet is actively exploiting the React2Shell vulnerability to infect vulnerable Next.js servers and deploy various malware. This ongoing campaign involves large-scale IoT exploitation and targeted attacks by North Korean hackers, affecting thousands of internet-exposed assets. #React2Shell #RondoDox
Unleash Protocol’s decentralized IP platform suffered a $3.9 million theft due to an unauthorized contract upgrade facilitated by a compromised multisig governance system. The stolen assets were anonymized using Tornado Cash, highlighting significant risks in DeFi security and governance controls. #UnleashProtocol #TornadoCash

Cybersecurity experts have identified a new modification of the Shai Hulud malware strain embedded in npm packages, demonstrating increased obfuscation and evasion tactics. Additionally, a malicious Maven package exploiting typosquatting techniques has been taken down, highlighting supply chain security challenges. #ShaiHulud #MavenMalware…

IBM has revealed a critical security vulnerability in API Connect that enables unauthorized remote access due to an authentication bypass flaw. Although not yet exploited in the wild, companies using affected versions are urged to apply security patches promptly. #CVE-2025-13915 #APIConnect…

A Chinese threat actor known as DarkSpectre has launched multiple malicious browser extension campaigns affecting over 8.8 million users across Chrome, Edge, and Firefox for over seven years. These campaigns include data theft, affiliate fraud, and corporate espionage through sophisticated, long-term operations. #DarkSpectre #BrowserExtensions…

Finnish authorities have seized a suspect ship believed to have damaged a subsea telecommunications cable in the Baltic Sea, amid rising concerns over Russian sabotage activities. Recent incidents involve cable faults possibly linked to Russian vessels, prompting increased NATO patrols and investigations into potential sabotage efforts. #SubseaCableDamage #RussianSabotage…

The Shai-Hulud 2.0 worm exploited the NPM ecosystem to leak information and infect packages, leading to a $8.5 million theft from Trust Wallet. This industry-wide supply chain attack affected multiple sectors, highlighting the need for better security measures. #ShaiHulud #TrustWallet #NPM #SupplyChainAttack…