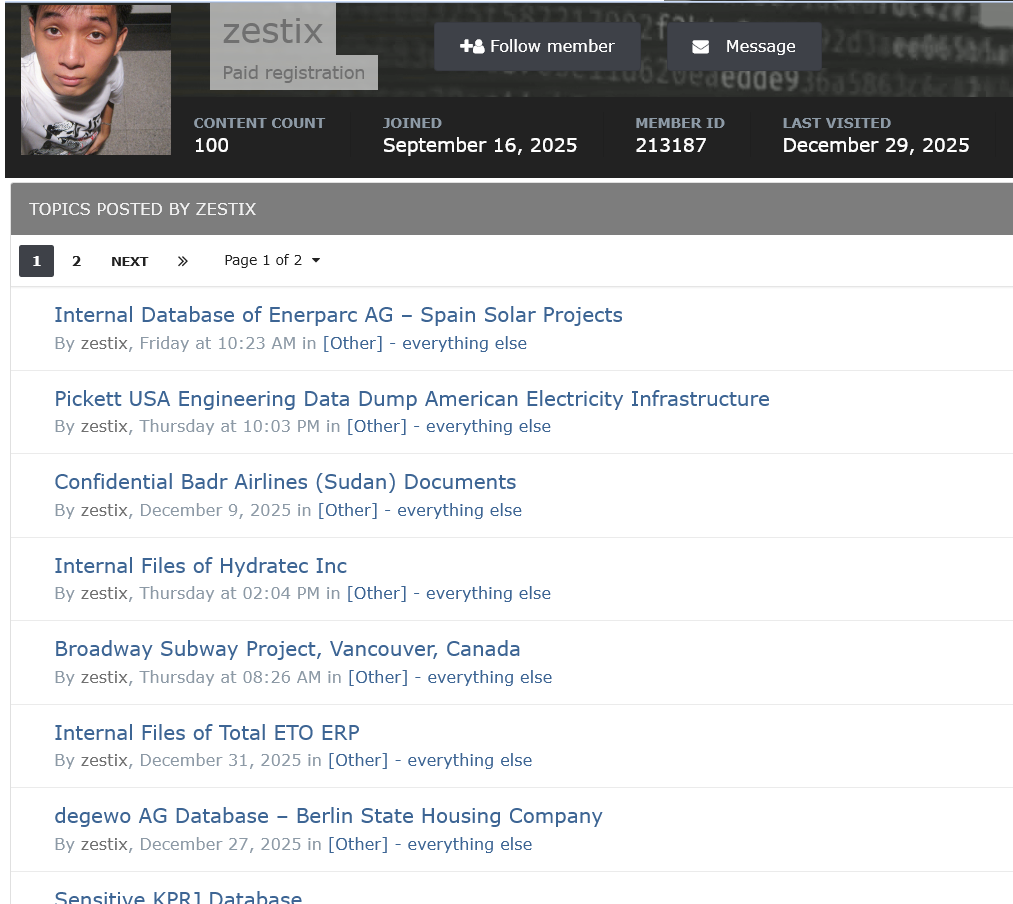
A threat actor named Zestix, also known as Sentap, exploits infected employee devices and weak security practices to access and sell corporate cloud credentials. This campaign highlights the importance of enforcing Multi-Factor Authentication and monitoring for compromised credentials in preventing data breaches. #Zestix #Sentap #Infostealer #ShareFile #Nextcloud
Category: Cyber Security News
NordVPN clarified that the recent data leak involved only dummy data from a third-party test environment, not their core infrastructure. Despite claims of a breach involving sensitive information, the company confirmed no customer or operational data was compromised. #NordVPN #SalesforceSecurity
Agentic AI introduces new identity challenges for security teams, emphasizing the need for lifecycle management and visibility to prevent breaches. Proper governance and correlation of identity signals are critical to ensuring safe and scalable AI deployment. #AgenticAI #IdentitySecurity
Ledger has notified customers about a data breach affecting personal information due to a third-party payment processor, Global-e. The incident exposed customer names and contact details, but did not compromise financial or cryptocurrency wallet information. #Globale #LedgerDataBreach

AI-powered IDEs like Cursor and Windsurf recommend extensions not available in OpenVSX, creating a vulnerability for malicious actors to exploit. Threat actors can claim unclaimed namespaces and upload malicious extensions, posing security risks. #OpenVSX #ExtensionNamespaces

Ilya Lichtenstein, involved in the 2016 Bitfinex hack, has been released early from prison under the First Step Act. He plans to contribute positively to cybersecurity, despite his past criminal activities. #BitfinexHack #CryptocurrencyTheft…

This report highlights the evolving landscape of cybersecurity, emphasizing architecture, trust, and rapid response over traditional point solutions. It discusses advancements in authentication, data security, network visibility, AI-driven defense, human risk management, and supply chain protection. #Yubico #Metomic #Corelight #Axiado #usecure #SecureCo #UnknownCyber #ShadowDragon #CrowdStrike #SentinelOne…

The European Commission is investigating X for inappropriate AI-generated content involving minors, following incidents with its tool Grok. The platform faces potential sanctions amid ongoing legal actions and criticism over harmful and illegal outputs. #Grok #DigitalServicesAct…

A UK high school is temporarily closed due to a cyberattack that disrupted its IT systems, including emails and telephones. Authorities are investigating, and the school has engaged cybersecurity experts to assess and respond to the incident. #RansomwareAttacks #UKEducationSystems…

The Kimwolf botnet has infected over 2 million Android devices through residential proxy networks, mainly targeting cheap Android TV boxes. It has the potential to launch massive DDoS attacks and monetize infected devices by selling proxy bandwidth. #Kimwolf #AndroidTV #DDoS #ProxyNetworks…
The US cybersecurity agency CISA has identified 1,484 vulnerabilities that have been exploited in the wild, with a significant increase in the Known Exploited Vulnerabilities list in 2025. Notable flaws include those exploited in ransomware attacks, such as CitrixBleed 2 and Oracle E-Business Suite, affecting multiple industries and security systems. #CISA…
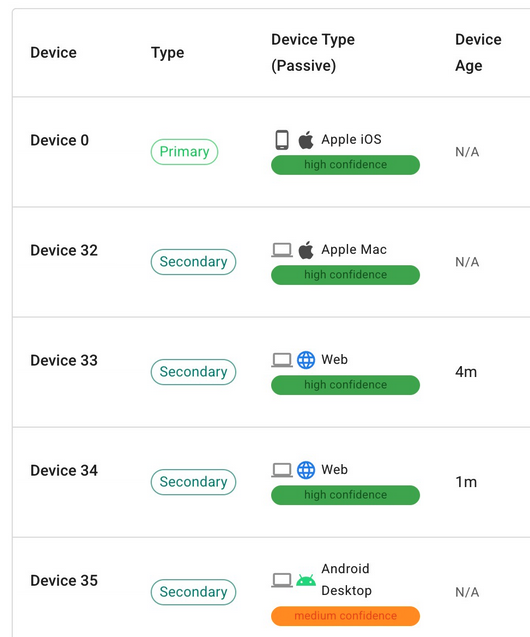
Meta is working to address WhatsApp vulnerabilities related to device fingerprinting and zero-day exploits that allow spyware delivery. Despite some progress, these issues highlight ongoing challenges in protecting user privacy and preventing targeted attacks on the platform. #WhatsAppZeroDay #DeviceFingerprinting…

Cybersecurity experts have uncovered VVS Stealer, a Python-based information thief that targets Discord credentials and browser data. The stealer is sold on Telegram and employs advanced obfuscation to evade detection, showcasing a growing trend of stealthy malware using legitimate tools. #VVS$tealer #TelegramMalware…
A security firm SlowMist identified a critical vulnerability at HitBTC Exchange but received no response after responsible disclosure attempts. This incident reflects ongoing concerns about transparency and security in the cryptocurrency trading sector. #HitBTC #SlowMist #Vulnerability #CryptocurrencySecurity…
IBM has released urgent security updates for a critical vulnerability in IBM API Connect that allows remote attackers to bypass authentication and access sensitive data. This flaw, CVE-2025-13915, affects multiple versions of the platform and is considered highly severe with a CVSS score of 9.8. #CVE-2025-13915 #IBMAPIConnect…