A critical vulnerability in n8n (CVE-2025-68668) allows authenticated users to execute arbitrary system commands through a sandbox bypass in the Python Code Node. This flaw affects all versions before 2.0.0 and has been mitigated in recent releases through architectural changes and security enhancements. #n8n #CVE-2025-68668…
Category: Cyber Security News

The European Commission is investigating Grok, an AI chatbot on X, over the generation of sexually explicit images of minors and its compliance with EU laws. This case highlights ongoing global concerns about the misuse of AI for creating harmful and illegal content. #GrokAI #XPlatform #ChildSexualAbuseMaterial…

Daily Recap, researchers spotlight a WhatsApp metadata leak as Meta begins rolling out fixes to address exposure of message metadata, while ManageMyHealth remains under investigation for a cyberattack affecting its systems and patient services, and IBM API Connect contains a critical authentication bypass that could let attackers impersonate users and access protected APIs; SlowMist flags a potential security risk at HitBTC that could threaten user funds and platform integrity. On the malware/APT front, VVS Stealer targets Discord via obfuscated Python, and Transparent Tribe (APT36) campaigns weaponize JLPT exam notifications to deliver fileless espionage tools against targets in India, with a weekly threat recap for 04 Jan 2026.
#VVSStealer #APT36
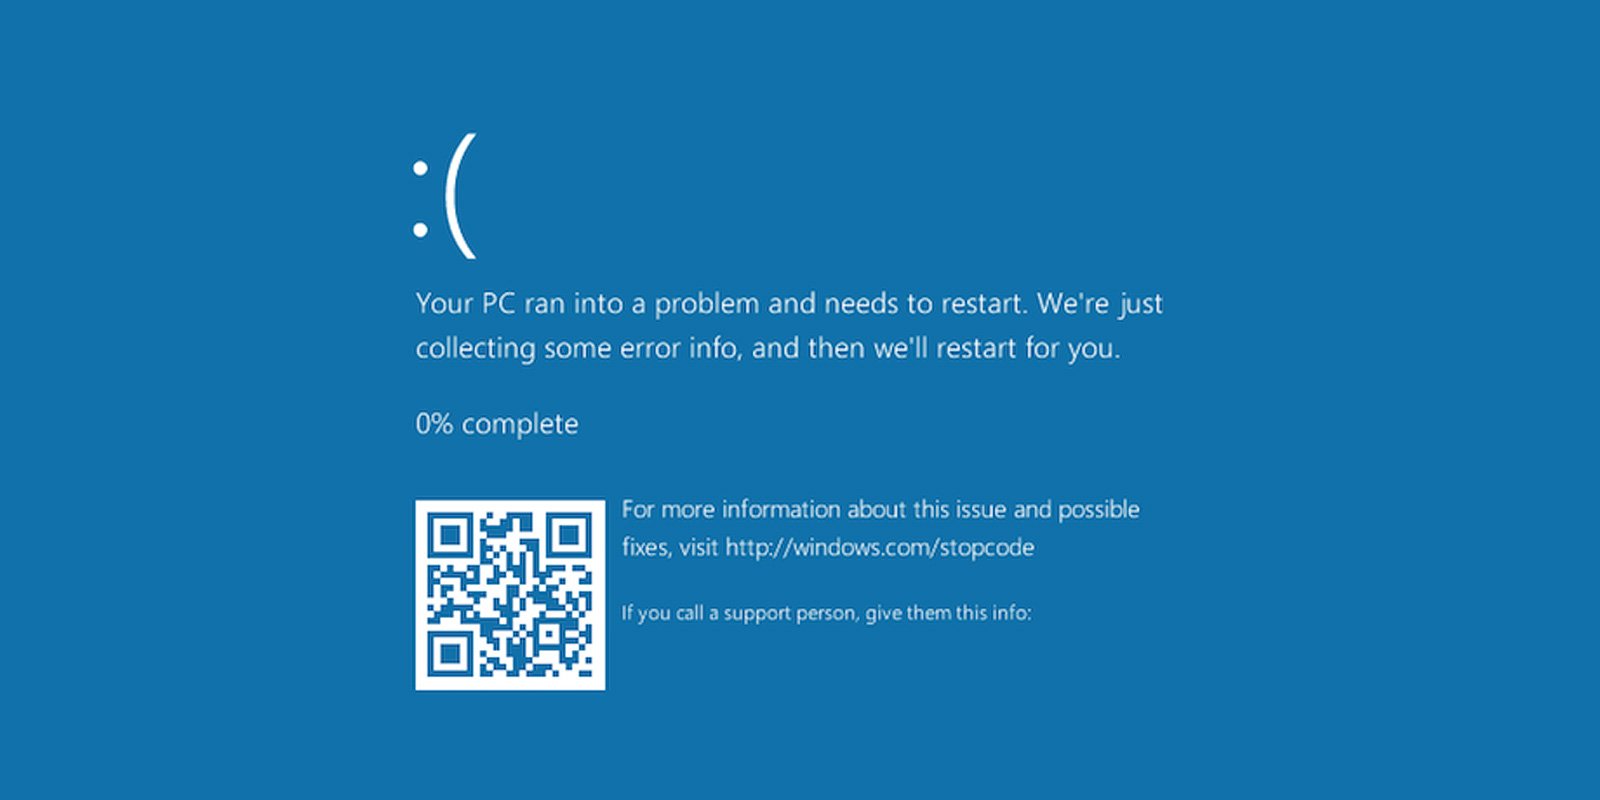
A new ClickFix social engineering campaign targets the European hospitality industry by using fake BSOD screens to trick users into executing malware. This attack involves sophisticated fake websites, fake error messages, and malware deployment for remote access and data theft. #ClickFix #PHALT#BLYX #DCRAT #Booking.com
Threat actor Zestix is selling stolen corporate data from dozens of companies, likely after breaching cloud platforms like ShareFile, Nextcloud, and OwnCloud. The breaches often involve credentials obtained through infostealers such as RedLine, Lumma, and Vidar, highlighting significant security gaps. #Zestix #Infostealers

In 2025, the growth of known exploited vulnerabilities accelerated after a stabilization period, with more vulnerabilities being added to CISA’s KEV catalog than in previous years. Ransomware groups continue to exploit a range of vulnerabilities, particularly targeting major vendors like Microsoft, Oracle, and Fortinet. #CISAKEV #RansomwareVulnerabilities…
Brightspeed is responding to a cybersecurity breach claimed by the Crimson Collective, which alleges to have stolen data belonging to over 1 million customers. The incident highlights ongoing threats from hacking groups targeting ISP providers and corporate data. #CrimsonCollective #Brightspeed #RedHat #AWS #ScatteredLapsus$Hunters
A cybercriminal claims to have stolen sensitive engineering data from Pickett and Associates, a Florida-based utility engineering firm, and is selling it for nearly $585,000 in Bitcoin. The breach involves files related to major American utilities like Tampa Electric, Duke Energy Florida, and American Electric Power, raising concerns about the security…

The Kimwolf botnet has infected over 2 million Android devices by exploiting residential proxy networks and is involved in monetization via app installs, proxy bandwidth sales, and DDoS attacks. Its infrastructure leverages proxy providers like IPIDEA, targeting mainly devices with exposed ADB services, leading to large-scale DDoS attacks and credential-stuffing campaigns….

UAC-0184, a Russia-aligned threat group, targets Ukrainian military and government entities using Viber and other messaging apps to deliver malware. The group employs sophisticated techniques like DLL side-loading and memory injection to evade detection and deploy Remcos RAT for espionage and data theft. #UAC-0184 #Remcos #Hive0156 #HijackLoader #CyberEspionage…
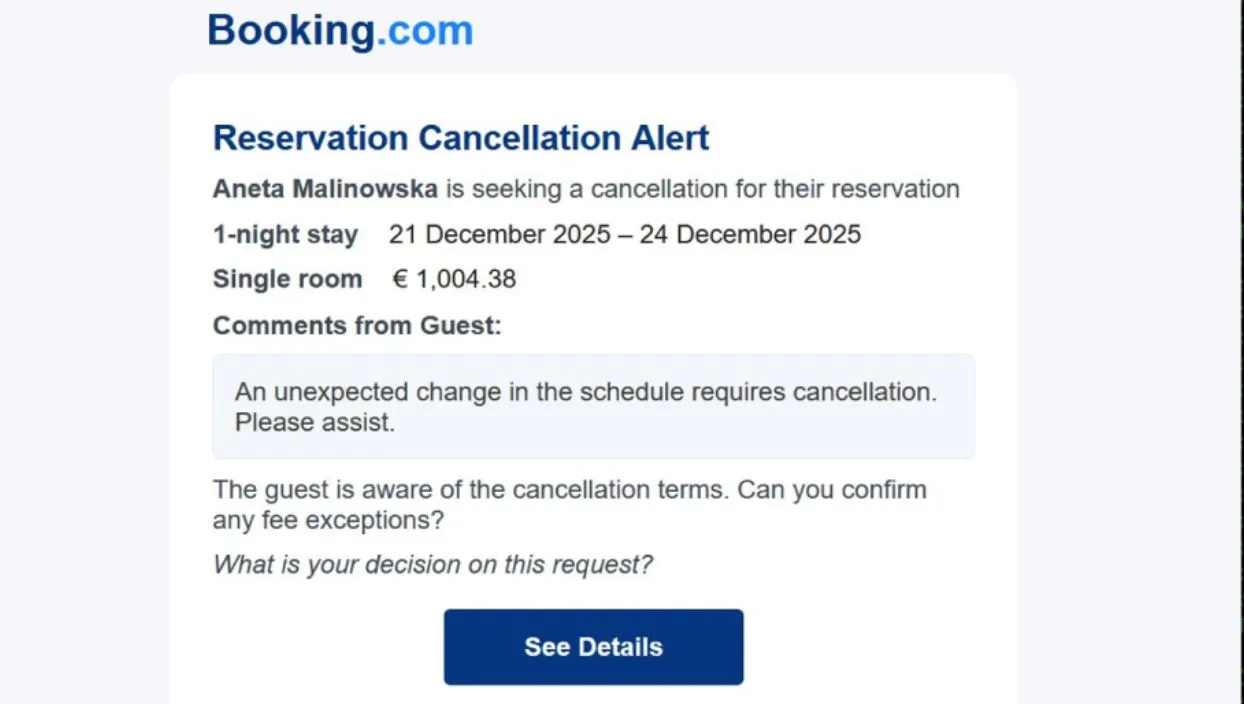
Suspected Russian hackers are using fake error pages and a “Blue Screen of Death” tactic to infect European hotel systems with DCRat malware. This campaign demonstrates advanced social engineering and technical methods to bypass defenses and establish persistent access. #PHALT#BLYX #DCRat…
Sedgwick, a provider of claims services to US government agencies, experienced a cyberattack affecting its isolated file transfer system, with no impact on its broader network. The TridentLocker ransomware group claimed to have stolen and leaked data from Sedgwick Government Solutions. #TridentLocker #SedgwickGovernmentSolutions…
Brightspeed is under investigation after Crimson Collective claimed to have stolen personal data of over 1 million customers. The hacking group’s recent boast highlights ongoing threats to telecommunication providers and their customers. #CrimsonCollective #Brightspeed…

Greece experienced a significant air traffic communication failure that caused widespread flight disruptions, but officials confirmed it was unlikely due to a cyberattack. An investigation is ongoing to determine the exact cause, with several agencies involved. #Eurocontrol #GreekCivilAviationAuthority…

A hacking group, Crimson Collective, has claimed to obtain and released personal data of over a million Brightspeed customers. The data includes sensitive customer information that could facilitate phishing attacks, though no payment or password data was disclosed. #CrimsonCollective #Brightspeed #PersonalDataLeak…