Logitech’s Options+ and G Hub apps on macOS failed due to an expired code-signing certificate, disrupting user customizations and productivity. Logitech released updated versions to fix the issue, emphasizing the importance of timely software updates. #Logitech #Certificates
Category: Cyber Security News
Crimson Collective claims to have breached Brightspeed’s infrastructure, disrupting numerous customers’ home internet services and potentially accessing sensitive data. The group has also attempted to sell the stolen data, raising concerns about targeted phishing and identity theft risks. #CrimsonCollective #Brightspeed #DataBreach…
The UK government has announced a significant cybersecurity strategy with over £210 million to enhance defenses across public sector institutions. The plan includes establishing security standards, incident response improvements, and collaboration with major firms. #CyberActionPlan #NISRegulations
Veeam has issued security updates to address multiple vulnerabilities, including a critical RCE flaw in its Backup & Replication software. The exploitation of these flaws by ransomware gangs highlights the importance of applying patches and following security best practices. #Veeam #CVE-2025-59470
ownCloud urges users to enable multi-factor authentication following reports of credential theft attacks on its platform. The attacks involved infostealer malware like RedLine, Lumma, and Vidar, which compromised user credentials. #ownCloud #HudsonRock #RedLine #CredentialTheft

These vulnerabilities in Columbia Weather Systems MicroServer could allow attackers to hijack connections, gain administrative access, or execute limited shell commands. Security experts recommend remote access restrictions and network segmentation to mitigate these risks. #CVE2025-61939 #CVE2025-64305 #CVE2025-66620 #ColumbiaWeatherSystemsMicroServer…

A critical security flaw in Open WebUI (CVE-2025-64496) allows attackers to hijack user accounts and possibly fully compromise servers. The vulnerability exploits the Direct Connections feature, enabling malicious server connections to execute harmful JavaScript in browsers. #OpenWebUI #CVE202564496…
The UK launches a significant cybersecurity initiative with a £210 million investment to enhance digital public service defenses and establish a dedicated Government Cyber Unit. This initiative aims to improve risk management, incident response, and security standards, aligning government practices with those of critical infrastructure providers. #UKCyberActionPlan #GovernmentCyberUnit…

A critical vulnerability in Dolby audio decoders (CVE-2025-54957) was patched in the January 2026 Android security update, affecting devices including Pixel. Researchers warn this flaw could lead to out-of-bounds write exploits, especially when combined with other vulnerabilities. #DolbyDDplus #AndroidSecurity…

Non-human identities like bots, AI agents, and automation scripts are becoming essential yet risky components of modern enterprise security. Organizations need to treat NHIs as first-class citizens in their security strategies, implementing zero-trust and secrets management practices. #NonHumanIdentities #ZeroTrustSecurity…

n8n, an open-source workflow automation platform, has disclosed a critical security vulnerability (CVE-2026-21877) that could allow authenticated remote code execution, risking full system compromise. Users are urged to update to version 1.121.3 or higher to mitigate this threat and limit exposure. #n8n #CVE21877…

Modern cyber threats increasingly use stealthy techniques that bypass traditional file-based detection methods, creating a significant blind spot for security teams. The webinar will explore advanced tactics like “Living off the Land” and fileless attacks, emphasizing the importance of behavior analysis and zero-trust models. #PowerShell #WMI…

A high school in Britain experienced a cyberattack that disrupted its IT systems, leading to a delay in reopening plans. The school is working with cybersecurity experts and authorities to investigate, with a phased reopening expected soon. #HighamLaneSchool #Cyberattack #Ransomware #InformationCommissioner…
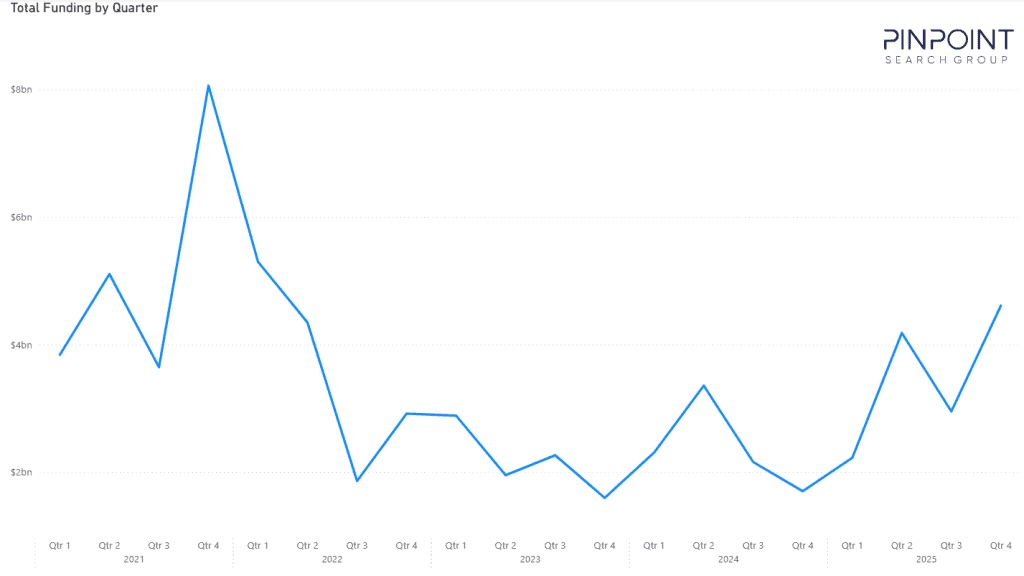
Cybersecurity funding reached nearly $14 billion in 2025, marking a strong rebound after a contraction since 2021, with growth focused on governance, identity, and AI security. Investors are now favoring vendors with proven outcomes, emphasizing strategic links to operational disciplines and evolving buyer needs. #CybersecurityFunding #AIProtection…

Veeam has released an update to patch multiple vulnerabilities in its Backup & Replication solution that could allow remote code execution. Organizations should urgently apply these patches to prevent potential exploitation, especially given the history of threat actors targeting Veeam products. #CVE-2025-59470 #CVE-2025-55125…