The jsPDF library, widely used for generating PDFs in JavaScript, has a critical vulnerability (CVE-2025-68428) that exposes sensitive filesystem data through local file inclusion and path traversal. This flaw specifically affects Node.js versions before 4.0.0, posing a risk of data theft for affected systems. #jsPDF #CVE-2025-68428
Category: Cyber Security News
A new wave of GoBruteforcer botnet malware is targeting exposed databases of cryptocurrency and blockchain projects, exploiting weak server configurations often generated by AI. The malware relies on brute-force attacks on FTP, MySQL, and phpMyAdmin services, mainly compromising Linux servers using default credentials. #GoBruteforcer #AIgeneratedConfigurations
A cybersecurity firm revealed a data breach involving Iberia, where threat actor Zestix stole sensitive aviation and customer data using infostealer malware. The incident highlights ongoing risks from organized cybercriminal groups operating within Russian-language forums. #Zestix #Funksec #Iberia #InfostealerMalware…
Taiwan’s National Security Bureau reports a significant increase in Chinese cyber attacks targeting Taiwan’s critical infrastructure in 2025, with energy and emergency services being primary targets. The coordinated cyber operations are closely linked to physical military activities, highlighting a hybrid threat strategy by China. #ChineseCyberAttacks #TaiwanCriticalInfrastructure…

Cybersecurity researchers have revealed a critical vulnerability in n8n that allows remote attackers to gain full control over affected instances through a content-type confusion flaw. This flaw, tracked as CVE-2026-21858, can enable file access, secret extraction, and remote code execution without requiring authentication. #n8n #CVE-2026-21858…

A cybercrime group called Black Cat is conducting SEO poisoning campaigns by creating fake websites that impersonate popular software to deliver backdoor malware and steal sensitive data. Their activities have compromised hundreds of thousands of hosts in China and have successfully stolen significant amounts of cryptocurrency. #BlackCat #SEOpoisoning…

Cambodian authorities have arrested and extradited Chen Zhi, the head of Prince Group, linked to extensive cyber scam operations and illegal activities across Southeast Asia. This action marks a significant crackdown on the region’s large-scale online crime and money laundering networks. #PrinceGroup #ChenZhi #OnlineScams #Extradition #SoutheastAsia…

A Michigan-based stalkerware company owner pleaded guilty to federal charges for selling spying applications aimed at tracking individuals without their consent. This case marks the first successful prosecution of a stalkerware operator since 2014, highlighting increasing legal actions against such threats. #pcTattletale #BryanFleming…

The Illinois Department of Human Services unintentionally exposed personal information of over 700,000 residents on the internet for up to four years. This breach involved protected health information related to disabled customers and Medicaid/Medicare recipients, with no known misuse reported. #IDHS #DataBreach #HIPAA #PhishingAttack…

Two malicious Chrome extensions impersonating legitimate tools exfiltrated sensitive user conversations and browser data, impacting over 900,000 downloads. These extensions abused hosting infrastructure to steal chat data and URL information, risking corporate and personal security. #ChatGPT #DeepSeekAI #AITOPIA #BrowserSecurity…
This article emphasizes the importance of practical, evidence-based decision-making in cybersecurity, warning against hype, panic, and dismissive attitudes. It highlights how unaccountable advice and trend-chasing can undermine security efforts and trust. #SecurityAdvice #SecurityLeadership…
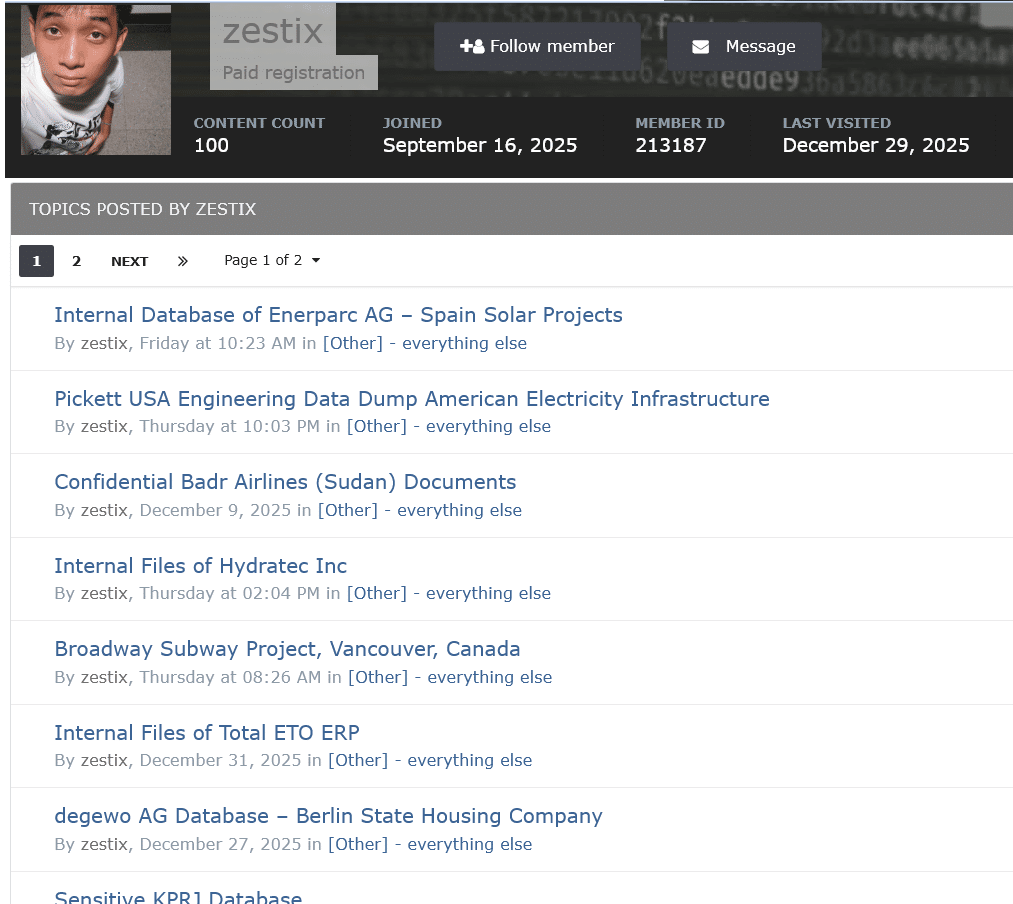
Infostealer malware infections combined with the absence of Multi-Factor Authentication (MFA) have led to numerous data breaches at major global institutions. Threat actors like Zestix and Sentap exploit stolen credentials from infected devices to access critical systems without needing zero-day vulnerabilities. #Zestix #Infostealer…
Hackers are leveraging artificial intelligence as an easy and powerful tool to commit cybercrime without requiring deep technical skills. The rise of “vibe hacking” and AI-branded crime services aims to lower barriers to entry and expand victim pools, normalized by confidence rather than expertise. #AIJailbreaking #HackingGPT
Microsoft is investigating a bug in the classic Outlook client that prevents opening encrypted emails with “Encrypt Only” permissions after a recent update. Microsoft is working on a fix, but temporary workarounds include reverting to an earlier version or saving emails before sending. #OutlookBug #EncryptOnlyEmails
The Ni8mare vulnerability (CVE-2026-21858) impacts the popular open-source automation platform n8n, allowing attackers to gain control over server files without authentication. Researchers highlight the risks of sensitive data exposure and system compromise due to flawed data parsing logic. #Ni8mare #n8n #CVE-2026-21858