A security flaw in the discontinued Totolink EX200 range extender can allow attackers to gain full control over vulnerable devices via an unintentional Telnet interface. Users are advised to restrict access and consider replacing affected devices as no patch is available. #TotolinkEX200 #CERTCC…
Category: Cyber Security News

The telecommunications sector remains a prime target for ransomware attacks, nation-state espionage, and hacktivist disruptions in 2025. Key threat actors include groups like Qilin, Akira, and state-sponsored campaigns, highlighting the need for enhanced security measures. #Qilin #SaltTyphoon…

A critical security flaw in legacy D-Link DSL gateway routers is being actively exploited, allowing remote attackers to execute arbitrary commands. The vulnerability affects several models and is associated with DNS modification behavior known as DNSChanger. #CVE-2026-0625 #D-LinkDSLrouters…
A critical unpatched vulnerability, CVE-2025-65606, affects the TOTOLINK EX200 wireless extender, allowing full remote control through root access via an unauthenticated telnet service. Since the device is end-of-life and no fix is available, users face ongoing security risks and are advised to replace it. #CVE-2025-65606 #TOTOLINKEX200…

CERT/CC has disclosed a critical vulnerability in the TOTOLINK EX200 wireless range extender that could allow authenticated attackers to gain full control via an unintentional root-level telnet service. The flaw, CVE-2025-65606, stems from errors in firmware upload handling and is yet unpatched, raising significant security concerns for affected users. #TOTOLINK #CVE202565606…

Cybersecurity researchers have uncovered malicious Chrome extensions that exfiltrate user chatbot conversations and browsing data to remote servers, posing severe privacy risks. These extensions impersonate legitimate tools, collecting sensitive information that can be exploited for espionage, identity theft, or targeted attacks. #UrbanVPNProxy #PromptPoaching…

The UK government has admitted its cybersecurity strategy has been flawed and announced a new, more centralized approach to protect public services from cyber threats. The plan includes establishing a Government Cyber Unit, improving incident response, and enforcing stricter security contracts, but funding remains a concern. #GCHQ #SynnovisAttack…
This article emphasizes that cybersecurity in 2026 will require a focus on resilience over prevention due to increasing automation and sophistication in cyber threats. Building organizational resilience through governance, technology, and culture is essential for enduring emerging risks like AI manipulation, third-party vulnerabilities, and quantum threats. #CyberResilience #AIThreats…
Katie Paxton-Fear’s hacking journey is deeply influenced by her neurodivergence, especially her autism, which fosters her curiosity and obsession with system disassembly. Her strong moral code and analytical skills underpin her ethical approach to cybersecurity and hacking. #Bugcrowd #CybersecurityPhD…
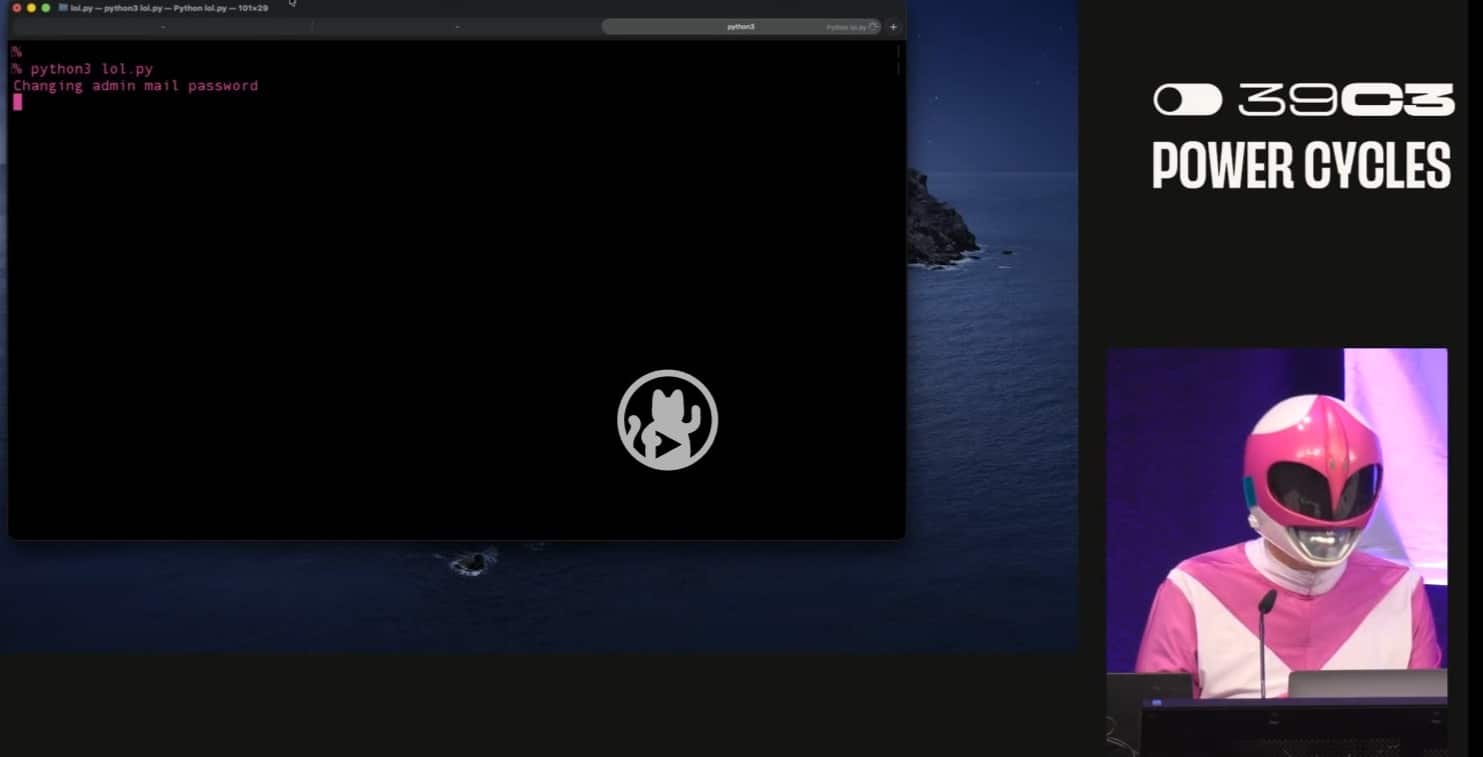
A hacktivist named Martha Root exposed and deleted three white supremacist websites during a conference presentation, revealing poor cybersecurity practices and leaking user data. The incident highlights vulnerabilities in illicit online platforms and the use of AI tools for investigation. #WhiteDate #DDoSecrets…

The Kimwolf botnet, a malware variant targeting Android devices, has infected over two million hosts, primarily exploiting vulnerabilities in residential proxy networks. It is used for DDoS attacks, proxy resale, and app monetization, with most infections in Vietnam, Brazil, India, and Saudi Arabia. #Kimwolf #AndroidVulnerabilities
Threat actors are exploiting a command injection vulnerability, CVE-2026-0625, in outdated D-Link DSL routers to execute remote commands. The flaw impacts unsupported models, emphasizing the importance of replacing end-of-life devices and applying security best practices. #CVE-2026-0625 #D-LinkDSLrouters
Microsoft has canceled plans to implement a daily limit on external recipients for Exchange Online bulk email senders after negative customer feedback. The decision aims to balance security needs with operational usability for Microsoft 365 customers. #ExchangeOnline #SpamPrevention

Taiwan’s National Security Bureau reports a tenfold increase in Chinese cyberattacks targeting the energy sector in 2025, with overall threat activity rising significantly. The attacks included hardware and software vulnerabilities, DDoS, social engineering, and supply-chain incidents, mainly aimed at critical infrastructure and government agencies. #BlackTech #MustangPanda
VVS stealer is a sophisticated Python-based malware targeting Discord users to extract sensitive data using advanced obfuscation techniques. Its capabilities include stealing Discord tokens, hijacking sessions, and extracting web browser information, highlighting the importance of enhanced monitoring for credential theft. #VVSstealer #DiscordTokens…