Microsoft has issued a temporary workaround for Outlook users experiencing freezes after installing recent Windows security updates, affecting Windows 10, 11, and Windows Server platforms. The issue causes Outlook to hang, particularly for POP email users with PST files stored on cloud services like OneDrive, and Microsoft is investigating a permanent fix. #OutlookFreeze #WindowsSecurityUpdates
Category: Cyber Security News

Zoom and GitLab released security updates addressing critical vulnerabilities that could lead to remote code execution, denial-of-service attacks, and 2FA bypasses. The most severe flaw affects Zoom Node Multimedia Routers, while GitLab fixed multiple high-severity flaws impacting its Community and Enterprise editions. #ZoomNodeMMR #GitLabVulnerabilities…
The European Commission proposes new measures to enhance cybersecurity by certifying trusted suppliers and phasing out high-risk foreign vendors, particularly in critical infrastructure. The proposal has sparked tensions with China and the US, highlighting geopolitical and trade concerns surrounding supply chain security. #Huawei #ZTE…

Greek police have dismantled a mobile scam operation using a hidden fake cell tower installed in a vehicle to send phishing messages across Athens. This case highlights the global spread of SMS blaster attacks facilitated by Chinese-manufactured equipment and organized criminal groups. #SMSBlaster #Phishing #GreekPolice #Cybercrime #FakeCellTower…
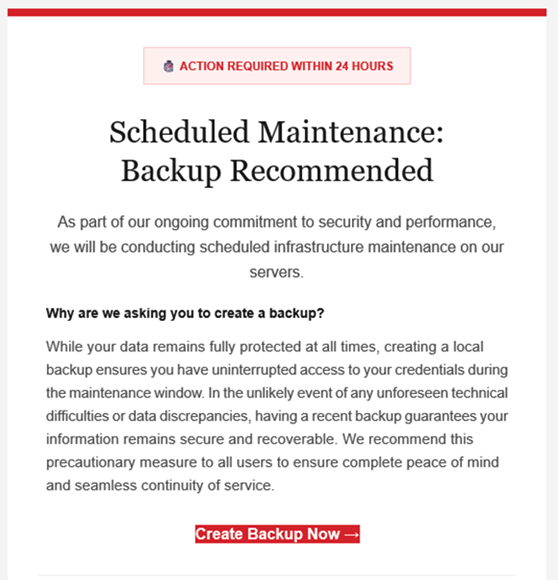
LastPass alerts customers about a new phishing campaign using fake emails to steal master passwords through malicious links. This attack exploits urgency and targets vault backups, continuing the trend of sophisticated social engineering tactics. #LastPass #PhishingEmails…
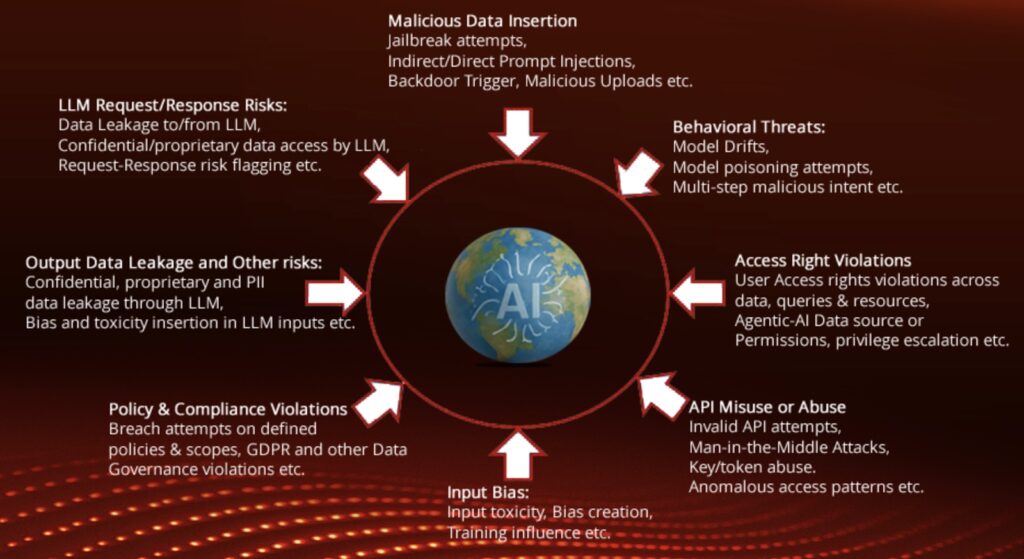
AI security is evolving with aiFWall, a two-way firewall designed to protect agentic AI systems by filtering harmful inputs and outputs. The company emphasizes contextual, just-in-time threat detection and self-learning virus detection, addressing emerging AI-specific threats like PromptLock and attacks from state-sponsored groups. #aiFWall #PromptLock…
Asymmetric Security, a cybersecurity startup specializing in digital forensics and incident response, has emerged from stealth mode with $4.2 million in pre-seed funding. The company utilizes AI to automate investigations, analyze attack data, and assist responders, aiming to enhance defenses against AI-driven threats. #AsymmetricSecurity #AIInCybersecurity…
A critical vulnerability in the Advanced Custom Fields: Extended plugin for WordPress could allow attackers to take full control of affected websites without authentication. This flaw, assigned a severity of 9.8, is primarily a privilege escalation issue involving improper user role validation during registration. #WordPress #AdvancedCustomFields…
Security researchers successfully exploited multiple zero-day vulnerabilities in automotive and charging systems during the Pwn2Own Automotive 2026 competition, earning over half a million dollars in rewards. These findings highlight the critical need for timely security updates in connected vehicle technologies and charging stations. #TeslaInfotainment #ZeroDayVulnerabilities

Security vulnerabilities in the open-source AI framework Chainlit, known as ChainLeak, can lead to data leaks and lateral movement within organizations. These flaws, addressed in version 2.9.4, highlight the growing security risks associated with AI infrastructure and third-party components. #Chainlit #ChainLeak #CVEs #AIvulnerabilities #ServerSideRequestForgery…

Gartner has introduced the Exposure Assessment Platforms (EAP) category, signaling a shift away from traditional Vulnerability Management toward Continuous Threat Exposure Management (CTEM) for better security. The new approach consolidates environment discovery, prioritizes based on context, and guides targeted remediation efforts to reduce attack paths and improve risk posture. #XM Cyber…

Managed security providers are adopting AI to transform service delivery, achieve higher margins, and meet client demands with fewer resources in 2026. AI automation is enabling MSSPs to standardize, scale, and provide CISO-level protection without increasing headcount. #AI #MSSP #CybersecurityServices…
This article discusses the growing importance, proliferation, and security challenges of Application Programming Interfaces (APIs) in the context of AI advancements and cyber threats. It highlights how the rapid increase in APIs, especially with autonomous AI systems, expands the attack surface, making effective security measures more critical than ever. #SesameOp #OpenAIAPI…
MITRE has launched the Embedded Systems Threat Matrix (ESTM), a cybersecurity framework aimed at protecting critical embedded systems across various industries. The framework is designed to map attack tactics and techniques specific to hardware and firmware environments, improving vulnerability identification and security practices. #ESTM #MITRE #embeddedsecurity…
Multi-factor authentication (MFA) is widely adopted and effective but not foolproof against modern cyber threats like phishing and social engineering. Organizations are increasingly turning to advanced, phishing-resistant authentication methods and identity threat detection to strengthen security. #FIDO2 #YubiKey…