
The Everest ransomware group has claimed to have breached McDonald’s India, exfiltrating 861 GB of sensitive data including customer and internal documents. The authenticity of these claims remains unverified, and further investigation is ongoing. #EverestRansomware #McDonaldsIndia…
Category: Cyber Security News

These vulnerabilities in Rockwell Automation Verve Asset Manager could allow attackers to access sensitive data stored in environment variables and during playbook execution. The issues impact various versions and are associated with insecure storage practices—highlighting the importance of securing industrial control systems. #RockwellAutomation #VerveAssetManager…
Two critical vulnerabilities in the open-source AI framework Chainlit pose significant security risks, including data leaks and full system takeovers. Organizations using Chainlit should update to the patched version 2.9.4 to mitigate these threats. #Chainlit #CVE-2026-22218 #CVE-2026-22219 #AIFrameworkSecurity…
Anthropic has fixed three vulnerabilities in its Git MCP server that could be exploited through prompt injection and chaining with other MCP tools for remote code execution. Researchers warn that as agentic AI systems become more complex, the attack surface increases, requiring careful security assessments. #Anthropic #GitMCP #PromptInjection #AgenticAI #CodeExecution…

A security vulnerability in the binary-parser npm library could allow attackers to execute arbitrary JavaScript code through untrusted input. Users are urged to update to version 2.3.0 to mitigate the risk. #CVE-2026-1245 #binaryparser…

LastPass warns users about a new phishing campaign impersonating their service to steal master passwords. The attack involves fake emails claiming maintenance, directing users to malicious sites. #LastPass #PhishingCampaign…
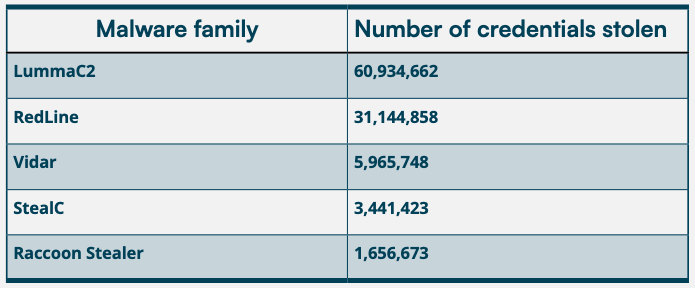
Despite ongoing security efforts, users continue to use simple and default passwords like ‘123456’ and ‘admin’, leaving critical systems vulnerable. The report highlights the persistent risk posed by reused, predictable credentials in enterprise environments, often exploited by malware and threat actors. #Lumma #RedLine…

This article highlights the increasing cyber threats faced by healthcare organizations in 2025, emphasizing the need for enhanced cyber resilience strategies. It discusses the importance of Zero Trust, AI, supply chain vigilance, and leadership accountability in strengthening cybersecurity in healthcare. #CyberResilience #HealthcareSecurity #AI #ZeroTrust #SupplyChainSecurity…
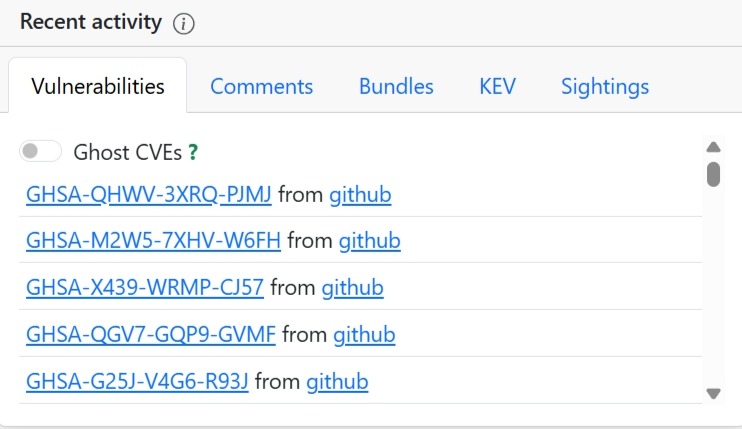
The EU has launched the GCVE vulnerability platform to enhance digital sovereignty and reduce dependence on centralized systems like CVE. This decentralized database aggregates data from multiple sources and provides open API access, supporting Europe’s cybersecurity independence. #GCVE #DigitalSovereignty…
The UK’s NCSC warns that Russian-aligned hacktivist groups are intensifying their disruptive cyberattacks on British organizations, particularly targeting critical infrastructure and local government. Organizations are advised to strengthen their defenses against denial-of-service (DoS) attacks and improve resilience through practical mitigation measures. #NoName05716 #DDoSia #UKNCSC…
The UK is exploring the possibility of banning social media for children aged 15 and under, inspired by Australia’s recent law. This initiative aims to improve children’s online wellbeing through measures like stricter age verification and platform restrictions. #Australia #SocialMediaBan #ChildrenOnlineSafety…

Daily Recap, The daily cybersecurity recap emphasizes proactive defence for 2026 with CISOs prioritizing attack surface visibility and threat hunting, while noting the ETSI AI security standard and Olympics-linked cyber risk as more connected environments emerge. The summary also highlights high-profile items across malware and threats, including Black Basta leadership and an INTERPOL Red Notice, the LOTUSLITE backdoor tied to a Mustang Panda campaign targeting the U.S. government, and notable vulnerabilities and incidents such as StealC, TamperedChef ads, RondoDox using an HPE OneView flaw, Windows Cloud PC bugs, GhostPoster extensions, the CIRO data breach, a Supreme Court hack, Iran TV hijack, and OpenAI ads. #BlackBasta #MustangPanda
Researchers demonstrated how to bypass Google Gemini’s defenses using natural language instructions to leak private calendar data via malicious calendar invites. The attack exploits Gemini’s automatic data parsing and reasoning capabilities, enabling sensitive information exfiltration without triggering security alerts. #GoogleGemini #PromptInjection
The European Commission has proposed new cybersecurity legislation aimed at removing high-risk foreign suppliers and enhancing defenses against cyber threats targeting critical infrastructure. This legislation seeks to strengthen Europe’s technological sovereignty and improve the security of ICT supply chains and telecommunications networks. #Huawei #ZTE #ENISA #CybersecurityAct #EUCriticalInfrastructure

The VoidLink malware framework is an advanced Linux-based tool developed with significant AI assistance, likely by a single proficient developer. Its rapid development and sophisticated features demonstrate a new era of AI-driven malware creation. #VoidLink #AIDrivenMalware