
Ingram Micro confirmed more than 42,000 people had personal and employment data stolen after a July 2025 ransomware attack that paralysed its logistics systems for about a week. Attackers accessed internal file repositories between July 2–3, 2025, the intrusion was discovered on December 26, 2025, and the company is offering two…
Category: Cyber Security News

Daily Recap, WordPress ACF plugin vulnerabilities put thousands of sites at risk, with one add-on affecting 100,000 sites and another flaw giving admins access on 50,000 sites. The roundup also notes patches for Zoom and GitLab addressing RCE and a high-severity 2FA bypass, a Cloudflare WAF bypass via the ACME path, AI-generated threats like VoidLink, and malware campaigns such as PDFSider and LinkedIn RAT. #VoidLink #PDFSider
PcComponentes, a leading Spanish retailer, has denied a major data breach but confirmed a credential stuffing attack affecting some customer accounts. The incident involved leaked order details and personal data from compromised accounts, prompting enhanced security measures. #CredentialStuffing #InfostealingMalware
A new Android click-fraud Trojan family utilizes TensorFlow.js for visual analysis, bypassing traditional script-based methods. The malware is distributed through Xiaomi’s GetApps store, third-party APK sites, and Telegram channels. #TensorFlowJS #ClickFraudTrojan
Cisco has addressed a critical remote code execution vulnerability, CVE-2026-20045, exploited in active attacks, impacting multiple Unified Communications products. Urging urgent updates, Cisco and CISA highlight the severity of the flaw, which allows attackers to gain root access. #CVE-2026-20045 #CiscoUnifiedCommunications
Two critical vulnerabilities in the Chainlit framework, dubbed ‘ChainLeak,’ enable attackers to read sensitive files and execute server-side request forgery, posing a serious threat to internet-facing AI systems. Organizations using Chainlit are urged to update to version 2.9.4 or later to mitigate risks. #ChainLeak #CVE-2026-22218 #CVE-2026-22219 #Chainlit
A widespread spam wave exploits unsecured Zendesk support systems, flooding users with alarming and bizarre emails. Companies like Dropbox, 2K, and Discord were affected, highlighting vulnerabilities in support platform security. #ZendeskRelaySpam #UnsecuredSupportSystems

This article discusses the Contagious Interview campaign linked to North Korean threat actor PurpleBravo, which has targeted over 3,000 IP addresses across multiple sectors in various regions. It highlights the use of malicious code, fake job offers, and sophisticated infrastructure to conduct cyber espionage and financial theft, emphasizing the vulnerabilities in…

CyberNut secures $5 million in funding to expand its AI-driven cybersecurity awareness platform for K-12 schools. The investment aims to accelerate product development and broaden its reach to protect educational institutions from phishing and social engineering threats. #CyberNut #AIThreatDetection…
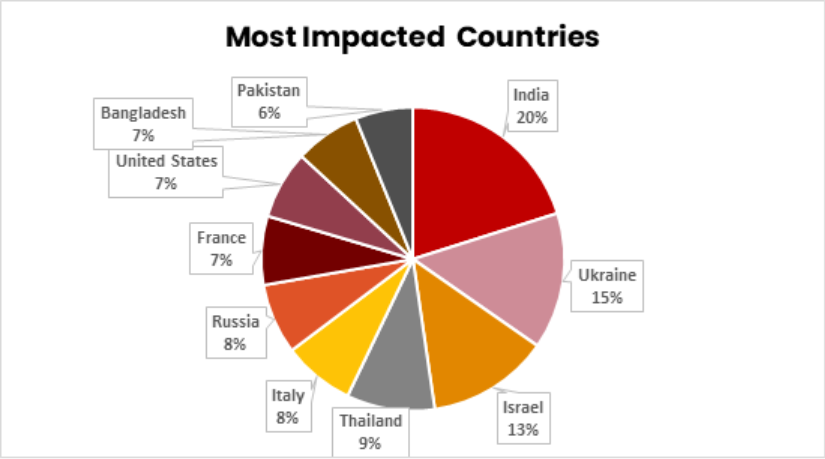
Hacktivists in 2025 shifted their focus from DDoS and defacements to targeting critical infrastructure, including ICS and IoT systems, with increased sophistication and alignment with nation-states. The threat landscape is expected to intensify in 2026, with more attacks on vulnerable OT and HMI systems, driven by geopolitical motives and automated scanning…

The European Commission proposes new legislation to enhance cybersecurity of the EU’s ICT supply chains by excluding high-risk suppliers, especially from countries like Russia and China. The reforms aim to increase supply chain security, streamline certification processes, and expand cybersecurity protections across critical sectors. #Huawei #Russia #China #ENISA #NIS2Directive…
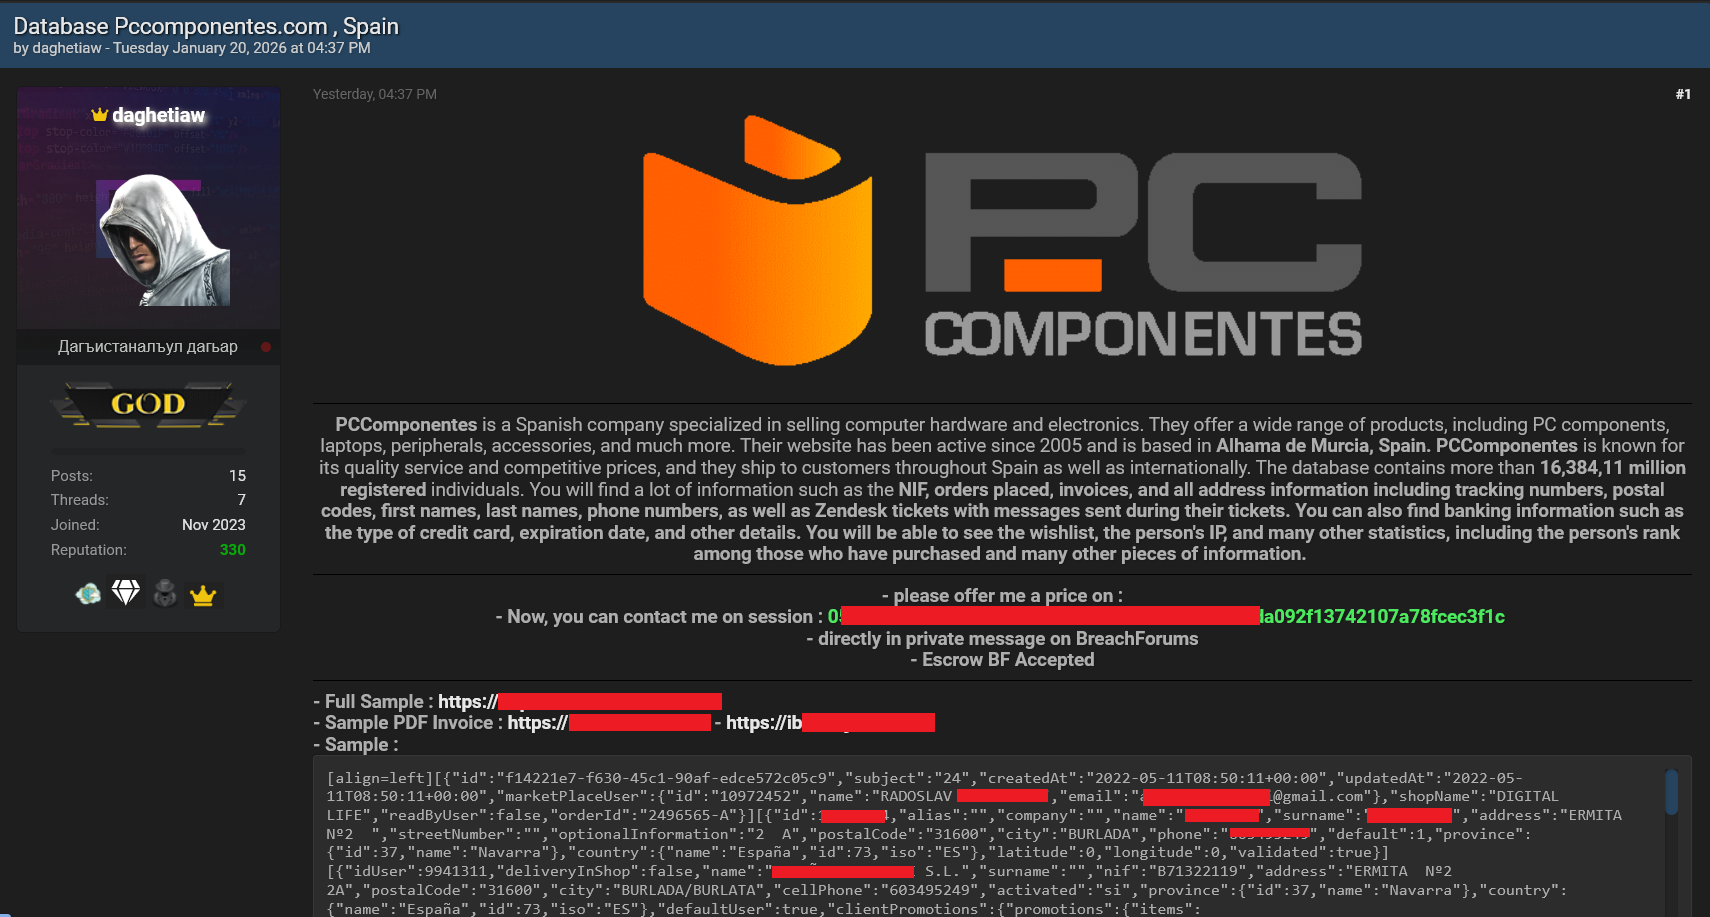
A recent incident involving Pccomponentes demonstrates how threat actors weaponize Infostealer logs to create convincing “fake breaches” that cause significant PR damage. Monitoring and early detection of credential theft from infected devices could have prevented this incident. #InfostealerLogs #CredentialStuffing
GitLab has issued security patches for multiple high-severity vulnerabilities, including a critical two-factor authentication bypass and flaws allowing denial-of-service attacks. The platform’s widespread use by Fortune 100 companies highlights the importance of immediate updates to mitigate risks. #GitLab #CVE-2026-0723 #DevSecOps
Cybercriminals are actively exploiting misconfigured web applications used for security training to compromise cloud environments of Fortune 500 companies, deploying crypto miners and webshells. Major cloud providers like AWS, GCP, and Azure are affected, with many exposed systems still using default credentials and overly privileged roles. #DVWA #OWASPJuiceShop
Even experienced cybersecurity professionals can fall victim to sophisticated phishing attacks due to human factors like distraction and emotional state. Modern phishing tactics leverage AI, automation, and an industrialized ecosystem to deceive users at scale. #PhaaS #PhishGPT