
SecurityWeek and Abnormal AI will host a live webinar on January 22, 2026 at 1PM ET to discuss the state of email security and how organizations can better defend against evolving threats. The session will emphasize behavioral analysis, real-time risk evaluation, and AI-driven adaptive models as essential tools to detect sophisticated…
Category: Cyber Security News
TU Graz researchers have revived Linux page cache attacks and demonstrated they are far more practical and dramatically faster than prior work, affecting kernel versions from 2003 to the present. The techniques enable precise password-prompt detection, synchronized phishing overlays, inter-keystroke timing, cross-container spying in Docker, and site-identification via Firefox resources, and…
The article compares Stranger Things’ Upside Down to modern enterprise attack surfaces, warning that unmanaged IT, OT, IoT, and cloud assets act as unseen portals for threats like the Mind Flayer and Demogorgon. It calls for continuous visibility, remediation prioritization, IT/OT segmentation, and cross-functional teamwork to detect and stop threats before…

A critical Fortinet SSO vulnerability, CVE-2025-59718, is being actively exploited against systems believed to be patched, with breaches reported on FortiOS 7.4.9. Administrators are urged to disable FortiCloud SSO via CLI and audit for unauthorized forticloud-sso logins, new admin accounts, and configuration exports to mitigate the persistent “Zombie” vulnerability. #CVE-2025-59718 #FortiOS…
The Bank of England’s CBEST assessments found widespread failures in basic cyber hygiene across financial firms and financial market infrastructures, with gaps in patching, hardening, identity and access control, detection, encryption, network security, incident response, and staff training. The report urges firms to address root causes through sustained measures—such as stronger…

Cisco patched a critical zero-day remote code execution vulnerability tracked as CVE-2026-20045 (CVSS 8.2) that is being actively exploited and affects Unified CM, Unified CM SME, IM & Presence, Unity Connection, and Webex Calling Dedicated Instance. An unauthenticated remote attacker can send crafted HTTP requests to the web management interface to…
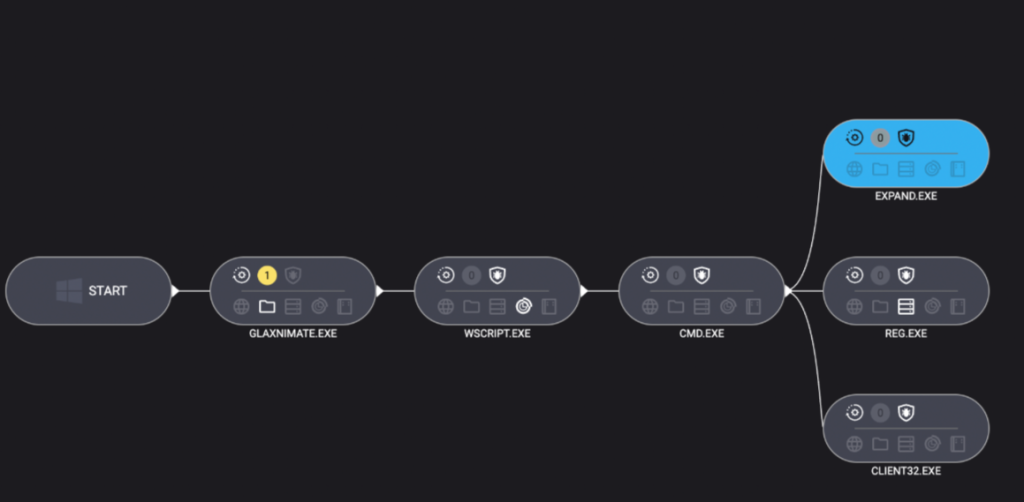
Remcos and NetSupport Manager were deployed via a multi-stage infection chain that relied exclusively on Windows built-in utilities (LOLBins) to evade detection and persist. The attack used forfiles, mshta, PowerShell curl and tar, scripting engines, and stealthy registry persistence before Malwarebytes detected and blocked the intrusion. #Remcos #NetSupportManager…

A critical authentication bypass in SmarterTools’ SmarterMail (tracked as WT-2026-0001) is being actively exploited shortly after a patch, allowing unauthenticated requests to reset any administrator password via the /api/v1/auth/force-reset-password endpoint. The flaw can be chained to achieve SYSTEM-level remote code execution through the product’s Volume Mount Command feature, and watchTowr Labs…

A malicious PyPI package named sympy-dev impersonating SymPy has been found to deliver a cryptomining payload that downloads and executes ELF binaries on Linux hosts. The backdoored polynomial routines fetch a remote JSON configuration and an ELF payload from a threat-actor server (63.250.56.54) then launch XMRig in memory using memfd_create and…
Cisco released patches for a critical zero-day, CVE-2026-20045, that affects multiple unified communications products including Unified Communications Manager, Unity Connection, IM & Presence, and Webex Calling Dedicated Instance. The flaw allows unauthenticated remote attackers to execute commands and escalate to root via specially crafted HTTP requests, and CISA has added it…
Atlassian, GitLab, and Zoom released security updates this week addressing more than two dozen vulnerabilities across multiple products. Administrators are urged to apply these patches promptly to remediate critical and high-severity flaws, including CVE-2026-22844 and several third-party dependency issues. #Atlassian #Zoom…

Cybersecurity startup Furl raised $10 million in seed funding led by Ten Eleven Ventures to prepare broader availability of its AI-driven vulnerability remediation platform. The Los Angeles-based company, founded by veterans of Rapid7, Automox, and Censys, uses agentic AI to ingest tool data, investigate context, and autonomously execute remediation to reduce…

Cisco released urgent patches for a critical zero-day vulnerability (CVE-2026-20045) in multiple Unified Communications products and Webex Calling Dedicated Instance that allows unauthenticated remote attackers to execute arbitrary OS commands and escalate to root. There are no workarounds, the flaw is being actively exploited in the wild and CISA added it…

Arctic Wolf warns of a new cluster of automated malicious activity beginning January 15, 2026, that involves unauthorized configuration changes on Fortinet FortiGate devices. Threat actors exploited CVE-2025-59718 and CVE-2025-59719 to bypass FortiCloud SSO, create persistent admin accounts, export firewall configurations, and grant VPN access; operators are advised to disable admin-forticloud-sso-login….
A Vodafone Business survey finds many UK firms remain poorly prepared for a major cyberattack, with widespread gaps in training, weak password practices, and high exposure to phishing and AI-driven deepfake scams. While awareness has risen after high-profile incidents, fewer than half of businesses have basic cyber-awareness training in place, and…