
A Virginia federal judge ruled that the warrantless use of 176 Flock automated license plate reader cameras in Norfolk is constitutional and dismissed the plaintiffs’ Fourth Amendment challenge. The court found the camera network not sufficiently pervasive to constitute unconstitutional tracking, and the Institute for Justice said it will appeal. #FlockSafety…
Category: Cyber Security News

Zscaler ThreatLabz uncovered two recent cyberespionage campaigns—Gopher Strike and Sheet Attack—targeting Indian government entities and deploying custom Golang tools while using legitimate infrastructure to evade detection. The operations introduce new malware like GOGITTER, GOSHELL, and GITSHELLPAD and suggest experimentation with generative AI, pointing to a possible Pakistan-linked subgroup. #GopherStrike #GITSHELLPAD…
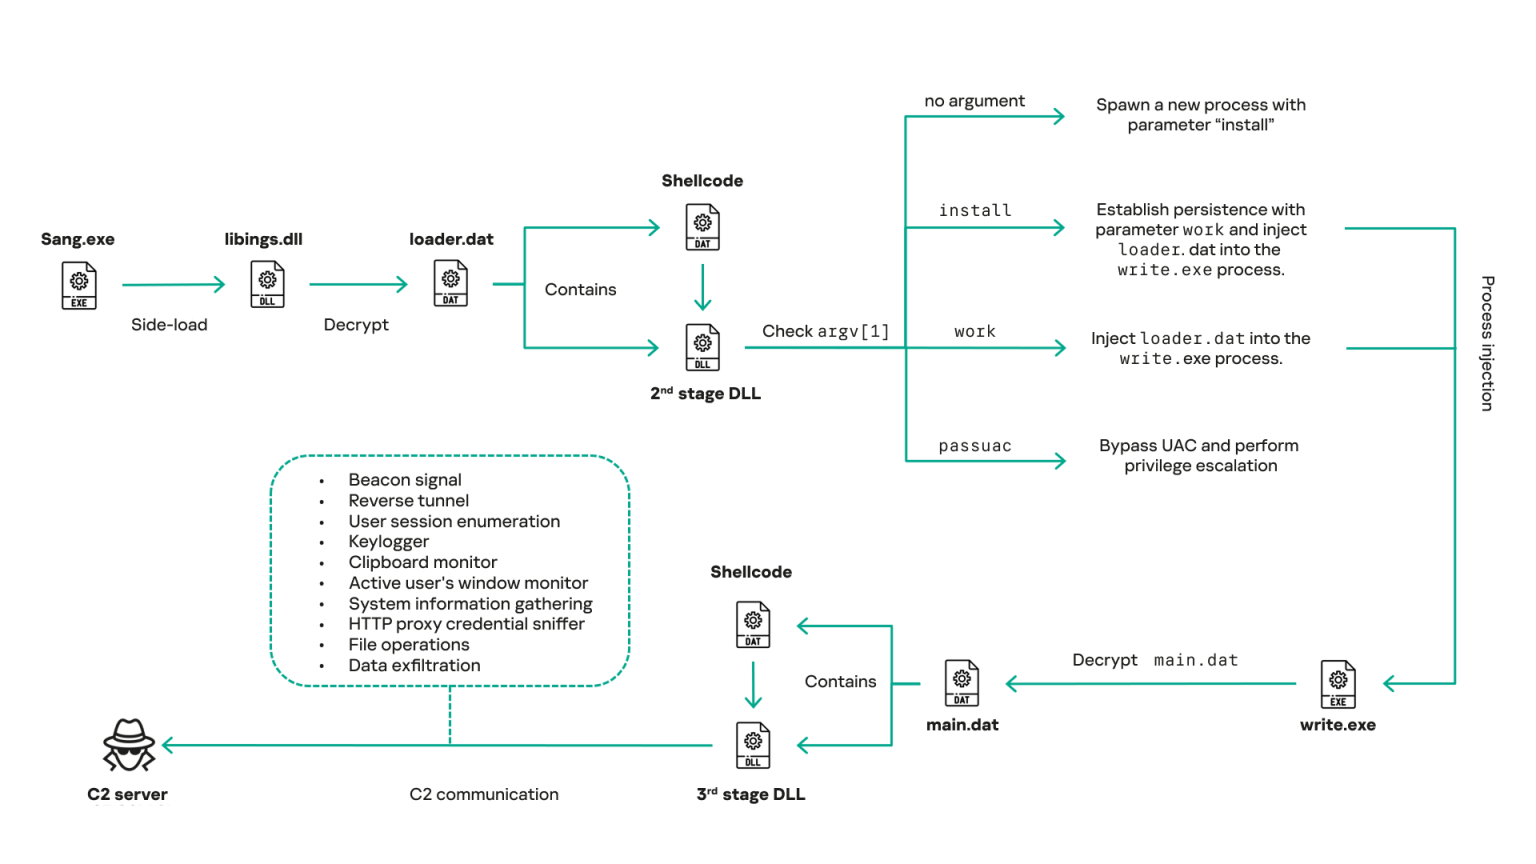
Kaspersky Labs reports that the espionage group HoneyMyte (aka Mustang Panda/Bronze President) has upgraded its toolkit in 2025, shifting from simple document theft to active, invasive surveillance of victims. The group has retooled the CoolClient backdoor, deployed browser-login stealers and keylogging/clipboard-monitoring scripts, and now exfiltrates data covertly via public file-sharing services…

Daily Recap, VMware’s critical vCenter remote code execution flaw (CVE-2024-37079) is actively exploited, with federal agencies ordered to patch within three weeks after a June 2024 DCERPC heap-overflow fix. 1Password adds auto-enabled phishing warnings to curb credential theft amid rising AI-amplified phishing risks, while Microsoft investigates Windows 11 boot failures due to UNMOUNTABLE_BOOT_VOLUME in KB5074109 affecting 25H2 and 24H2, with separate OOB fixes for Outlook PST cloud freezes, and HendryAdrian’s daily threat recap provides a weekly summary.
#VMware #CVE-2024-37079
Ransomware in 2025 has evolved from a file-encryption problem into systematized extortion that weaponizes stolen data, legal liability, and psychological pressure. Defenders must shift from backup-driven recovery to legal and communications readiness, intelligence-driven vulnerability prioritization, and targeted configuration audits to detect and mitigate data exposure. #SafePay #Cl0p

A Nebraska federal grand jury charged 31 additional defendants in an ATM jackpotting scheme that allegedly used Ploutus malware to steal millions from U.S. ATMs and was orchestrated by members of the Venezuelan gang Tren de Aragua. Authorities say suspects tampered with ATM hardware to install malware, erased evidence to conceal attacks, laundered the proceeds, and now face a wide range of federal charges with potential sentences totaling decades. #Ploutus #TrenDeAragua
A critical vulnerability in the vm2 Node.js sandbox (CVE-2026-22709) lets attackers escape the sandbox and execute arbitrary code on the host by bypassing Promise callback sanitization. Users should upgrade to the patched vm2 releases immediately to mitigate this trivial-to-exploit flaw. #vm2 #CVE-2026-22709
Nike is investigating a reported “potential cyber security incident” after the World Leaks gang published 1.4 TB of allegedly stolen Nike data on its dark web leak site. The leak listing was later removed, suggesting possible negotiation or payment, while researchers link World Leaks to the Hunters International group and related attacks like OVERSTEP installations on SonicWall SMA 100 devices. #WorldLeaks #Nike
Multiple state-sponsored and financially motivated actors are actively exploiting the high‑severity CVE-2025-8088 WinRAR path‑traversal vulnerability to gain initial access and deliver varied malicious payloads. The flaw leverages Alternate Data Streams to hide and extract LNK/HTA/BAT/CMD/script files (often into Startup folders) for persistence, with exploitation observed since July 18, 2025, including zero‑day use by RomCom. #CVE-2025-8088 #RomCom

LayerX Research discovered at least 16 malicious Chrome extensions impersonating ChatGPT productivity tools that are designed to steal account credentials and session tokens. These extensions inject scripts to capture authorization details and metadata, enabling attackers to access chat histories and connected services like Slack and GitHub. #ChatGPT #ChromeWebStore…
Microsoft released out-of-band security updates to address an actively exploited Office zero-day vulnerability tracked as CVE-2026-21509 that bypasses OLE security protections and affects multiple Office versions. Exploitation requires convincing a user to open a malicious Office file, and mitigations include a service-side fix for Office 2021 and later plus registry-based or…
North Korea–aligned cyber spies are abusing Visual Studio Code tunnels to hide command-and-control traffic and maintain prolonged access to South Korean systems. The campaign uses spear-phishing JSE scripts disguised as Hangul documents that impersonate the Ministry of Personnel Management and coordinates via a compromised site (yespp[.]co[.]kr). #DPRK #VisualStudioCode…

Security researcher c0baltstrik3d uncovered a persistent state‑affiliated espionage campaign targeting government and financial organizations in Kazakhstan and Afghanistan, revealing a previously unreported Windows Remote Access Trojan dubbed KazakRAT that has operated since at least August 2022. KazakRAT is a simple DLL-based implant delivered via malicious MSI files and decoy documents, using…
Koi disclosed six “PackageGate” vulnerabilities in NPM, PNPM, VLT, and Bun that can bypass supply-chain protections and enable remote code execution via malicious dependencies. PNPM, VLT, and Bun have issued fixes while NPM/GitHub considers some behavior intentional, even as Koi warns threat actors are discussing PoC abuse of malicious .npmrc files….
Many major organizations appear to have been targeted in an Okta SSO vishing campaign tied to ShinyHunters that involved fake domains and leaked data listings. Security firms warn attackers used real-time client-side phishing kits to intercept credentials and bypass MFA, urging adoption of phishing-resistant methods like FIDO2 and tighter app and…