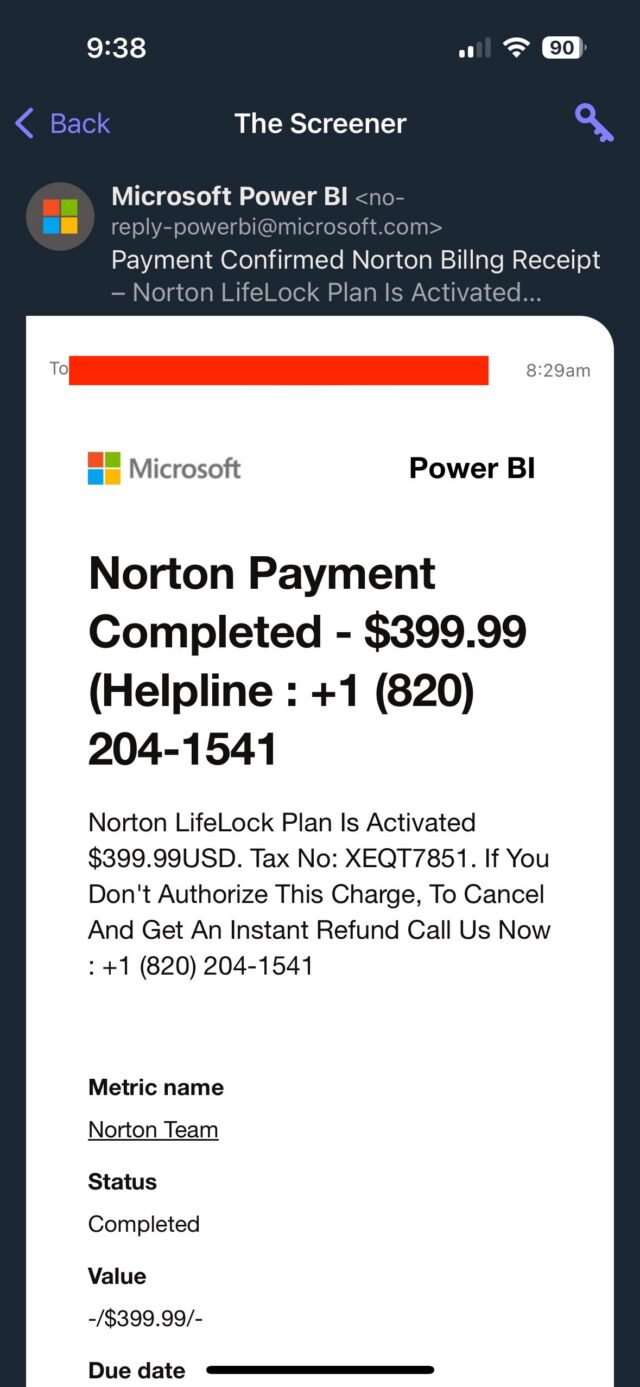
Scammers are abusing a legitimate Microsoft Power BI address ([email protected]) to send subscription-style scam emails that falsely claim a $399 charge and urge recipients to call a phone number. Multiple victims and researcher Proofpoint report the messages bury a subscription notice and instruct callers to install remote-access software, risking device takeover….
Category: Cyber Security News

Google’s Threat Intelligence Group warns that a path-traversal flaw in WinRAR (CVE-2025-8088) disclosed and patched six months ago is still being actively exploited by a diverse set of attackers. Nation-state actors linked to Russia and China and financially motivated cybercriminals have been deploying silent, no-interaction payloads into critical locations like the…
The US Department of Justice charged 31 additional individuals in an international ATM jackpotting operation, bringing the total targeted to 87. Authorities say mostly Venezuelan nationals, including members of the Tren de Aragua syndicate, used Ploutus malware and physical tampering to force ATMs to dispense cash and then erase forensic traces….
WhatsApp announced Strict Account Settings, a lockdown-style feature rolling out in the coming weeks to protect at-risk users like journalists and public figures from sophisticated cyberattacks. The feature can block attachments and media from unknown senders, silence calls from unknown numbers, and enable additional extreme protections via Settings > Privacy >…

Threat actors are actively exploiting a critical insecure-deserialization flaw in React Server Components—tracked as CVE-2025-55182 and dubbed React2Shell—to achieve remote code execution across multiple industries. Exploitation has led to widespread deployment of miners and botnets such as XMRig, RustoBot, Kaiji, Sliver, and EtherRAT, with persistence via systemd/cron, container escape chains, DNS…
Federal prosecutors unsealed a new Nebraska indictment charging 31 more individuals in an international ATM jackpotting conspiracy tied to the Tren de Aragua gang, bringing the total accused to 87. The scheme allegedly used the Ploutus malware to force ATMs to dispense cash and funnel millions to TdA’s criminal and terrorist…
The American Hospital Association has released two guides—Strategies for Medical Surge Management During Public Emergencies and Strategies for Cyber Preparedness in Health Care—to help U.S. hospitals strengthen preparedness, support staff, and sustain care during crises. The guidance centers on the “four S’s” (staffing, supply, space, systems) and offers practical measures such…

Indian government entities were targeted in two campaigns—Gopher Strike and Sheet Attack—using previously undocumented tradecraft attributed to a Pakistan-linked group operating in parallel to APT36. The intrusions use phishing and legitimate services for C2, deploy Golang tools that establish persistence and GitHub-based command-and-control, and ultimately deliver loaders to deploy Cobalt Strike….

Meta announced Strict Account Settings on WhatsApp to protect high-risk users by locking accounts to the most restrictive options and blocking attachments and media from people not in a user’s contacts. The company is also rolling out a Rust-based “wamedia” library and additional memory-safety hardening across WhatsApp to reduce exposure to…

Fortinet has issued security updates after active exploitation of a critical FortiOS FortiCloud SSO authentication bypass (CVE-2026-24858) that also impacts FortiManager and FortiAnalyzer. The company disabled and re-enabled FortiCloud SSO to block malicious accounts and now requires customers to upgrade firmware, audit configurations, and rotate credentials. #CVE-2026-24858 #FortiCloud…
A large-scale cyberattack on Delta, a Russian provider of alarm and security systems, disrupted services and left many customers unable to access alarm and vehicle functions. Delta says no signs of customer data compromise so far, but restoration is ongoing amid reports of vehicle lockouts, alarm failures, an alleged data archive…
Chinese espionage group Mustang Panda updated its CoolClient backdoor to a variant that can steal browser login data, monitor the clipboard, and deploy a previously unseen rootkit. The attacks have used legitimate Sangfor software to target government entities in Myanmar, Mongolia, Malaysia, Russia, and Pakistan while adding new plugins, infostealers for Chromium browsers, and exfiltration via hardcoded Google Drive and Pixeldrain tokens. #MustangPanda #CoolClient #Sangfor #ToneShell #PlugX #LuminousMoth
Fortinet confirmed an actively exploited critical FortiCloud single sign-on (SSO) authentication bypass tracked as CVE-2026-24858 and mitigated attacks by blocking FortiCloud SSO connections from devices running vulnerable firmware. Attackers abused FortiCloud SSO to gain administrative access to FortiOS, FortiManager, and FortiAnalyzer devices—creating rogue local admin accounts from accounts such as [email protected] and exfiltrating firewall configurations—while Fortinet disabled abusive FortiCloud accounts, globally restricted SSO, and is developing patches. #FortiCloud #FortiGate
New Chainalysis research finds Chinese-language money laundering networks processed roughly 20% of illicit cryptocurrency in 2025, averaging $44 million laundered per day (about $16.1 billion) and contributing to an estimated $82 billion laundered on-chain last year. These professionalized operations advertise on Telegram, use “guarantee” marketplaces, money mules, swapping and “Black U”…
WhatsApp is introducing “Strict Account Settings,” a lockdown-style option that blocks attachments and media from people not in a user’s contacts to protect journalists and other public-facing individuals from sophisticated spyware. The feature follows past attacks—most notably the 2019 Pegasus campaign by NSO Group that targeted about 1,400 users—and will roll…