
Dragos attributes a late-December 2025 coordinated cyber attack on multiple sites in the Polish power grid to the Russian state-sponsored crew ELECTRUM with medium confidence, calling it the first major incident targeting distributed energy resources (DERs). The attackers breached RTUs and communications at about 30 distributed generation sites, disabling some OT…
Category: Cyber Security News

Security researchers discovered a malicious VS Code extension impersonating a Moltbot AI assistant that stealthily installs a remote-access payload on hosts. The extension auto-runs on IDE launch, fetches config.json from clawdbot.getintwopc[.]site to deploy a ConnectWise ScreenConnect client that phones home to meeting.bulletmailer[.]net:8041 and includes multiple fallback delivery mechanisms. #Moltbot #ScreenConnect…

Hungarian and Romanian police arrested four young suspects linked to coordinated swatting and doxing campaigns that prompted repeated false bomb threats and emergency responses across the region. Authorities seized computers and phones during raids, charged a 17‑year‑old Romanian with terrorism‑related and false‑reporting offenses, and continue analyzing data while a separate probe…
The FTC, led by Commissioner Mark Meador, is urging age verification online to protect children and promote AI-driven behavioral checks as a privacy-conscious tool. The agency has ramped up COPPA enforcement — including a $10 million Disney settlement and a lawsuit against Sendit — while mixed court rulings, including a Supreme…
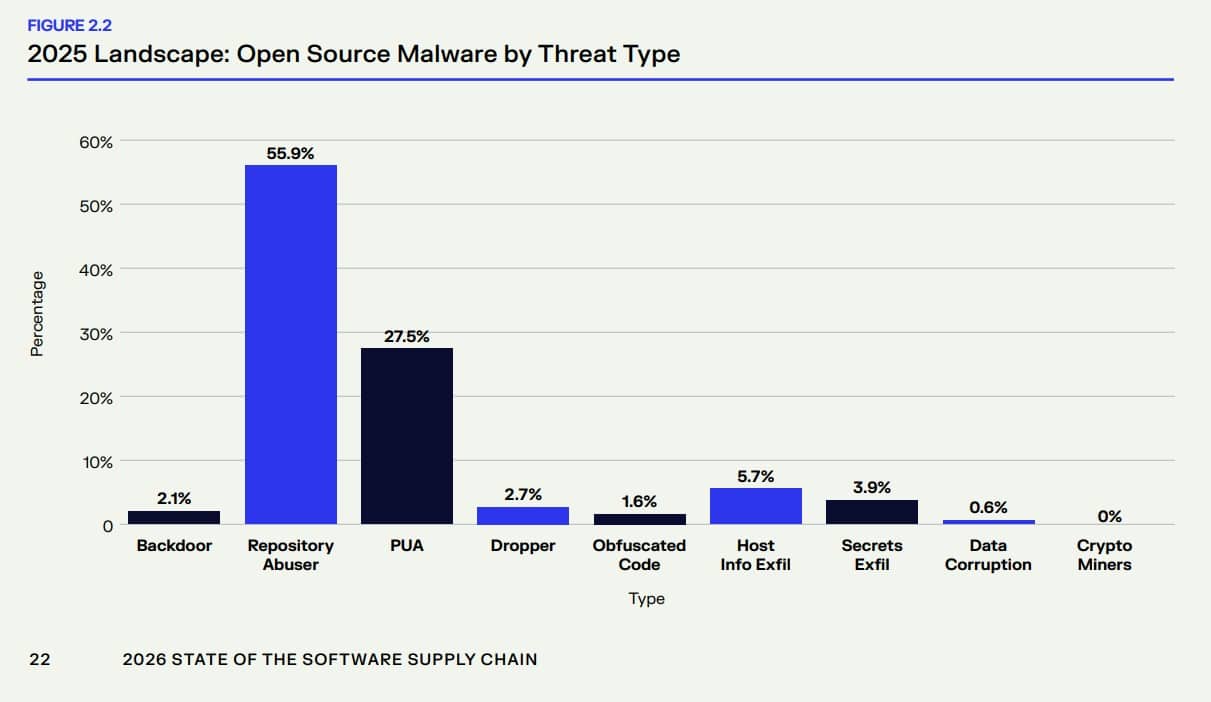
Malicious open source packages surged into industrialized, large-scale campaigns in 2025, with researchers identifying more than 454,600 new malicious packages across npm, PyPI, Maven Central, NuGet, and Hugging Face and attacks increasing in sophistication. The report spotlights npm as the primary vector—featuring self-replicating packages like Shai-Hulud, activity from threat actors such…
Meta is rolling out “Strict Account Settings” on WhatsApp to provide lockdown-style protections for journalists, public figures, and other high-risk users against sophisticated threats like spyware and zero-click exploits. The opt-in feature applies extreme controls from a user’s primary device—enabling two-step verification, blocking unknown media and calls, disabling link previews, and locking profile and presence data—as WhatsApp also migrates parts of its codebase to Rust for added resilience. #WhatsApp #NSOGroup
A Slovakian national, Alan Bill (also known as “Vend0r” or “KingdomOfficial”), admitted he helped operate Kingdom Market—a darknet marketplace that sold narcotics, cybercrime tools, fake IDs, and stolen personal information. He pleaded guilty to conspiracy to distribute controlled substances, surrendered the market domains and cryptocurrency assets, and faces sentencing on May 5 with a mandatory minimum five-year term. #KingdomMarket #AlanBill
Researchers at Pillar Security observed over 35,000 attack sessions in 40 days targeting exposed LLM endpoints in a large-scale campaign they named “Bizarre Bazaar.” The operation monetizes unauthorized access—using cryptomining, reselling API access via SilverInc/NeXeonAI, exfiltrating prompts, and attempting lateral movement through MCP servers. #BizarreBazaar #SilverInc
SolarWinds released updates for Web Help Desk to patch multiple critical authentication bypass and remote command execution flaws, including CVE-2025-40551 through CVE-2025-40554, plus a high-severity hardcoded credentials issue. Administrators are urged to upgrade to Web Help Desk 2026.1 and apply patches immediately because WHD vulnerabilities have been repeatedly exploited in attacks and flagged by CISA. #SolarWinds #WebHelpDesk
AI agents are being embedded into regulated workflows and act autonomously in ways that undermine compliance controls designed for human actors. As agents drift, hold broad permissions, and produce opaque decisions, CISOs increasingly bear responsibility for identity, access, logging, and demonstrating continuous compliance. #SOX #GDPR
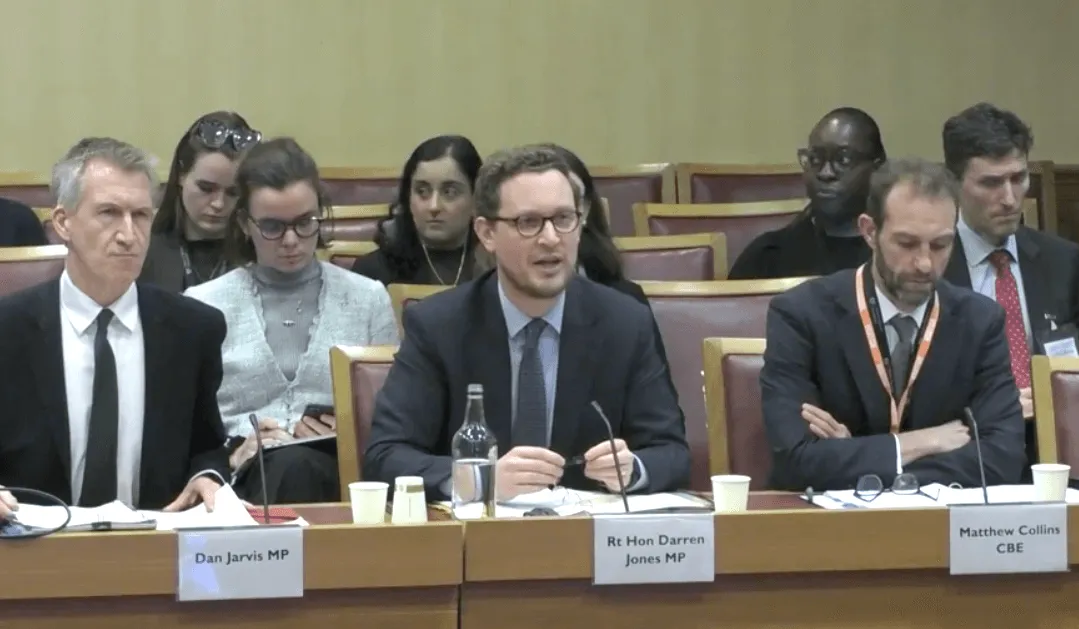
Britain risks being left exposed to cyberattacks and hybrid warfare, Lord Sedwill warned, unless it develops the ability to impose costs on hostile states rather than relying solely on resilience. Ministers defended NATO-linked spending plans and promised a refreshed National Cyber Action Plan, but MPs cautioned that vague accounting for resilience…

A coordinated cyberattack in late December targeted Poland’s distributed energy generation systems, compromising control and communications at about 30 facilities but stopping short of disrupting the national transmission backbone or causing widespread outages. Cybersecurity firm Dragos attributed the intrusion to the Russian-linked group Sandworm and reported the use of data-wiping malware…
Relying on fully autonomous AI defenses creates a risky closed loop where poor data, model drift, and lack of oversight can produce systemic failure. To stay resilient against accelerating AI-enabled threats, organizations must pair human judgment with transparent governance, auditable models, and human-in-the-loop controls. #UnitedNationsScientificAdvisoryBoard #HumanInTheLoop…
Mesh Security raised $12 million in Series A funding, bringing total investment in the company to over $16 million. The Palo Alto- and Tel Aviv-based startup operationalizes Cybersecurity Mesh Architecture by unifying fragmented security stacks into an autonomous execution layer, and will use the funds to expand agentic remediation capabilities and…
Offensive security and red teaming are shifting from periodic exercises to continuous, AI-augmented programs that combine automation, threat intelligence, and human expertise to find and fix vulnerabilities faster. This evolution includes hybrid in-house and external models, greater collaboration with blue teams, and an urgent focus on combating AI-enhanced social engineering. #Bugcrowd…