The acting director of CISA, Madhu Gottumukkala, triggered internal cybersecurity alerts after uploading “for official use only” CISA contracting documents into the public version of ChatGPT, prompting a DHS damage assessment. The temporary authorization to use ChatGPT, internal reviews involving senior DHS legal and IT officials, and potential disciplinary consequences have…
Category: Cyber Security News
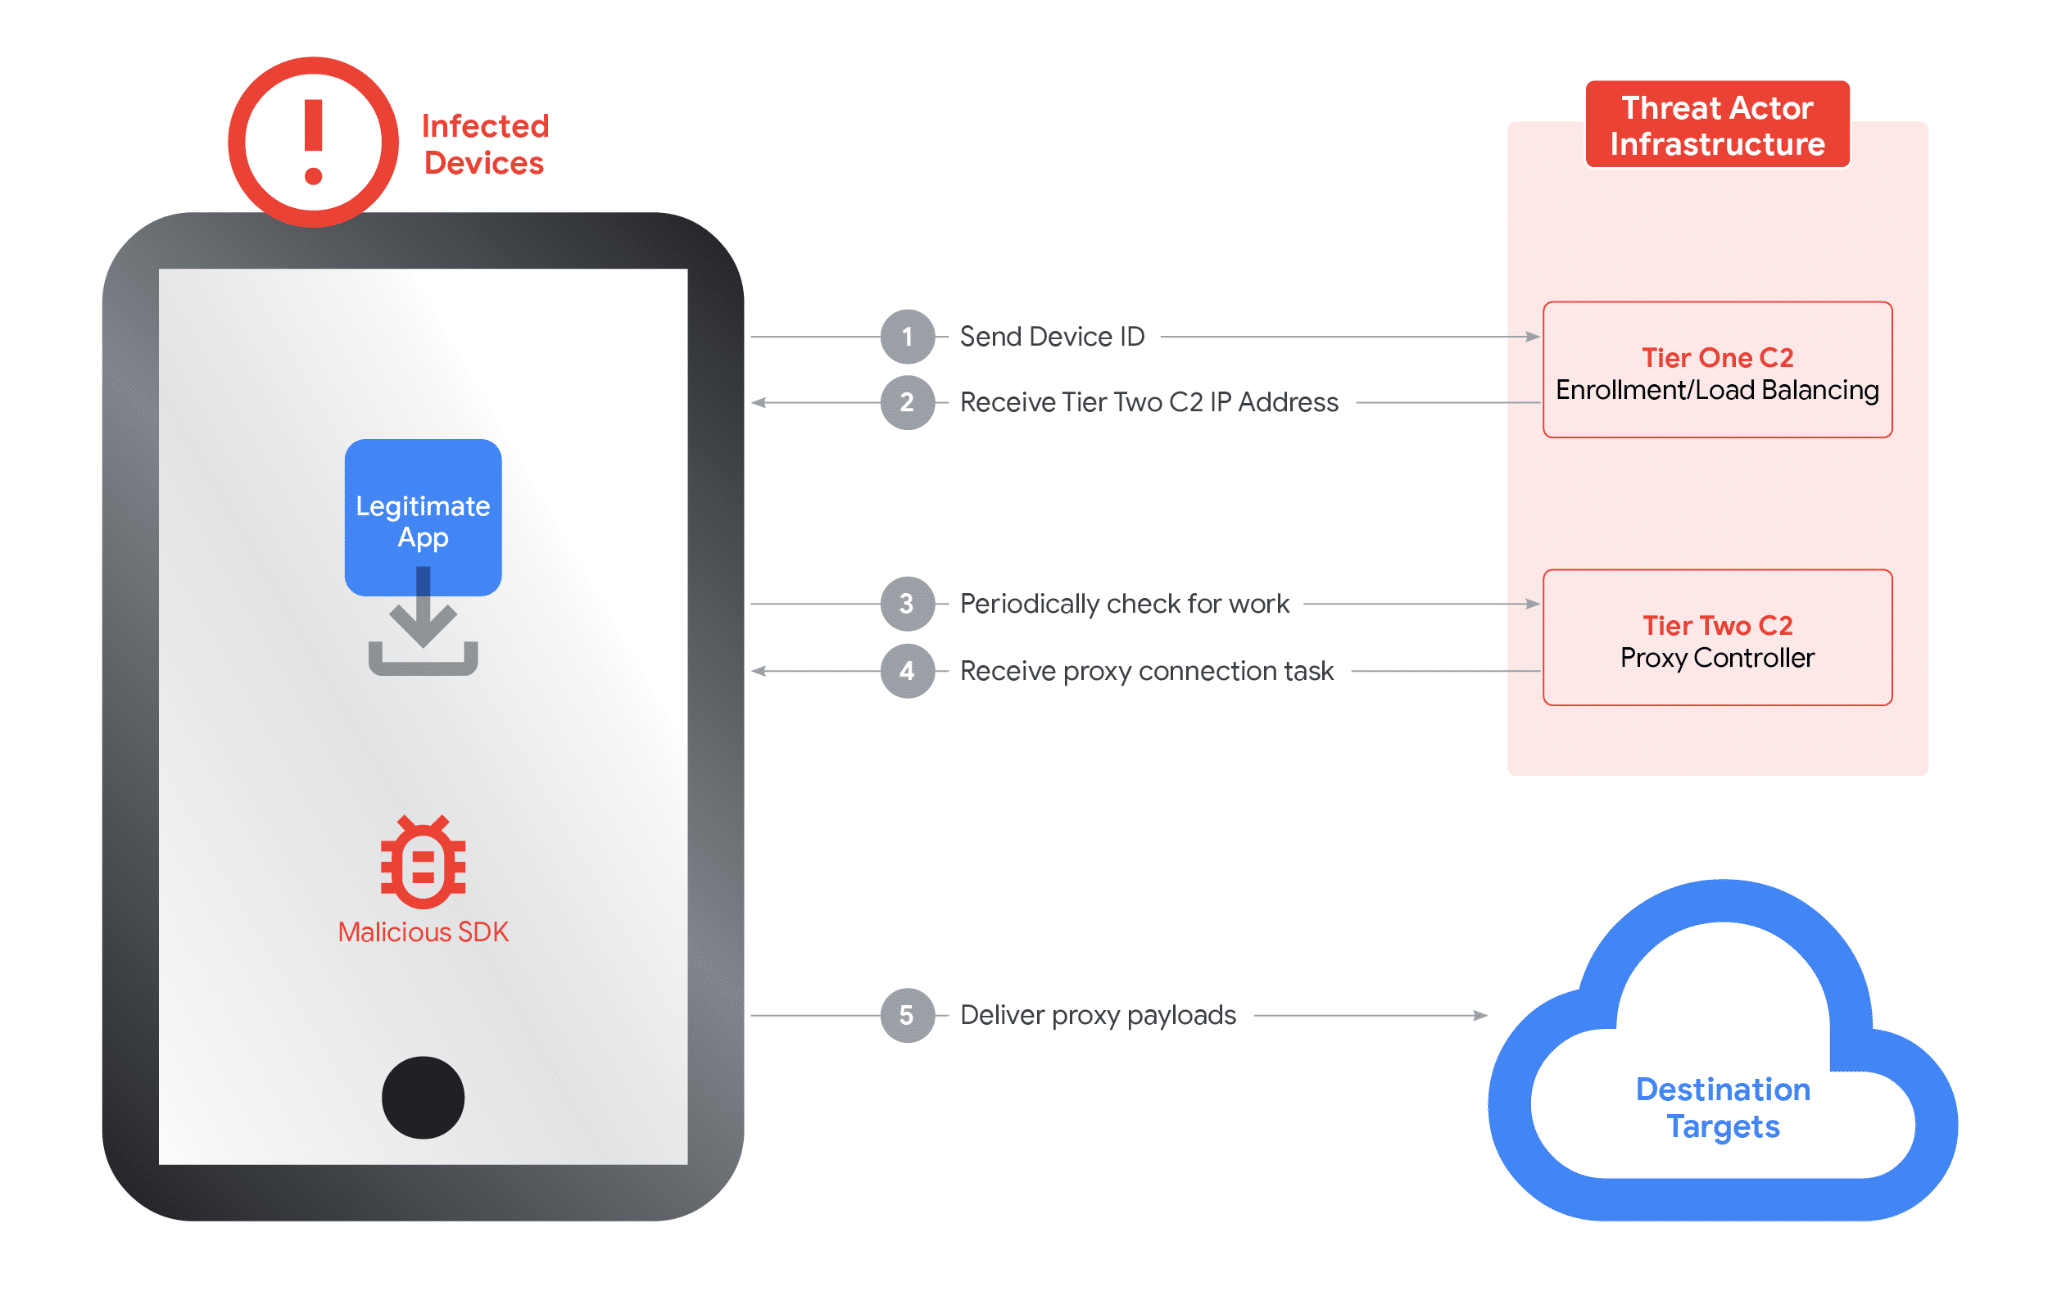
Google dismantled a global IPIDEA residential proxy network that had covertly enrolled millions of consumer devices as proxy exit nodes, seizing domains and coordinating with providers and law enforcement to disrupt the infrastructure. The network enabled large-scale espionage and cybercrime through SDKs embedded in benign apps and a two-tier command-and-control system…
A wave of cyberattacks hit Bumble, Panera Bread, Match Group, and CrunchBase, with companies reporting limited data exposure and some contractor account compromises. The hacking group ShinyHunters has claimed responsibility and reportedly used vishing and extortion techniques while law enforcement and investigators continue to examine the incidents. #ShinyHunters #Bumble…
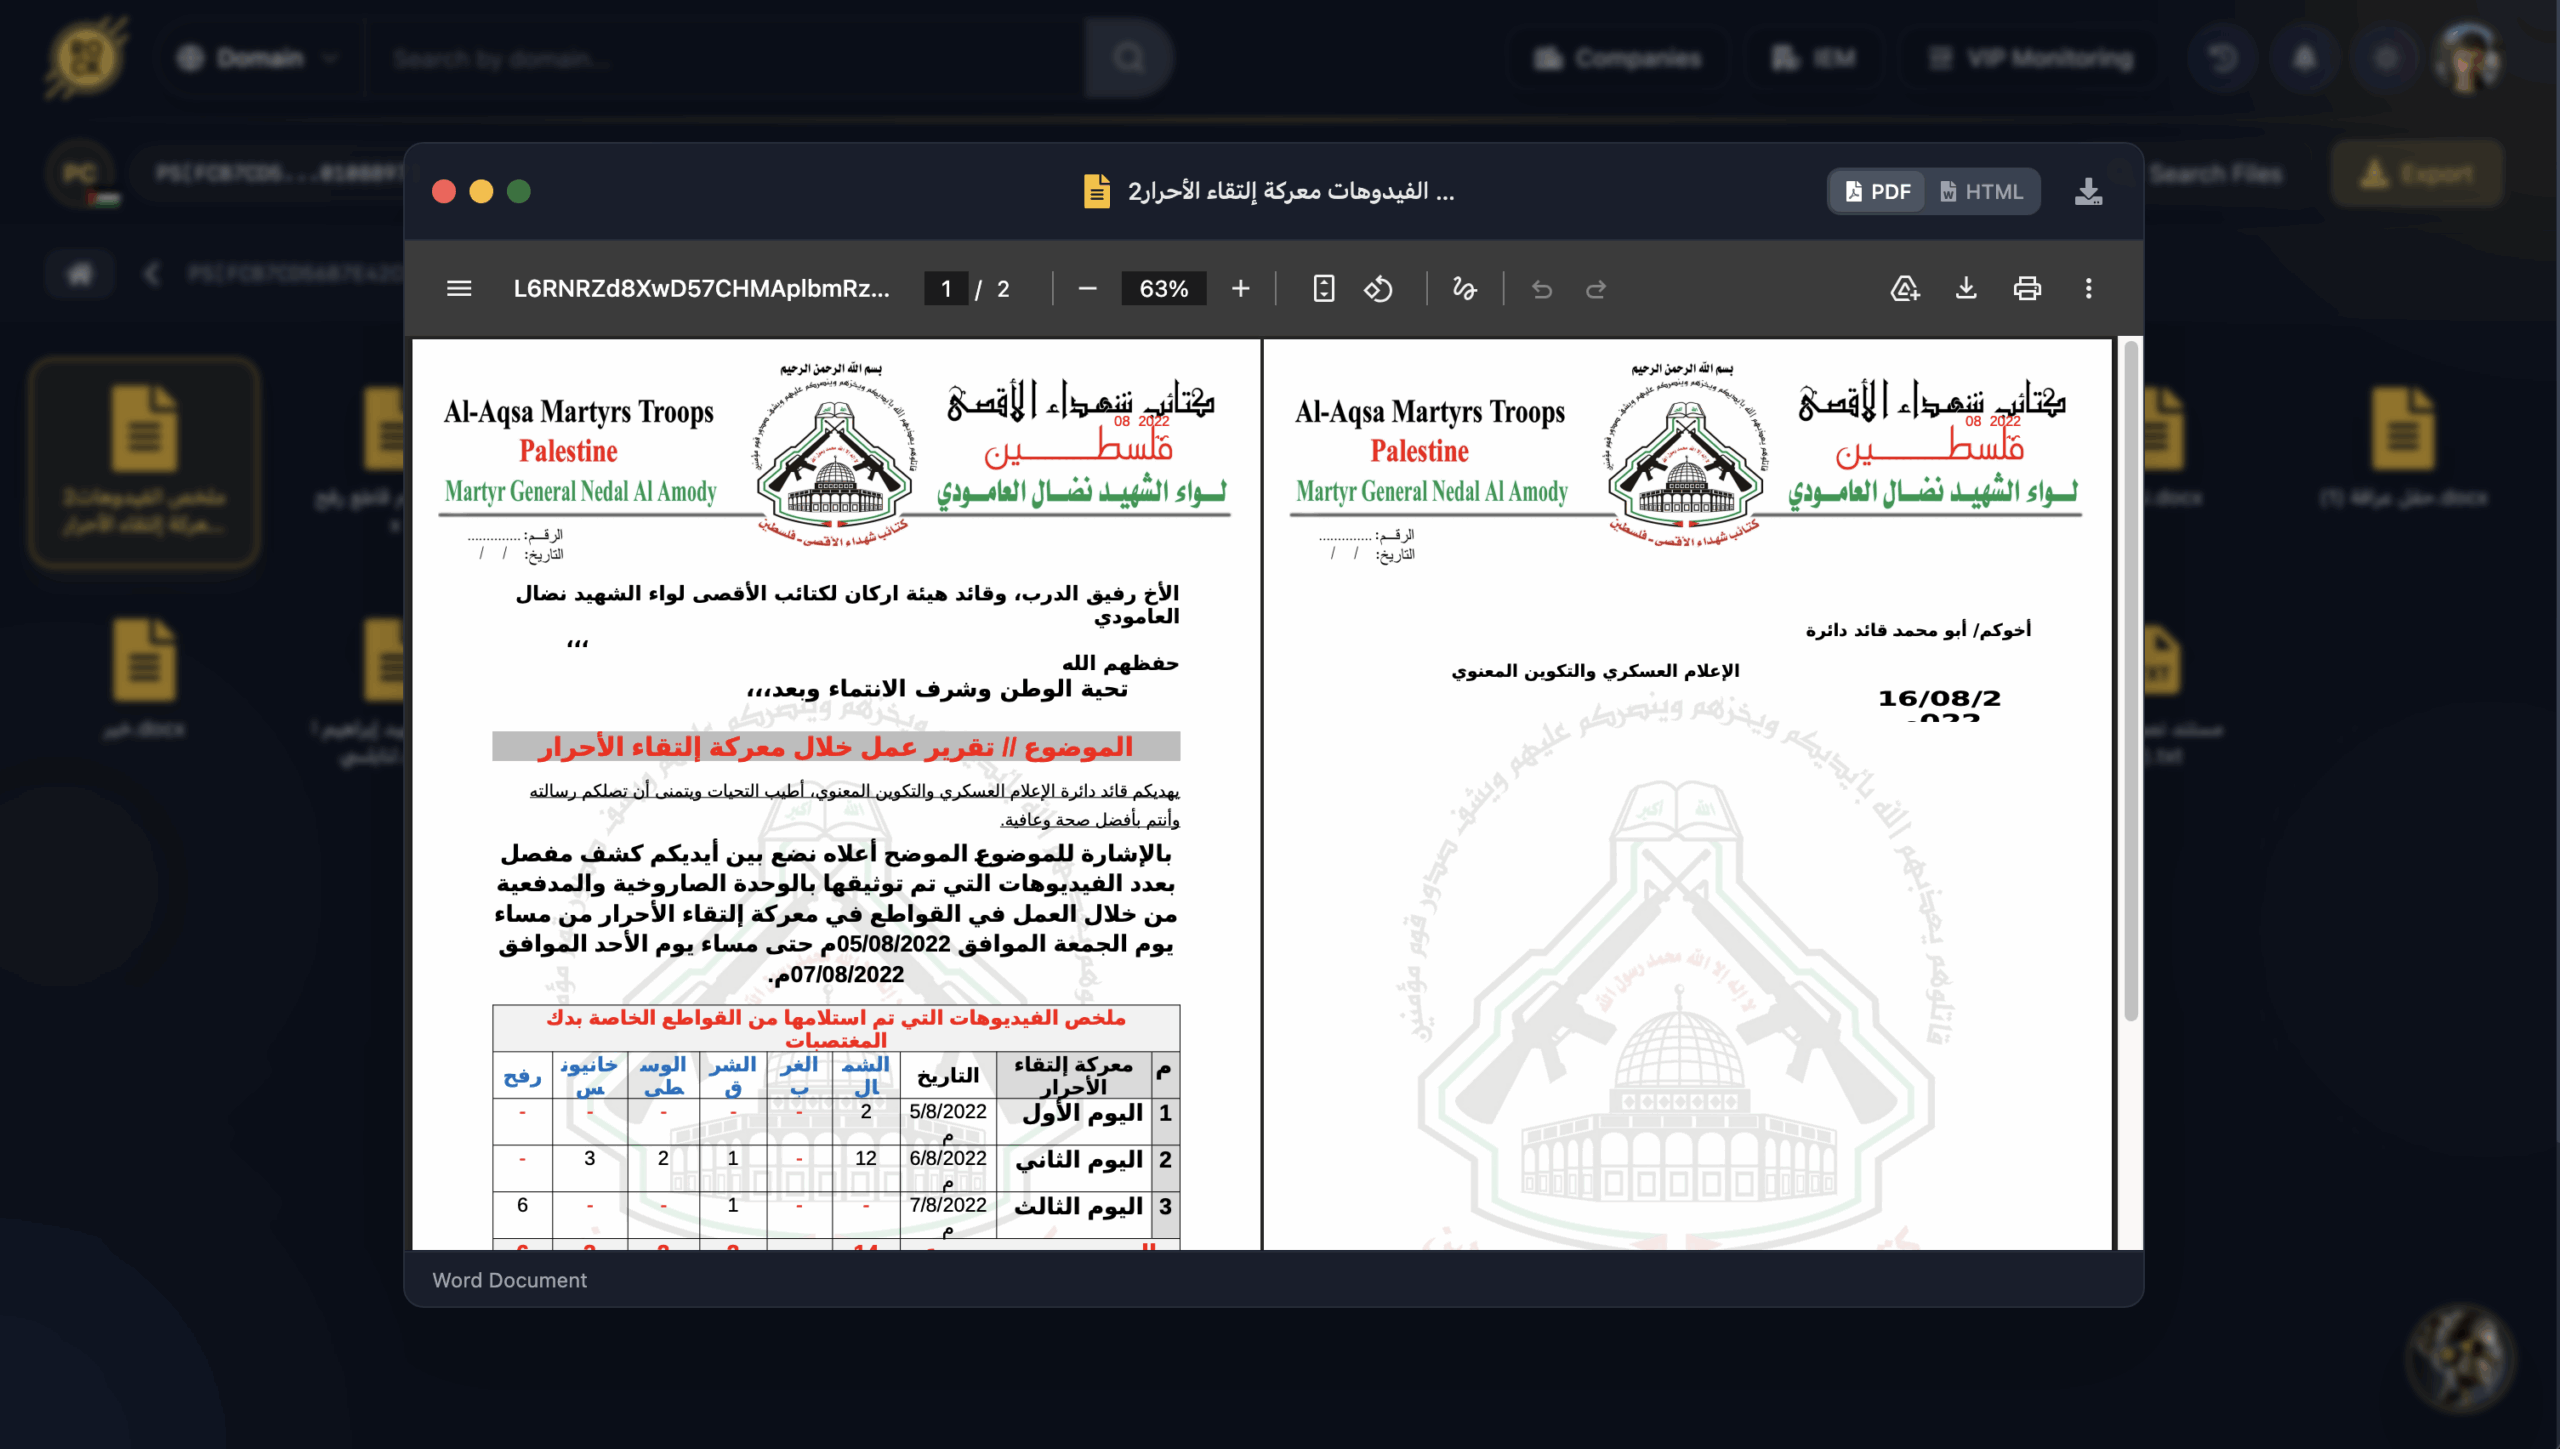
Hudson Rock recovered original internal documents from the Al-Aqsa Martyrs’ Brigades exfiltrated by an infostealer from a Gaza Strip machine, revealing pre-authorized escalation triggers and detailed operational planning from the August 2022 Breaking Dawn operation. The files expose internal disciplinary fractures documented in the Rafah Declaration, coordinated media-priority strategies with outlets like Al-Kofiya TV, and explicit OPSEC requests for VPNs, clean laptops, and burner phones signed by spokesman Abu Muhammad. #AlAqsaMartyrsBrigades #Infostealer
In late December a coordinated attack on Poland’s power grid targeted multiple distributed energy resource (DER) sites—including combined heat and power (CHP) facilities and wind and solar dispatch systems—and affected at least 12 confirmed sites, with Dragos estimating around 30. Although attackers damaged OT equipment beyond repair and wiped Windows systems, they failed to cut power (about 1.2 GW or 5% of supply); Dragos attributes the campaign with moderate confidence to the Russian-linked Electrum group, which deployed destructive wipers such as DynoWiper, Caddywiper and Industroyer2 and disrupted RTUs, edge devices, and communications—raising risks of frequency instability. #Electrum #DynoWiper
Initial access broker TA584 has escalated operations, using hundreds of compromised aged accounts sent through SendGrid and Amazon SES to deliver geofenced redirect chains that funnel victims through CAPTCHA and ClickFix pages to run PowerShell loaders that deploy Tsundere Bot or XWorm in memory. Tsundere Bot, a Node.js-based malware-as-a-service that retrieves C2 via the Ethereum blockchain, communicates over WebSockets, checks system locale to avoid CIS languages, and supports data collection, lateral movement, SOCKS proxying and a built-in bot marketplace, is assessed to likely enable ransomware follow-on activity. #TA584 #TsundereBot

Researchers disclosed two new eval-injection vulnerabilities in the n8n workflow automation platform, including a critical remote code execution flaw (CVE-2026-1470) and a Python sandbox bypass (CVE-2026-0863). JFrog warned successful exploitation can let attackers hijack entire n8n instances even in internal execution mode and urged users to apply the provided patches; the…

A critical sandbox escape in Grist-Core allows a single malicious spreadsheet formula to break out of the Pyodide WebAssembly sandbox and achieve remote code execution on the host. Cyera Research Labs disclosed the CVSS 9.1 flaw and Grist patched it in version 1.7.9 by running Pyodide under Deno with permission-based isolation,…

CISA added critical vulnerabilities in Microsoft Office, GNU InetUtils, SmarterTools SmarterMail, and the Linux kernel to its Known Exploited Vulnerabilities catalog, flagging multiple flaws that enable privilege escalation, remote code execution, and authentication bypass. Notable entries include the Mutagen Astronomy Linux kernel integer overflow, an actively exploited Microsoft Office security bypass…

Daily Recap, emergency fixes have been issued for Microsoft’s Office zero-day CVE-2026-21509 and a critical VMware vCenter DCERPC flaw (CVE-2024-37079) that attackers are already exploiting, with patches and mitigations urging rapid remediation. The roundup also highlights Dormakaba Exos flaws enabling remote door access, the Stanley malware-as-a-service for Chrome extensions, the Amatera infostealer via in-memory PowerShell with the ClickFix method, extortion-linked data breaches at Nike and by ShinyHunters, a Sandworm-linked DynoWiper attempt against Poland’s power grid, a Cloudflare BGP leak, and regulatory actions around Grok, AI privacy and platform governance. #OfficeZeroDay #CVE-2026-21509 #VMwareVCenter #CVE-2024-37079 #DormakabaExos #StanleyService #Amatera #DynoWiper #Sandworm #PolandPowerGrid #Nike #WorldLeaks #ShinyHunters #Cloudflare #BGPLeak #Grok #X
A Virginia man who co-created Empire Market pleaded guilty to federal drug conspiracy charges after operating a TOR-accessible AlphaBay clone that facilitated about $430 million in illicit transactions from 2018 to 2020. Authorities documented extensive drug sales, undercover purchases, seizures of drugs and roughly $75 million in cryptocurrency, and the defendants agreed to large forfeitures while facing lengthy federal prison terms. #EmpireMarket #RaheimHamilton
The FBI has seized the RAMP cybercrime forum, and its Tor and clearnet domains now display an FBI seizure notice with name servers switched to ns1.fbi.seized.gov and ns2.fbi.seized.gov. The action gives law enforcement access to user data that could identify operators and affiliates, and alleged RAMP founder Mikhail Matveev (aka Orange) has acknowledged the seizure after being previously linked to Babuk, LockBit, and Hive operations. #RAMP #Babuk
Two sandbox‑escape vulnerabilities in the n8n workflow automation platform (CVE-2026-1470 and CVE-2026-0863) can enable authenticated attackers to achieve full remote code execution, access sensitive data, and compromise the underlying host. Discovered by JFrog, the flaws — including a critical 9.9-rated JS AST escape in CVE-2026-1470 — have been patched in specific n8n releases and fixed on n8n Cloud, but many self-hosted instances remain unpatched. #n8n #CVE-2026-1470

Security researchers warn that insecure enterprise deployments of the Moltbot (formerly Clawdbot) AI assistant can leak API keys, OAuth tokens, conversation history, and credentials while allowing command execution and root access. Exposed admin interfaces, supply-chain risks via malicious Skills, and a lack of sandboxing have led to incidents like Signal account pairing and warnings about info‑stealers such as RedLine targeting local Moltbot storage. #Moltbot #RedLine
MicroWorld Technologies confirmed that a regional eScan update server configuration was breached and an unauthorized, malicious update was distributed to customers who downloaded updates during a two-hour window on January 20, 2026. Security firm Morphisec analyzed the incident (identifying a modified Reload.exe and a backdoor CONSCTLX.exe) while eScan says it isolated and rebuilt affected infrastructure, rotated credentials, provided remediation, and disputes aspects of Morphisec’s disclosure. #eScan #CONSCTLX