SolarWinds released patches for six vulnerabilities in its Web Help Desk product, including four critical flaws that could enable unauthenticated remote code execution via untrusted data deserialization and AjaxProxy bypasses. The defects, discovered by Horizon3.ai and WatchTowr, are fixed in Web Help Desk version 2026.1 and organizations are urged to update…
Category: Cyber Security News
Two critical vulnerabilities in the n8n workflow automation platform—CVE-2026-1470 and CVE-2026-0863—can be abused to bypass AST-based sandboxes and achieve remote arbitrary code execution in JavaScript and Python evaluation flows. JFrog reports these flaws allow full n8n instance takeover and were fixed in n8n releases 1.123.17/1.123.14, 2.4.5/2.3.5, and 2.5.1/2.4.2. #n8n #JFrog…
Pillar Security reports Operation Bizarre Bazaar, a large-scale LLMjacking campaign that scans for and hijacks exposed LLM and MCP endpoints to monetize resources, resell API access, exfiltrate data, and move laterally. The operation uses a scanner, a validator tied to silver.inc, and a marketplace called The Unified LLM API Gateway, with…
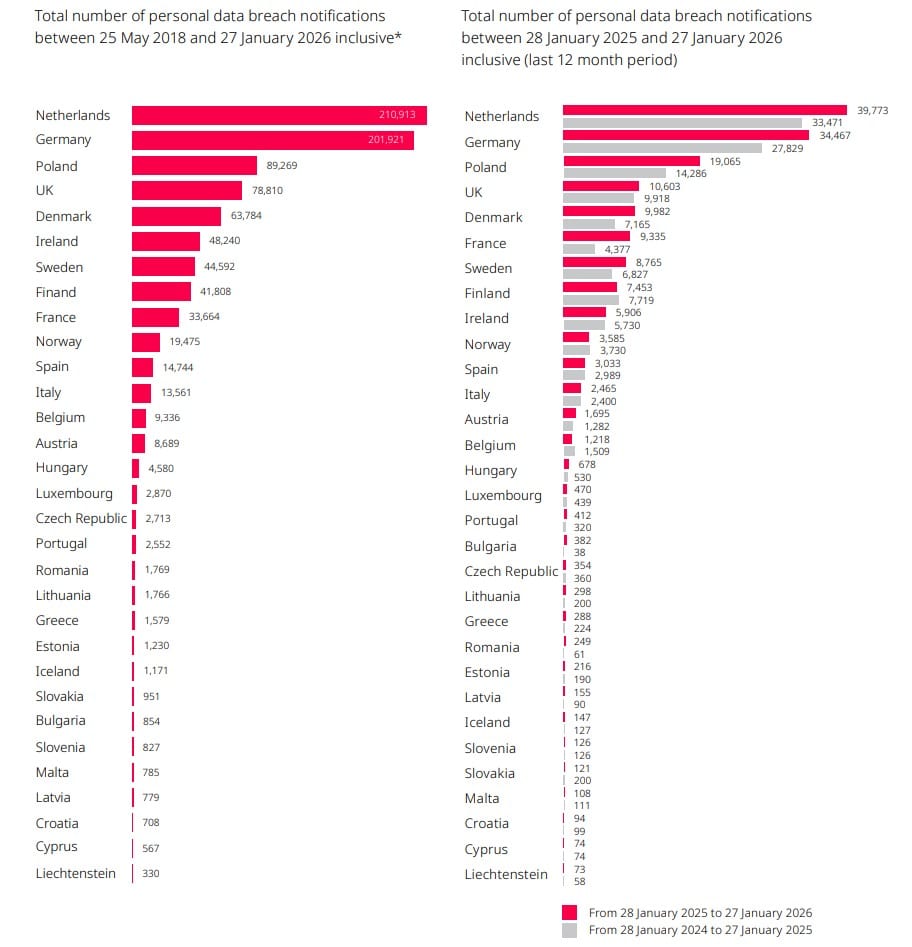
A DLA Piper report finds EU data breach notifications rose 22% year‑on‑year, averaging 443 notifications per day, while GDPR fines remained high at about €1.2 billion in 2025. The report warns that the EU Digital Omnibus proposals to raise the incident‑notification threshold, alongside laws like NIS2 and DORA, could reshape enforcement…
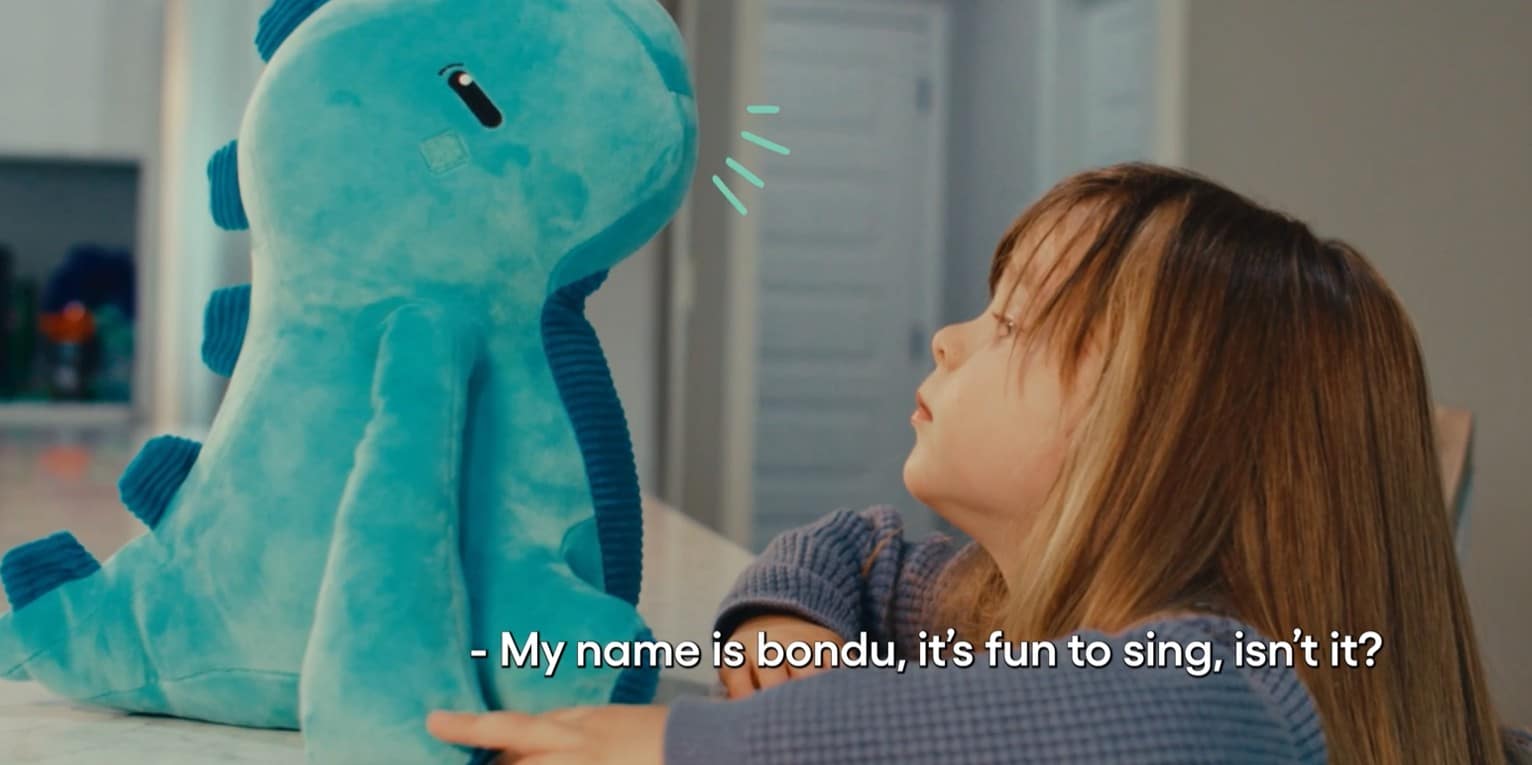
A security researcher discovered an exposed Bondu AI toy admin panel that allowed anyone with a Google account to access tens of thousands of children’s conversation transcripts and detailed personal data. The team also found an IDOR vulnerability and authentication bypass; Bondu promptly took down the console and launched an investigation…
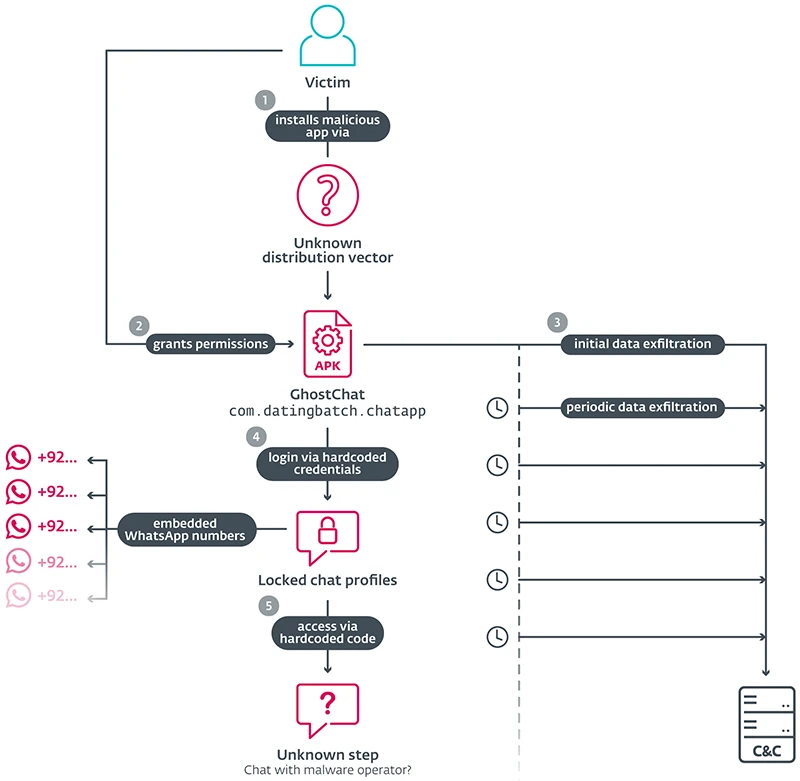
ESET researchers uncovered an Android spyware campaign called GhostChat that uses fake dating/chat profiles and romance-scam tactics to trick users in Pakistan into installing a malicious app disguised as a chat service. The app runs silent surveillance—exfiltrating images and documents—while the wider infrastructure uses ClickFix social engineering and WhatsApp QR device-linking…

Researchers found 16 malicious browser extensions for Google Chrome and Microsoft Edge that steal ChatGPT session tokens and send them to attacker-controlled servers. Distributed under the publisher name ChatGPT Mods and in some cases marked as featured, these extensions grant attackers full access to users’ ChatGPT accounts, conversation history, and metadata,…

HEURRemoteAdmin.GoToResolve.gen has been identified as a Potentially Unwanted Application that can install silently and maintain a persistent presence on Windows systems. Researchers at Point Wild’s Lat61 team warn it can load the Windows Restart Manager (RstrtMgr.dll)—a component previously abused by Conti, Cactus ransomware and the BiBi wiper—to terminate security processes, meaning…

Enterprises must prioritize actionable, business-specific threat intelligence to reduce dwell time and prevent costly operational downtime. ANY.RUN’s STIX/TAXII-compatible TI Feeds deliver fresh, validated indicators and behavioral context that boost early detection, cut false positives, and shorten MTTD/MTTR for faster incident response. #ANYRUN #TIFeeds…

OMICRON’s multi-year IDS deployments across more than 100 substations, power plants, and control centers revealed widespread technical, organizational, and operational security gaps in OT networks that expand the attack surface of energy infrastructure. StationGuard’s passive and active monitoring exposed unpatched PAC devices (including CVE-2015-5374), risky external connections, weak segmentation, and incomplete…
Google announced it disrupted IPIDEA, a large residential proxy network that covertly enrolled users’ devices via embedded SDKs and proxy software. Legal action and collaborative technical measures removed control domains, reduced the device pool by millions, and degraded IPIDEA’s proxy operations. #IPIDEA #CastarSDK…
SecurityWeek’s Cyber Insights 2026 aggregates dozens of expert perspectives that frame zero trust as an ongoing, identity-first journey complicated by AI, non-human identities, OT/IT convergence, and legacy perimeters. Experts emphasize continuous verification, microsegmentation, and measured incremental progress—while warning that AI, regulation, and insurance will both accelerate adoption and introduce new risks….
Russian and Chinese state-backed groups and financially motivated actors have been exploiting CVE-2025-8088 in WinRAR to drop malware into Windows Startup folders using a path traversal vulnerability combined with Alternate Data Streams. The flaw remained widely abused months after RARLAB released WinRAR 7.13, with actors like UNC4895 (RomCom), APT44 (FROZENBARENTS), Turla,…

A sophisticated Pakistan-linked campaign dubbed “Sheet Attack” is targeting Indian government entities by abusing Google Sheets as a command-and-control (C2) channel to blend malicious traffic into trusted cloud services. Researchers at Zscaler ThreatLabz report the operation uses tools such as SHEETCREEP, FIREPOWER, and MAILCREEP and shows signs of generative AI-assisted malware…
PwC and Google Cloud are expanding their strategic alliance with a $400 million, three-year commitment to build AI-powered security operations. The partnership will integrate Google’s threat intelligence and security technologies with PwC’s transformation and managed services to create a proactive, AI-driven security platform for hybrid and multi-cloud environments. #PwC #GoogleCloud…