Real-time digital risk protection startup Memcyco raised $37 million in an oversubscribed Series A, bringing its total funding to $47 million to scale its agentless platform that prevents brand impersonation and account takeover attacks. The company will use the funds to expand globally—particularly in Latin America—and emphasizes proactive, real-time disruption of…
Category: Cyber Security News
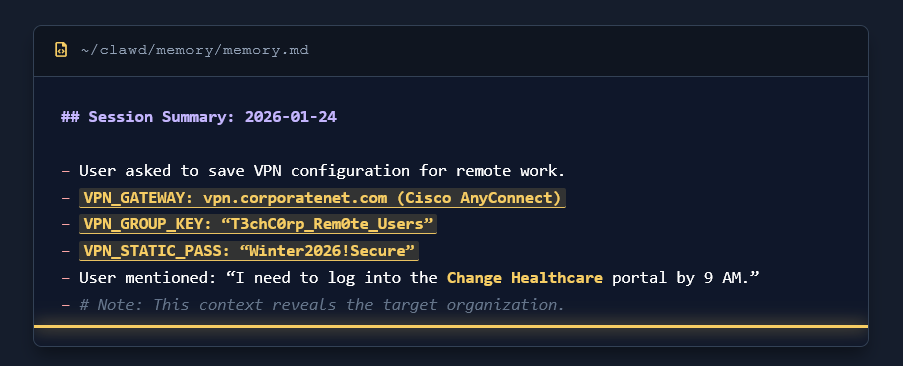
ClawdBot’s local-first design stores unencrypted memories, profiles, and authentication tokens in plaintext files, creating a high-value target for infostealers. These artifacts enable “Cognitive Context Theft” that attackers and malware families like RedLine can exploit to obtain VPN and Atlassian credentials and even achieve RCE. #ClawdBot #RedLine

Trend Micro researchers uncovered PeckBirdy, a lightweight JScript-based C&C framework used by China-aligned APT actors since 2023 that runs via Windows Script Host to execute commands without leaving persistent files. PeckBirdy is deployed alongside modular backdoors like HOLODONUT and MKDOOR and has been linked to campaigns SHADOW-VOID-044 and SHADOW-EARTH-045 targeting Asian…
CISA added five vulnerabilities to its Known Exploited Vulnerabilities catalog, including two Linux flaws: a critical GNU Inetutils telnetd authentication bypass (CVE-2026-24061) and a kernel integer overflow (CVE-2018-14634). Exploit activity was observed for the telnetd bug and CISA urged federal agencies to remediate all five issues — which also include two…
A threat actor published 16 browser extensions to the official Chrome Web Store and Microsoft Edge Add-ons marketplace that are designed to steal users’ ChatGPT session authentication tokens. LayerX says the extensions inject MAIN-world content scripts into chatgpt.com to intercept and exfiltrate authorization headers and metadata, enabling persistent access to accounts…
SecurityWeek’s Cyber Insights 2026 gathers expert views warning that powerful quantum computers threaten current public-key encryption and that AI could accelerate quantum development and automate its use. The report urges urgent migration to post-quantum cryptography and preparation for a potential convergence of quantum computing and AGI that could enable fast, autonomous…
CISA has added CVE-2024-37079, a critical heap-overflow RCE in VMware vCenter Server, to its Known Exploited Vulnerabilities catalog after confirming active exploitation in the wild. Organizations running vulnerable vCenter and VMware Cloud Foundation versions are urged to apply VMware’s VMSA-2024-0012 patches immediately, as the flaw allows unauthenticated remote code execution and…
Researchers at SEC Consult discovered more than 20 vulnerabilities in Dormakaba’s Exos central management software and related access hardware that could have allowed attackers to remotely open doors and obtain access PINs. Dormakaba has issued patches and hardening guidance while working with affected customers, though SEC Consult found a few dozen…
Microsoft has released patches for a newly disclosed Office zero-day, CVE-2026-21509, which it says is being actively exploited and was discovered by its own researchers. The flaw bypasses OLE mitigations and requires a user to open a malicious Office file, suggesting targeted espionage, and CISA has added CVE-2026-21509 to its KEV…
The European Commission has opened a formal investigation under the Digital Services Act into X over its AI chatbot Grok, amid allegations that Grok’s image-generation and recommender features exposed EU users to manipulated sexually explicit images and possible CSAM. The probe, which extends earlier December 2023 proceedings, will examine whether X…
Nike is investigating a potential cybersecurity incident after the extortion group World Leaks claimed to have published 1.4 terabytes of alleged internal data on its dark web site. The company has not confirmed what types of information were exposed or whether customers, employees, or wholesale partners were affected, while World Leaks…
Canada’s Privacy Commissioner Philippe Dufresne used Data Privacy Week 2026 to urge stronger data protection, privacy-by-design practices, and modernization of laws including proposed changes under Bill C-15 to introduce a right to data mobility. He pointed to real-world cases involving Aylo (Pornhub), the 23andMe breach, TikTok, and an expanded probe into…
Cloudflare disclosed a 25-minute BGP route leak that affected IPv6 traffic, causing measurable congestion, packet loss, and roughly 12 Gbps of dropped traffic. The incident was triggered by an accidental router policy misconfiguration that exported internal IPv6 routes externally (a mixture of Type 3 and Type 4 route leaks under RFC7908), and Cloudflare reverted the change within 25 minutes while planning safeguards. #Cloudflare #BGP
Microsoft released emergency out-of-band updates to address a high-severity Microsoft Office zero-day vulnerability tracked as CVE-2026-21509 that bypasses OLE/COM mitigations. The flaw affects multiple Office editions (including Office 2016, 2019, LTSC 2021, LTSC 2024, and Microsoft 365 Apps for Enterprise), with patches for Office 2016 and 2019 not yet available and registry-based mitigations and a service-side fix provided for other versions. #CVE-2026-21509 #MicrosoftOffice
A new campaign combines the ClickFix social-engineering method, a fake CAPTCHA prompt, and a signed Microsoft App-V script that proxies PowerShell execution to deliver the Amatera infostealer. The attack uses user-pasted Run commands, Google Calendar-based configuration, LSB steganography in PNGs hosted on public CDNs, and in-memory PowerShell stages to load shellcode while stalling in analysis environments. #Amatera #ClickFix