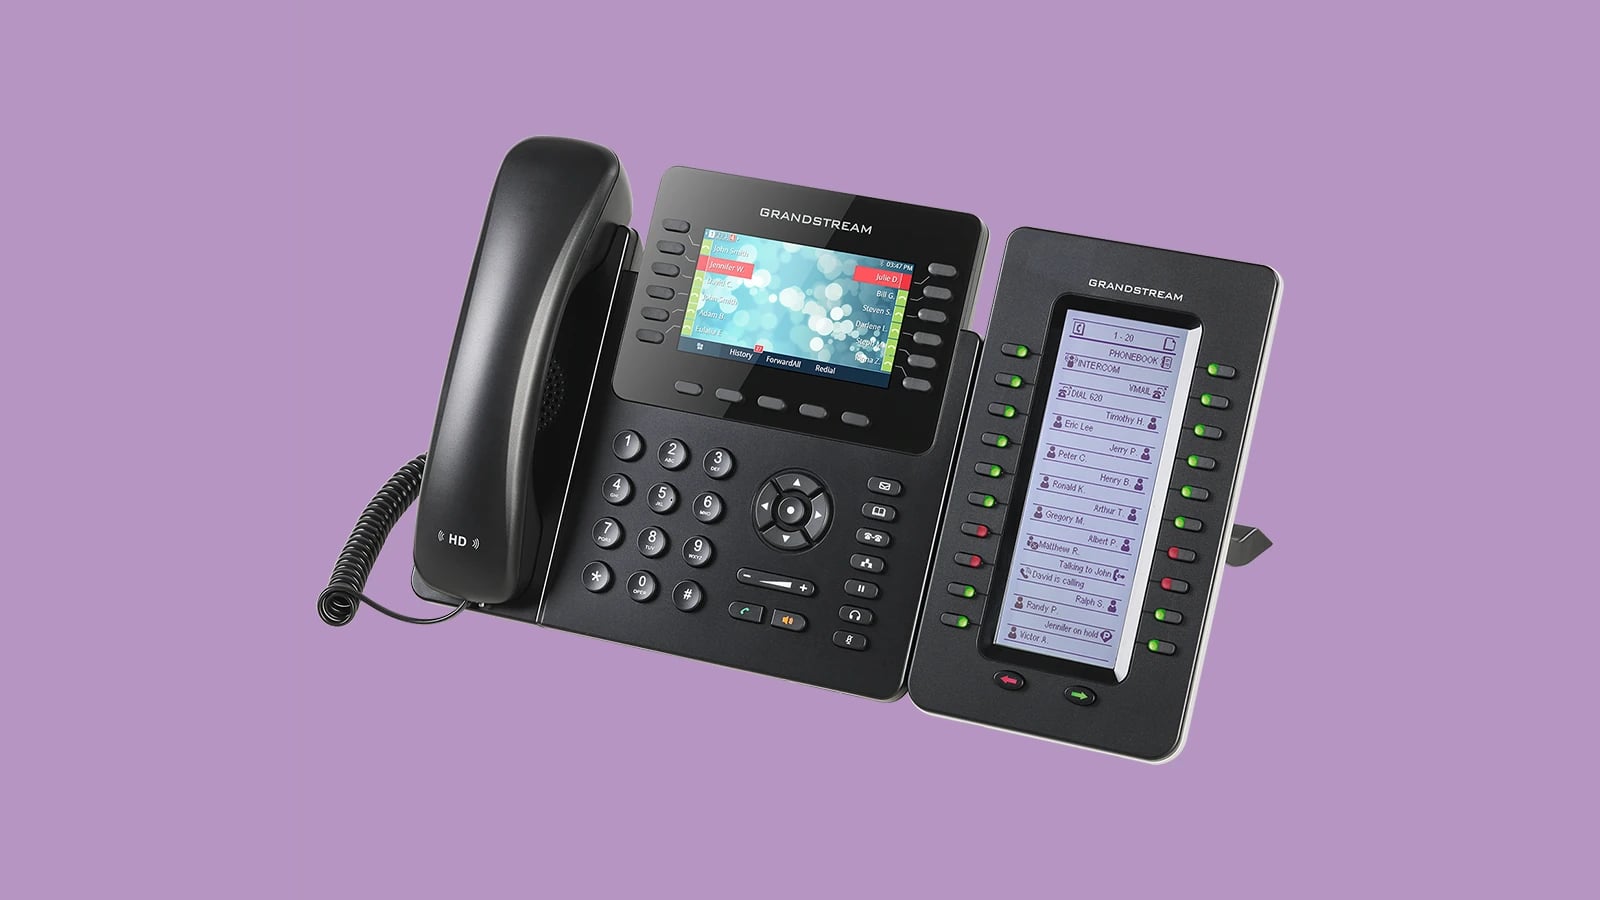
A critical stack-buffer overflow in Grandstream GXP1600 series VoIP phones allows a remote unauthenticated attacker to gain root privileges and silently eavesdrop on calls. Rapid7 published technical details and a Metasploit module demonstrating exploitation of CVE-2026-2329, and Grandstream released firmware 1.0.7.81 to fix the issue; administrators should update immediately. #CVE-2026-2329 #Grandstream
Category: Cyber Security News

The government of the Cheyenne and Arapaho Tribes was extorted after a ransomware attack in January that shut down schools, the tribal Department of Education systems, and other critical services. The Rhysida gang claimed responsibility and demanded 10 bitcoin (about $660,000) for stolen data, while Governor Reggie Wassana said the tribe…

The U.K. government will require tech companies to remove intimate images shared without consent within two days, enforce single-report takedowns across platforms, and use digital markings or hash matching to block reuploads. The announcement follows xAI’s Grok posting millions of nudified images and hands Ofcom and DSIT powers to fine or…
Venice Security emerged from stealth with $33 million in funding to launch an adaptive privileged access management platform that eliminates standing privilege by default. The Tel Aviv- and New York-based company — formerly Valkyrie — offers agentless, real-time access control across cloud, on-premises, and SaaS environments, backed by a $25M Series…
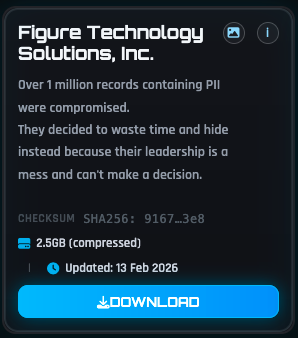
Nearly 1 million user records were exposed in a breach at blockchain-powered lender Figure Technology Solutions after an employee fell victim to a social engineering attack. The ShinyHunters group claimed responsibility and published more than 2.4GB of stolen files, with Have I Been Pwned identifying roughly 967,000 affected Figure records, including…
France’s Ministry of Economy disclosed a breach of the national bank account registry FICOBA that exposed information on 1.2 million accounts after an official’s credentials were stolen. The intrusion occurred in late January, the attacker’s access has been terminated, and affected individuals are being notified but warned about potential scams and…
PromptSpy is the first known Android malware to embed generative AI (Google Gemini) into its execution flow to perform context-aware UI automation and persist in the recent apps list. ESET found the campaign targeting Argentina via phishing sites and a Chase-themed app called MorganArg, and Play Protect blocks known variants though…
Researchers discovered a new Android banking malware named Massiv that disguises itself as an IPTV app to steal digital identities and access online banking accounts. In a campaign observed by ThreatFabric, Massiv targeted a Portuguese government app integrated with Chave Móvel Digital and uses screen overlays, keylogging, MediaProjection and Accessibility-based UI-tree control to bypass protections, open fraudulent accounts, and enable money laundering and account takeovers. #Massiv #ChaveMovelDigital
INTERPOL-coordinated Operation Red Card 2.0 led to 651 arrests and the recovery of more than $4.3 million in a multinational crackdown on investment fraud, mobile money scams and predatory loan apps. Across 16 countries the action identified 1,247 victims, seized 2,341 devices and took down 1,442 malicious websites, domains and servers linked to over $45 million in losses. #INTERPOL #OperationRedCard2_0
Dragos’ 2025 report warns that three new OT-focused threat groups emerged while a Beijing-linked crew continued compromising cellular gateways, routers, and US electric, oil, and gas networks. The report details Voltzite’s long-term embedding in utility control systems, use of Sierra Wireless AirLink devices and the JDY botnet, and the roles of…
At the India AI Impact Summit 2026, global leaders highlighted the need to move AI in education from pilots to large-scale, responsible, and equitable classroom adoption centered on teachers and pedagogy. They called for 2026 to be a year of action emphasizing teacher training, transparent AI literacy policies, interoperable infrastructure, and…
Researchers uncovered critical vulnerabilities in four widely used Visual Studio Code extensions — Live Server, Code Runner, Markdown Preview Enhanced, and Microsoft Live Preview — that together have been installed over 128 million times. OX Security warned these flaws could enable remote code execution, file exfiltration, and lateral movement from developer…

Daily Recap, the latest cyber threats cover exploited zero-days like Dell RecoverPoint CVE-2026-22769 used by UNC6201 to deploy GRIMBOLT/SLAYSTYLE with Ghost NICs, and a spectrum of high-impact flaws, supply-chain breaches, and targeted espionage campaigns. The recap also notes active exploitation of TeamT5 CVE-2024-7694, Ivanti EPMM backdoors bypassing patches, Keenadu firmware backdoors, CrescentHarvest espionage, and AI/Cloud risks including Copilot as C2 and Grok deepfakes, plus notable data leaks and enforcement actions. #UNC6201 #GRIMBOLT #SLAYSTYLE #DellRecoverPoint #TeamT5 #IvantiEPMM #Keenadu #CRESCENTHARVEST #Copilot #Grok #Eurail #Cellebrite #DavaIndia #Notepad++ #Chrysalis #PaloAltoNetworks #Koi #VulnCheck
Researchers at Check Point demonstrated that AI assistants with web browsing and URL-fetching capabilities, such as Grok and Microsoft Copilot, can be abused as stealthy relays for command-and-control communications. Malware can use WebView2 to interact with these AI agents, fetch attacker-controlled URLs, and parse chat outputs to receive commands or exfiltrate encrypted data, making detection and blocking more difficult. #Grok #MicrosoftCopilot
CISA warns of a critical 9.8-severity vulnerability (CVE-2026-1670) in multiple Honeywell CCTV products that allows unauthenticated attackers to change recovery emails and take over camera accounts. The flaw stems from an exposed unauthenticated API endpoint affecting several mid-level Honeywell camera models; users should minimize network exposure and contact Honeywell support for patch guidance. #Honeywell #CVE-2026-1670