
Researchers at Forcepoint X-labs found a campaign targeting organisations in the UK, US, Canada, and Northern Ireland where attackers impersonate the US Social Security Administration to trick users into running a malicious .cmd script. The script disables Windows defenses, hides payloads using Alternate Data Streams, and silently installs ConnectWise ScreenConnect as…
Category: Cyber Security News

Researchers disclosed multiple security vulnerabilities in four popular Microsoft Visual Studio Code extensions—Live Server, Code Runner, Markdown Preview Enhanced, and Microsoft Live Preview—that can allow attackers to exfiltrate local files and execute code remotely. With more than 125 million combined installs, OX Security warns that a single malicious extension or vulnerability…

Researchers disclosed a critical unauthenticated stack-based buffer overflow in Grandstream GXP1600-series VoIP phones that can enable remote code execution with root privileges. Tracked as CVE-2026-2329 with a CVSS score of 9.3, the flaw resides in the web API (/cgi-bin/api.values.get), affects multiple GXP16xx models, and was patched in firmware 1.0.7.81. #CVE-2026-2329 #GrandstreamGXP1600…

Citizen Lab found high-confidence indicators that Kenyan authorities used Cellebrite forensic extraction tools on pro-democracy activist Boniface Mwangi’s Samsung phone while it was in police custody in July 2025. Separate investigations also confirmed Intellexa’s Predator spyware infected Angolan journalist Teixeira Cândido’s iPhone in May 2024, highlighting a broader pattern of commercial…
Kaspersky researchers discovered a previously undocumented Android backdoor named Keenadu embedded in tablet firmware that can infect devices before they reach consumers and grant attackers virtually unrestricted control. The campaign, linked to advertising-fraud modules and found in devices from multiple manufacturers including Alldocube, resists standard Android removal methods and may require…
A Chinese state-backed hacking group has been exploiting a critical zero-day in Dell RecoverPoint for Virtual Machines (CVE-2026-22769) since at least mid-2024 to deploy backdoors and target organizations across North America. Dell, Google/Mandiant and U.S. agencies have issued advisories and fixes, and CISA ordered immediate federal patching while researchers report use…
Microsoft says a bug in the Microsoft 365 Copilot “work tab” chat has been summarizing confidential emails from users’ Sent Items and Drafts since late January, bypassing sensitivity labels and configured data loss prevention controls. Microsoft identified the issue as a code error, began rolling out a fix in early February, and is monitoring the deployment while contacting affected users without providing a full remediation timeline. #Microsoft365Copilot #CopilotChat
Hackers stole personal and contact information from nearly 1 million accounts after breaching Figure Technology Solutions in a social engineering attack, with Have I Been Pwned reporting data from 967,200 accounts dating to January 2026. Extortion group ShinyHunters claimed responsibility and posted roughly 2.5GB of stolen loan applicant data, and the incident is linked to broader vishing campaigns targeting SSO providers and multiple high‑profile organizations. #Figure #ShinyHunters
Microsoft confirmed that a logic error in Exchange Online’s heuristic detection for credential phishing incorrectly flagged thousands of legitimate URLs as phishing, blocking links in emails and Microsoft Teams messages between February 5 and February 12. The false positives triggered automated removals, misleading alerts, and were amplified by other security tools and a signature-system bug; Microsoft tracked the event as EX1227432 and will publish a final report within five business days. #Microsoft #ExchangeOnline
Flare researchers observed threat actors rapidly sharing proof-of-concept exploits, offensive tools, and stolen administrator credentials for SmarterMail vulnerabilities CVE-2026-24423 and CVE-2026-23760, leading to automated mass exploitation and confirmed ransomware activity. Incidents including a SmarterTools breach and ties to the Warlock cluster highlight that email servers are identity-critical and require urgent patching, segmentation, and enhanced monitoring. #SmarterMail #CVE-2026-24423
Texas Attorney General Ken Paxton sued TP-Link, alleging the company deceptively marketed secure networking devices while allowing Chinese state-sponsored actors to exploit firmware vulnerabilities. The complaint cites Check Point Research linking Camaro Dragon campaigns to TP-Link flaws and frames the case as part of a broader move to treat security claims…
Researchers at Novee discovered 16 vulnerabilities in Apryse WebViewer and Foxit PDF cloud services that could enable account takeover, data exfiltration, arbitrary code execution, and persistent compromise. Both vendors were responsibly notified and have released patches addressing issues such as XSS, SSRF, path traversal, and OS command injection. #Apryse #Foxit…

Cogent Security raised $42 million in Series A funding led by Bain Capital Ventures to develop autonomous AI agents for vulnerability remediation, bringing total funding to $53 million. Its agentic AI platform automates investigation, prioritization, and remediation by normalizing vulnerability data, incorporating business context, and integrating tailored remediation plans into existing…

Researchers at Kaspersky have analyzed Keenadu, an Android backdoor found preinstalled in device firmware or delivered via OTA updates and malicious apps, which gives operators full remote control and is primarily used for ad fraud. Kaspersky detected roughly 13,000 infections across countries including Russia, Japan, Germany, Brazil, and the Netherlands, and…
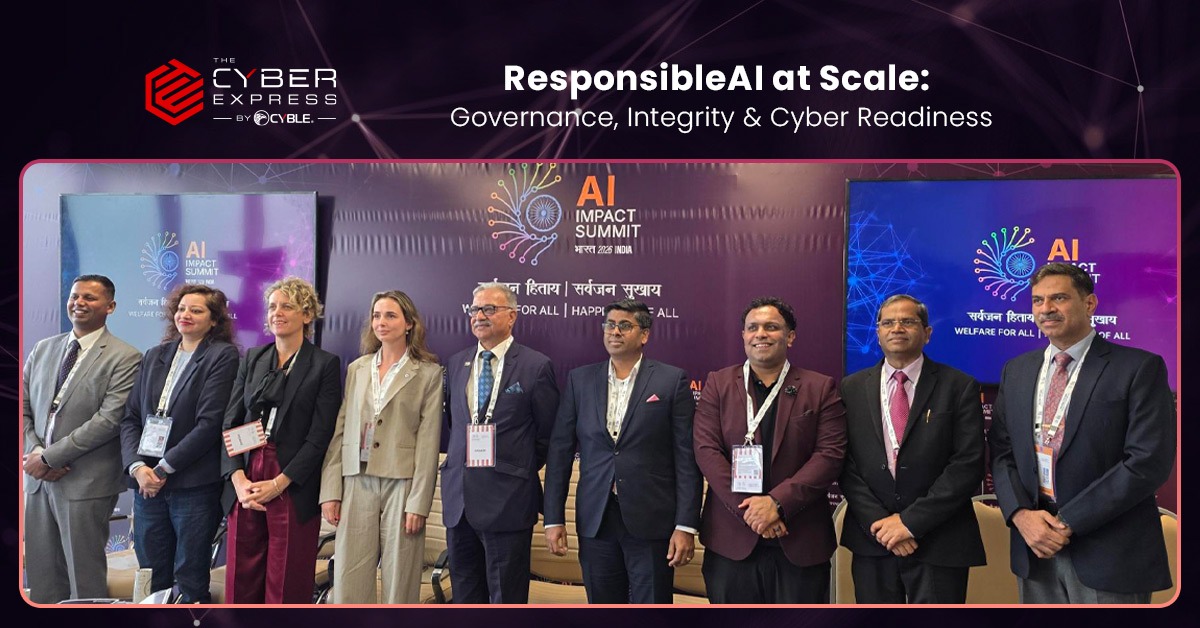
At the India AI Impact Summit 2026, leaders from government, industry, and academia argued that scaling AI must be matched by strong governance and cyber readiness. Panelists stressed proactive measures like red teaming and continuous stress-testing to counter industrialized threats such as deepfake audio and preserve public trust. #Deepfake #Cyble…