AI is actively reshaping cyber risk, driving AI-powered ad fraud, deepfake incidents, and novel malware events while regulators and enterprises race to respond in real time. This weekly roundup highlights AI-driven ghost click ad fraud, the Ireland GDPR probe into X’s Grok, and a suspected ransomware incident at Advantest, underscoring the…
Category: Cyber Security News

Two former Google engineers and one of their husbands were indicted in the U.S. for allegedly stealing trade secrets from Google and other tech firms and transferring them to unauthorized locations, including Iran. The stolen material reportedly included processor security and cryptography details tied to Google’s Tensor processor, and the defendants…

ESET researchers analyzed PromptSpy, an Android malware that uses a VNC module and Accessibility Services to capture screens, steal unlock credentials, and enable remote control of compromised devices. The malware uniquely leverages Google’s Gemini generative AI at runtime—sending UI element XML to Gemini and following its JSON instructions for taps and…

Daily Recap, today’s briefing covers a surge of mobile threats led by PromptSpy leveraging Google Gemini for Android phishing in Argentina, along with Massiv banking malware and Keenadu infections spanning Russia, Japan, Germany, Brazil and the Netherlands. The update also highlights critical CVEs in Dell RecoverPoint for VMs, several VS Code extensions, Grandstream GXP1600 and Honeywell CCTV, notable breaches like Figure and ScreenConnect hijacks, evolving surveillance tools usage, and recent enforcement actions such as Red Card 2.0, with AI governance and security funding developments shaping the broader cyber landscape. #PromptSpy #Gemini #Argentina #Massiv #ChaveMovelDigital #Keenadu #Russia #Japan #Germany #Brazil #Netherlands #BRICKSTORM #GRIMBOLT #DellRecoverPointForVMs #VSCode #Grandstream #Honeywell #SmarterMail #Figure #ScreenConnect #VoltTyphoon #Cellebrite #Predator #TPLink #EX1227432 #Copilot #Grok #RedCard2

PromptSpy is the first known Android malware to integrate generative AI into its execution flow, using Google’s Gemini model to generate device-specific instructions that help it pin and persist in Recent Apps. The spyware also includes a VNC module for full remote access, can capture PINs and screen activity, and uses invisible overlays to block uninstallation. #PromptSpy #Gemini

Operation Red Card 2.0, led by INTERPOL and 16 African countries, resulted in 651 arrests and the recovery of more than $4.3 million while targeting high-yield investment scams, mobile money fraud, and fraudulent mobile loan apps. The eight-week effort exposed scams linked to over $45 million in losses, identified 1,247 victims,…

Researchers have identified PromptSpy, the first Android malware that leverages Google’s Gemini generative AI to analyze on-screen UI and provide step-by-step instructions to automate malicious interactions. The malware uses those AI-driven instructions to pin itself in recent apps, deploy a VNC module for remote access, steal lockscreen credentials, and resist uninstallation….
Dragos reports that Chinese-linked threat actor Volt Typhoon continued compromising U.S. utilities through 2025, embedding in operational technology networks to pre-position for disruptive attacks. Researchers warn many compromises—especially in smaller water-sector utilities—may never be found, with initial access groups like SYLVANITE handing breaches to Volt Typhoon. #VoltTyphoon #SYLVANITE…
Criminals are increasingly using ATM jackpotting malware to steal cash, with the FBI reporting more than 1,900 incidents since 2020 and over 700 in 2025 that involved more than $20 million in losses. The Ploutus family of malware lets attackers bypass XFS and directly control ATMs—often after gaining physical access with…
Japanese semiconductor test-equipment supplier Advantest is responding to a ransomware attack that impacted multiple company systems after detecting unusual activity and isolating affected networks. The investigation is ongoing with cybersecurity experts as reports highlight a sharp rise in ransomware gangs targeting industrial and semiconductor firms, with past victims including Microchip Technology…
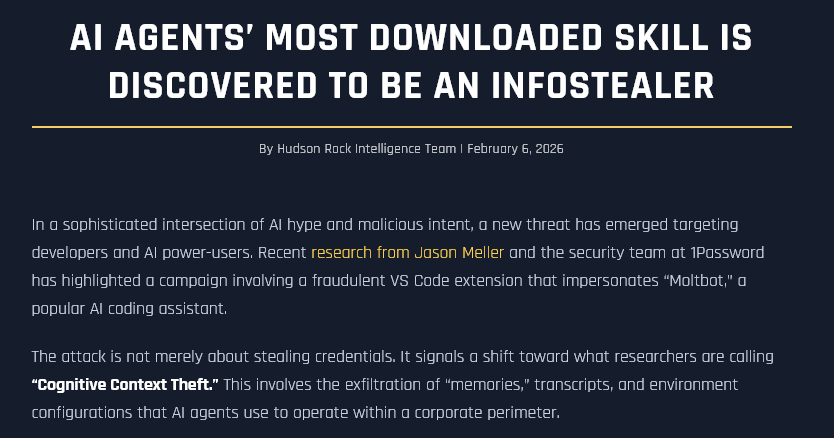
Infostealers have evolved into primary entry points for sophisticated global attacks by abusing malicious AI “skills”, harvesting OpenClaw configurations (tokens and AI memory), and converting compromised employee credentials into delivery vectors. The resulting infostealer logs feed APT operations, enable high-fidelity sextortion, and have also provided researchers with intelligence linking actors and incidents such as Bitter APT and the ByBit heist. #Infostealer #OpenClaw
A Nigerian national, Matthew Abiodun Akande, was sentenced to eight years in prison for hacking multiple Massachusetts tax preparation firms and filing over 1,000 fraudulent tax returns seeking more than $8.1 million in refunds. He used the Warzone RAT and a crypter, delivered via CEO‑impersonation phishing emails with a disguised Dropbox link, to steal clients’ Social Security numbers and prior-year tax data before funneling refunds through co-conspirators. #WarzoneRAT #MatthewAkande
Modern infostealers harvest credentials along with browser cookies, browsing history, and system files, enabling attackers to tie technical data back to real people and organizations. Specops research of 90,000+ infostealer dumps (800M+ rows) shows credential reuse and session data let attackers escalate personal compromises into enterprise breaches, and continuous Active Directory scanning with Specops Password Policy can block known-compromised credentials to reduce that risk. #SpecopsPasswordPolicy #LinkedIn
CISA ordered federal agencies to patch a maximum-severity hardcoded-credential vulnerability in Dell RecoverPoint (CVE-2026-22769) within three days after researchers found it has been actively exploited since mid-2024. Security firms attribute the exploitation to suspected Chinese threat cluster UNC6201, which has used the flaw for lateral movement and to deploy payloads including SLAYSTYLE, BRICKSTORM, and a new hard-to-analyze backdoor named GRIMBOLT. #UNC6201 #GRIMBOLT
Google says it blocked more than 255,000 Android apps from obtaining excessive access to sensitive user data and rejected over 1.75 million apps from Google Play through 2025 as part of strengthened protections. The company expanded AI-assisted reviews, Play Protect scanning, Play Integrity API checks, and Android 16 tapjacking defenses to detect malicious developers, curb review-bombing, and prevent app-based fraud. #Google #Android