OpenClaw’s popularity was weaponized by attackers who posted fake “OpenClaw Windows” installers on GitHub and leveraged Bing AI suggestions to drive users to malicious repositories that delivered information stealers and the GhostSocks proxy. Huntress researchers found Vidar (cloudvideo.exe), GhostSocks (serverdrive.exe), and a new “stealth packer” used to run loaders and in-memory…
Category: Cyber Security News
A threat actor sent extortion emails to customers of restaurants using the HungerRush POS platform, claiming access to millions of customer records and threatening to expose data if demands were not met. HungerRush says the actor used a third‑party vendor’s compromised credentials to access its email marketing service, has disabled the…
Researchers at ClearSky uncovered a campaign that leverages ukr.net email addresses to deliver a ZIP that contains an HTA disguised as an HTML file. The operation, named BadPaw, uses tracking redirects, Windows install-age sandbox checks, steganography-backed persistence, and staged C2 downloads that deploy the MeowMeowProgram backdoor. #BadPaw #MeowMeowProgram…

LastPass warned users about an active phishing campaign that spoofs its display name and sends fake security alerts to trick victims into revealing their master password. The emails direct recipients to a fraudulent SSO site to harvest credentials and LastPass urges users to report suspicious messages. #LastPass #verify-lastpass…
A Russian national, Evgenii Ptitsyn, pleaded guilty to a wire fraud conspiracy for administering the Phobos ransomware operation that breached hundreds of victims worldwide and helped collect over $39 million from more than 1,000 organizations. He was extradited from South Korea, faces up to 20 years with sentencing set for July 15, and international law enforcement actions under Operation Aether disrupted Phobos infrastructure and led to multiple arrests. #Phobos #EvgeniiPtitsyn
Cisco warns that two additional Catalyst SD-WAN Manager vulnerabilities (CVE-2026-20122 and CVE-2026-20128) are being actively exploited in the wild and urges administrators to upgrade vulnerable devices. The flaws—one a high-severity arbitrary file overwrite accessible with read-only API credentials and the other a medium-severity information disclosure needing local vManage credentials—affect Catalyst SD-WAN Manager regardless of configuration and follow earlier zero-day compromises like CVE-2026-20127. #CatalystSDWANManager #CVE202620122

Tycoon 2FA was a subscription-based phishing-as-a-service toolkit that enabled adversary-in-the-middle credential harvesting at scale, capturing credentials, MFA codes, and session cookies to facilitate account takeovers across thousands of organizations. A coordinated law enforcement and private-sector operation disrupted the platform by taking down 330 domains and dismantling the infrastructure behind the service….

Researchers disclosed a Russian-linked campaign targeting Ukrainian entities that uses phishing emails and HTA lures to deploy two previously undocumented malware families, BadPaw and MeowMeow. The infection chain features sandbox evasion, a .NET loader that contacts a C2 to fetch a MeowMeow backdoor, and has been attributed with moderate confidence to…
Cisco released fixes for 50 vulnerabilities across its products, including 48 affecting ASA, Secure FMC, and Secure FTD appliances, bundled in a March 2026 publication containing 25 security advisories. Two critical CVEs (CVE-2026-20079 and CVE-2026-20131, both rated 10.0) allow remote attackers to execute arbitrary scripts or Java code and gain root…
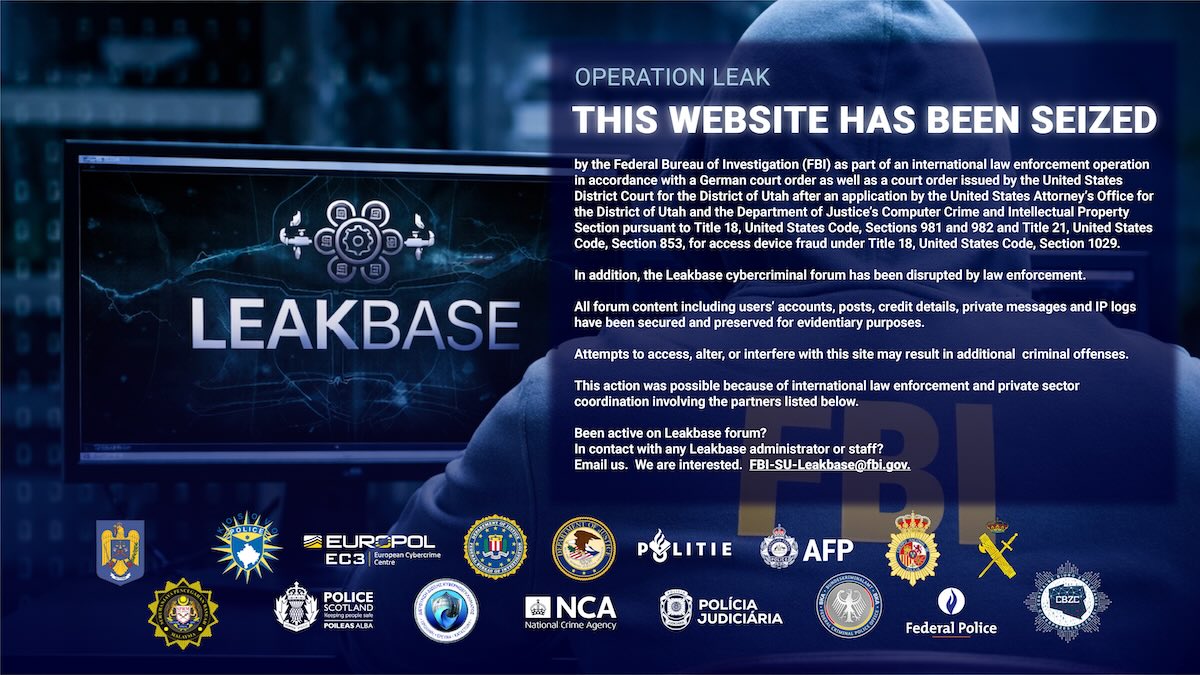
International law enforcement shut down the cybercrime forum LeakBase and seized its database under Operation Leak, enabling investigators to identify multiple users and carry out arrests and searches across North America, Europe, and the APAC region. Evidence including account details, forum posts, approximately 215,000 private messages, IP logs, and transaction records…
A Florida software distributor, Heidi Richards, was sentenced to 22 months in federal prison and ordered to pay a $50,000 fine after a jury convicted her of conspiring to traffic in Microsoft Certificate of Authenticity (COA) labels. Investigators found she bought thousands of genuine COA labels through Trinity Software Distribution, extracted…

CYFIRMA researchers exposed a sophisticated campaign by Pakistan-aligned Transparent Tribe (APT36) targeting Indian government and defense organizations using social-engineered ZIPs and a multi-stage infection chain for long-term espionage. The operation uses deceptive LNK shortcuts and a PowerPoint PPAM with macro-based payload reconstruction to deploy a RAT (hsuzoiaisaacrhy.exe) that connects to a…
Check Point Research disclosed Silver Dragon, an advanced persistent threat linked to APT41, conducting stealthy espionage against government and high-profile organizations across Southeast Asia and Europe since mid-2024. The group delivers Cobalt Strike through three infection chains and operates GearDoor, a .NET backdoor that uses Google Drive for file-based C2, enabling…

ClearSky Team uncovered a targeted Russian state-aligned campaign against Ukraine that uses border-crossing appeals to deliver two novel malware strains, BadPaw and MeowMeow. The multi-stage attack uses ukr.net phishing, an HTA/VBScript loader that extracts payloads via steganography, a .NET Reactor-protected BadPaw loader with a ‘-renew’ parameter check, and a MeowMeow backdoor…
Researchers from Google Threat Intelligence Group and iVerify independently identified a nation-state–grade iOS exploit kit, internally named Coruna, containing 23 exploits across five full exploit chains targeting iOS 13 through 17.2.1. The kit was used by UNC6353 in watering‑hole attacks against Ukrainians and later repurposed by UNC6691 for mass crypto‑wallet theft;…