
Europol-led international law enforcement has dismantled LeakBase, a prominent online marketplace for stolen credentials that hosted over 142,000 registered users, thousands of posts, and extensive stealer logs. Coordinated actions across multiple countries seized the forum’s domain, targeted top users, exposed weaknesses in perceived anonymity, and prompted warnings that stolen data often…
Category: Cyber Security News
Researchers report a suspected Russian espionage campaign targeting Ukraine that starts with a phishing email containing a ZIP archive and a malicious Ukrainian-language document, which triggers a loader called BadPaw and installs a backdoor named MeowMeow. The MeowMeow backdoor enables file access and manipulation, includes anti-analysis checks that terminate execution in…

The FBI and international partners executed Operation Leak to dismantle Leakbase, seizing the forum’s database, domains, and hosting infrastructure after coordinated actions in over a dozen countries. The multi-year effort produced 13 arrests, dozens of searches and interviews, and highlights law enforcement’s push to disrupt marketplaces trading stolen credentials and exploits….
Zurich has agreed to acquire UK-based Beazley for approximately £8.1 billion, aiming to strengthen its cyberinsurance and specialty lines by integrating Beazley’s Full Spectrum Cyber offering and Lloyd’s market presence. The combined entity is expected to generate roughly $15 billion in specialty gross written premiums, deliver about $150 million in annual…
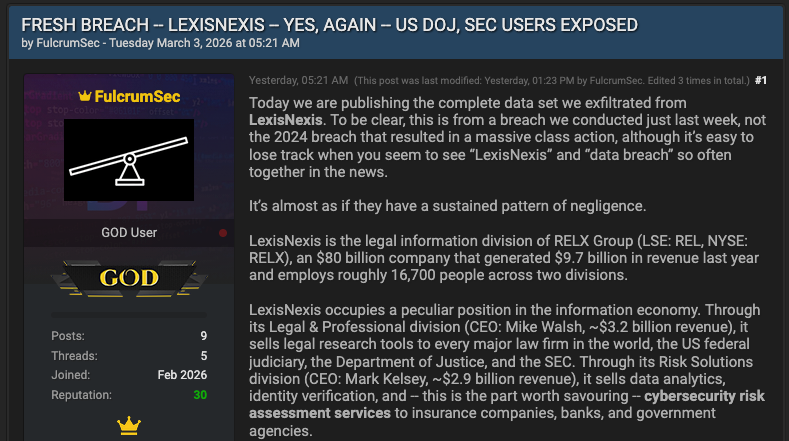
LexisNexis confirmed a data breach after hackers leaked data allegedly stolen from its systems, saying the impact is limited and that compromised servers primarily held legacy data from before 2020. The attackers claimed to exploit the React2Shell vulnerability and misconfigured AWS instances to exfiltrate over 2GB of data, allegedly including enterprise…
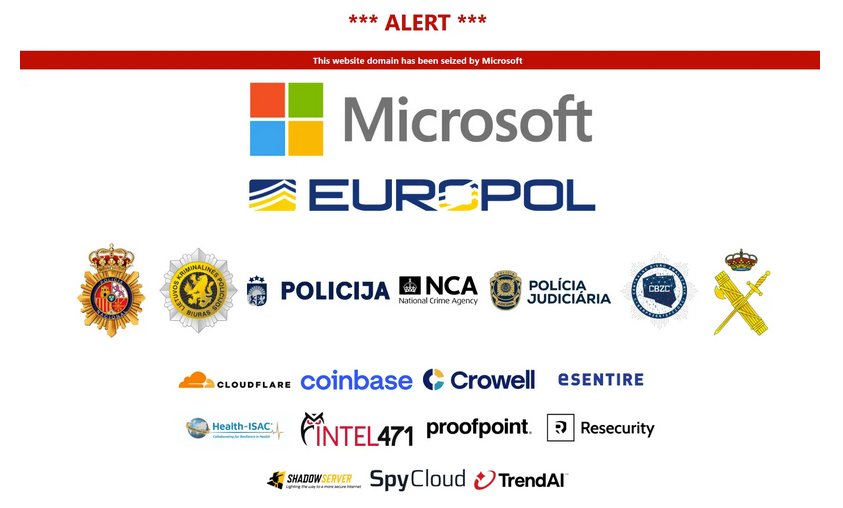
Europol, Microsoft, and multiple cybersecurity firms coordinated a takedown of the subscription-based phishing-as-a-service platform Tycoon 2FA, which enabled attackers to impersonate users, deploy convincing phishing pages, and bypass multi-factor authentication to access email and cloud accounts. The operation seized 330 active domains, disrupted tens of millions of phishing emails affecting roughly…
Cisco has released security updates to fix two maximum-severity vulnerabilities in its Secure Firewall Management Center (FMC) that could allow remote, unauthenticated attackers to gain root access or run arbitrary code. The flaws—an authentication bypass (CVE-2026-20079) and a remote code execution via serialized Java objects (CVE-2026-20131)—have been patched and Cisco PSIRT reports no current evidence of active exploitation or published proof-of-concept code at this time. #CVE202620079 #CVE202620131
LastPass is warning users about a phishing campaign that spoofs the ‘LastPass Support’ display name and uses fake forwarded internal email threads to pressure recipients into clicking links like “report suspicious activity,” “disconnect and lock vault,” and “revoke device.” The links lead to credential-stealing pages on domains such as verify-lastpass[.]com and lookalikes; LastPass says its systems were not breached, reminds users support will never ask for their master password, and asks that suspicious messages be reported to [email protected]. #LastPass #verify-lastpass
Microsoft released KB5075039 to fix a longstanding issue that prevented some users from accessing the Windows Recovery Environment (WinRE) after October 2025 updates. The update corrects the WinRE startup failure introduced by KB5068164 and requires a WinRE partition of at least 256MB to install, so users should back up data before resizing partitions. #WinRE #KB5075039
A maximum-severity remote code execution vulnerability in the FreeScout helpdesk platform (CVE-2026-28289) allows unauthenticated attackers to achieve server compromise by delivering a single crafted email attachment. Researchers at OX Security say the flaw bypasses a previous fix (CVE-2026-27636) using a leading zero-width space to create executable dotfiles; administrators should upgrade to FreeScout 1.8.207 and consider disabling AllowOverrideAll in Apache. #FreeScout #CVE-2026-28289
Bitwarden now lets users sign into Windows 11 with passkeys stored in the manager’s encrypted vault, enabling phishing‑resistant passwordless authentication. The feature is available on all plans and requires Entra ID–joined devices, FIDO2 security key sign‑in enabled, and a registered Entra ID passkey in the Bitwarden vault, with Bitwarden acting as the passkey provider to allow cross‑device recovery and reduce credential exposure. #Bitwarden #Windows11 #EntraID #FIDO2
LexisNexis Legal & Professional confirmed that threat actor FulcrumSec exploited the React2Shell vulnerability in an unpatched React frontend to access its AWS infrastructure and exfiltrated roughly 2.04 GB of data, including Redshift tables, plaintext AWS Secrets Manager secrets, and records tied to government-affiliated email addresses. The company says the accessed material…

Daily Recap, a multi-vector campaign by state-aligned actors and hacktivists is escalating after allied strikes, with claimed intrusions and a plunge in Iranian connectivity to 1–4% that raises supply-chain and high-value target risks. In notable developments, SloppyLeming targeted Pakistan, Bangladesh and Sri Lanka with BurrowShell and Excel keyloggers; APT28 is linked to the CVE-2026-21513 MSHTML zero-day; breaches at the University of Hawaiʻi Cancer Center and Madison Square Garden were disclosed, while TPMS privacy tracking and Singapore router security efforts illustrate broader defensive trends. #SloppyLemming #BurrowShell #APT28 #MSHTML #CVE2026-21513 #UH #MSG #TPMS #SingaporeRouters #MerkleTreeCerts #GTA

Data analytics firm LexisNexis confirmed that information posted on a cybercriminal forum is legitimate and related to a recent security incident in which a threat actor accessed a limited number of servers containing mostly legacy, pre-2020 data such as customer names, user IDs, business contact information, product usage details and support…

The California Privacy Protection Agency fined PlayOn Sports $1.1 million and ordered changes after finding the company required users — including large numbers of high school students — to accept tracking to access tickets and services. The CPPA said PlayOn’s opt-out process improperly relied on third-party tools and lacked clear disclosures,…