A critical vulnerability (CVE-2026-1492) in the WPEverest User Registration & Membership WordPress plugin lets attackers register accounts with an administrator role, affecting more than 60,000 sites. Site owners should update to version 5.1.4 or disable the plugin immediately to prevent privilege escalation, data theft, and malware distribution; Wordfence blocked over 200…
Category: Cyber Security News
UAT-9244, a China-linked APT, has been targeting telecommunication service providers in South America since 2024, compromising Windows, Linux, and network-edge devices. Cisco Talos links the campaign to three new malware families—TernDoor, PeerTime, and BruteEntry—and published technical details and IoCs to help defenders. #UAT-9244 #TernDoor #PeerTime #BruteEntry
Evgenii Ptitsyn, a 43-year-old Russian national, pleaded guilty to wire fraud after U.S. prosecutors accused him of being a key developer and operator of the Phobos ransomware gang that began attacking organizations in November 2020. He faces up to 20 years in prison, was extradited from South Korea in November 2024,…

A criminal network in Spain exploited dozens of displaced Ukrainian women to open bank accounts that the group hijacked to launder roughly $5.5 million through automated betting schemes. Police arrested 12 suspects after a two-year probe, seizing cash, cryptocurrency, luxury vehicles and devices, and uncovering over 5,000 stolen identities and about…

Passaic County, New Jersey, reported a malware attack that disrupted county IT systems and phone lines used across government offices, affecting services for nearly 600,000 residents. Officials say they are working with federal and state partners to investigate and contain the incident amid a wider wave of attacks on smaller municipalities…
Check Point Research reports that Iranian‑nexus threat actors have intensified campaigns to compromise IP cameras across the Middle East, using known Hikvision and Dahua vulnerabilities to create a real‑time reconnaissance network that supports missile operations and battle damage assessment. The activity—linked to events like a 2025 missile strike on the Weizmann…
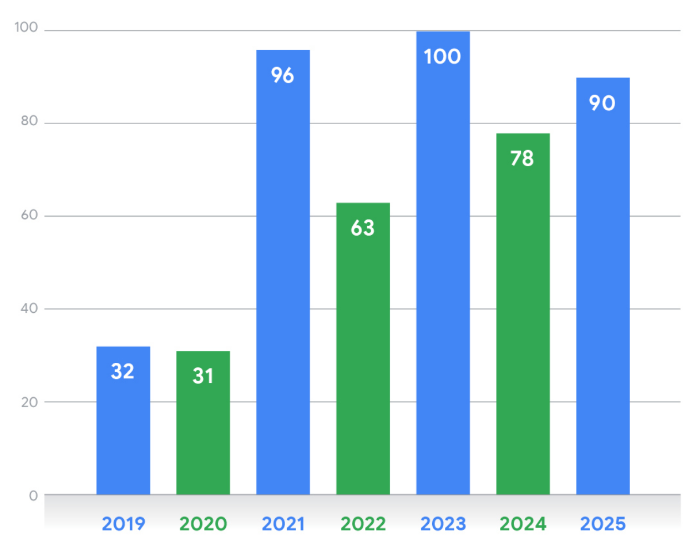
Google’s Threat Intelligence Group reported 90 zero-day vulnerabilities exploited in the wild in 2025, up from 78 in 2024, with operating systems and mobile devices increasingly targeted and Microsoft, Google, Apple, and Cisco among the most affected vendors. Attribution links 42 zero-days to specific actors—commercial surveillance vendors exploited the largest share…
The 2026 State of Browser Security Report shows that browsers have become the most critical and least protected control point as AI-native browsers and embedded copilots moved from experiment to mainstream in 2025. The report highlights growing gaps in visibility and governance—especially around sensitive uploads, personal accounts, browser-based attacks, and risky extensions. #KeepAware #AIcopilots
Google Threat Intelligence Group tracked 90 zero-day vulnerabilities actively exploited in 2025, nearly half of which targeted enterprise software and appliances. Commercial spyware vendors overtook state-sponsored groups in zero-day use, Microsoft was the most-targeted vendor, and the report highlights campaigns like Brickstorm while warning exploitation will likely remain high into 2026 due to AI-assisted discovery. #Microsoft #Brickstorm
Spanish and Ukrainian authorities dismantled a criminal ring that exploited war-displaced Ukrainian women to open bank accounts and launder nearly €4.75 million through automated low-odds bets on online gambling platforms using stolen identities. Spanish police arrested 12 suspects after a joint probe with Ukrainian authorities, seizing devices, bots, vehicles, SIM cards, freezing properties and blocking accounts across multiple countries. #SpanishNationalPolice #Europol

International law enforcement dismantled a major phishing-as-a-service platform called Tycoon 2FA, seizing 330 domains used to host phishing sites and operate its infrastructure. The service intercepted authentication sessions to bypass multi-factor authentication, sending tens of millions of phishing emails monthly and targeting over 500,000 organizations—particularly hospitals and schools—leading to operational disruptions…
Reclaim Security announced a $20 million Series A round led by Acrew Capital, bringing its total funding to $26 million to expand engineering, integrations, and go-to-market efforts in North America and Europe. The startup’s autonomous platform uses an AI Security Engineer and a simulation engine called PIPE to predict remediation impact,…
Cisco warns that two recently patched Catalyst SD-WAN vulnerabilities (CVE-2026-20128 and CVE-2026-20122) are being actively exploited in the wild. These incidents follow a separate exploited zero-day (CVE-2026-20127) linked to threat actor UAT-8616, highlighting targeted attacks against Catalyst SD-WAN devices. #CatalystSDWAN #UAT8616…
Evgenii Ptitsyn, a 43-year-old Russian national, has pleaded guilty in the United States to wire fraud conspiracy for his role in the Phobos ransomware operation. He was arrested in South Korea in June 2024, extradited to the U.S. in November, faces up to 20 years in prison with sentencing set for…
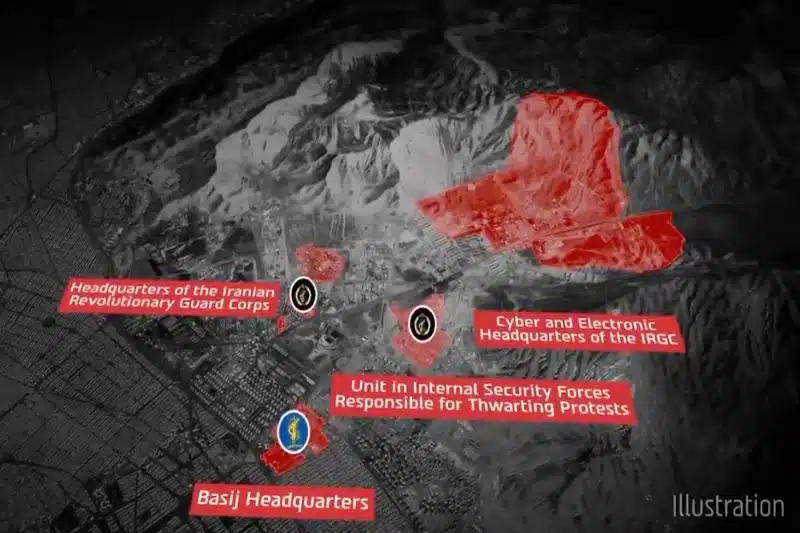
Israel says it struck a Tehran compound hosting Iran’s cyber warfare headquarters, the IRGC and the Intelligence Directorate, but officials have provided few details and the strike’s effect on Tehran’s cyber capabilities remains unclear. Researchers warn pre-positioned APT footholds (MuddyWater, APT42, Prince of Persia, CRESCENTHARVEST), a RedAlert-themed Android phishing campaign and…