
An unknown threat actor cloned the CERT-UA website and sent phishing emails distributing a password‑protected archive that installed AGEWHEEZE, a Go‑based remote access trojan. The campaign—claimed by CyberSerp and using OVH‑hosted WebSocket C2 infrastructure—was largely unsuccessful according to CERT‑UA, which published IOCs and mitigation guidance. #CERT-UA #AGEWHEEZE…
Category: Cyber Security News
Cybersecurity Is a Calling, Not Just a Career — Dr. Priyanka Sunder (PD) on Women Leading the Charge
Dr. Priyanka Sunder is a multi-award-winning cybersecurity strategist and co-founder of CHRIO SecureMojo with two decades of leadership in GRC, cloud security, and enterprise resilience across nine countries. She describes the shift from checkbox compliance to continuous resilience, promotes Security by Design for aligning frameworks like NIST and ISO 27001, and…
The UAE is facing an unprecedented surge in AI-powered cyberattacks—estimated at 500,000 to 700,000 attempts daily—driven by hostile, state-linked actors using tools like ChatGPT for reconnaissance, phishing, deepfakes, and malware development. The Cyber Security Council says national defenses, including a zero-trust framework and the National Cyber Security Operations Centre, are detecting…
Attackers are actively exploiting CVE-2026-21643, a critical SQL injection in Fortinet’s FortiClient EMS that allows unauthenticated actors to execute arbitrary code via the EMS web interface. The flaw affects FortiClient EMS 7.4.4 and can be remediated by upgrading to 7.4.5 or later, while thousands of instances remain exposed online according to Shodan and Shadowserver. #CVE202621643 #FortiClientEMS
Microsoft has paused the rollout of optional Windows 11 preview update KB5079391 after users encountered installation failures that return error 0x80073712. The update—which targeted 24H2 and 25H2 with 29 changes including Smart App Control and display improvements—will be investigated and is likely to be fixed before the April 14 Patch Tuesday release to allow broader testing. #KB5079391 #Windows11

Cybersecurity Threat Research ‘Weekly’ Recap: A broad survey of supply-chain compromises, credential theft, phishing, and malware campaigns spanning PyPI, npm, Docker images, and cloud developer tooling. It highlights operations by LiteLLM/TeamPCP, GlassWorm, EvilTokens, Remcos/XWorm, VoidLink, DarkSword, and PawnStorm among others, with defender guidance on monitoring pipelines, web threats, persistence, and detection across platforms. #LiteLLM #TeamPCP #GlassWorm #EvilTokens #Remcos #XWorm #VoidLink #DarkSword #PawnStorm #PRISMEX #Magecart #WebLogic #CVE2026-21962 #Cloudflare #Telnyx #FriendlyDealer #Keitaro #InfinitiStealer #IceCloudScanner #Trivy #GhostCampaign #OpenClaw #TroyDen
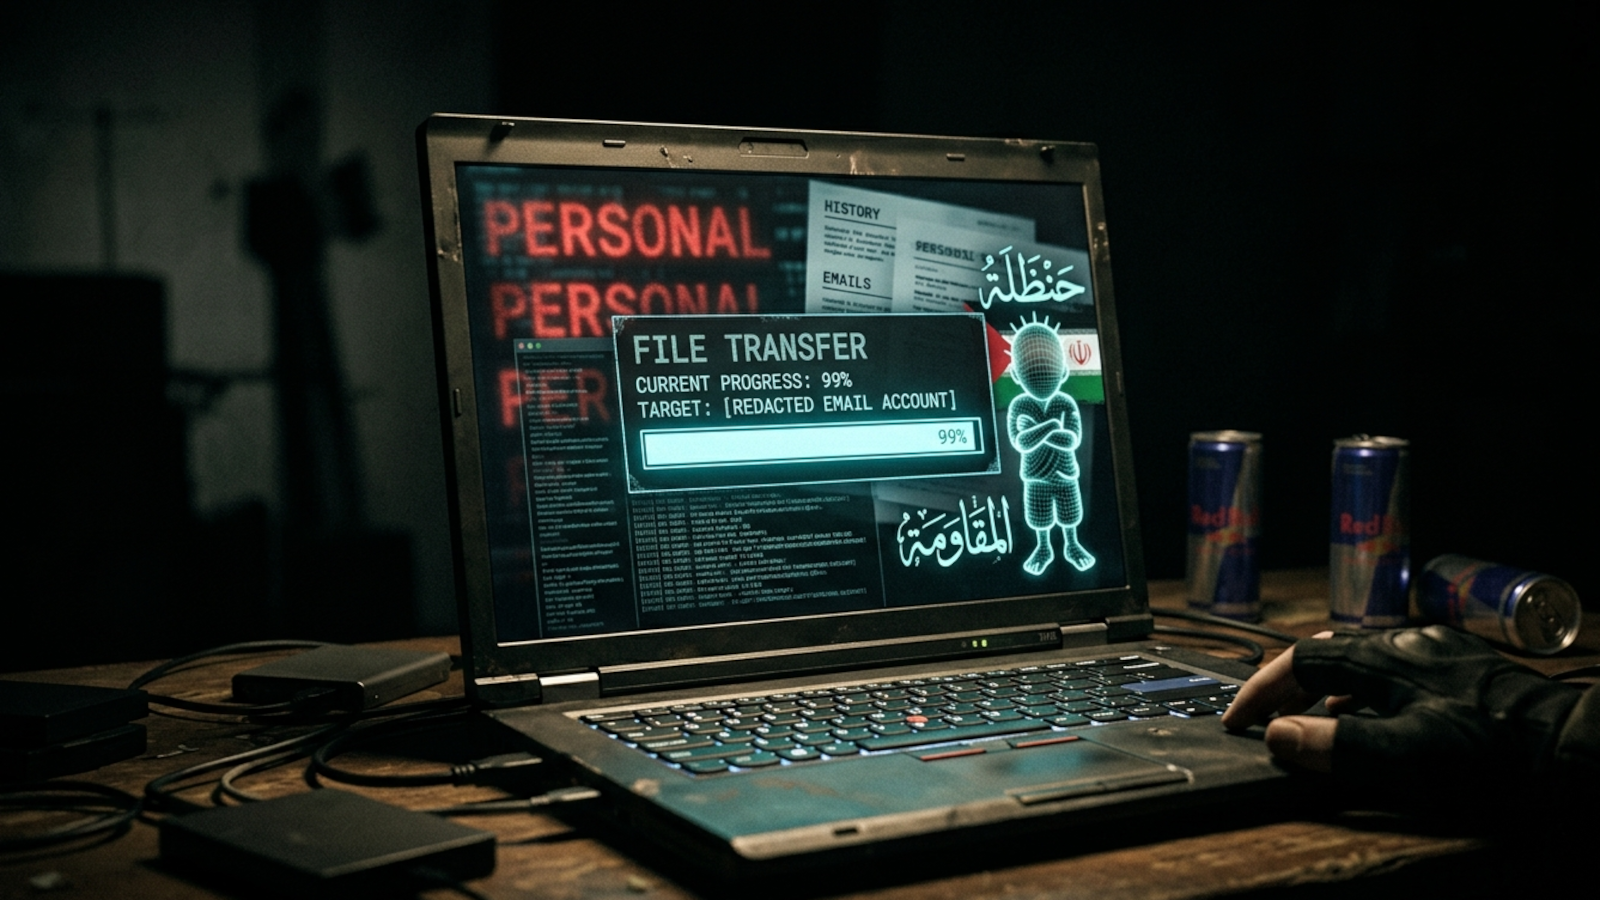
Iran-linked Handala hackers breached the personal Gmail account of FBI Director Kash Patel and published photos, documents, and historical email correspondence. The FBI confirmed the compromise involved non-government, historical data and said it has taken steps to mitigate risks. #Handala #KashPatel
A vulnerability in the Smart Slider 3 WordPress plugin, installed on over 800,000 sites, allows authenticated subscriber-level users to read arbitrary server files—including wp-config.php—putting database credentials, keys, and salts at risk and enabling full site takeover. Tracked as CVE-2026-3098 and fixed in version 3.5.1.34, the flaw stems from missing capability and file-type checks in AJAX export actions and leaves roughly 500,000 sites still running vulnerable versions that should update immediately. #SmartSlider3 #CVE-2026-3098

Daily Recap, a roundup of recent cybersecurity activity highlights macOS ClickFix delivering Infiniti Stealer via a Nuitka loader, iOS exploitation by TA446 using DarkSword to deploy GHOSTBLADE and MAYBEROBOT, and backdoored Telnyx PyPI packages pushed by TeamPCP that use WAV steganography to exfiltrate SSH keys and tokens. The report also covers critical advisories (CVE-2026-3055, CVE-2025-53521), the Open VSX Open Sesame fix, major breaches including the European Commission cloud incident and Handala’s alleged exfiltration of FBI director materials, plus governance moves such as the CSAM ruling, UK donation limits, the Chip Security Act, and OpenAI’s Bug Bounty program. #InfinitiStealer #DarkSword #GHOSTBLADE #MAYBEROBOT #TeamPCP #Telnyx #NetScaler #CVE2026-3055 #CVE2025-53521 #EuropeanCommission #AnimePlay #Handala #OpenAI #Bugcrowd #OpenVSX #CSAMRuling #ChipSecurityAct

Iran-linked threat actors operating under the Handala Hack persona breached FBI director Kash Patel’s personal email and published historical photos and documents online. The group, assessed as tied to Iran’s MOIS and known for destructive wiper operations including the Stryker attack, leverages compromised VPNs, Microsoft Intune abuse, RDP lateral movement, Telegram…
A new info-stealing campaign called Infinity Stealer targets macOS by delivering a Python payload compiled into a native executable with the Nuitka compiler and lures users via a ClickFix fake Cloudflare CAPTCHA. The payload performs anti-analysis checks, harvests browser credentials, macOS Keychain entries, cryptocurrency wallets and plaintext developer secrets, and exfiltrates data to a C2 via HTTP while notifying operators via Telegram; users should never paste unknown commands into Terminal. #InfinityStealer #Nuitka
Malwarebytes reports a macOS-targeted ClickFix campaign that lures victims to paste and run a Cloudflare-themed Terminal command which downloads a Bash script that deploys a Nuitka-compiled loader and the Infiniti Stealer information stealer. The Python-based stealer harvests browser credentials, Keychain items, crypto wallets, developer secrets and screenshots, exfiltrates data to a…
Daily Recap, critical flaws in PTC Windchill/FlexPLM are being exploited or mitigated, with mitigations available but no patch yet and German authorities mobilized, while Langflow’s code-injection flaw (CVE-2026-33017) is being actively exploited for unauthenticated RCE and requires upgrading to 1.9.0 or disabling the endpoint. Breaches and espionage actions span energy-sector ransomware campaigns by FrostyGoop, RansomHub and Zerosevengroup; Bearlyfy’s GenieLocker deployments against Russian firms; Nova Scotia Power data exposure after SocGholish intrusion; and state-linked activity around Red Menshen, Nasir Security, RedLine, Xinbi, plus enforcement moves such as Apple’s age-verification push and Snapchat’s DSA probe. #PTCWindchill #Langflow #Claude #ShadowPrompt #GenieLocker #Bearlyfy #NovaScotiaPower #RedMenshen #NasirSecurity #RedLine #Xinbi #TikTokForBusiness #Snapchat #SocGholish

Proofpoint disclosed a targeted email campaign by Russia-linked TA446 that used the leaked DarkSword iOS exploit kit to target iPhones and iPads. The attacks spoofed the Atlantic Council, delivered the GHOSTBLADE dataminer and MAYBEROBOT backdoor, and prompted Apple to send Lock Screen warnings as DarkSword code leaked on GitHub. #TA446 #DarkSword…

CISA added a critical F5 BIG-IP Access Policy Manager flaw, CVE-2025-53521 (CVSS v4 9.3), to its Known Exploited Vulnerabilities catalog after evidence of active exploitation that can lead to remote code execution. F5 confirmed exploitation, published file and log indicators plus TTPs to detect compromise, and advised patched fixes for affected…