
A critical input-validation flaw, CVE-2026-3055 (CVSS 9.3), in Citrix NetScaler ADC and NetScaler Gateway is seeing active reconnaissance as attackers probe /cgi/GetAuthMethods to fingerprint authentication methods and identify SAML IDP configurations. Organizations running affected NetScaler versions must patch immediately because exploitation could leak sensitive information and past NetScaler flaws have been…
Category: Cyber Security News
TeamPCP compromised the official Telnyx PyPI package by publishing backdoored versions 4.87.1 and 4.87.2 that install credential‑stealing malware hidden via steganography in WAV files and deploy second‑stage payloads to exfiltrate SSH keys, cloud tokens, wallets, and other secrets. Researchers (Aikido, Socket, Endor Labs) attribute the supply‑chain attack to TeamPCP, advise rolling back to Telnyx 4.87.0, treating any importer as fully compromised, and rotating all secrets immediately. #TeamPCP #Telnyx

Open VSX’s pre-publish scanning pipeline contained a bug that misinterpreted scanner failures as “no scanners configured,” allowing a malicious VS Code extension to pass vetting and go live. The flaw, dubbed Open Sesame, could be triggered by flooding the publish endpoint to exhaust the database connection pool and was fixed in…

TeamPCP compromised the telnyx PyPI package by publishing malicious versions 4.87.1 and 4.87.2 that use audio steganography in .WAV files to deliver credential-harvesting payloads across Windows, Linux, and macOS; users should immediately downgrade to 4.87.0 and follow mitigation steps. The campaign persists on Windows via a Startup-dropped msbuild.exe, exfiltrates collected data…

Apple is sending Lock Screen notifications to iPhones and iPads running older iOS and iPadOS to warn users of web-based attacks and urge installation of a critical update. The alerts follow disclosures about exploit kits Coruna and DarkSword—used by multiple threat actors to deliver malicious payloads via compromised websites—and advise updating…

An Iran-linked hacking group called Handala published alleged personal photographs and emails taken from FBI Director Kash Patel’s personal email following U.S. domain seizures and a $10 million reward for information on the group. The Justice Department and FBI say the material is historical and non-governmental, while Handala framed the leak…

The European Parliament voted against extending a temporary rule that allowed tech platforms to scan private communications for child sexual abuse material (CSAM), meaning those scanning tools will lose their legal exemption from strict privacy rules when the rule lapses next Friday. Supporters including law enforcement, several European commissioners and major…
The Alliance for Creativity and Entertainment (ACE) shut down AnimePlay, a major illegal anime streaming platform that hosted over 60 terabytes of content and more than 5 million registered users. ACE seized the app and its underlying infrastructure—including 15 domains, hosting servers, source code and 29 GitHub repositories—after the developer surrendered backend systems, as part of its broader anti-piracy campaign with partners such as the Motion Picture Association. #AnimePlay #ACE
The European Commission is investigating a breach after a threat actor gained access to at least one of its Amazon Web Services accounts and claims to have stolen over 350 GB of data, including employee information and an email server. AWS says its services operated as designed, the Commission’s incident response team detected the intrusion quickly, and the actor says they will not extort the Commission but intend to leak the data later; the incident follows other EPMM-related attacks and coincides with EU efforts to strengthen defenses and sanction hostile cyber actors. #EuropeanCommission #AWS

A large-scale campaign is targeting developers on GitHub by posting fake Visual Studio Code security alerts in repository Discussions to trick users into downloading malware. The posts impersonate maintainers, include fake CVE IDs and external Google Drive links that redirect to drnatashachinn[.]com, which runs a JavaScript reconnaissance script to profile victims before delivering a second-stage payload. #VisualStudioCode #GitHub

Two major reports warn that foreign interference in U.K. democracy is becoming more complex and spans both financial systems and the information environment, with hostile and transnational actors exploiting divisive issues and online platforms. The government plans tighter rules on political donations — including a temporary ban on cryptocurrency donations and…
OpenAI has announced a public safety bug bounty program focused on AI-specific abuse and safety risks in its products, complementing its existing security bounty program. The Bugcrowd-run program accepts reports on prompt injection, data exfiltration, agentic product abuse, connector vulnerabilities, and exposure of proprietary information, with discretionary rewards up to $7,500…

This week’s roundup highlights disruptions to transit and critical services, high-profile account hijacking campaigns, data breaches, and advances in defensive technology and policy. Key items include a Los Angeles Metro lockout amid a World Leaks claim, FBI and CISA warnings about messaging-account hijacks, outages at Intoxalock and Heritage Bank data theft,…
Pro-Iranian hacking group Handala claimed it breached a personal email account of FBI Director Kash Patel and published years-old photos, a resume, and other personal documents online. The FBI acknowledged a personal account was compromised earlier, and the Justice Department has seized web domains tied to Iranian-linked hacking operations. #Handala #KashPatel…
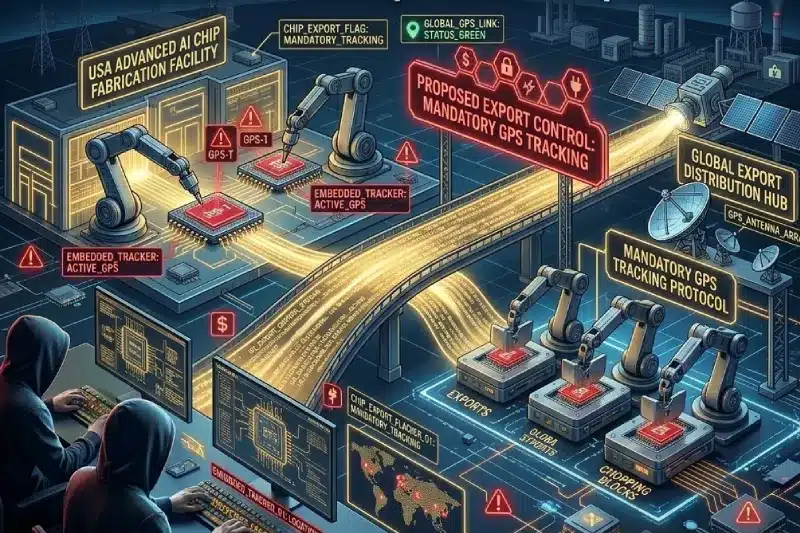
DeepSeek’s use of restricted Nvidia accelerators prompted Congress to move the Chip Security Act through the House Foreign Affairs Committee, shifting smuggling from an enforcement problem to a legislative emergency. The bill would require continuous location-verification mechanisms on exported advanced AI chips, mandate prompt diversion reporting, and aims to prevent trans-shipment…