Cisco released security updates for multiple critical vulnerabilities, including an Integrated Management Controller (IMC) authentication bypass (CVE-2026-20093) that can let attackers gain Admin access to UCS C‑Series and E‑Series servers. Patches are strongly recommended because there are no mitigations; fixes also cover a Smart Software Manager On‑Prem RCE (CVE-2026-20160), the FMC RCE previously exploited by Interlock (CVE-2026-20131), and follow a reported breach tied to the Trivy supply chain attack. #CiscoIMC #CVE-2026-20093 #SSMOnPrem #CVE-2026-20160 #FMC #CVE-2026-20131 #Interlock #Trivy
Category: Cyber Security News
Stryker says it is fully operational three weeks after a cyberattack claimed by the Iranian‑linked Handala group that stole roughly 50 terabytes of data and wiped nearly 80,000 devices after compromising a Windows domain admin and creating a Global Administrator account. CISA and Microsoft issued guidance to secure Intune and harden Windows domains, the FBI seized two Handala websites, investigators found a stealthy malicious file used to hide activity, and Stryker reports production moving rapidly toward full capacity. #Stryker #Handala
Two vulnerabilities in Progress ShareFile’s Storage Zones Controller can be chained to enable unauthenticated file exfiltration and remote code execution on affected systems. The flaws (CVE-2026-2699 and CVE-2026-2701) were reported by watchTowr and fixed in Progress ShareFile 5.12.4 on March 10, but exposed instances should be patched immediately. #ProgressShareFile #StorageZoneController
Threat actors are abusing vacant residential properties, real estate listings, postal services, and weak identity verification to intercept and redirect mail for identity theft and financial fraud. Flare analysts observed tutorials on Telegram and dark web forums showing how to find “drop” addresses, use services like Informed Delivery and Change of Address, and set up persistent mail forwarding with fake identities to scale low-tech, hard-to-detect fraud operations. #InformedDelivery #USPS
Cisco released patches addressing two critical and six high-severity vulnerabilities that could enable authentication bypass, remote code execution, privilege escalation, and information disclosure. The critical flaws — CVE-2026-20160 in Cisco Smart Software Manager On-Prem and CVE-2026-20093 allowing password-change authentication bypass — can lead to root-level command execution and administrator account takeover;…
AVrecon is a modular router-targeting malware that scans for exposed services and exploits RCE, command injection, and SOAP flaws to convert home and SOHO routers into proxy nodes. Law enforcement linked AVrecon to the SocksEscort residential proxy service, which sold access to roughly 369,000 compromised devices used for banking fraud, ad…
The FBI warns that many popular foreign-developed mobile apps—particularly those from China—can collect extensive device data, harvest contacts and location information, and store that data on servers subject to Chinese law, creating privacy and jurisdictional risks. The advisory also cautions that some apps may contain hidden malware and urges users to…
Shadowserver has found over 14,000 F5 BIG-IP APM instances exposed online amid active attacks exploiting CVE-2025-53521, a flaw recently reclassified from a denial-of-service to a remote code execution vulnerability. F5 has published IOCs and remediation guidance, urging checks of disks, logs, and terminal history and recommending rebuilding systems from known-good sources, while CISA ordered federal agencies to secure their BIG-IP APM systems. #CVE-2025-53521 #BIG-IP_APM
Microsoft is investigating a known issue that prevents some Classic Outlook users from sending emails via Outlook.com, causing non-delivery reports and a permissions error (0x80070005-0x0004dc-0x000524). Microsoft recommends temporary mitigations—removing the M365 Address Book, hiding the Outlook.com contact from the tenant GAL, creating a new Classic Outlook profile, or using New Outlook/Outlook on the web—while it continues to investigate. #ClassicOutlook #ExchangeOnline
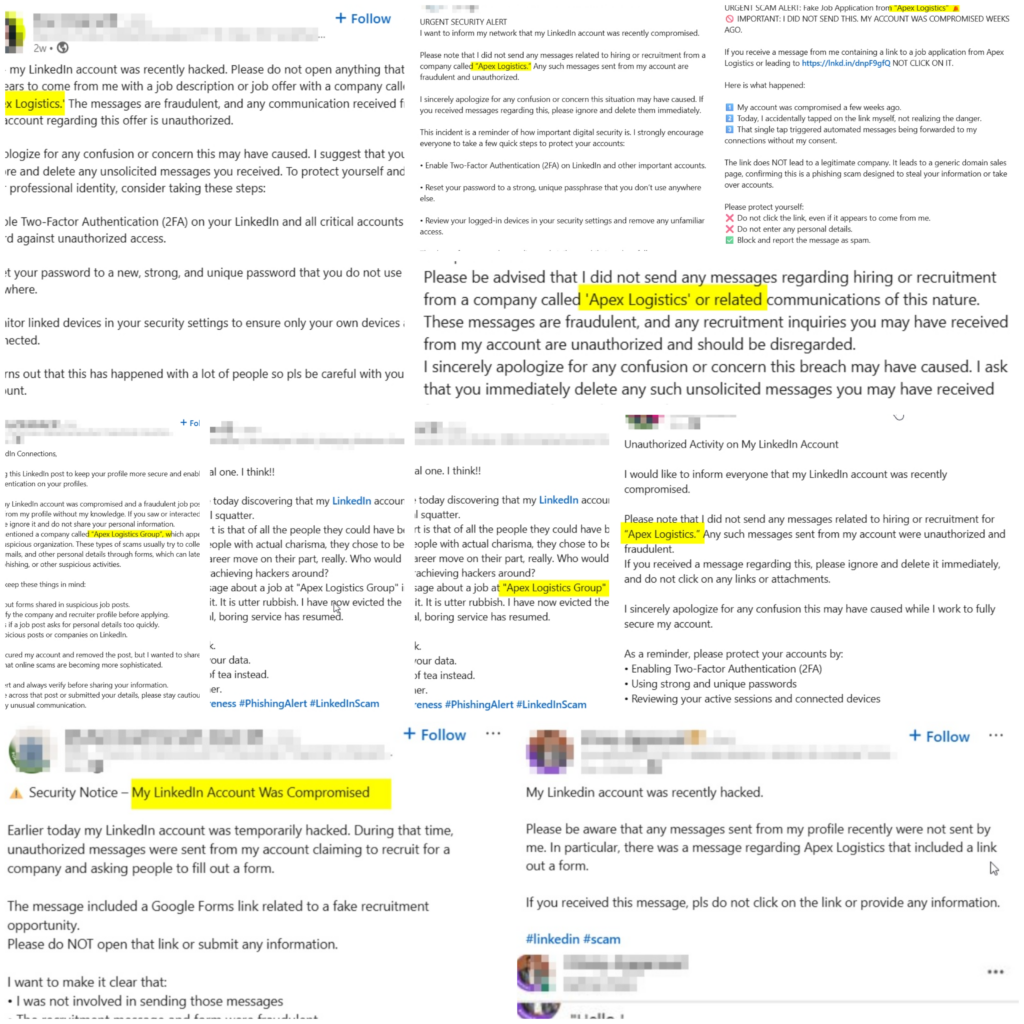
A newly exposed global campaign shows Vietnam‑linked actors using LinkedIn and spoofed recruiter accounts such as Apex Logistics Group to distribute PXA Stealer and siphon credentials, crypto wallet data, and other sensitive information from professionals across multiple countries. The multi‑stage operation leverages Google Forms, URL shorteners, cloud‑hosted ZIPs with oversized DLLs,…
Linx Security raised $50 million in a Series B led by Insight Partners, bringing its total funding to $83 million. The New York startup’s AI-native platform and Autopilot AI agent map, monitor, and automatically remediate identity risks across human and non-human identities in real time. #LinxSecurity #AutopilotAI…
CrystalX is a new malware-as-a-service promoted on Telegram and YouTube that offers remote access, data theft, keylogging, clipboard hijacking, and a variety of prankware features. Kaspersky links CrystalX to WebRAT (Salat Stealer) and describes a Go-based builder, user-friendly control panel, zlib-compressed ChaCha20-encrypted payloads, WebSocket C2, browser and app infostealers, remote VNC control, audio/video capture, and real-time keylogging. #CrystalX #WebRAT

Blocking and invasive endpoint controls push employees into a “Workaround Economy” of unmanaged tools and browser extensions, creating invisible data-exfiltration paths. Security should shift from theatrical blocking to session-level governance—prompt-level DLP, extension risk-scoring, and agentless controls—to enable productivity while preventing leaks. #DeepSeek #ChatGPT…

Microsoft warns of a new campaign that uses WhatsApp messages to distribute malicious Visual Basic Script (VBS) files that initiate a multi-stage infection chain. The attackers rename legitimate Windows utilities, retrieve secondary payloads from AWS, Tencent Cloud, and Backblaze B2, tamper with UAC and registry settings, and install unsigned MSI packages…

CERT-UA disclosed a phishing campaign that impersonated the agency to distribute a password-protected ZIP hosting a Go-based remote access trojan named AGEWHEEZE. The campaign, attributed to UAC-0255/Cyber Serp, targeted state, medical, educational, financial, security, and software organizations but resulted in limited confirmed infections while the actor claimed larger-scale compromises and posted…