WhatsApp said it alerted about 200 users—mostly in Italy—that they were tricked into installing a fake iPhone WhatsApp client infected with spyware the company blames on SIO’s ASIGINT subsidiary. WhatsApp logged out and warned the victims, stressed this was not a WhatsApp vulnerability, and linked the incident to prior spyware campaigns…
Category: Cyber Security News
EvilTokens is a phishing-as-a-service kit sold via Telegram that integrates device code phishing to hijack Microsoft accounts and enable large-scale business email compromise campaigns. Sekoia researchers observed document-based lures that redirect victims through legitimate Microsoft device login flows, allowing attackers to obtain access and refresh tokens for persistent access across email, files, and Teams. #EvilTokens #Microsoft
Attackers exploited a zero-day in TrueConf’s update mechanism (CVE-2026-3502) to replace legitimate updates with malicious executables and distribute them to all connected endpoints. Check Point links the TrueChaos campaign to Chinese-nexus activity and observed DLL sideloading, UAC bypass, reconnaissance, and likely use of the Havoc C2; TrueConf versions 8.1.0–8.5.2 were patched in 8.5.3 (March 2026). #TrueConf #Havoc
Apple has expanded availability of iOS 18.7.7 so more devices running iOS 18 can receive security updates that protect against the actively exploited DarkSword exploit kit. DarkSword abused six tracked CVEs and was used by actors such as PARS Defense, UNC6748, and UNC6353 to deploy infostealers and backdoors including GhostBlade, GhostKnife, and GhostSaber. #DarkSword #GhostBlade

A 15-year-old integer underflow in strongSwan’s EAP-TTLS plugin can trigger massive heap corruption and allow an attacker to knock VPN services offline by forcing impossible memory allocations. Bishop Fox and strongSwan (CVE-2026-25075) advise upgrading vulnerable installations to 6.0.5 or later, disabling EAP-TTLS if unused, and using the provided non-crashing test tool…
Nissan says recent breach claims relate to an undisclosed third‑party vendor and its investigation found no evidence that Nissan systems or customer information were compromised. The Everest hacking group claims to have stolen 910 GB from a file‑transfer system used by a vendor serving Nissan and Infiniti dealerships, threatened to release…
Security experts say hundreds of millions of dollars in cryptocurrency were stolen from Drift after the platform confirmed an active cyberattack and suspended deposits and withdrawals. Firms estimated losses between about $130 million and over $285 million as the attacker repeatedly converted funds while security teams and exchanges work to contain…

ReliaQuest has observed an in-the-wild campaign distributing a new malware family called DeepLoad that steals credentials and intercepts browser interactions. The campaign uses the ClickFix technique to trick users into running a persistent PowerShell loader that compiles evasive DLLs, injects into LockAppHost.exe, and facilitates real-time cryptocurrency theft. #DeepLoad #ClickFix…
Hasbro detected unauthorized access to its network on March 28, took some systems offline, and is working with external cybersecurity experts to determine the scope and whether any files were compromised. The company has activated business continuity plans to continue orders and shipping but warns interim measures may last several weeks…
Depthfirst raised $80 million in Series B, bringing total funding to $120 million just weeks after its Series A. The company also launched Dfs-mini1, an open-source security model focused on smart contracts that the team says can generalize across security domains. #Depthfirst #Dfs-mini1…
NoVoice is a new Android threat found in over 50 Google Play apps with at least 2.3 million installs that uses steganography and a suite of exploits to obtain root and install a persistent rootkit. It injects into apps to steal sensitive data—most notably WhatsApp encryption keys and backups—allowing attackers to clone accounts; #NoVoice #WhatsApp
Blackpoint Cyber’s 2026 Annual Threat Report shows attackers increasingly gain access by using valid credentials, trusted administrative tools, and user-driven social engineering instead of exploiting software vulnerabilities. Key vectors include SSL VPN abuse, widespread misuse of RMM tools like ScreenConnect, ClickFix-style campaigns, and session-token reuse after MFA, and the report urges treating remote access as high-risk and tightening controls to detect legitimate-looking intrusions #Roadk1ll #ScreenConnect.

Daily Recap, Open-source supply-chain attacks like Axios Attack chain from package managers to cloud credentials to harvest CI/CD tokens and pivot into AWS, enabling theft of source code and data. Patching urgency follows active exploits of Citrix NetScaler CVE-2026-3055 and F5 BIG-IP CVE-2025-53521, with teams like TeamPCP Move and emerging threats such as RoadK1ll continuing to broaden breach opportunities. #AxiosAttack #RoadK1ll
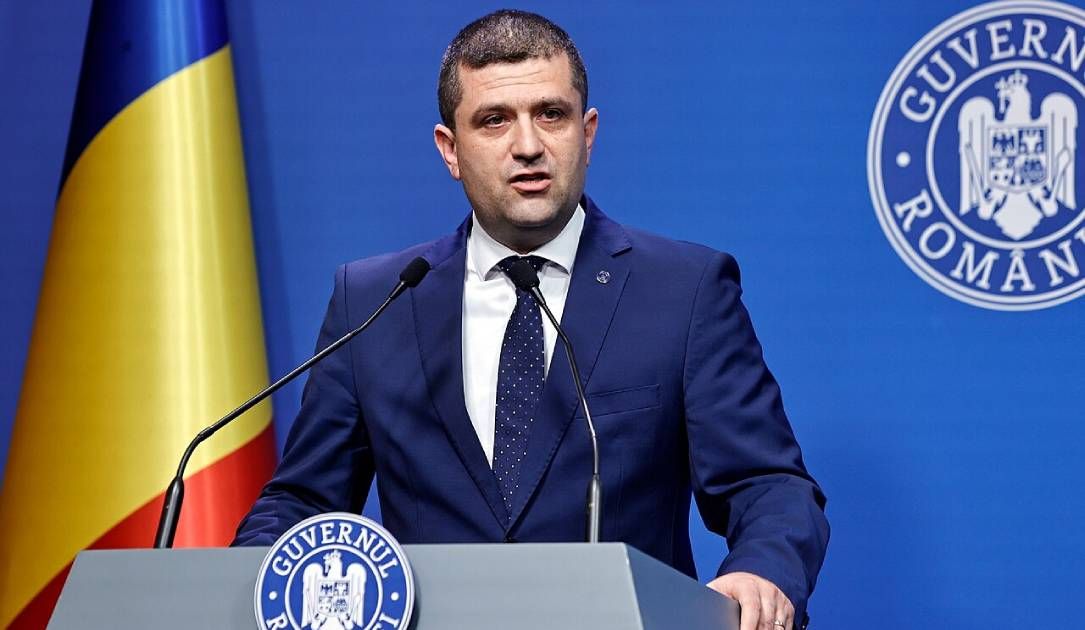
Romanian government institutions face more than 10,000 cyberattack attempts every day, targeting a wide range of public organizations, the defense minister said. Officials link many of the operations to Russian-connected actors and ransomware groups such as Qilin and Gentlemen, and note coordinated disinformation campaigns are also used to shape public opinion….

Agentic AI is reshaping identity security by autonomously planning, adapting, and executing controls, but many enterprise applications remain disconnected and manually managed, creating a last-mile vulnerability for attackers. Register for the April 1, 2026 webcast from SecurityWeek and Cerby to learn breach scenarios, Agentic AI’s current limits, and how to extend…