Microsoft has begun force-upgrading unmanaged Windows 11 24H2 Home and Pro devices to Windows 11 25H2 via a machine-learning-based intelligent rollout. Windows 11 24H2 reaches end of support on October 13, 2026, and users can manually install 25H2, pause updates temporarily, or follow Microsoft’s support guides while emergency updates address issues like Microsoft account sign-ins, Bluetooth visibility, and RRAS vulnerabilities. #Windows11_25H2 #Windows11_24H2
Category: Cyber Security News

The latest ThreatsDay Bulletin is a concise, no-fluff roundup of active internet threats this week, highlighting chained exploits, resurfaced flaws, stealthy log-evasion techniques, and supply-chain abuses. Quick checks are advised because threats like the NoVoice Android rootkit and unpatched ImageMagick zero-days can silently escalate from small bugs into widescale compromises. #NoVoice…

Cisco released urgent patches for a critical Integrated Management Controller (IMC) authentication bypass (CVE-2026-20093) and a Smart Software Manager On-Prem (SSM On-Prem) remote command execution flaw (CVE-2026-20160). Customers should update to the fixed versions immediately because both flaws carry CVSS scores of 9.8 and no workaround is available. #CVE-2026-20093 #CVE-2026-20160…

A large-scale credential harvesting campaign attributed to Cisco Talos cluster UAT-10608 exploits the React2Shell vulnerability in Next.js (CVE-2025-55182) to achieve remote code execution and deploy the NEXUS Listener framework that steals database credentials, SSH keys, cloud IAM tokens, API keys, and other secrets. At least 766 hosts across multiple regions and…
France’s Senate voted in favor of a bill that would restrict social media access for children under 15, potentially making France the first European country to follow Australia’s example. The measure creates two platform categories—those banned outright for harming children’s development and those allowed with parental consent—and aligns with wider EU…
Decentralized finance platform Drift confirmed that $280 million was withdrawn during a sophisticated security incident that involved a rapid takeover of its security council administrative powers and the execution of pre-signed transactions. Drift says deposits in borrow and lend features, vaults, and trading were affected and that the breach—attributed by Elliptic…

The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia
Unit 42 exposed a large, persistent cyberespionage campaign targeting a high-value Southeast Asian government organization, operated by three concurrent activity clusters linked to China-aligned threat actors. The clusters used USBFect/PUBLOAD via infected removable media, a multi-payload toolkit including EggStremeFuel and Masol/Gorem/TrackBak, and the Hypnosis loader delivering FluffyGh0st to maintain stealthy, long-term…
Thirty-eight cybersecurity M&A deals were announced in March 2026, featuring major strategic transactions across defense, cloud security, AI, and insurance. Notable moves included Google’s completion of its $32 billion acquisition of Wiz, Airbus agreeing to buy Ultra Cyber, Databricks acquiring Antimatter and SiftD.ai for its Lakewatch SIEM, and OpenAI’s purchase of…
Apple is rolling out iOS and iPadOS updates to older devices to protect them against the DarkSword exploit kit, which targets six iOS vulnerabilities and can fully compromise devices with minimal user interaction. DarkSword, linked to the Coruna infrastructure and used by state-sponsored groups and commercial surveillance vendors, was partially patched…
Anthropic accidentally published a JavaScript sourcemap that exposed Claude Code’s 512,000-line TypeScript operational blueprint, and researchers quickly reconstructed and redistributed the code. Separately, Adversa AI disclosed a critical permission-enforcement vulnerability that lets crafted prompt-injected command pipelines bypass deny rules, risking credential exfiltration and supply-chain or cloud compromise. #ClaudeCode #AdversaAI…
Drift Protocol lost at least $280 million after an attacker seized administrative control of its Security Council by leveraging durable nonce accounts and pre-signed transactions to time a precise takeover. Drift says no smart contract flaws or seed phrase compromises occurred, the protocol is effectively frozen while partners and authorities work to trace and recover funds. #DriftProtocol #Solana
Threat actors are exploiting the Claude Code source code leak by posting fake GitHub repositories that deliver the Vidar information-stealing malware to users seeking the leak. Zscaler researchers found a malicious repo by user “idbzoomh” that uses SEO to rank for leak queries and distributes a 7‑Zip archive whose Rust dropper ClaudeCode_x64.exe installs Vidar and the GhostSocks proxy. #Vidar #ClaudeCode
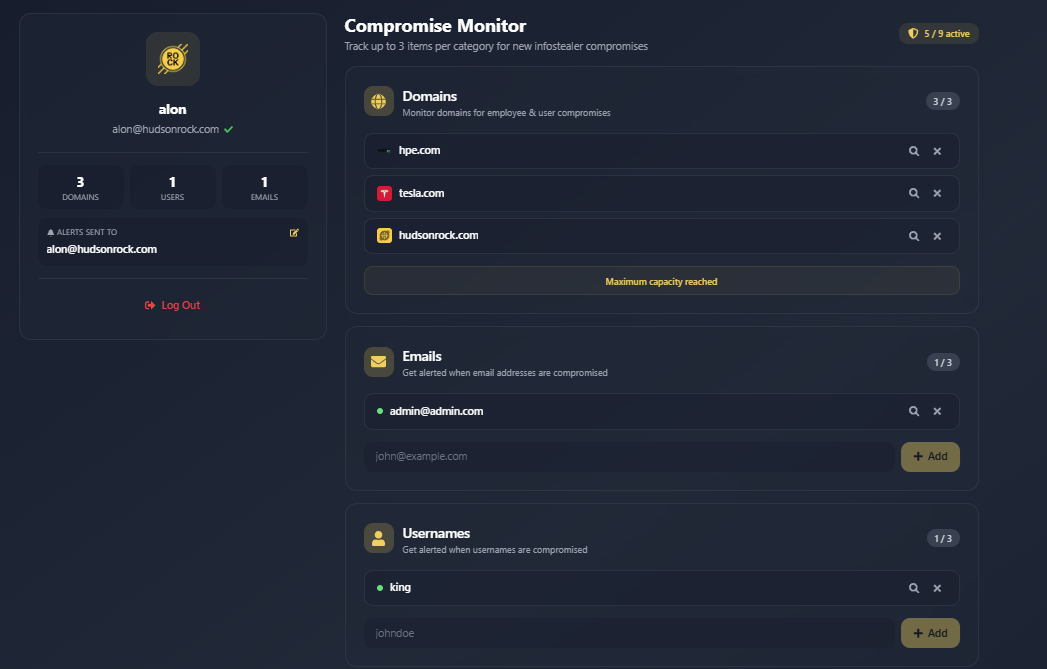
There is a large surge in Infostealer infections actively exfiltrating browser data and session tokens, not just historical breaches. Hudson Rock now offers a free, privacy-first monitoring dashboard that lets individuals track up to three emails, three usernames, and three domains with real-time alerts for active compromises. #Infostealer #HudsonRock
Researchers warn that short-lived, systematically rotated residential proxies make malicious traffic indistinguishable from legitimate home users and undermine IP reputation systems. GreyNoise’s analysis of 4 billion edge sessions found roughly 39% appearing to originate from home networks with 78% invisible to reputation feeds, and the company recommends shifting to behavior-based detection. #GreyNoise #IPIDEA

Daily Recap, the day’s headlines span supply‑chain compromises such as Axios trojanizing the npm package to drop SILKBELL and WAVESHAPER.V2, along with Anthropic Claude Code exposure, LiteLLM breaches affecting Mercor, and a Trivy‑related breach that exposed Cisco source code. Daily Recap, coverage also highlights AI/Cloud risks, CVEs and patches (Chrome CVE-2026-5281, Windows KB5086672, GIGABYTE CVE-2026-4415, TrueConf CVE-2026-3502) and editor RCEs for Vim/Emacs, plus nation‑state activity (APT28 PRISMEX, AgeWheeze, Handala Hack Team, Romania attacks), ransomware and crime trends (Meriden, Leak Bazaar, Uranium Theft) and policy shifts (FBI warning on Chinese apps, Proton Meet, Drive ransomware detection). #Axios #SILKBELL #WAVESHAPER #ClaudeCode #LiteLLM #Mercor #Trivy #Cisco #APT28 #PRISMEX #Romania #AgeWheeze #KashPatel #DutchTreasury #Meriden #LeakBazaar #Uranium #Vim #Emacs