
Grinex, a Kyrgyzstan-incorporated crypto exchange believed to be a rebrand of sanctioned Garantex, said it is suspending operations after a hack that stole about $13.74 million (over 1 billion rubles) and blamed Western intelligence agencies. Blockchain analysts traced the theft to transfers on TRON and Ethereum, highlighted rapid swaps from USDT…
Category: Cyber Security News

In 2024, 68% of cloud breaches were caused by compromised service accounts and forgotten API keys—unmanaged non-human identities, not phishing or weak passwords. Join the webinar to learn how to discover and eliminate these “Ghost Identities” with discovery scans, permission right-sizing, and automated lifecycle policies before attackers use them as backdoors….
A security researcher using the aliases Chaotic Eclipse and Nightmare Eclipse released two new proof-of-concept privilege-escalation exploits for Microsoft Defender, named RedSun and UnDefend, after earlier publishing BlueHammer. Huntress observed all three techniques used in the wild, with attackers dropping renamed exploit files into users’ Pictures and Downloads folders, mapping privileges and harvesting credentials, and Microsoft may need to issue an out-of-band patch. #RedSun #UnDefend
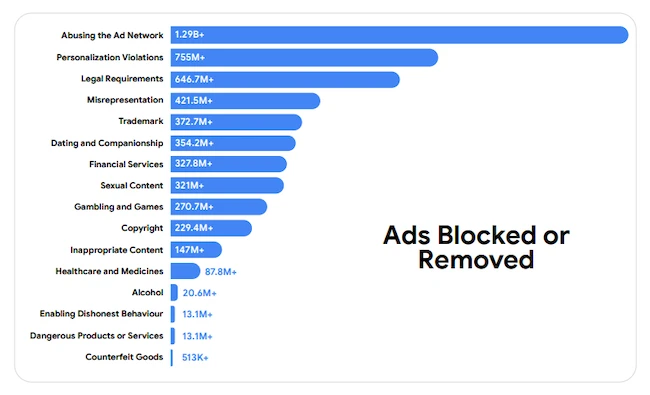
Google says its security teams use Gemini AI models around the clock to detect and block deceptive ads in real time by analyzing hundreds of billions of signals. In 2025 Google removed or blocked over 8.3 billion ads and suspended 24.9 million accounts, and says Gemini’s intent-based analysis and faster processing of user reports helped quadruple actionable reports and speed responses. #Google #Gemini #Malvertising #AdsSafetyReport
Ukrainian officials confirmed a long-running cyber-espionage campaign attributed to Russia-linked APT28 targeted dozens of local government and law enforcement email accounts, with Western researchers reporting more than 170 compromised accounts. The intrusions exploited vulnerabilities in the open-source Roundcube webmail platform, CERT-UA has tracked three waves since 2023, and affected agencies including SAP and ARMA say reviews found no clear evidence of internal data theft while warning leaks could fuel disinformation. #APT28 #Roundcube

Authorities from 21 countries dismantled 53 domains, arrested four people, and disrupted DDoS-for-hire infrastructure in a coordinated effort called Operation PowerOFF. Law enforcement seized databases with records for over 3 million alleged users, sent more than 75,000 warnings, served 25 search warrants, and removed advertising to curb use of IP stressors and booters. #OperationPowerOFF #Europol

Two New Jersey men were sentenced for running a scheme that placed North Korean operatives inside more than 100 U.S. companies, generating over $5 million for the regime and stealing sensitive, ITAR‑controlled defense files. The operation used shell companies, stolen identities and laptop farms to launder wages back to Pyongyang and poses ongoing national‑security risks due to the dual‑use intelligence capabilities of DPRK IT workers. #DPRK #ITAR

Congress is debating reauthorization of Section 702 of FISA under the 2024 Reforming Intelligence and Securing America Act (RISAA), with supporters saying it codified reforms and critics saying its real-world effects are unclear. Major disputes focus on ambiguous query counting tied to an FBI “participants” filter, possible expansion of covered service providers, a critical FISC opinion, and partisan disagreement over a clean extension. #Section702 #RISAA
Researchers from Fortinet FortiGuard Labs and Palo Alto Networks Unit 42 report threat actors exploiting vulnerabilities in TBK DVRs and end-of-life TP-Link routers to deploy Mirai-like botnets, including a Nexcorium variant. The campaigns leverage CVE-2024-3721 to deliver downloaders, use brute-force Telnet and other exploits for lateral movement and persistence, and scans…

Daily Recap, law enforcement across 21 countries disrupted DDoS-for-hire networks in Operation PowerOFF, seizing 53 domains and warning over 75,000 users. The roundup also covers prosecutions such as Kamerin Stokes for DraftKings account theft and North Korea laptop-farm schemes that redirected over $5 million, along with exploitation of nginx-ui CVE-2026-33032 and Apache ActiveMQ flaws enabling SYSTEM privileges. #PowerOFF #DraftKings #APT28 #GRU #LaptopFarms #NginxUI #ActiveMQ #Windows #KuwaitBanks #TennesseeHospital #NorthernIrelandEducationAuthority
Payouts King ransomware operators are abusing the QEMU emulator to run hidden Alpine Linux virtual machines on compromised hosts, using port forwarding and reverse SSH tunnels to execute payloads, harvest credentials, and bypass endpoint security. Sophos and Zscaler link these campaigns to GOLD ENCOUNTER and likely former BlackBasta affiliates, with initial access achieved via exposed VPNs, CitrixBleed 2 exploitation, Microsoft Teams phishing, and QuickAssist abuse. #PayoutsKing #QEMU
Law enforcement in more than 20 countries coordinated a takedown of DDoS-for-hire platforms, seizing over 50 domains, identifying about 75,000 users, executing 25 search warrants and arresting four people. U.S. authorities also seized eight sites including Vac Stresser and Mythical Stress and exposed low-cost subscription plans that enabled large-scale attacks. #VacStresser…
More than 18 months after the June 2024 Qilin ransomware attack on Synnovis, at least one NHS trust (SLaM) remains without fully restored pathology systems and is managing large backlogs of delayed test results. The attack disrupted blood testing, cancelled operations, exposed sensitive data of nearly one million patients, and has…

This SecurityWeek roundup highlights legislative, defensive, and investigative developments alongside multiple active threats and disclosures affecting cloud services, developer tools, and education systems. Notable stories include the W3LL phishing takedown, a spreading GlassWorm IDE dropper, active ShowDoc RCE exploitation, AWS RES fixes, and large data leaks tied to ShinyHunters. #GlassWorm #ShinyHunters…
Shadow AI emerges as employees adopt unapproved generative and agentic AI tools, creating invisible, unmanaged risks that magnify those of traditional shadow IT. CoChat provides enterprise visibility, governance, and a human-in-the-loop control layer to interrupt dangerous autonomous actions and enable collaborative use of multiple LLMs across teams. #CoChat #OpenClaw…