
White House chief of staff Susie Wiles plans to sound out Anthropic CEO Dario Amodei about the company’s new Mythos model, which has drawn federal attention for how it could transform national security and the economy. The meeting comes amid tensions with the Trump administration over Anthropic’s safeguards and limited release…
Category: Cyber Security News
The underground credit card market has grown more volatile and deceptive, pushing actors to adopt structured vetting, supplier validation, and stricter OPSEC to avoid scams and law enforcement exposure. A forum guide analyzed by Flare details vendor‑vetting checklists, mirror infrastructure, and payment hygiene—highlighting shops like CardingHub and the use of privacy coins such as Monero. #CardingHub #Monero
Kyrgyzstan-based crypto exchange Grinex suspended operations after a $13.7 million theft from wallets used by Russian users, an attack the exchange attributed to foreign (Western) intelligence agencies while blockchain analysts traced the stolen funds through TRON and Ethereum via the SunSwap protocol. Grinex, widely reported as a rebrand of sanctioned Russian exchange Garantex and operator of the ruble-backed stablecoin A7A5, says the attack aimed to harm Russia’s financial sovereignty, but independent firms Elliptic and TRM Labs have not published technical evidence linking the theft to a specific state actor. #Grinex #Garantex #A7A5 #SunSwap #TokenSpot
This week’s roundup covers multimillion-dollar crypto thefts, state-linked fraud schemes, regulatory scrutiny, underground exploit markets, and extortion-driven breaches. Attackers are increasingly exploiting routers, DNS layers, third-party services, and decentralized systems to intercept data, manipulate transactions, and evade enforcement. #Grinex #ShinyHunters…
Phishing and other AI-driven attacks are evolving faster than many MSP and corporate defenses, enabling targeted business email compromise and ransomware that can bypass traditional controls. BleepingComputer’s webinar with Kaseya on May 14, 2026 explores how integrating prevention, detection, and backup/BCDR enables MSPs to reduce downtime and ensure rapid recovery #Kaseya #BleepingComputer
A House subcommittee held a roundtable where lawmakers, AI executives, and academics aired existential concerns about the rapid development of artificial intelligence and its implications for national security, ethics, and the climate. Discussions highlighted risks such as misuse of AI for sensitive government data, deepfake likenesses, and Anthropic’s claim that its…
A 23-year-old Memphis man, Kamerin Stokes, was sentenced to 30 months in prison for his role in a 2022 credential-stuffing attack that compromised about 60,000 DraftKings accounts. Stokes, who used the alias ‘TheMFNPlug,’ sold bulk access to compromised accounts, was ordered to forfeit $125,000 and pay $1.3 million in restitution, and…

A critical authentication bypass in nginx-ui (CVE-2026-33032) enables unauthenticated attackers to interact with the /mcp_message endpoint and achieve a full Nginx server takeover, and exploitation has been observed in the wild. The issue can be chained with CVE-2026-27944 to retrieve node_secret from backups, and maintainers released nginx-ui 2.3.4 with fixes and…
Kuwait’s banking sector has deployed an advanced virtual operations system, led by the Kuwait Banking Association under the Central Bank of Kuwait, to detect and respond to financial fraud in real time. The centralized “virtual war room” links banks with government bodies to halt transactions, trace funds, and shift from reactive…
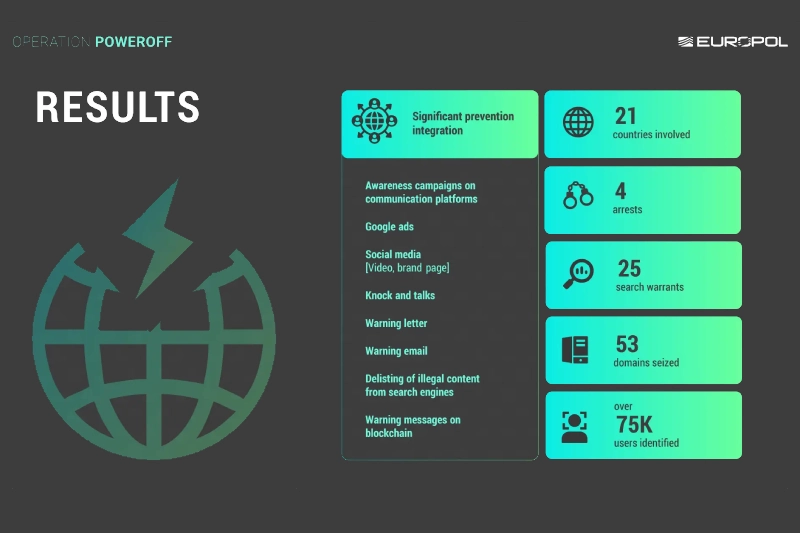
Law enforcement agencies across Europe, the United States, and partner nations coordinated Operation PowerOFF to disrupt the commercial DDoS-for-hire ecosystem, seizing domains, making arrests, and issuing over 75,000 warning notices to suspected users. The action targeted platforms including Vac Stresser and Mythical Stress and highlighted that DDoS services remain resilient, requiring…
Kamerin Stokes, 23, was sentenced to 30 months in prison for selling access to tens of thousands of DraftKings accounts hijacked in a November 2022 credential-stuffing attack linked to Nathan Austad and Joseph Garrison. After pleading guilty, briefly reopening his shop as TheMFNPlug with the tagline “fraud is fun,” and violating pretrial release, Stokes was remanded and ordered to pay $1,327,061 in restitution and $125,965.53 in forfeiture with three years of supervised release. #DraftKings #KamerinStokes
Microsoft confirmed that after installing the April 2026 security update (KB5082063), some Windows domain controllers using Privileged Access Management are entering restart loops due to LSASS crashes during startup. The problem affects non‑Global Catalog DCs across multiple Windows Server releases and may also cause KB5082063 install failures and BitLocker prompts on some Server 2025 devices, so administrators should contact Microsoft Support for mitigation. #LSASS #KB5082063
CISA warned that a high-severity Apache ActiveMQ vulnerability patched on March 30 (CVE-2026-34197) is being actively exploited, prompting an emergency federal patching deadline under BOD 22-01. Discovered after 13 years by Horizon3 researcher Naveen Sunkavally using Claude AI, the input-validation flaw allows authenticated attackers to execute arbitrary code and ShadowServer reports over 7,500 exposed ActiveMQ servers online. #ApacheActiveMQ #CVE202634197
Law enforcement in 21 countries coordinated Operation PowerOff to disrupt DDoS-for-hire (booter) services, resulting in the takedown of 53 domains, the arrest of four individuals, and the seizure of infrastructure. The operation exposed over 3 million criminal user accounts, sent 75,000 warning notices, executed 25 search warrants, and will transition to…
Straiker discovered NomShub, a vulnerability chain in Cursor that used hidden prompts in malicious repositories to trigger an indirect prompt injection and a sandbox bypass, allowing attackers to write code to developer machines and gain shell access via Cursor’s remote tunnel. Because the exploit leveraged a signed binary, macOS sandbox behavior,…